

 projectdiscovery/openrisk
openrisk is a tool that generates a risk score based on the results of a Nuclei scan.
 boreas37/cve-2026-44848-poc
PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.
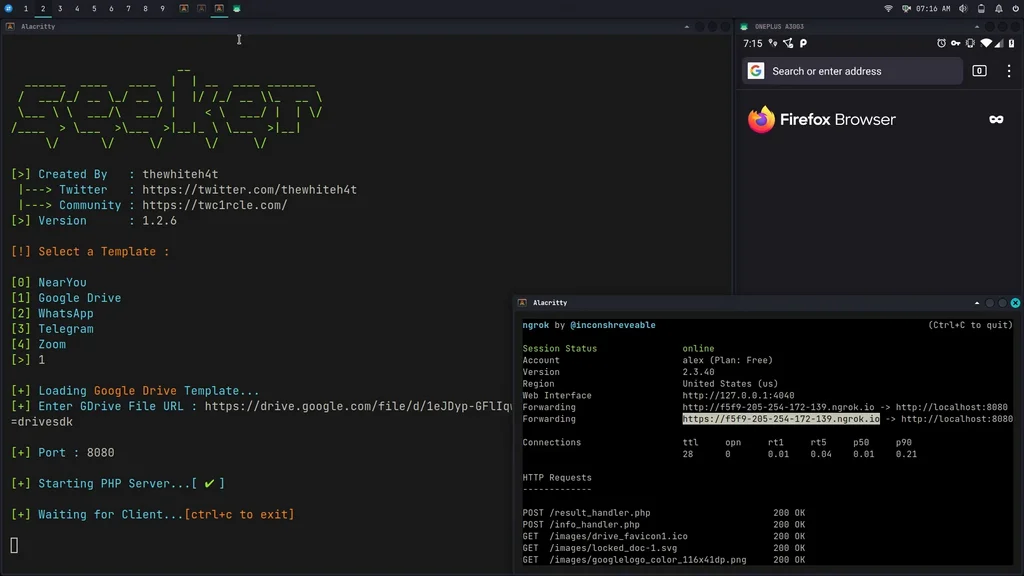 thewhiteh4t/seeker
Accurately Locate Smartphones using Social Engineering
 kouf320/docker-lab-cve-2017-5638-cve-2021-41773
Docker-based multi-stage attack emulation lab demonstrating CVE-2017-5638 and CVE-2021-41773 exploitation, lateral movement, and Suricata IDS…
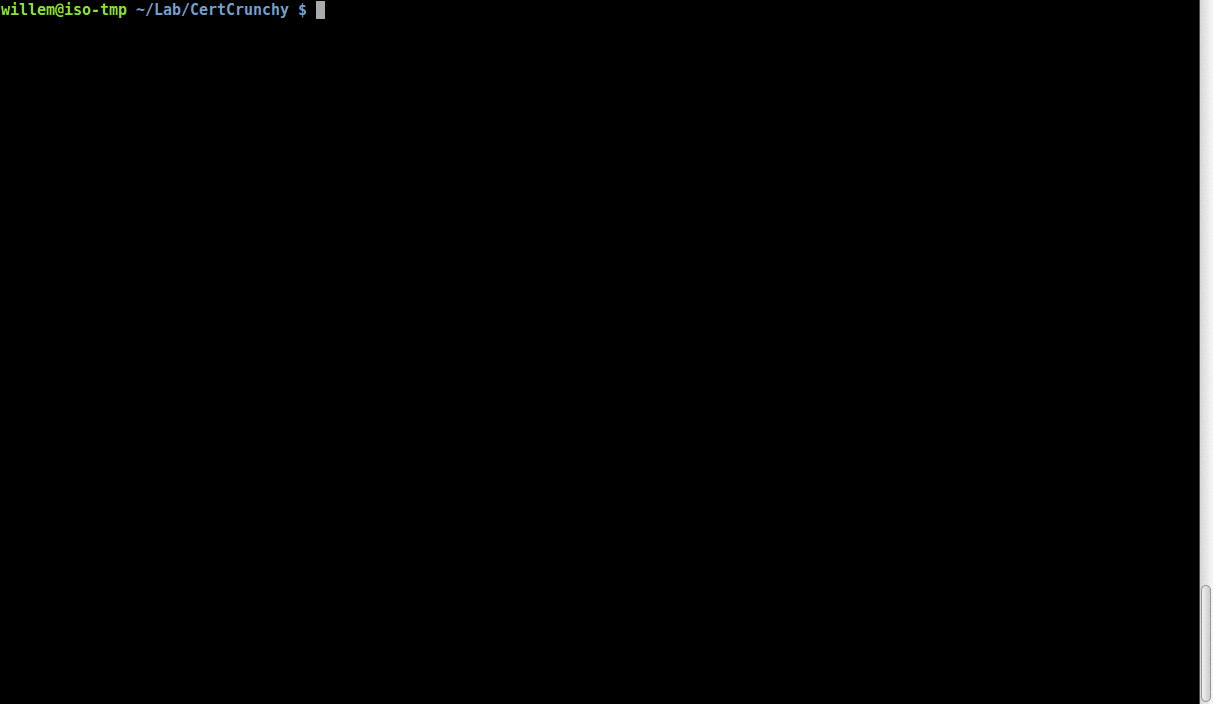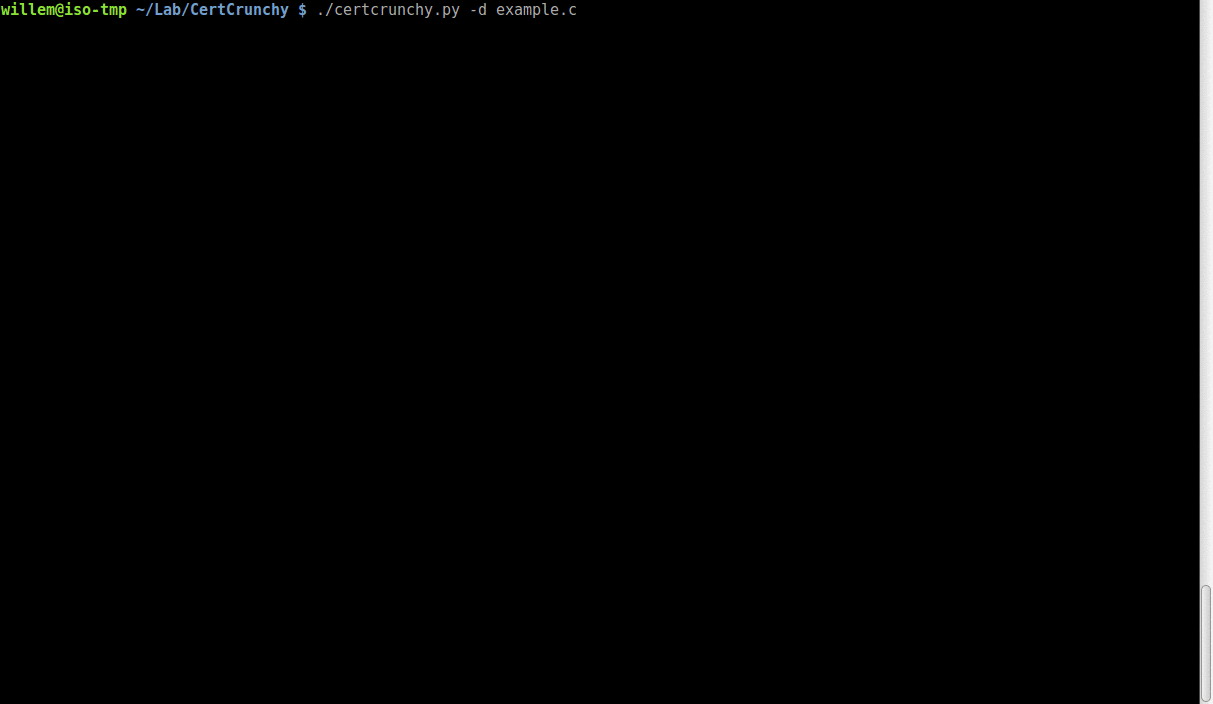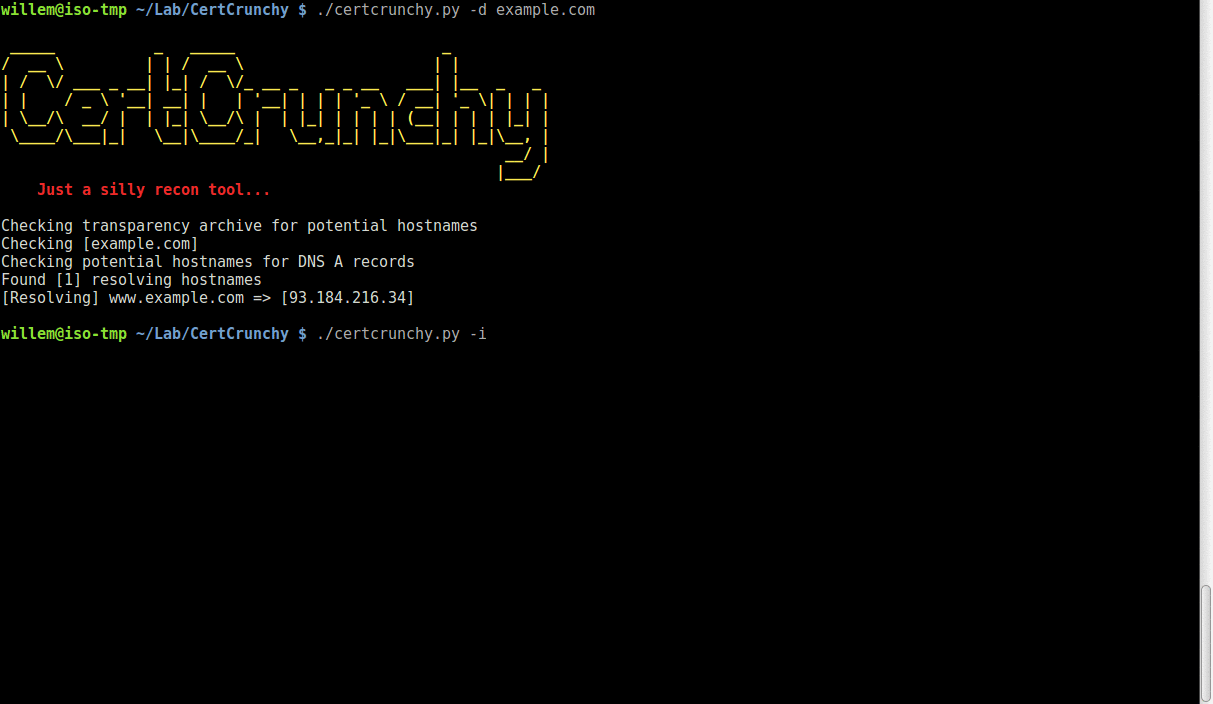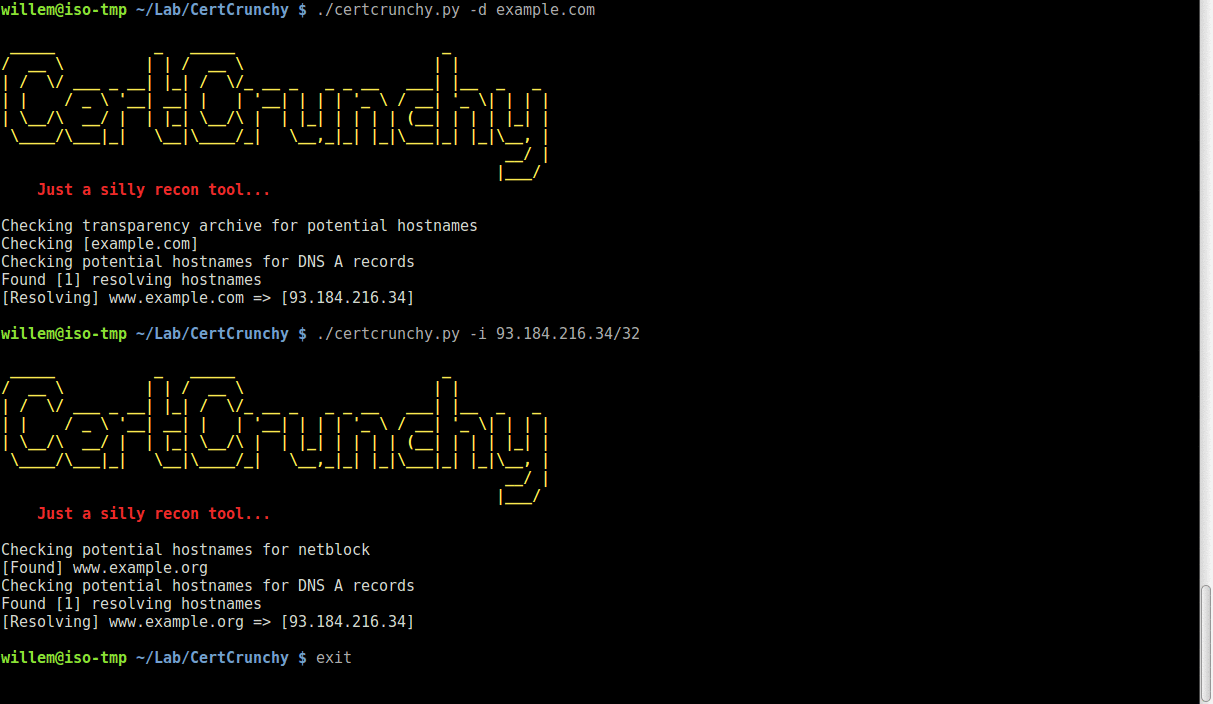 joda32/certcrunchy
Just a silly recon tool that uses data from SSL Certificates to find potential host names
 idov31/novahypervisor
Windows hypervisor for Intel x64: defensive host hypervisor for Windows designed to mitigate kernel-level attacks including BYOVD, compatible with…
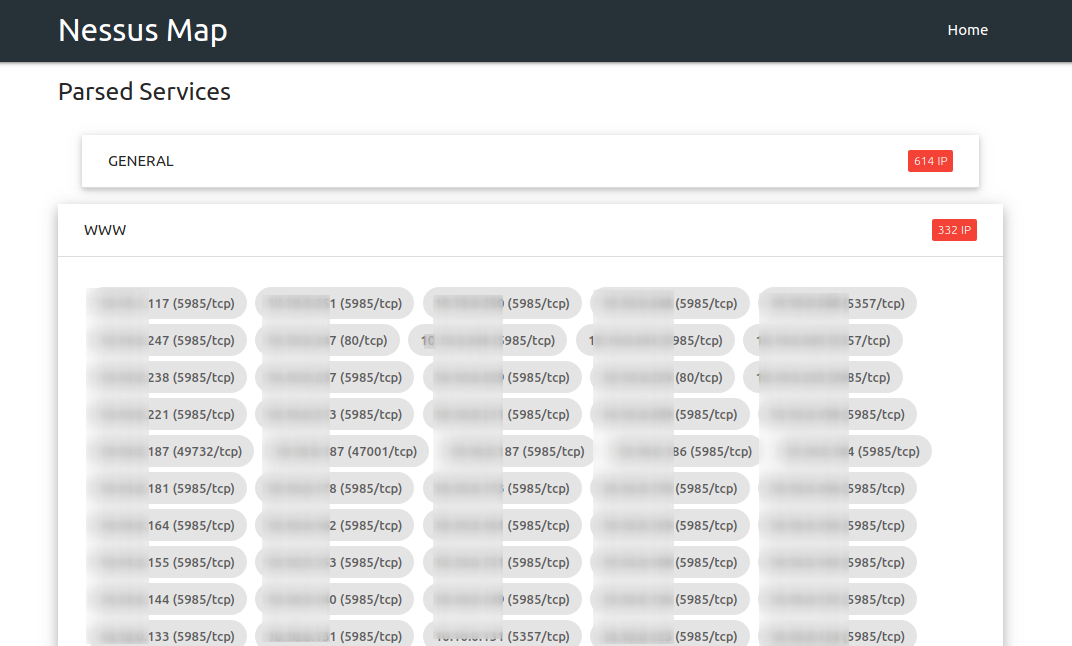 ebryx/nessus_map
Parse .nessus file(s) and shows output in interactive UI
 s_r_e_e_r_a_j/reconhound
ReconHound is a Python-based web reconnaissance tool designed for penetration testers, bug bounty hunters, and ethical hackers. It supports directory…
 yonathanpy/cve-2025-32462-cve-2025-32463-poc-lab
Container-based lab with proof-of-concept exploits for two critical sudo vulnerabilities: host validation bypass (CVE-2025-32462) and NSS library…
 nerium-security/cve-2025-55182
Host-based detection rules for the RCE vulnerability in the React JavaScript framework.
 enzocipher/cve-2025-25198
Captures password reset tokens from Mailcow Host header injection attacks.
 jamf/aftermath
Swift-based macOS incident response framework for collecting and analyzing host artifacts, including filesystem timestamps, browser data, unified…
 maaythm/cve-2025-32462_32463-lab
Docker PoC for CVE-2025-32462 & CVE-2025-32463 (sudo), based on Stratascale CRU research.
 marcnewlin/hi_my_name_is_keyboard
Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…
 orlikoski/skadi
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
 ccob/lsarelayx
System-wide NTLM relay tool that hooks Windows authentication APIs to relay incoming NTLM connections, downgrade Kerberos, and dump NetNTLM hashes…