
sj
 bishopfox/sj
A tool for auditing endpoints defined in exposed (Swagger/OpenAPI) definition files.
api-security-testingpenetration-testingvulnerability-scanners+1
878
bishopfox/sjA tool for auditing endpoints defined in exposed (Swagger/OpenAPI) definition files.
 s_r_e_e_r_a_j/ziprarhunter
ZipRarHunter is a powerful command-line ethical hacking tool designed to crack passwords of ZIP and RAR archive files using a wordlist.
 s_r_e_e_r_a_j/ftpbuster
FTPBuster is a powerful command-line brute-forcing tool designed to brute-force FTP, SFTP, and explicit FTPS servers by performing dictionary-based…
 s_r_e_e_r_a_j/sshbuster
SSHBuster is a powerful command-line SSH brute-forcing tool designed for ethical hacking and penetration testing. It performs dictionary-based…
 piotr-kniaz/eslockdecryptor
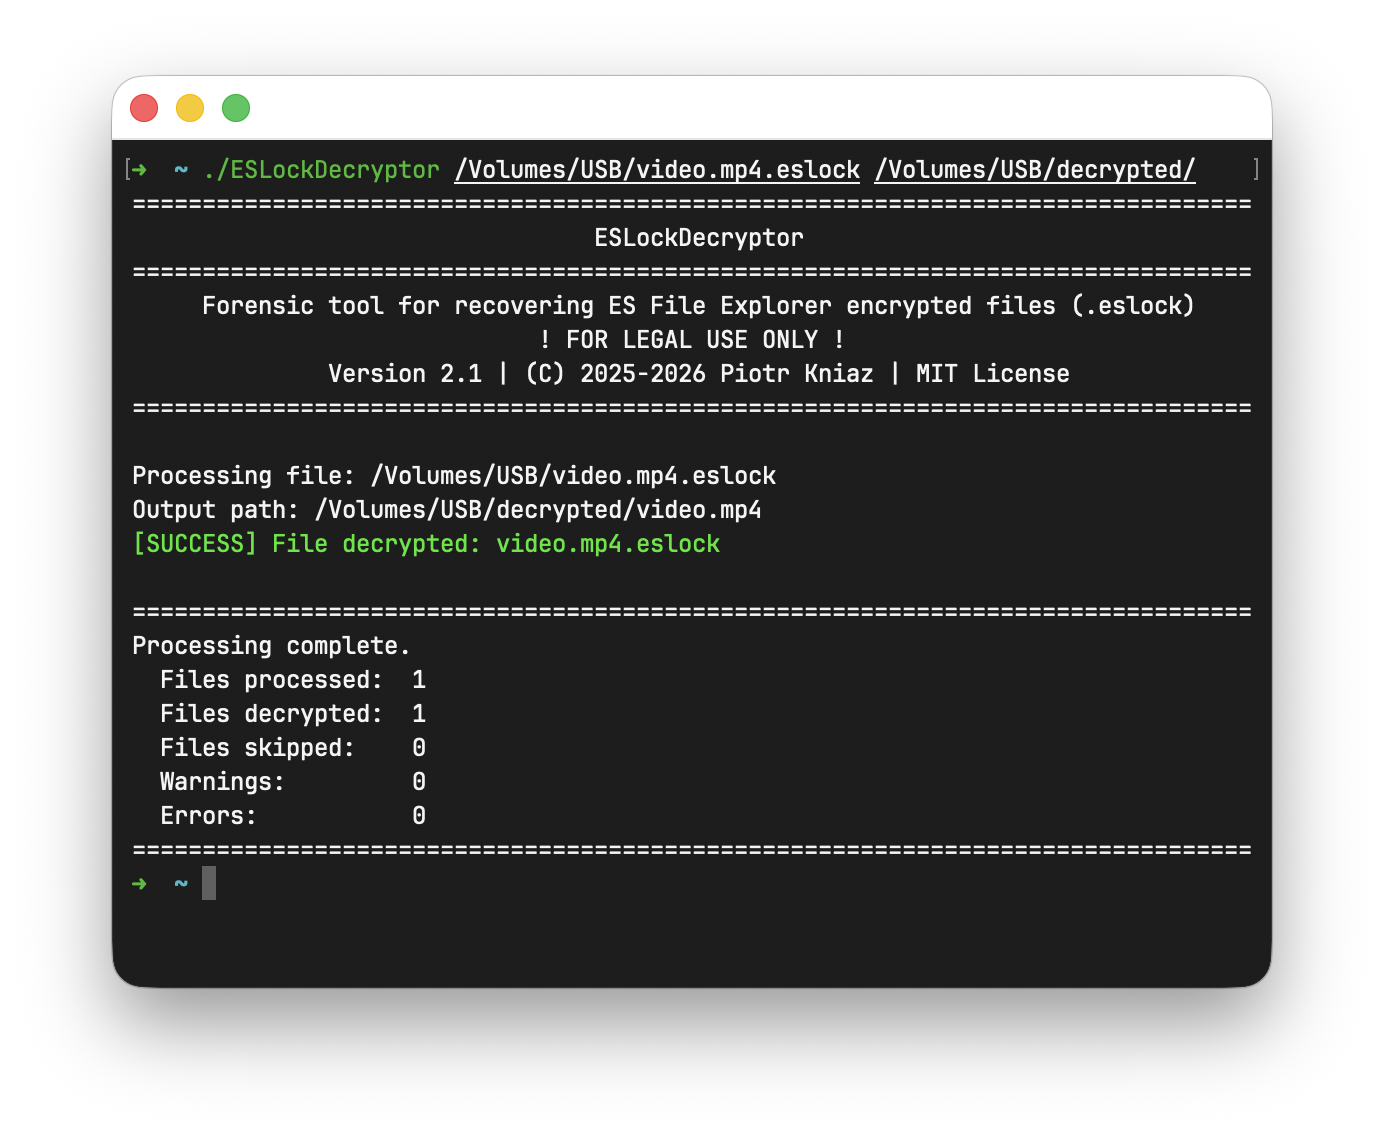
Utility for recovering ES File Explorer encrypted files (.eslock)
 dominicbreuker/pspy
Monitor linux processes without root permissions
 hueristiq/xsubfind3r
Passive subdomain discovery tool that aggregates results from multiple online sources via CLI, supporting stdin/stdout, JSONL output, and API key…
 hueristiq/xurlfind3r
Passive URL discovery tool that collects domain-associated URLs from multiple public sources via command-line, supporting stdin/stdout and JSONL…
 byt3hx/jsleak
Concurrent CLI tool for discovering secrets, API keys, and links in JavaScript files during web reconnaissance, with custom regex pattern support and…
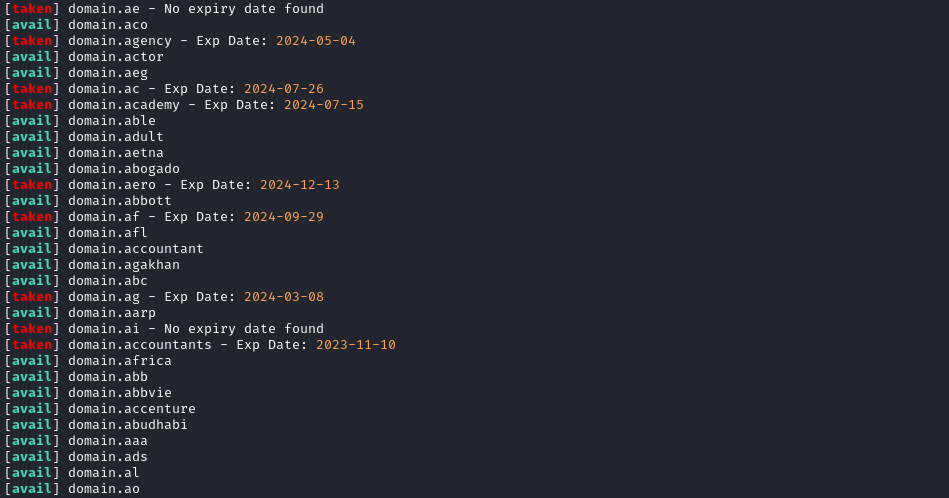 yuyudhn/tldhunt
Bash-based domain availability checker that scans WHOIS records across multiple TLDs to find unregistered domains for red teaming and phishing…
 m31r0n/sniprecover-cli
Detection and restoration of Windows Snipping Tool PNG captures vulnerable to CVE-2023-28303
 anonkryptiquz/nextsploit
NextSploit is a command-line tool designed to detect and exploit CVE-2025-29927, a security flaw in Next.js
 pixilated730/nextjs-exploit-
CVE-2025-29927
 0x11dfe/file-unpumper
Tool that can be used to trim useless things from a PE file such as the things a file pumper would add.
 0zer0d4y/fuegotest
A CLI tool for detecting CVE-2023-20048 vulnerability in Cisco Firepower Management Center.
 reneoliveirajr/wp_cve-2020-35489_checker
WordPress Sites Vulnerability Checker for CVE-2020-35489 - "Educational Use Only"
 daddycocoaman/dumpscan
Finding secrets in kernel and user memory
 nu11secur1ty/insect
High-performance web path discovery and directory brute-forcing tool. Discovers hidden files, directories, and endpoints using customizable…