
graylog2-server
 graylog2/graylog2-server
Centralized log management platform for collecting, indexing, and analyzing streaming logs, with alerting and event correlation for security…
defensive-toolsincident-responseintrusion-detection+1
8.2k
graylog2/graylog2-serverCentralized log management platform for collecting, indexing, and analyzing streaming logs, with alerting and event correlation for security…
 owasp-modsecurity/modsecurity
ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
 criticalpathsecurity/zeek-intelligence-feeds
Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…
 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring
 jm33-m0/emp3r0r
Linux post-exploitation C2 framework with gossip mesh networking, memory-only operations, modular payloads, and OPSEC-focused transport for red team…
 bert-janp/open-source-threat-intel-feeds
This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…
 sigmahq/pysigma-backend-opensearch
pySigma OpenSearch backend
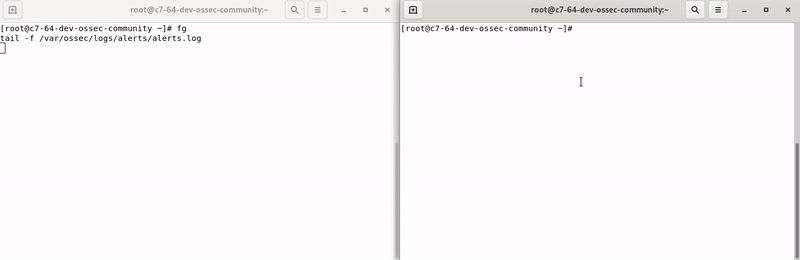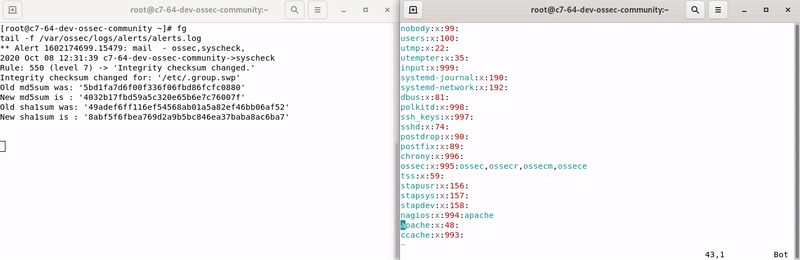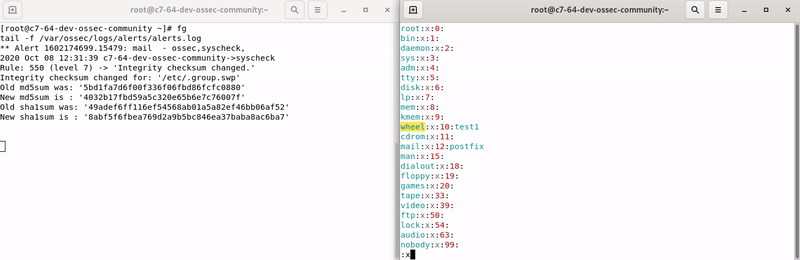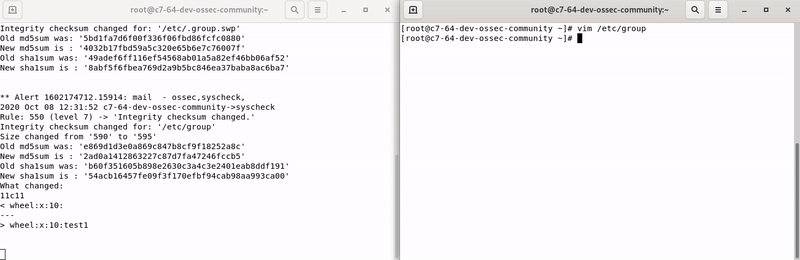 ossec/ossec-hids
OSSEC is an Open Source Host-based Intrusion Detection System that performs log analysis, file integrity checking, policy monitoring, rootkit…
 ntop/ndpi
Open Source Deep Packet Inspection Software Toolkit
 sk4r4b/ntdll-reconstruction
A technique that mixes NTDLL unhooking and hellsgate gate varients
 sigmahq/sigma-cli
The Sigma command line interface based on pySigma
 crowdsecurity/crowdsec
Open-source IDS/IPS and WAF engine that analyzes logs and HTTP requests to detect and block malicious IPs, leveraging a crowdsourced community…
 julioliraup/antiphishing
Advanced Phishing Protection: Suricata rulesets open and free
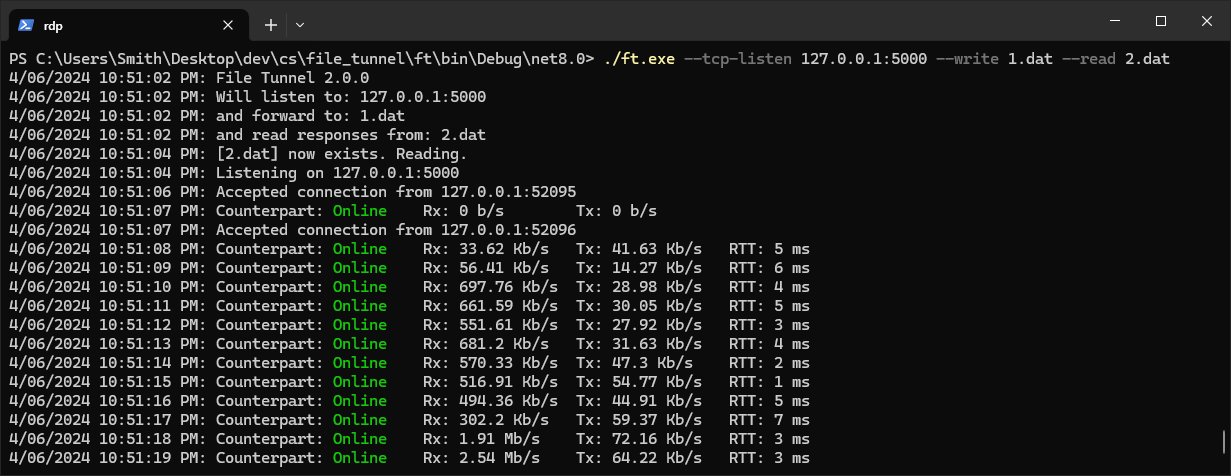 fiddyschmitt/file-tunnel
Tunnel TCP connections through a file
 matrixtm/mhddos
Best DDoS Attack Script Python3, (Cyber / DDos) Attack With 60 Methods
 thinkst/opencanary
Low-resource honeypot that emulates common network services to detect post-breach attacker activity, with extensible protocol modules and…
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
 fail2ban/fail2ban
Daemon to ban hosts that cause multiple authentication errors