
SliverMirage
 daniomass/slivermirage
Crystal Palace PICO loader for Sliver C2 dual-layer AMSI bypass, ETW silencing, AES-256-CBC encrypted payloads, 6 delivery variants
binary-analysiscommand-and-controlexploitation+4
46
daniomass/slivermirageCrystal Palace PICO loader for Sliver C2 dual-layer AMSI bypass, ETW silencing, AES-256-CBC encrypted payloads, 6 delivery variants
 kaandemir993/salat-stealer-telegram-proxy-decoy-c2-analysis
"Reverse engineering analysis of Salat Stealer, a Go-based info-stealer that uses a Telegram proxy decoy, C2 communication, and encrypted memory…
 gl1tch0x1/dirtyclone
Proof-of-concept local privilege escalation tool exploiting a kernel XFRM/ESP vulnerability (CVE-2026-43503) via crafted AES-CBC encrypted payloads…
 epsilonpointori/epsilonpointlnk
Generates obfuscated .lnk files exploiting CVE-2026-21510 with LNK stomping, encrypted payloads, and anti-forensics for authorized penetration…
 gmh5225/dsark64
BYOVD proof-of-concept abusing the WHQL-signed DsArk64.sys driver for ring-0 process termination and kernel read/write via encrypted IOCTLs and…
 arthurhendrich/cve-2022-42475-poc
Exploit for CVE-2022-42475, a pre-auth RCE in FortiOS SSL VPN. Supports validation, benign verification, and full exploitation with connect-back…
 dionissh/cve-2024-21413
Proof-of-concept exploit for Microsoft Outlook RCE (CVE-2024-21413) with SMTP-based phishing email delivery, malicious RTF attachment generation, and…
 maxymgorn/cve-2025-59287-exploit-poc
Proof-of-concept exploit for CVE-2025-59287, a critical unauthenticated RCE in WSUS via unsafe BinaryFormatter deserialization, achieving SYSTEM…
 ekkoo-z/cve-2019-18935-bypasswaf
Exploit for CVE-2019-18935 (Telerik UI) with WAF bypass via encrypted cookie payload injection and custom memory shell deployment.
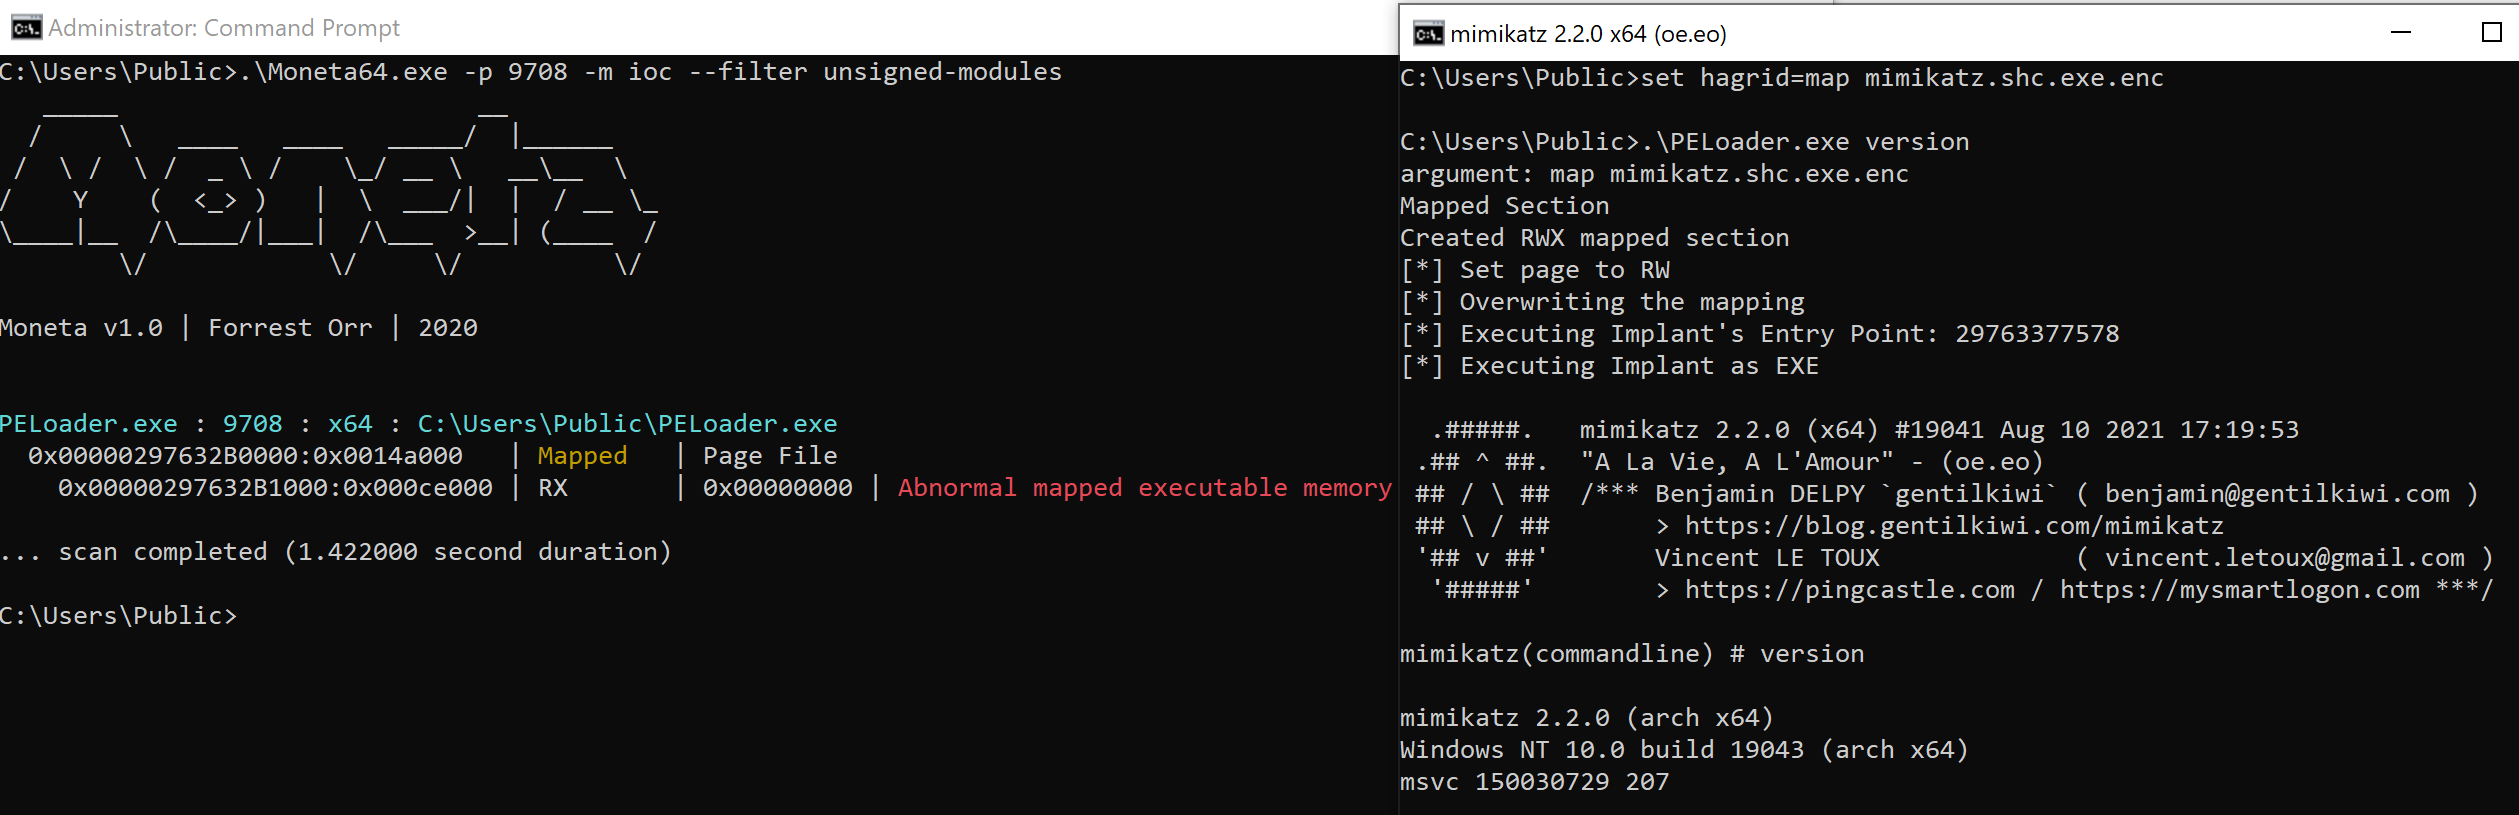 hagrid29/peloader
PE loader with various shellcode injection techniques
 jfmaes/sharpziprunner
Executes position independent shellcode from an encrypted zip