
ModSecurity
 owasp-modsecurity/modsecurity
ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
anti-botapi-securitydefensive-tools+7
9.7k
owasp-modsecurity/modsecurityModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
 baguette168/nmg
Generates parameterized .NET memory-shell payloads (VPP, MVC route, HttpListener) compatible with Godzilla, Behinder, and AntSword clients for red…
 holo-routing/holo
Rust-based routing protocol suite implementing BGP, OSPF, IS-IS, RIP, and VRRP with YANG-modeled configuration, gNMI/gRPC automation, and built-in…
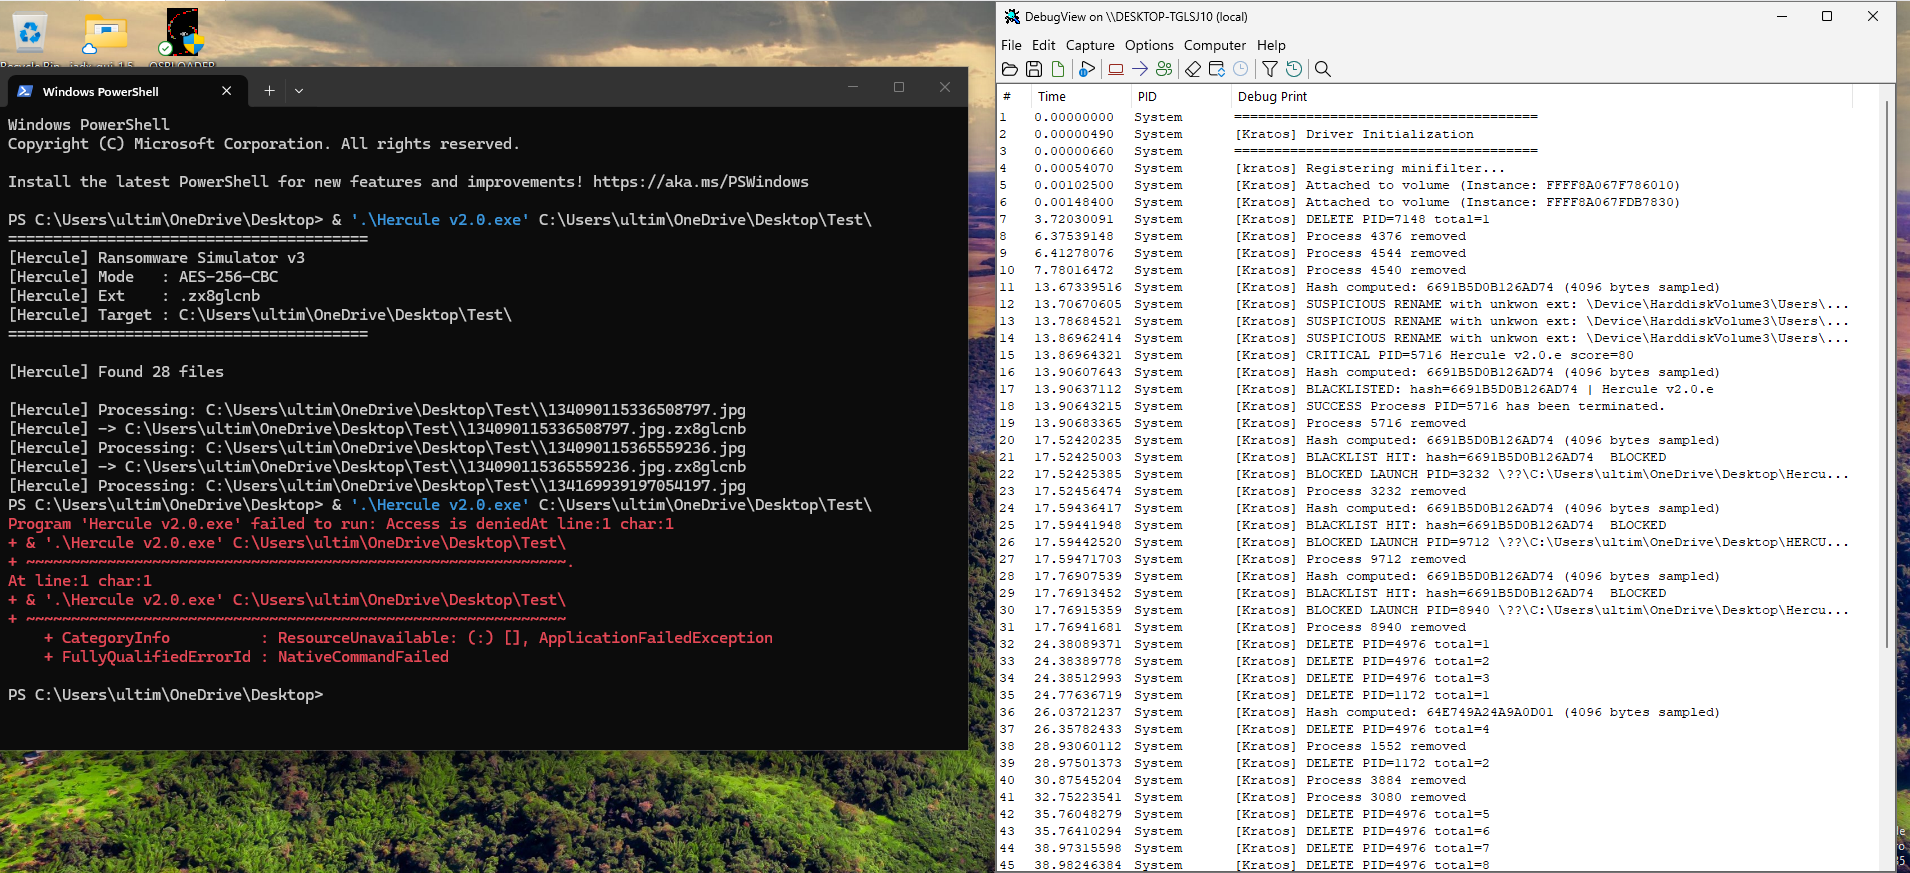 mukendi/kratosminifilter
Kratos Minifilter is a Windows kernel driver (FLTMGR.SYS) built for real-time ransomware detection and file I/O mitigation. It intercepts low-level…

 berraesen/nextjs-middleware-auth-bypass-lab
Bu laboratuvar ortamını sıfırdan kendim oluşturdum. Next.js uygulaması içerisinde giriş, ana sayfa ve admin sayfalarını hazırladım. Middleware ile…
 admin2099/penetration-testing-assessment-23-04-2026
Penetration testing assessment of a vulnerable IIS 6.0 WebDAV server, demonstrating reconnaissance, enumeration, exploitation (CVE-2017-7269), and…
 renzi25031469/cve-2026-49975-http-2-bomb
Disclosed on June 3, 2026, the "HTTP/2 Bomb" is an unauthenticated remote DoS that combines an HPACK compression bomb with a Slowloris-style hold to…
 danops-1/gpt-agreement-payment
ChatGPT Plus/Team/Pro 订阅协议端到端重放工具集 · hCaptcha 视觉求解器 · 反欺诈机制实证研究 / End-to-end protocol replay toolkit for ChatGPT Plus/Team/Pro subscription with…
 atiilla/cve-2026-42897
CVE-2026-42897 - Exchange Health Checker blind spot: outbound IIS URL Rewrite rules silently ignored, making EOMT mitigations invisible in diagnostic…
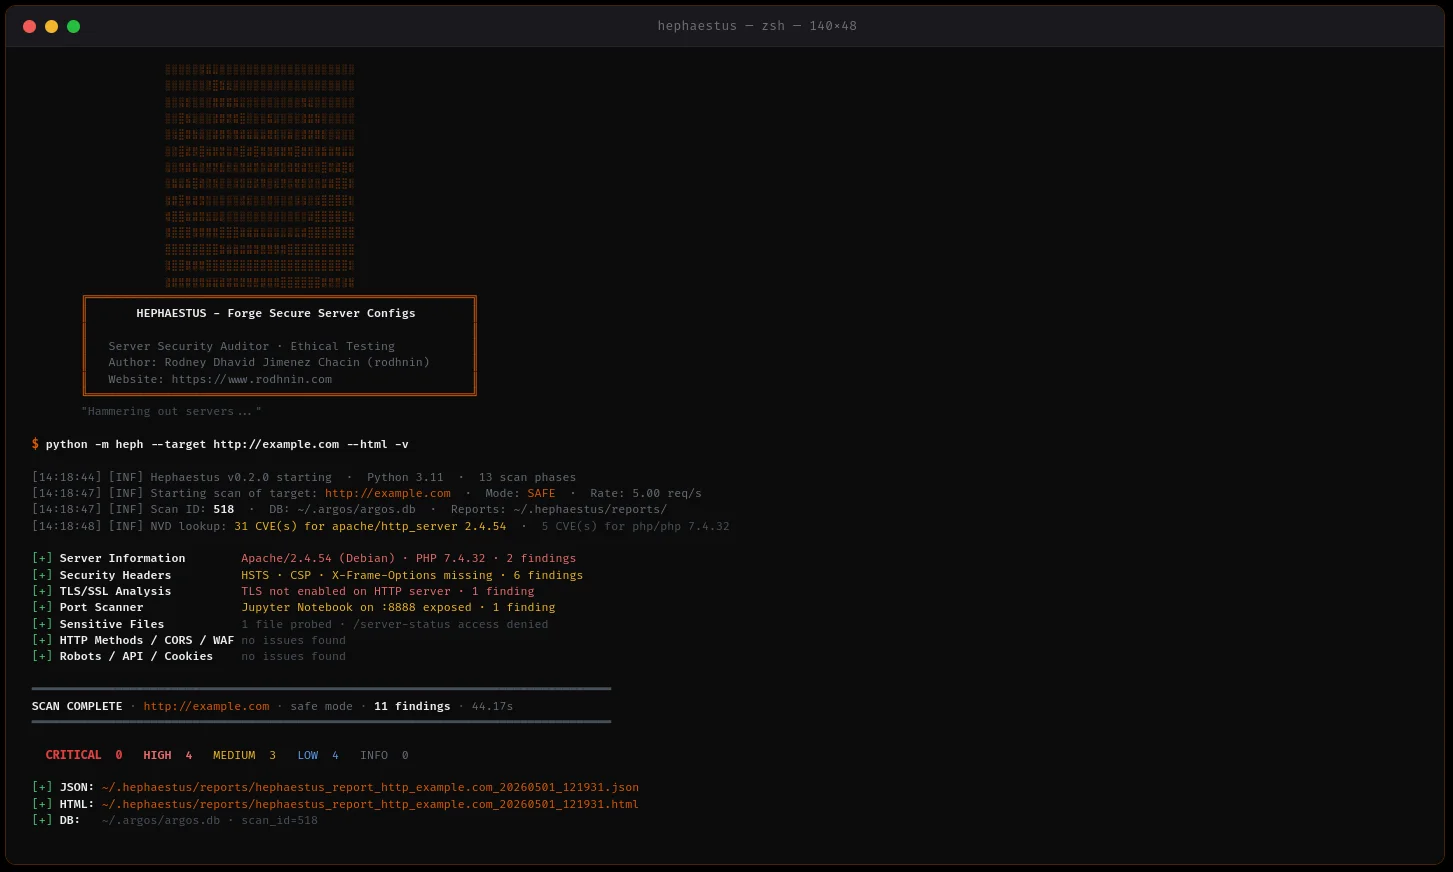 rodhnin/hephaestus-server-forger
server security auditor scanning Apache, Nginx, and IIS configurations with AI-powered hardening guides and professional reporting.
 justjeff211/conti-ransomware-writeup
Conducted a full SOC investigation into a Conti ransomware compromise of an Exchange server using Splunk 8.2.2. Analysed 28,145 events across Windows…
 hackingdave/btrpa-scan
Bluetooth Low Energy (BLE) scanner with Resolvable Private Address (RPA) resolution using Identity Resolving Keys (IRKs)
 boroeurnprach/ashwesker-cve-2026-21962
Exploit PoC and Nuclei template for CVE-2026-21962, a critical unauthenticated remote code execution in Oracle HTTP Server and WebLogic Proxy…
 killian0713/assignement_3-cve-2017-7269
Educational exploit reproduction of CVE-2017-7269, a buffer overflow in IIS 6.0 WebDAV, with setup guide, vulnerability analysis, and Metasploit…
 saykino/cve-2025-66838
Documentation of CVE-2025-66838: a rate-limiting vulnerability in ARIS file upload API allowing authenticated remote attackers to cause denial of…
 saykino/cve-2025-66837
Technical documentation and proof-of-concept for CVE-2025-66837, a remote authenticated file upload vulnerability in ARIS allowing arbitrary code…
 zach115th/toolshellfinder
Scans Windows IIS logs for signs of CVE-2025-53770 & CVE-2025-53771