
de4py
 fadi002/de4py
The ultimate AI-powered toolkit for python reverse engineering
ai-assisted-reversingbinary-analysiscode-analysis+6
fadi002/de4pyThe ultimate AI-powered toolkit for python reverse engineering
 anggatechi/cve-2026-3844
CVE-2026-3844 — Unauthenticated Arbitrary File Upload to RCE in Breeze Cache (WordPress). CVSS 9.8 CRITICAL. Mass scanner + auto shell injector with…
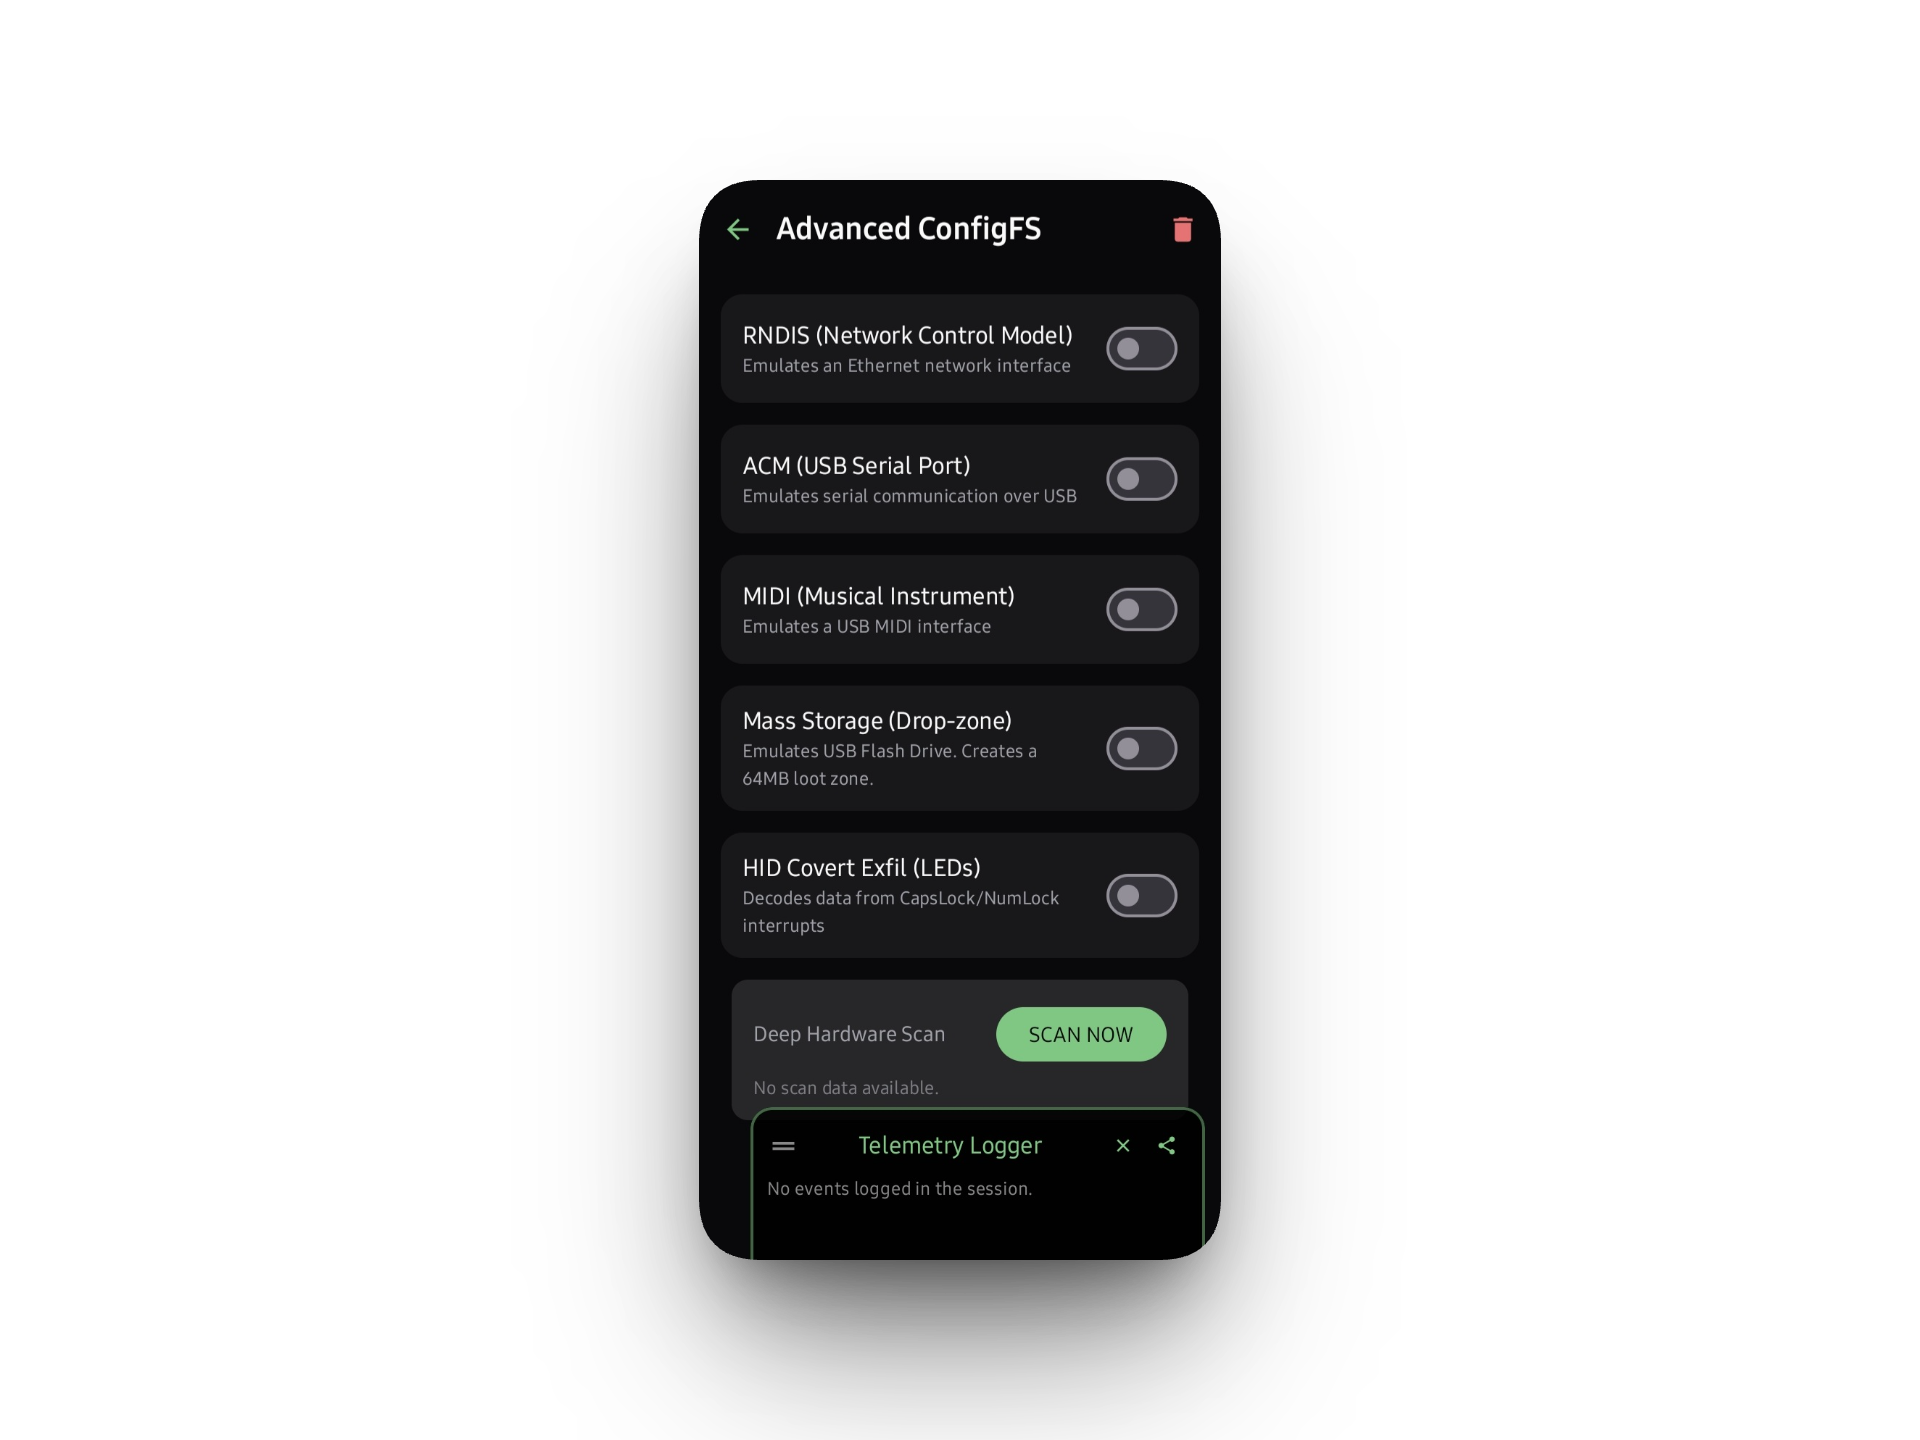 cipher-attack/chimera
Payload injector and HID emulator for Android like Hak5 and rubber ducky
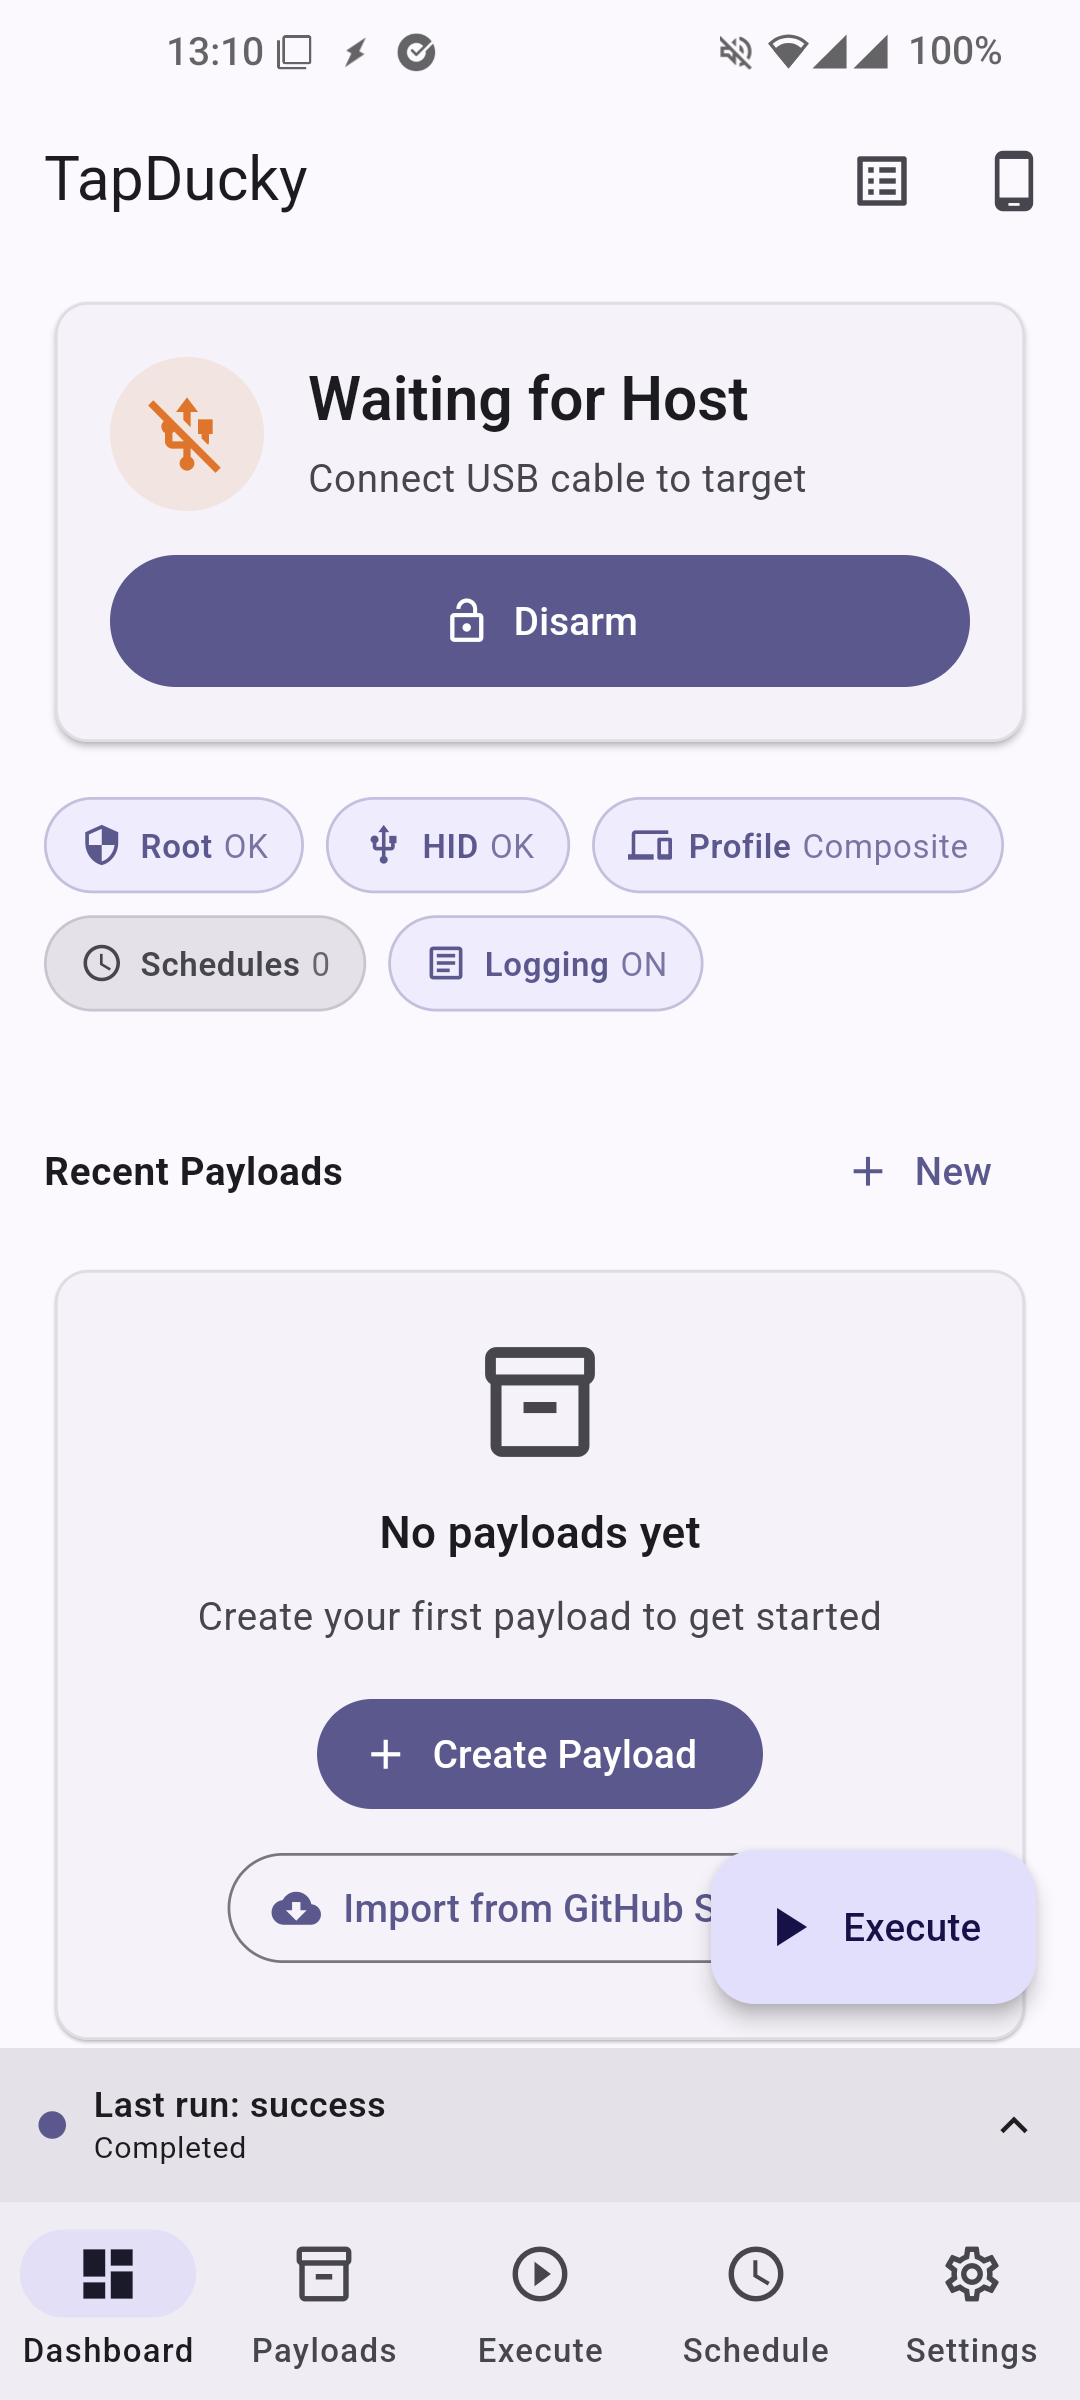 iodn/tap-ducky
Turns any rooted phone into the legendary USB Rubber Ducky. Android USB HID Keystroke Injector
 sensepost/dotnethookertoolkit
Frida-based .NET Framework injector and managed method hooking toolkit for runtime tracing, native entrypoint resolution, and dynamic analysis of…
 breadsquad/timeinjector
Time injector is a CVE-2018-14714 exploitation script
 deepinstinct/shimme
PoC for Windows privilege escalation and code injection using OfficeClickToRun RPC and undocumented shim manipulation to inject DLLs into SYSTEM…
 lleon1435/kernel_vadinjector
Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
 florylsk/recycledinjector
Native syscall shellcode injector using HellsGate/HalosGate/TartarusGate for undetectable execution, with external shellcode loading and EDR evasion…
 sighook/pixload
Image Payload Creating/Injecting tools
 magisterquis/chromecookiestealer
Steal/Inject Chrome cookies over the DevTools (--remote-debugging-port) protocol.
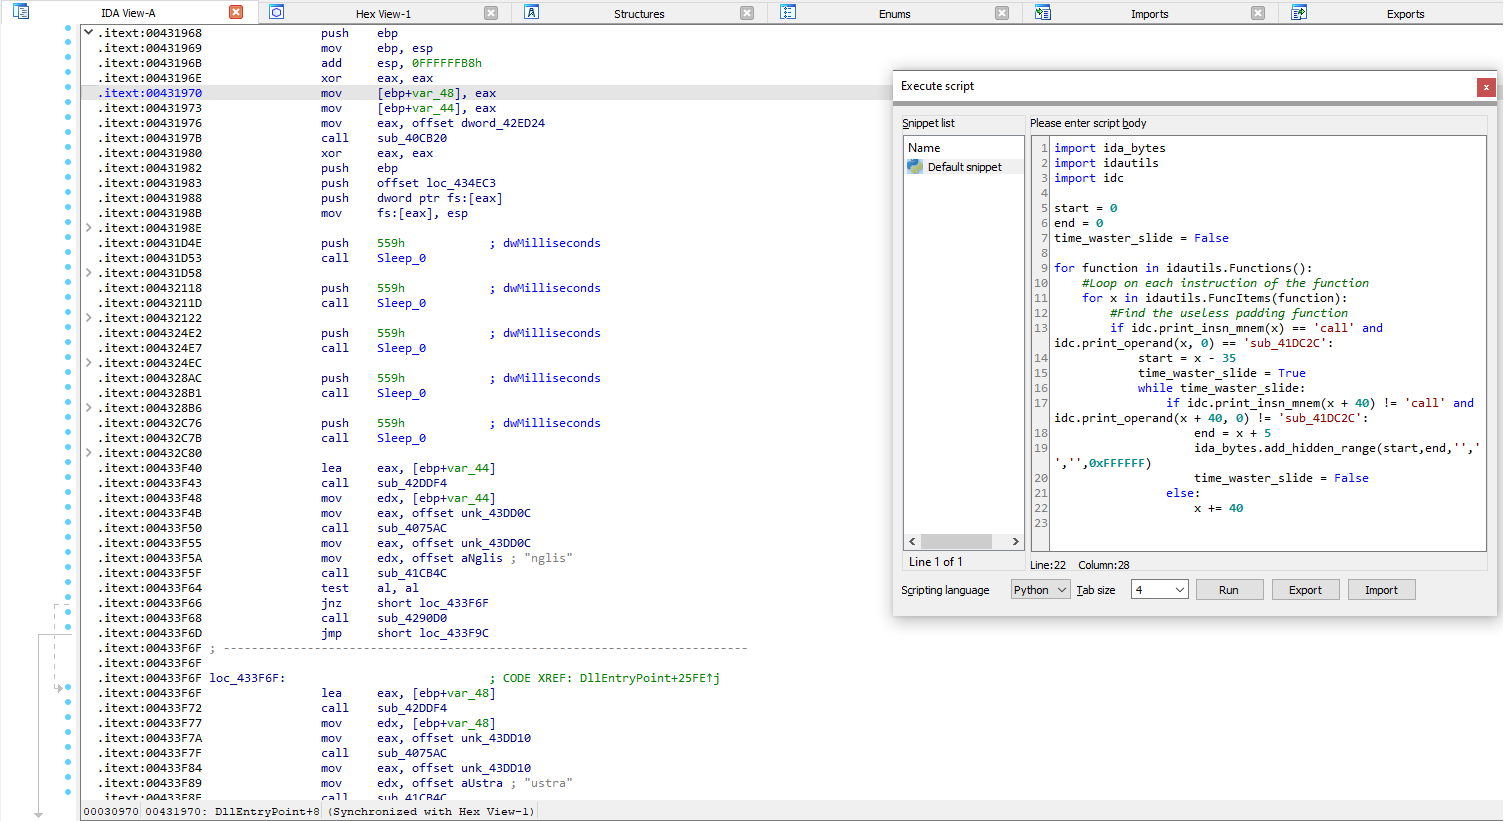 dodo-sec/astaroth-deobfuscator
IDA python script for deobfuscating Astaroth/Guildma injector DLL
 namazso/linux_injector
A simple ptrace-less shared library injector for x64 Linux
 carlospuenteg/file-injector
File Injector is a script that allows you to store any file in an image using steganography
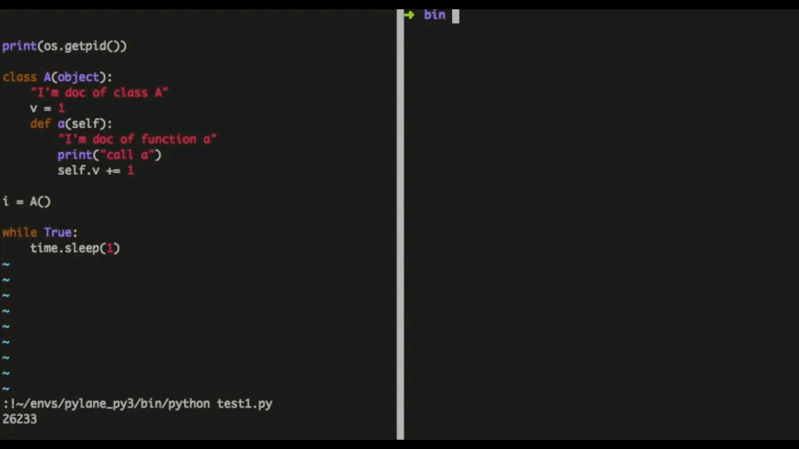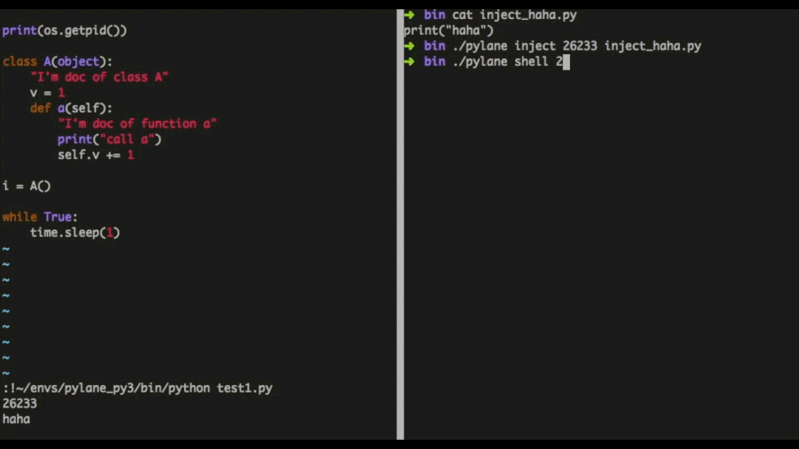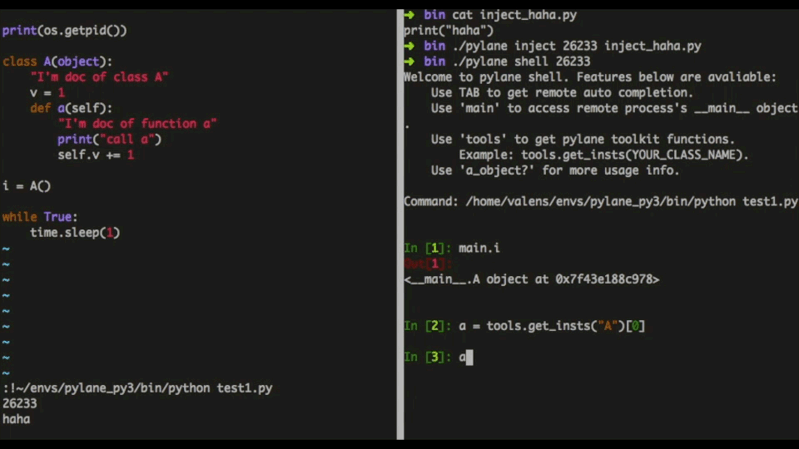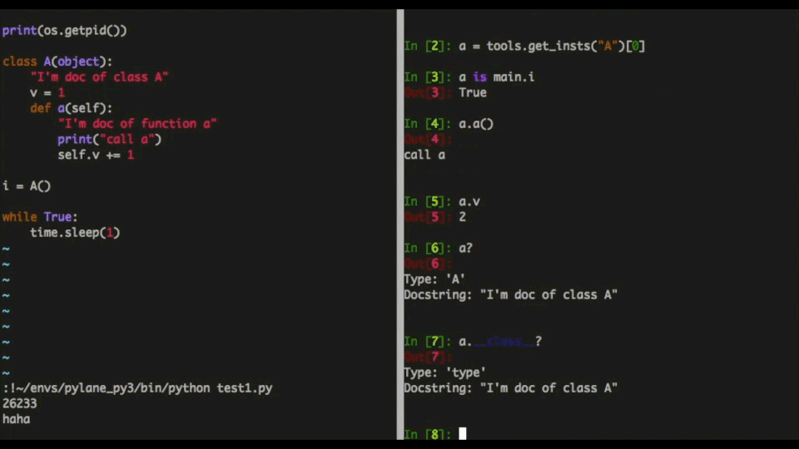 nteseyes/pylane
An python vm injector with debug tools, based on gdb.
 cerbersec/ares
Project Ares is a Proof of Concept (PoC) loader written in C/C++ based on the Transacted Hollowing technique
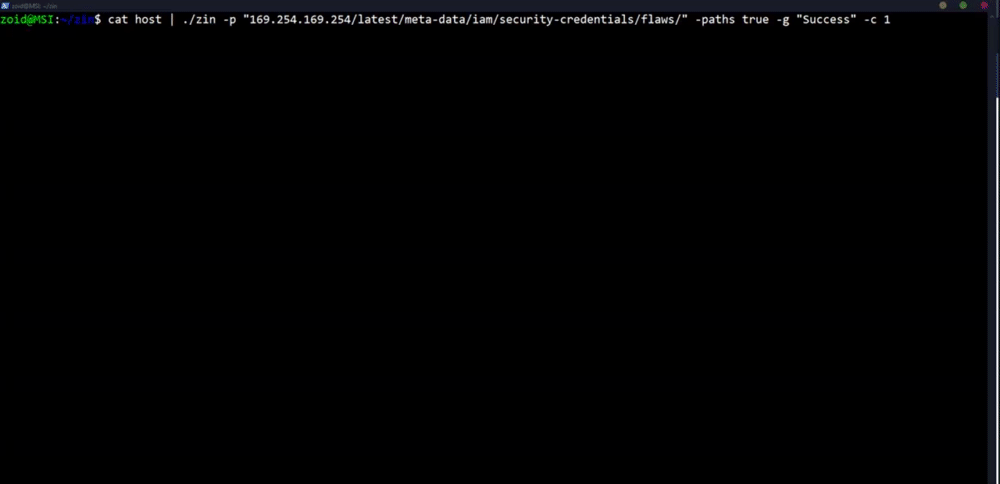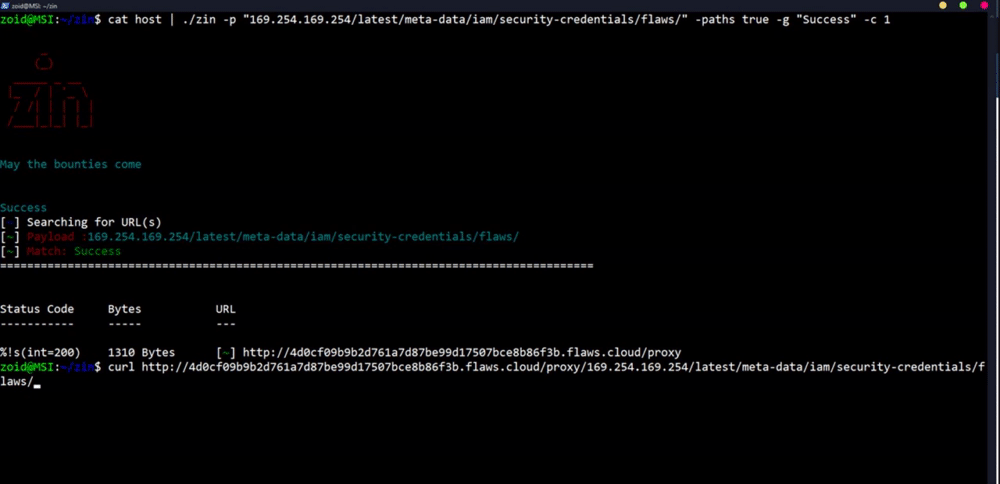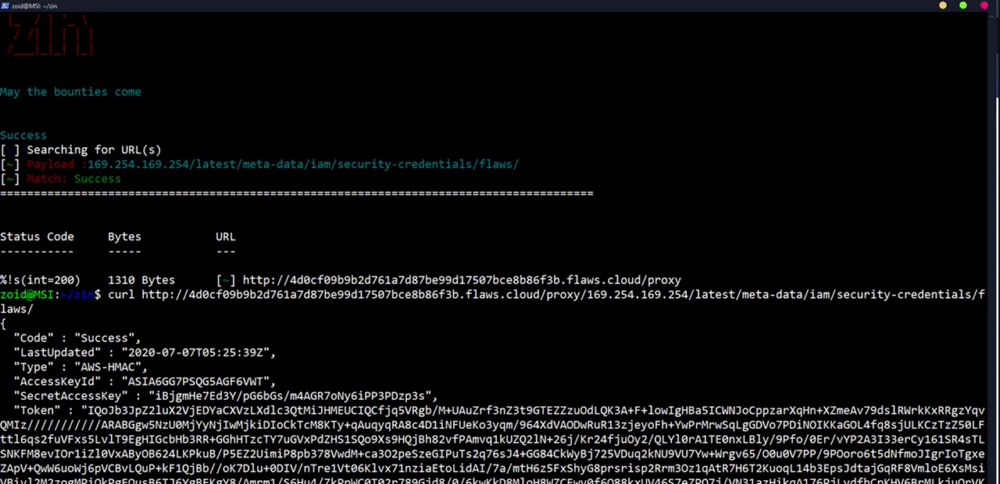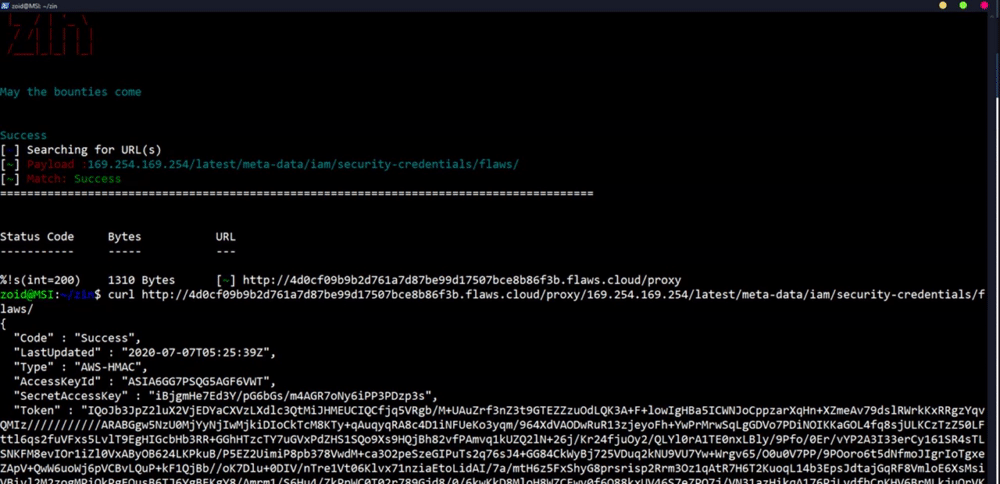 ethicalhackingplayground/zin
A Payload Injector for bugbounties written in go
 misje/dhcpoptinj
DHCP option injector