

coraza
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
api-securityapi-security-testingdefensive-tools+7
4.0k
corazawaf/corazaGo-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 go-appsec/toolbox
Collaborative application security testing between humans and agents via CLI and MCP
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 matrixleons/evilwaf
evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
 owasp/mastg
Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
 blacklanternsecurity/trevorproxy
A SOCKS proxy written in Python that randomizes your source IP address. Round-robin your evil packets through SSH tunnels or give them billions of…
 fkie-cad/sandroid_dexray-intercept
A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…
 juice-shop/juice-shop
Intentionally vulnerable web application covering OWASP Top 10 vulnerabilities for security training, CTF competitions, and penetration testing…
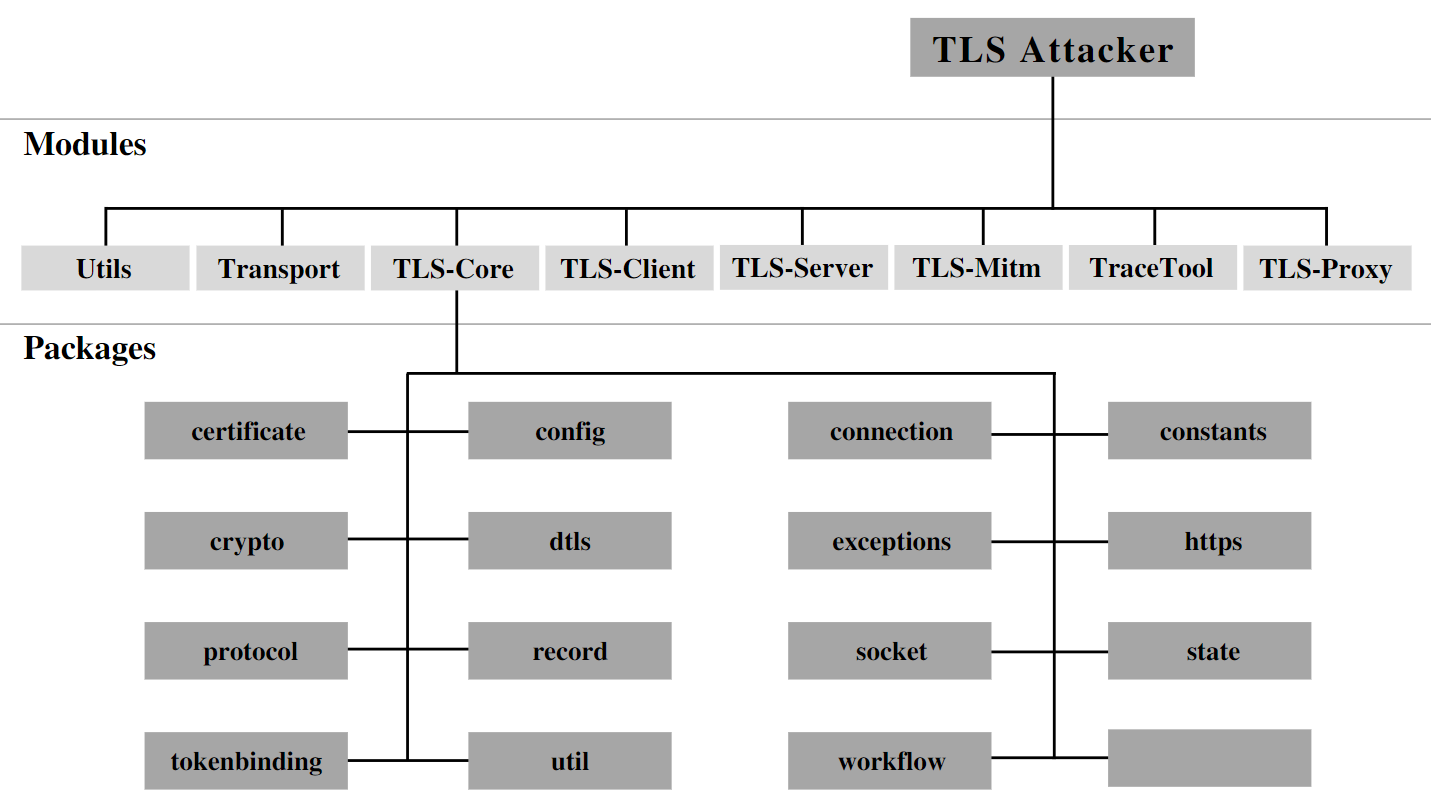 tls-attacker/tls-attacker
Java-based framework for systematic fuzzing and analysis of TLS libraries. Enables arbitrary protocol message crafting, modification, and testing of…
 zerodayevil/cve-2026-41940-poc
Proof-of-concept code demonstrating CVE-2026-41940, providing a reproducible test case for vulnerability verification and security research.
 zerodayevil/cve-2026-41096-poc
Proof-of-concept exploit for CVE-2026-41096, demonstrating the vulnerability and providing a reproducible test case for security researchers and…
 zerodayevil/cve-2026-40369-exploit
Proof-of-concept exploit code targeting CVE-2026-40369, demonstrating the vulnerability for research and authorized security testing.
 proviesec/xss-payload-list
Curated collection of cross-site scripting payloads, polyglots, and injection test rules for web application penetration testing and bug bounty…
 orevim/cve-2026-18963-poc
Proof of concept and vulnerability checker for CVE-2026-18963, an unauthenticated account takeover in the Keycloak reset-credentials flow.…