
my-cve-2021-4034-poc
 0x05a/my-cve-2021-4034-poc
Proof-of-concept exploit for CVE-2021-4034, a local privilege escalation in polkit's pkexec, demonstrating exploitation on Ubuntu systems.
exploitationexploit-frameworkspenetration-testing+2
0x05a/my-cve-2021-4034-pocProof-of-concept exploit for CVE-2021-4034, a local privilege escalation in polkit's pkexec, demonstrating exploitation on Ubuntu systems.
 wongwaituck/cve-2021-4034
Proof-of-concept exploit for CVE-2021-4034 (PwnKit) that escalates privileges to root on vulnerable Linux systems.
 ayypril/cve-2021-4034
Proof-of-concept exploit for CVE-2021-4034, a local privilege escalation in polkit's pkexec, demonstrating exploitation via GCONV_PATH manipulation.
 nikaiw/cve-2021-4034
Proof-of-concept exploit for CVE-2021-4034, a local privilege escalation vulnerability in polkit's pkexec, demonstrating exploitation for security…
 audiobahn/cve-2021-4034
Local privilege escalation exploit for CVE-2021-4034 targeting pkexec, providing proof-of-concept code for security testing and research.
 01rabbit/pakuri
Semi-automated penetration testing framework with TUI, integrating Nmap, OpenVAS, Metasploit, and Faraday for streamlined information gathering,…
 glowbase/cve-2019-19609
Python exploit script targeting unauthenticated remote code execution in Strapi CMS 3.0.0-beta.17.4 via CVE-2019-18818 and CVE-2019-19609, delivering…
 0x36/ghidra_kernelcache
a Ghidra framework for iOS kernelcache reverse engineering
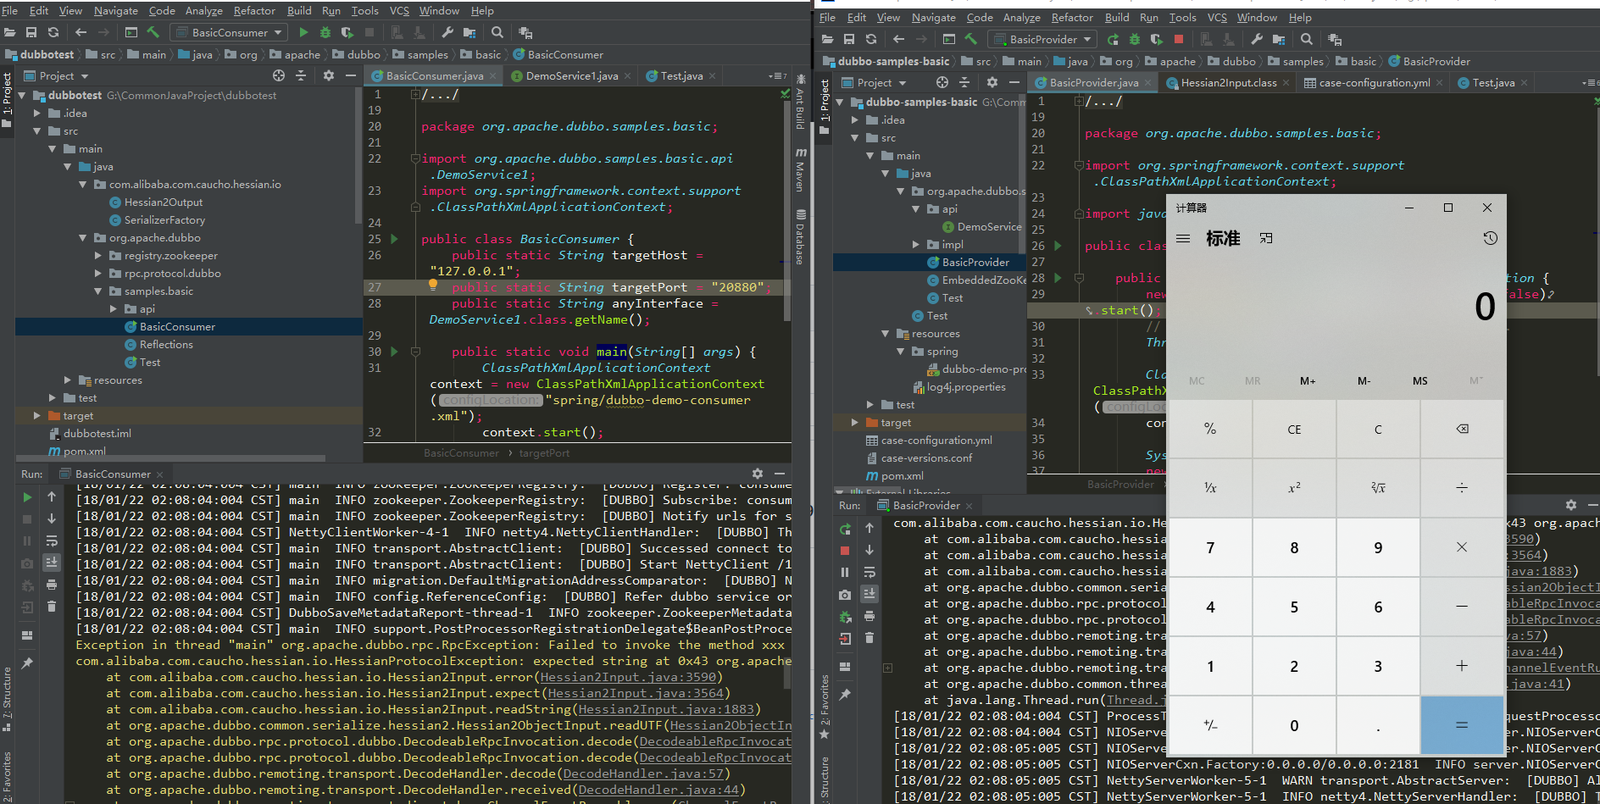 longofo/apache-dubbo-hessian2-cve-2021-43297
Demonstrates a proof-of-concept exploit for CVE-2021-43297, a deserialization vulnerability in Apache Dubbo's Hessian2 protocol, with provider and…
 bishopfox/cve-2021-35211
Python exploit for Serv-U SSH vulnerability (CVE-2021-35211) with multiple payload modes: stage, exec, and download-execute, enabling shellcode…
 aazhuliang/cve-2021-31956-exp
Exploit for CVE-2021-31956, a Windows kernel privilege escalation vulnerability, targeting Windows 10 1903. Provides a proof-of-concept…
 boyan-milanov/ropium
Automated ROP chain builder that extracts and analyzes gadgets from binaries using semantic queries, supporting X86/X64 architectures with a Python…
 ioactive/laf
This project intends to provide a series of tools to craft, parse, send, analyze and crack a set of LoRaWAN packets in order to audit or pentest the…
 andrewtrube/cve-2012-2593
Atmail XSS-CSRF-RCE Exploit Chain
 nate0634034090/nate158g-m-w-n-l-p-d-a-o-e
### This module requires Metasploit: https://metasploit.com/download# Current source: https://github.com/rapid7/metasploit-framework##class…
 marklindsey11/gh-repo-clone-marklindsey11--cve-2021-44228_scanner-applications-that-are-vulnerable-to-the-log4j-cv
Scans applications for the Log4Shell vulnerability (CVE-2021-44228) to identify systems at risk of remote code execution.
 taroballzchen/cve-2021-44228-log4jvulnscanner-metasploit
open detection and scanning tool for discovering and fuzzing for Log4J RCE CVE-2021-44228 vulnerability
 34zy/microsoft-office-word-mshtml-remote-code-execution-exploit
Exploits CVE-2021-40444 in Microsoft Office Word to achieve remote code execution through the MSHTML engine by injecting malicious content into a…