

lsawhisper-bof
 dazzyddos/lsawhisper-bof
A Beacon Object File (BOF) that talks directly to Windows authentication packages through the LSA untrusted/trusted client interface, without…
authenticationcommand-and-controlexploitation+4
296
dazzyddos/lsawhisper-bofA Beacon Object File (BOF) that talks directly to Windows authentication packages through the LSA untrusted/trusted client interface, without…
 estebanzarate/cve-2025-4517-python-tarfile-filter-data-bypass-poc
Proof-of-concept exploit for CVE-2025-4517, a path traversal vulnerability in Python's tarfile filter='data' sandbox, enabling arbitrary file writes…
 bgutowski/cve-2025-4517-poc-sudoers
Exploit for CVE-2024-6232 - Python Tarfile Realpath Overflow
 hvictor/shellcode-x64
Shellcodes for Windows >= 11 x64
 0p5cur/cve-2025-32462-poc
🔓 Local privilege escalation PoC for CVE-2025-32462 (sudo -h bypass) – gain root via misconfigured sudoers
 sliverarmory/malasada
Linux Shared Library to Shellcode Loader
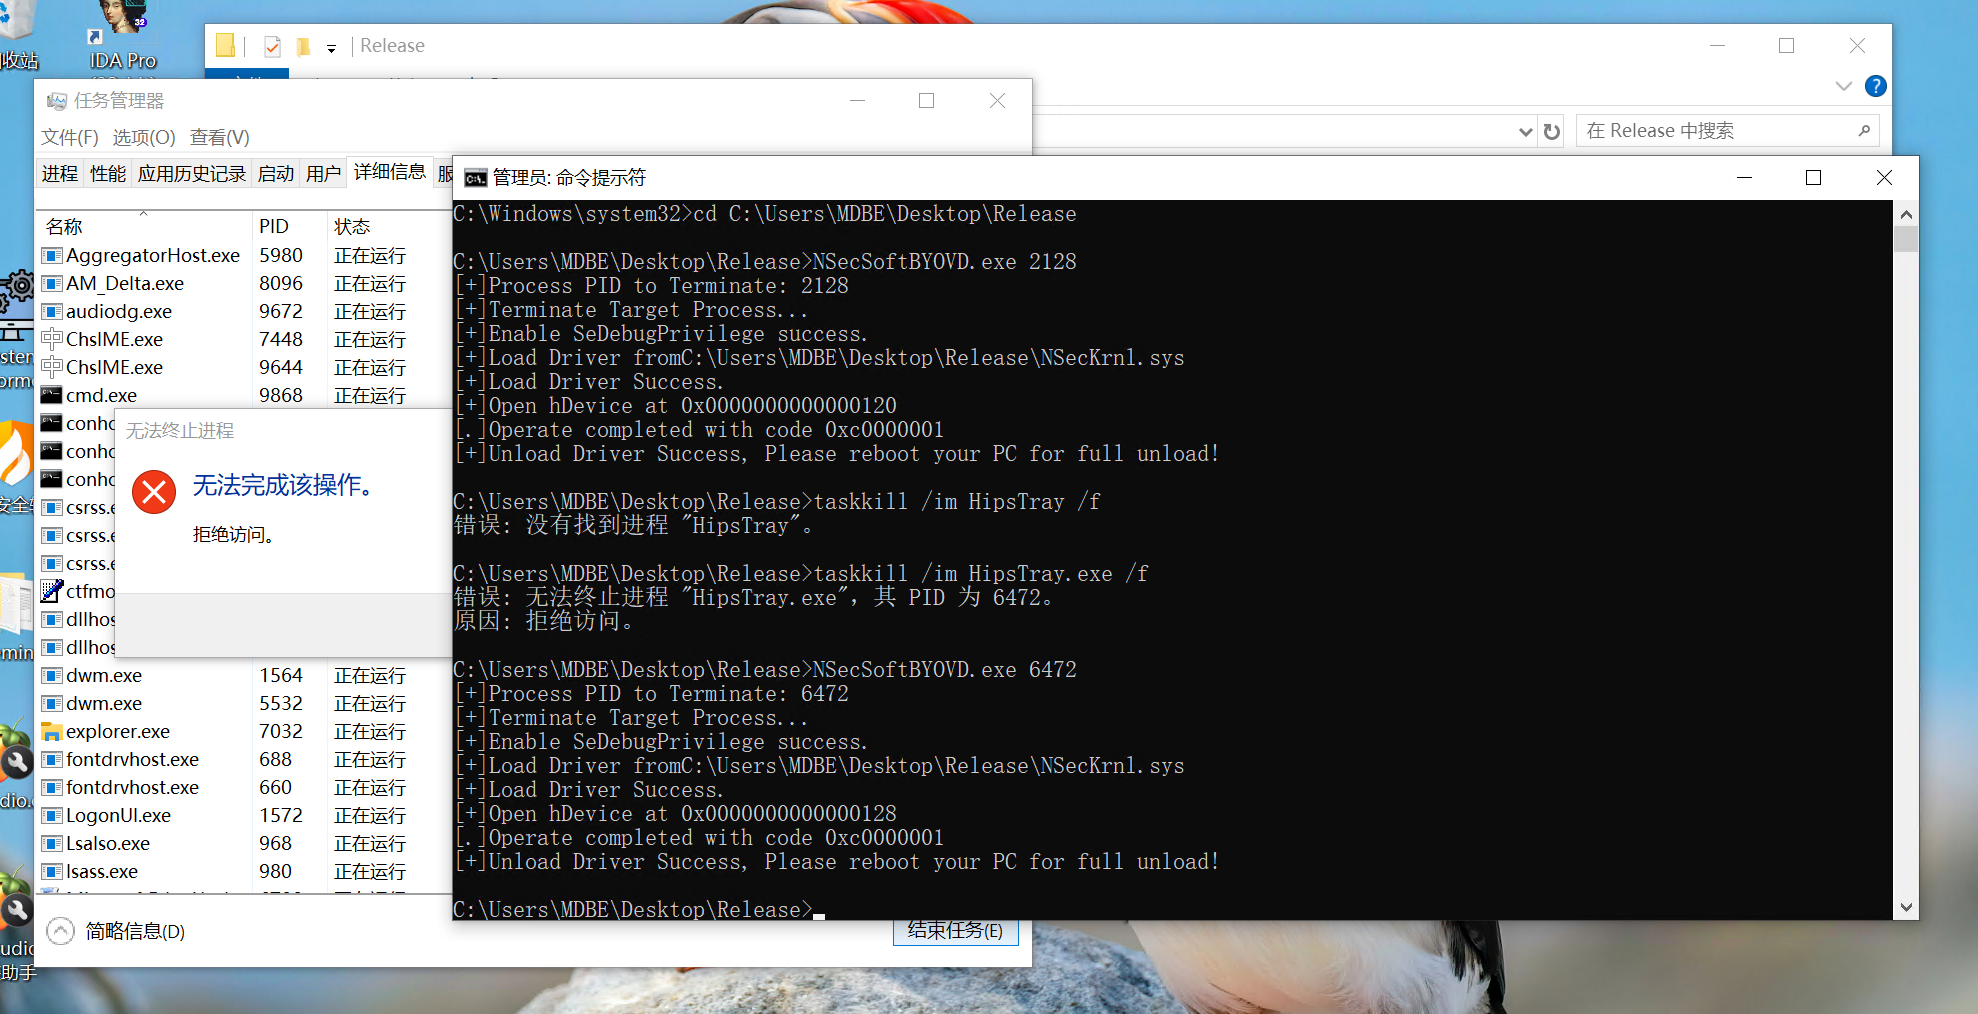
 joaoviictorti/rustbof
A Rust template for writing Beacon Object Files (BOFs)
 0xc4r/cve-2026-21508_poc
Proof-of-concept for CVE-2026-21508, demonstrating a DLL hijacking attack on Windows 11 that escalates privileges by loading a crafted DLL into…
 epsilonpoint88-glitch/epsilonpoint-
Modular exploit framework targeting CVE-2026-23550 in WordPress, featuring mass exploitation, obfuscation, post-exploitation, and Docker-based C2…
 hackerhouse-opensource/backdoors
Tools for maintaining access to systems and proof-of-concept demonstrations.
 hackerhouse-opensource/nofaxgiven
Code Execution & Persistence in NETWORK SERVICE FAX Service
 hackerhouse-opensource/iscsicpl_bypassuac
UAC bypass for x64 Windows 7 - 11
 hackerhouse-opensource/cve-2021-34527
CVE-2021-34527 AddPrinterDriverEx() Privilege Escalation
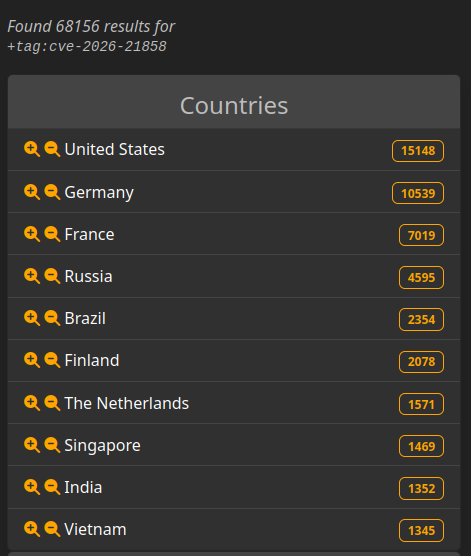 alhakim88/cve-2026-21858
Automated exploit chain for n8n combining arbitrary file read, admin token forgery, and sandbox bypass to achieve unauthenticated remote code…
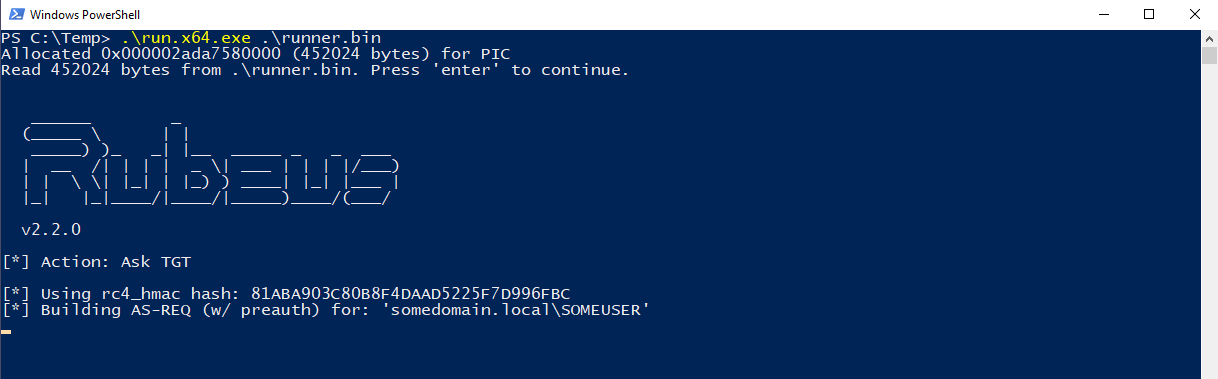 ofasgard/execute-assembly-pico
A PICO for Crystal Palace that implements CLR hosting to execute a .NET assembly in memory.
 hackinglz/cve-2025-27237
CVE 2025 27237 Zabbix LPE proof of concept.
 tralsesec/cve-2024-0670
CheckMK Agent Local Privilege Escalation (PoC)