

EDRception
 malwaretech/edrception
A proof of concept for abusing exception handlers to hook and bypass user mode EDR hooks.
defensive-toolsexploitationids-ips-evasion+3
1992 years ago
malwaretech/edrceptionA proof of concept for abusing exception handlers to hook and bypass user mode EDR hooks.
 gmh5225/bedaisy-bypass
Kernel-mode hook that intercepts, decrypts, and nullifies BEDaisy-to-service report traffic to suppress anti-cheat detection on UEFI and non-UEFI…
 zer0condition/reversekit
x64 Dynamic Reverse Engineering Toolkit
 pietroborrello/customprocessingunit
The first analysis framework for CPU microcode
 rad9800/hwbp4mw
Hardware breakpoint hooking engine for Windows that uses debug registers to hook functions, bypass ETW/AMSI, and evade user-land EDR monitoring.
 aetsu/neton
Agent-based tool that collects OS, hardware, file, and hook data from internet-connected sandboxes via HTTPS exfiltration, aiding Red Team artifact…
 gmh5225/iat-hook
C++ DLL that performs Import Address Table hooking by parsing PE headers and redirecting imported function addresses to a custom hook inside a target…
 jbaines-r7/hook
Proof of Concept for WatchGuard Authenticated Arbitrary File Read (CVE-2022-31749)
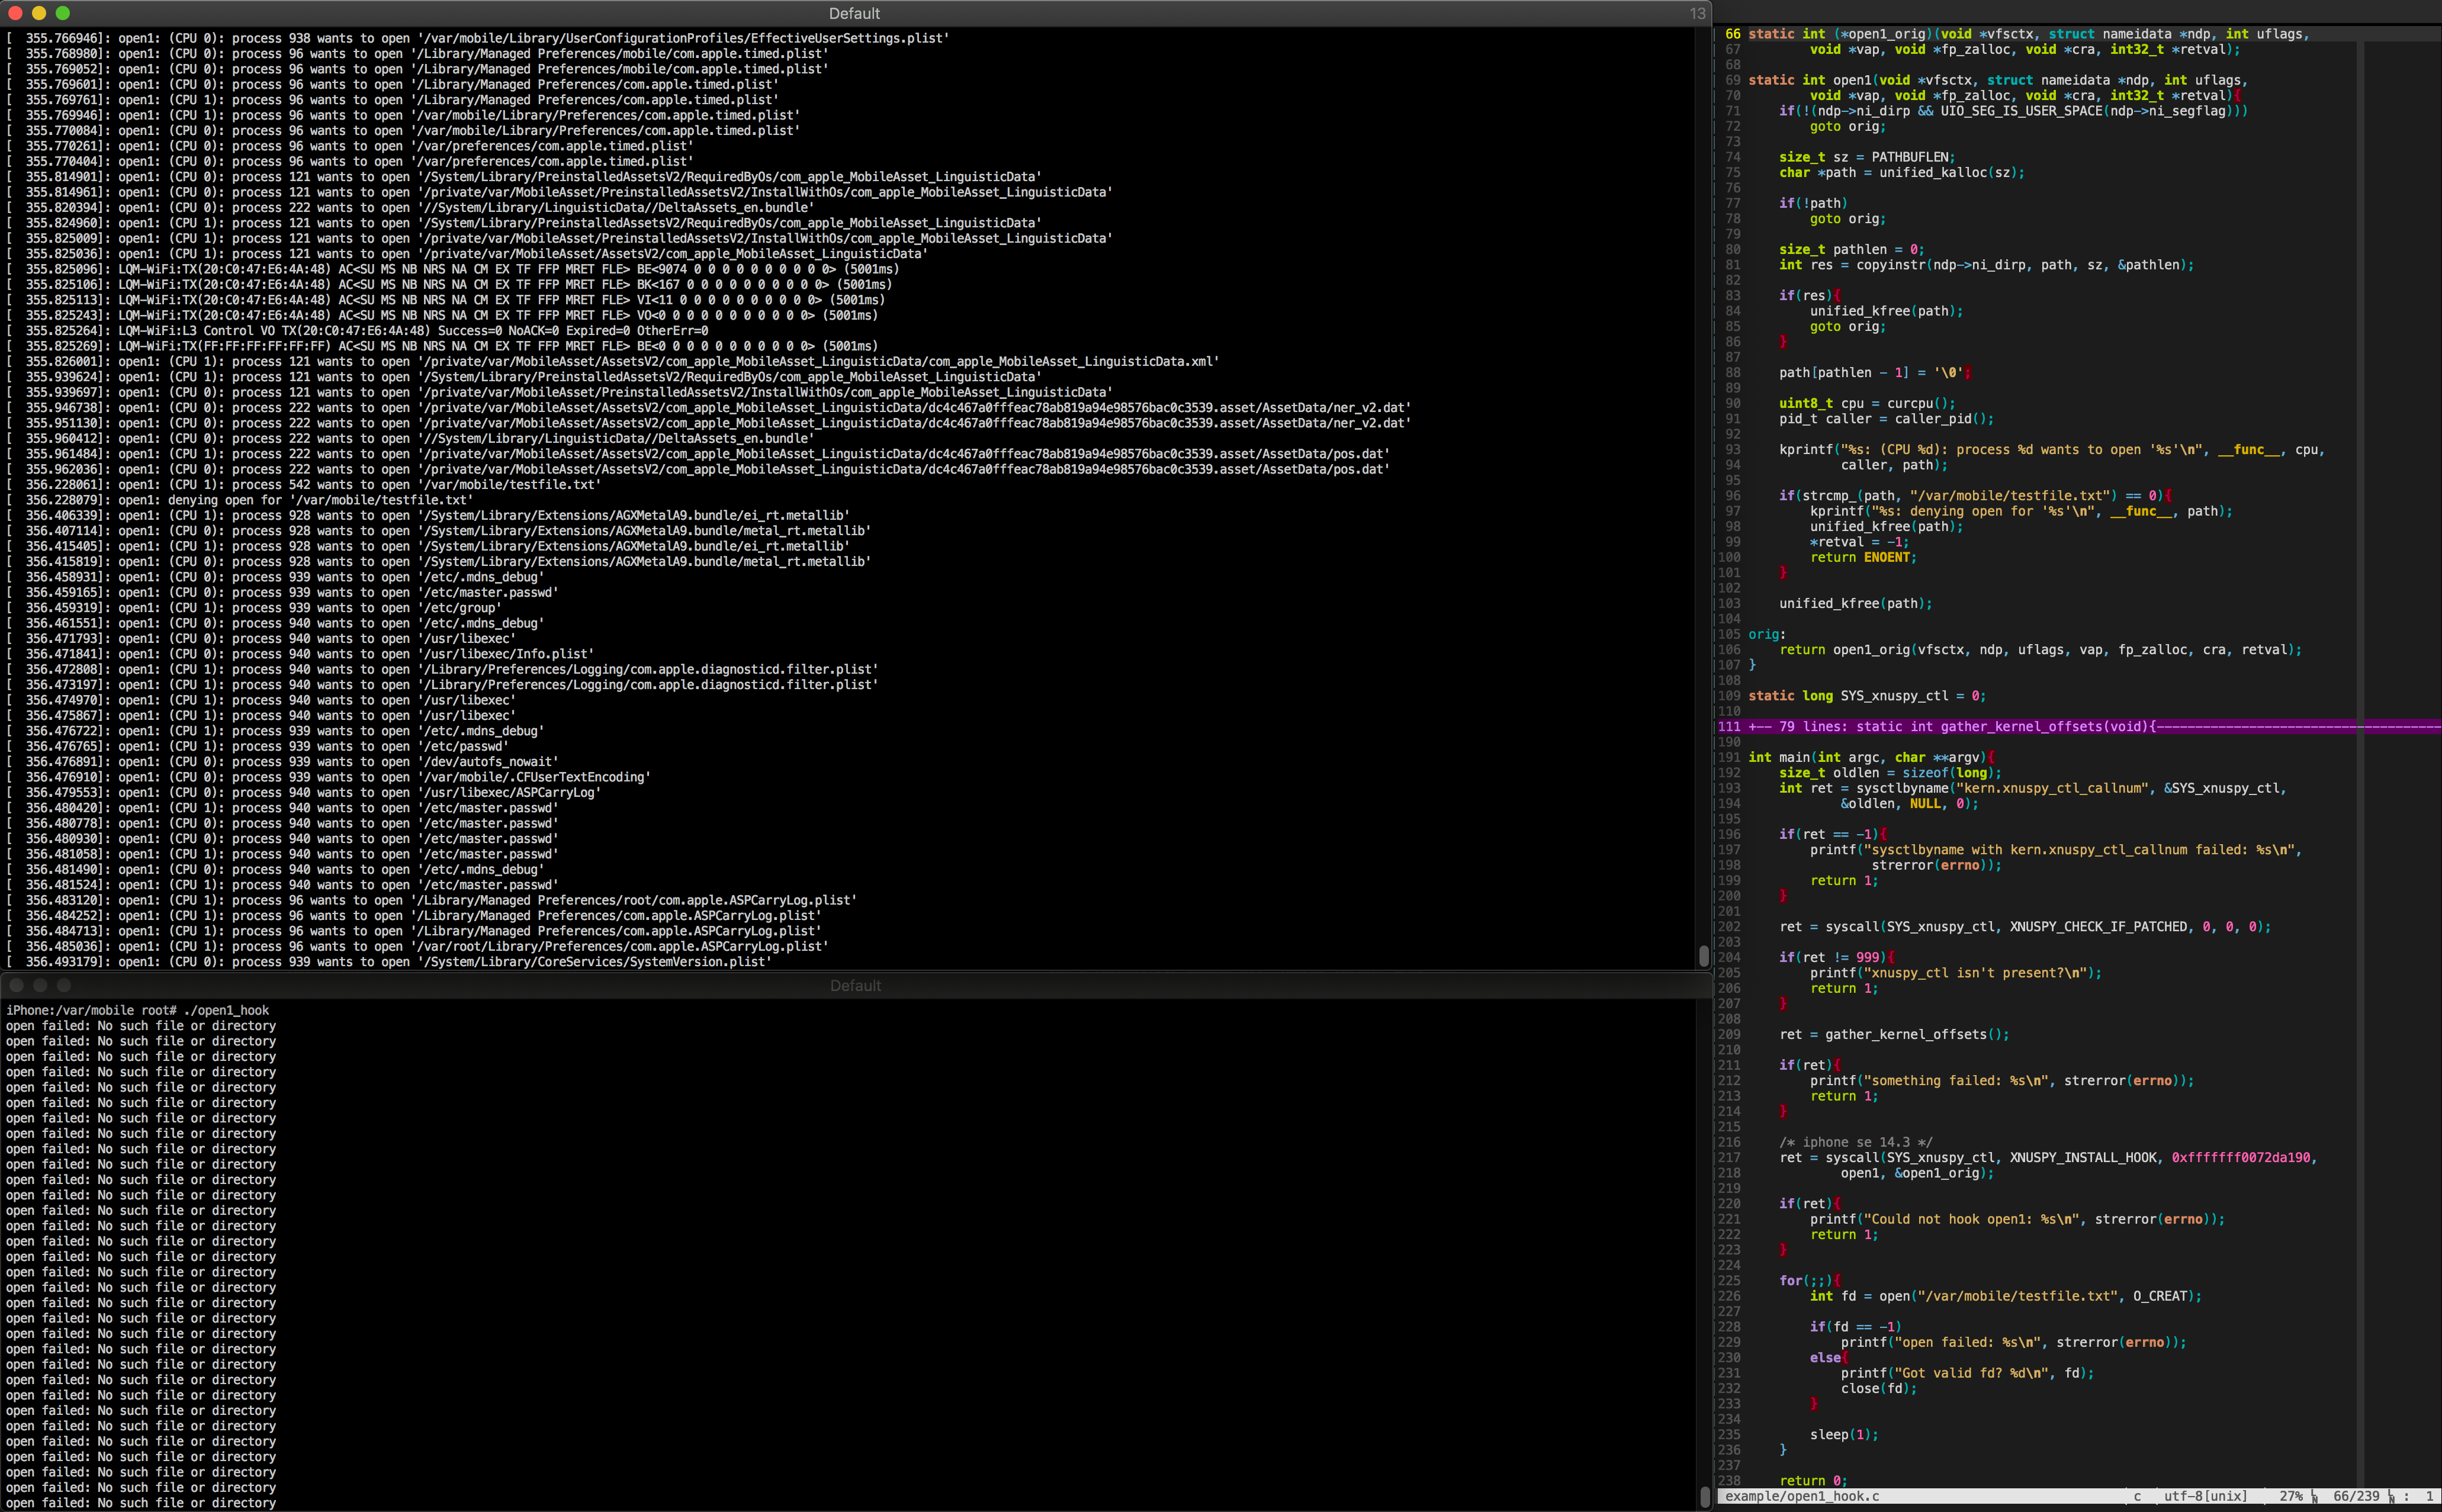 jsherman212/xnuspy
an iOS kernel function hooking framework for checkra1n'able devices
 t43wiu6/cve-2019-0887
exp for CVE-2019-0887
 al1ex/hook-passwordchangenotify
Hook PasswordChangeNotify
 hasan-khalil/cve-2020-6514
Exploit for CVE-2020-6514 targeting WebRTC SCTP memory corruption in Android applications. Uses Frida to hook native functions and alter SCTP packets…
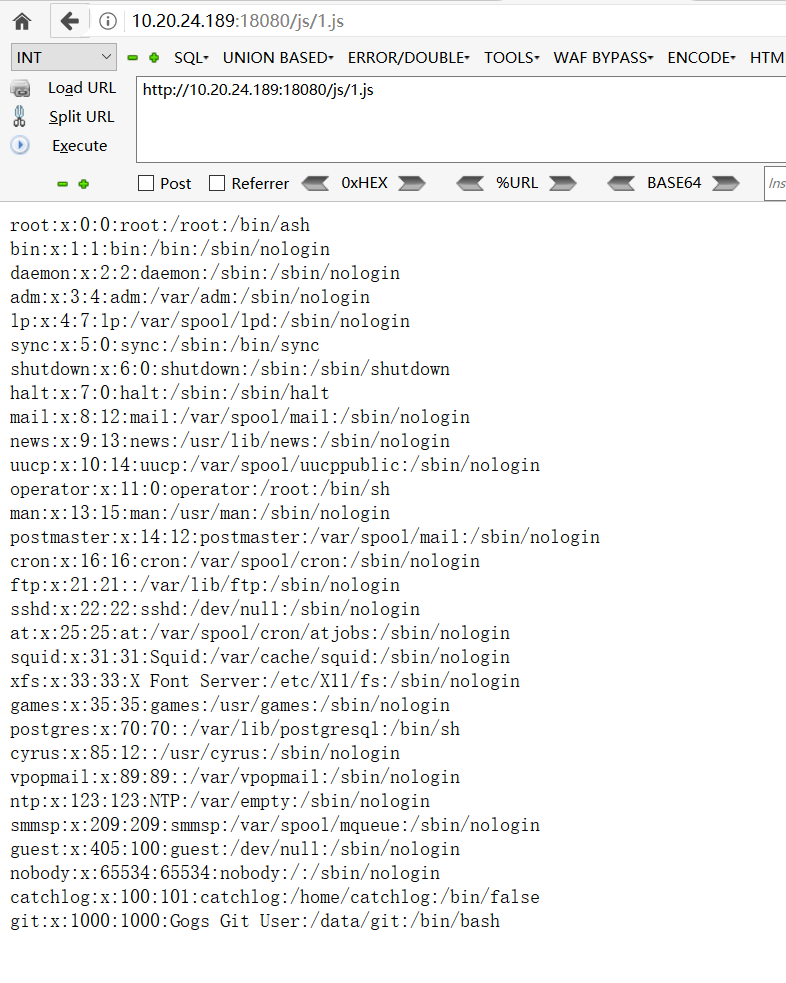 jas502n/gogs_rce
Exploit for Gogs RCE (CVE-2018-18925) leveraging session forgery and Git hook injection to achieve arbitrary command execution with root privileges.
 bats3c/ghost-in-the-logs
Kernel-level tool to disable Sysmon and Windows Event Logging via driver-based hook injection, enabling stealthy post-exploitation operations on…
 humoud/hooketh
A set of scripts that ease working with frida
 nishitm/gobox
GO sandbox to run untrusted code
 andripwn/cve-2018-18852
CERIO RCE CVE-2018-18852, authenticated (vendor defaults) web-based RCE as root user.