How-To-Secure-A-Linux-Server

Step-by-step guide for hardening a Linux server, covering SSH security, firewalls, intrusion detection, auditing, and system configuration to reduce…

Step-by-step guide for hardening a Linux server, covering SSH security, firewalls, intrusion detection, auditing, and system configuration to reduce…

Simple and flexible tool for managing secrets

WordPress plugin Welcart e-Commerce < 2.8.5 - Arbitrary File Read

Proof-of-concept for stored XSS in RISE CRM item title field (CVE-2026-36392), demonstrating session hijacking and account takeover with remediation…

Go-based CLI tool that scans codebases for launch readiness, detecting missing configuration, security hygiene issues, secret leaks, and integration…

Intentionally vulnerable PHP/MariaDB web application for practicing common web security vulnerabilities across multiple difficulty levels in a legal,…

Multi-cloud security posture scanner that audits AWS, Azure, GCP, and OCI for misconfigurations, compliance violations (HIPAA, PCI, CIS), and…

Exploit for CVE-2026-81780: unauthenticated file upload in WordPress Hash Form plugin leading to remote code execution via crafted PHP payloads.

Web Application Security Scanner

Exploit for CVE-2025-55182, a React2Shell vulnerability, providing proof-of-concept code to demonstrate remote code execution.

my poc for CVE-2026-53787

Git diff for SBOMs—compare CycloneDX, SPDX, and Syft documents, detect tampering, and gate CI.

Keycloak: Unauthorized organization registration via improper invitation token validation

Proof-of-concept exploit for CVE-2026-18963, a Keycloak reset-credentials bypass leading to account takeover. Demonstrates the vulnerability and…

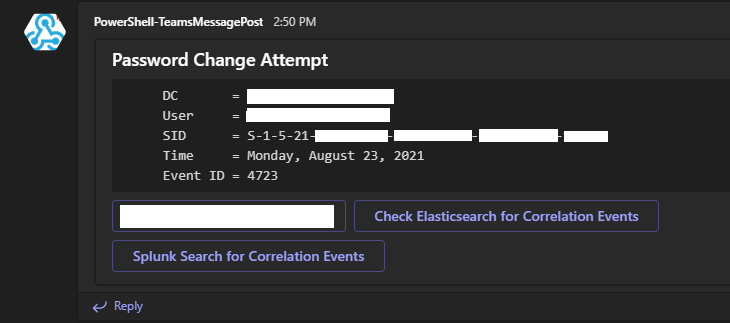
PowerShell-based security toolkit for small-to-medium enterprises, providing automated alerts, Active Directory hardening, Windows Event Forwarding,…

a reflected XSS vulnerability in YesWiki's Bazar widget handler.

Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.

Proof-of-concept exploit for CVE-2025-3248, a remote code execution vulnerability in Langflow, demonstrating exploitation of the vulnerable endpoint.