
Archived
wwwgrep
 owasp/wwwgrep
OWASP Foundation Web Respository
code-analysisinformation-gatheringpenetration-testing+3
36
 assetnote/batchql
GraphQL security auditing script with a focus on performing batch GraphQL queries and mutations
 mthbernardes/artlas
Apache Real Time Logs Analyzer System
 owasp/application-security-curriculum
Structured curriculum for learning application security, covering secure coding, threat modeling, and DevSecOps practices. Designed for self-paced…
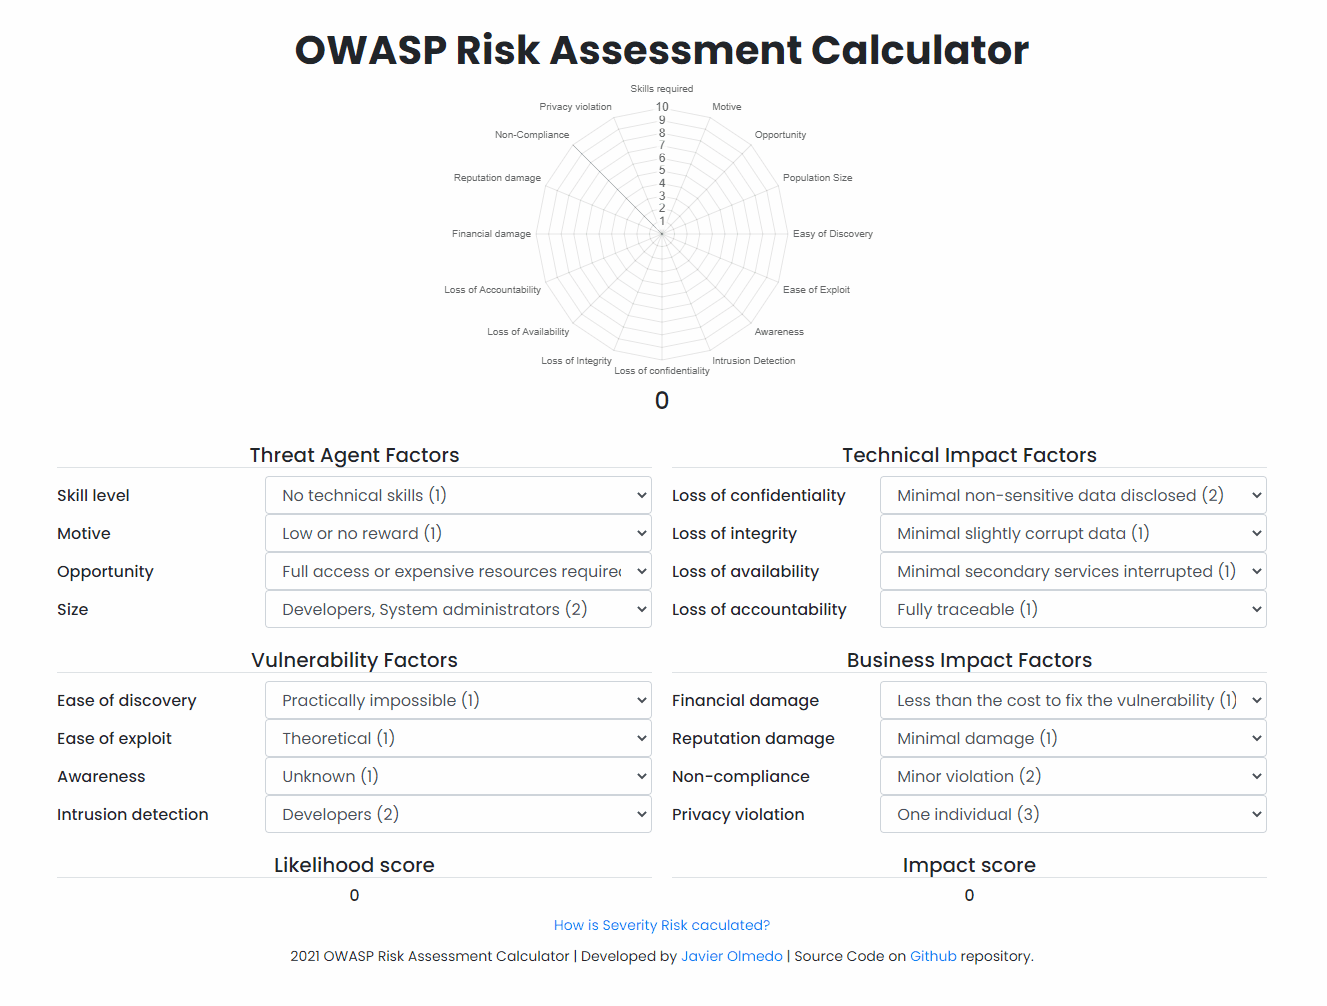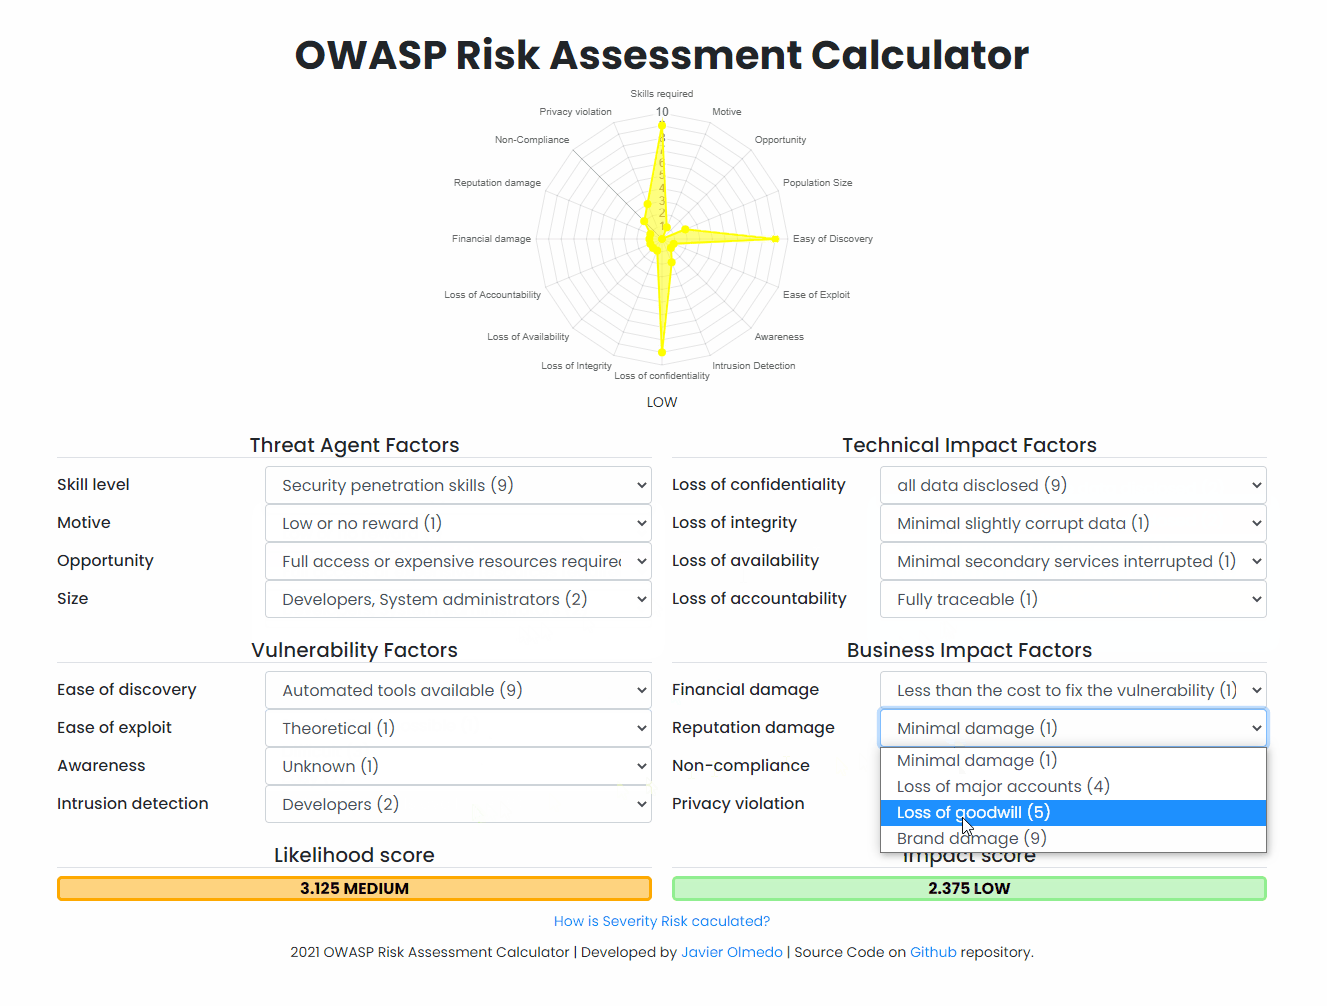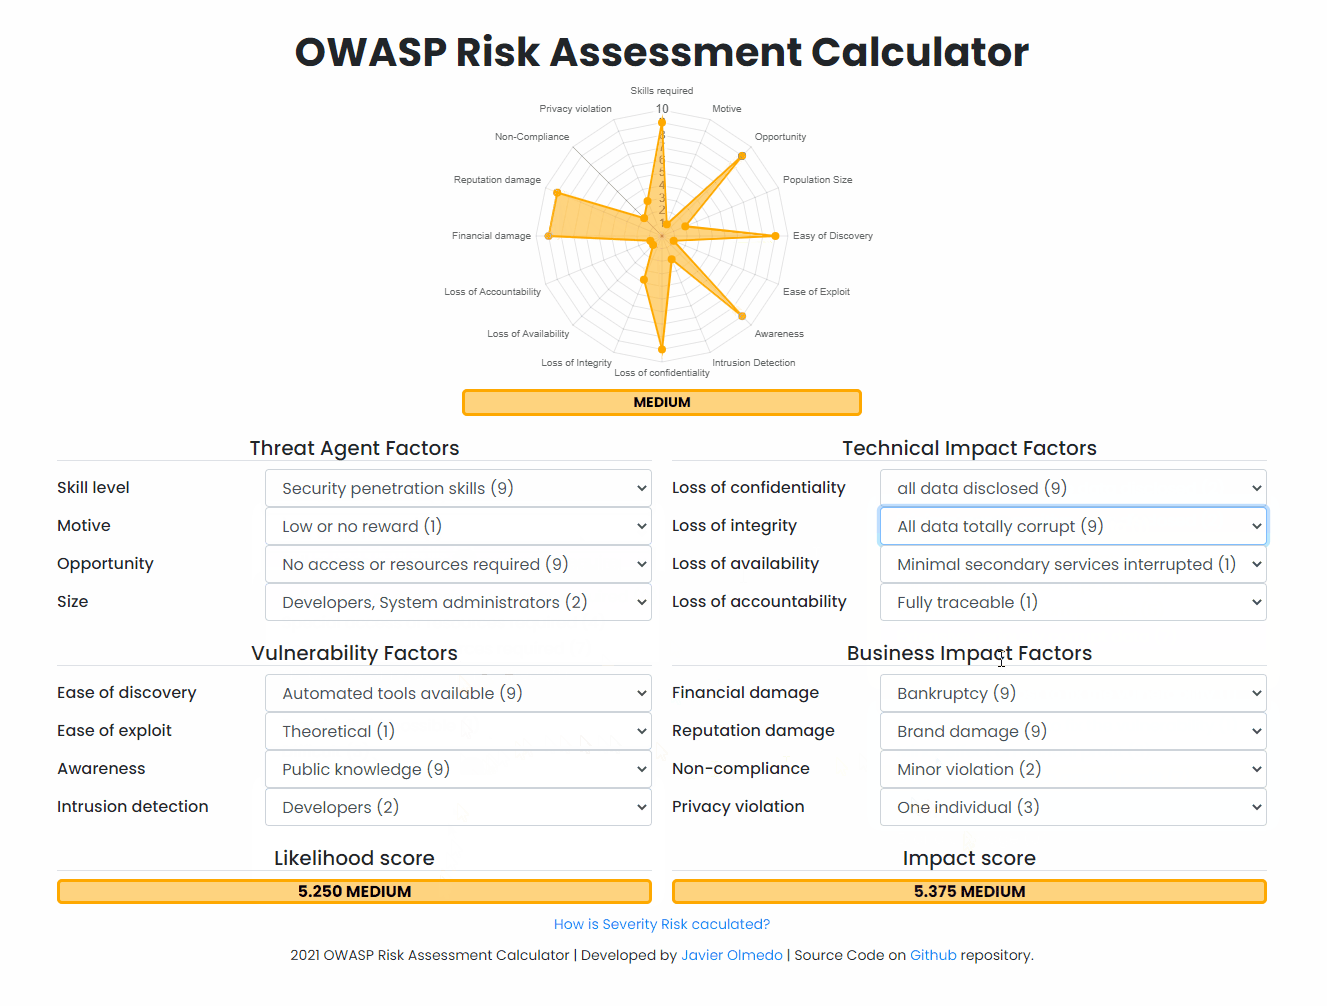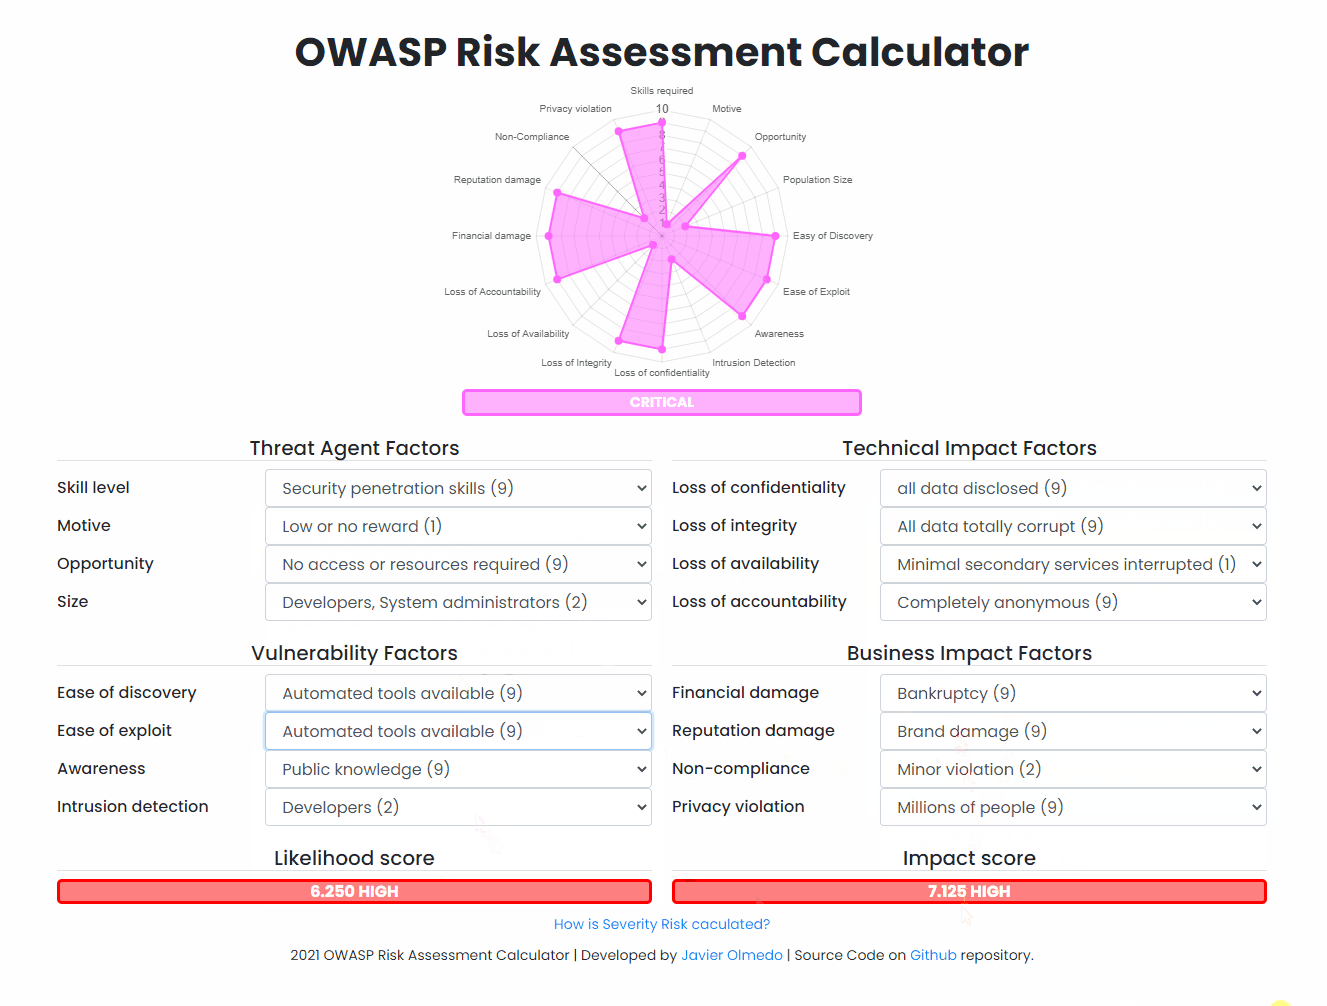 javierolmedo/owasp-calculator
🧮 An online calculator to assess the risk of web vulnerabilities based on OWASP Risk Assessment
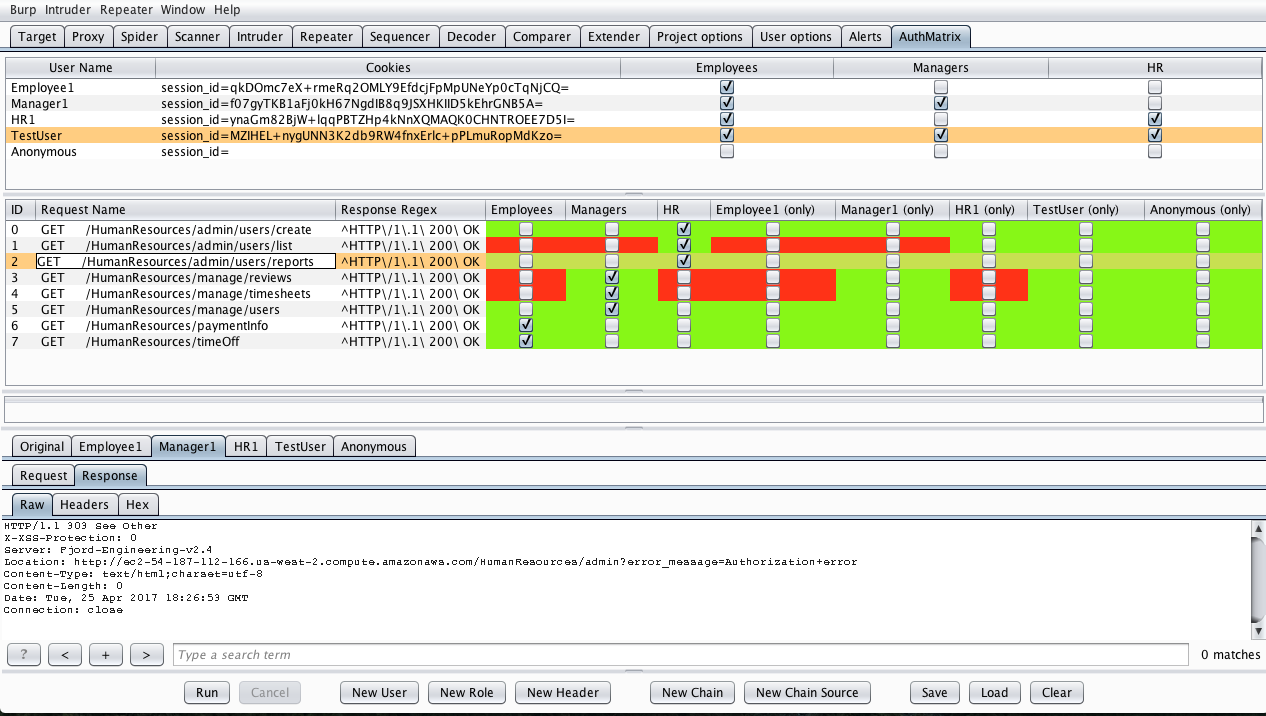 securityinnovation/authmatrix
AuthMatrix is a Burp Suite extension that provides a simple way to test authorization in web applications and web services.
 net-hunter121/api-wordlist
Curated wordlists of API function names, verbs, and nouns for fuzzing web application endpoints with Burp Suite Intruder.
 santandersecurityresearch/corsair_scan
Automated CORS misconfiguration scanner that tests Origin header injection, wildcard reflection, and credential leakage across web applications and…
 ebryx/aes-killer
Burp Plugin to decrypt AES encrypted traffic on the fly
 voorivex/pentest-guide
Penetration tests guide based on OWASP including test cases, resources and examples.
 boku7/cve-2020-23839
Public PoC Disclosure for CVE-2020-23839 - GetSimple CMS v3.3.16 suffers from a Reflected XSS on the Admin Login Portal
 ngalongc/openapi_security_scanner
Automated authorization security scanner for OpenAPI-based APIs. Tests GET endpoints with multiple credential sets to detect privilege escalation and…
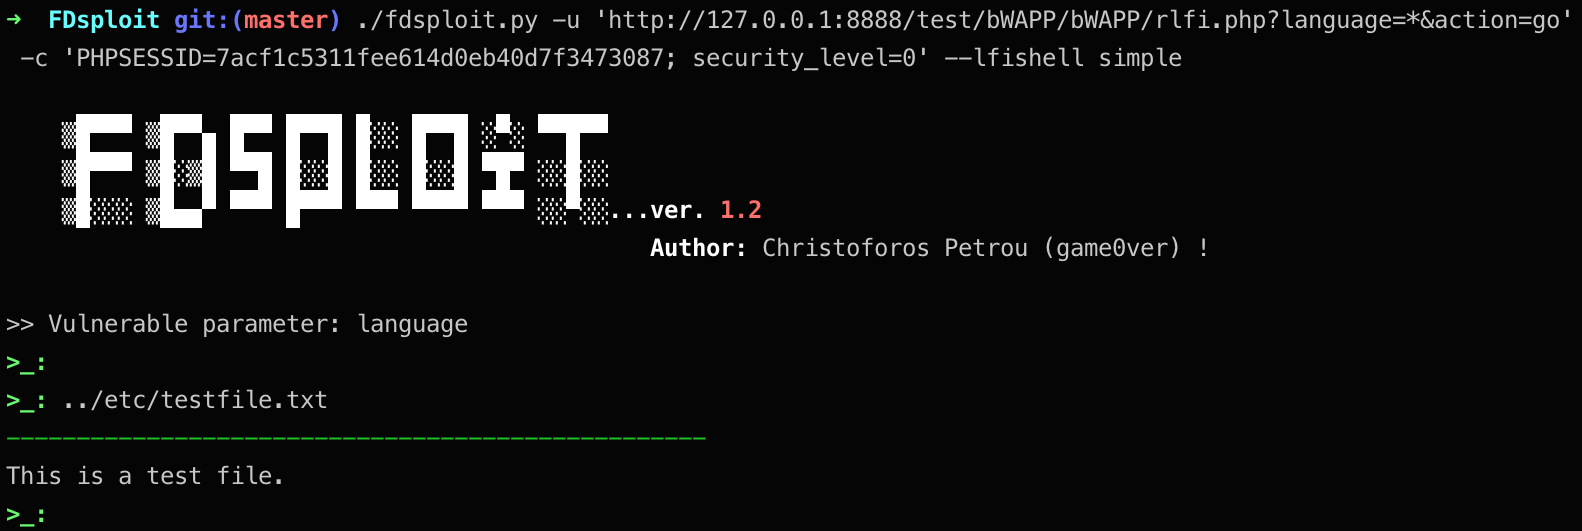 chrispetrou/fdsploit
File Inclusion & Directory Traversal fuzzing, enumeration & exploitation tool.
 rapid7/hackazon
A modern vulnerable web app
 owasp/packman
A documentation and tracking project with the goal of making package management systems more secure.
 moniik/poc_salesforce_lightning
Academic purposes only. Attack against Salesforce lightning with guest privilege.
 owasp/passfault
OWASP Passfault evaluates passwords and enforces password policy in a completely different way.
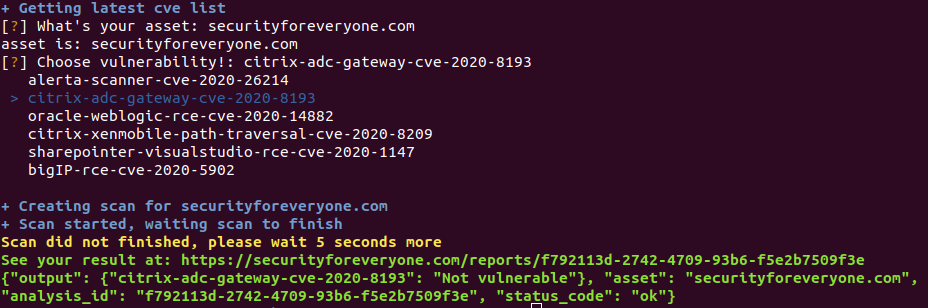 s4e-io-old-labs/s4e-cve-scanner
API-based scanner that retrieves and lists the latest Common Vulnerabilities and Exposures (CVEs) for automated security assessment and vulnerability…