
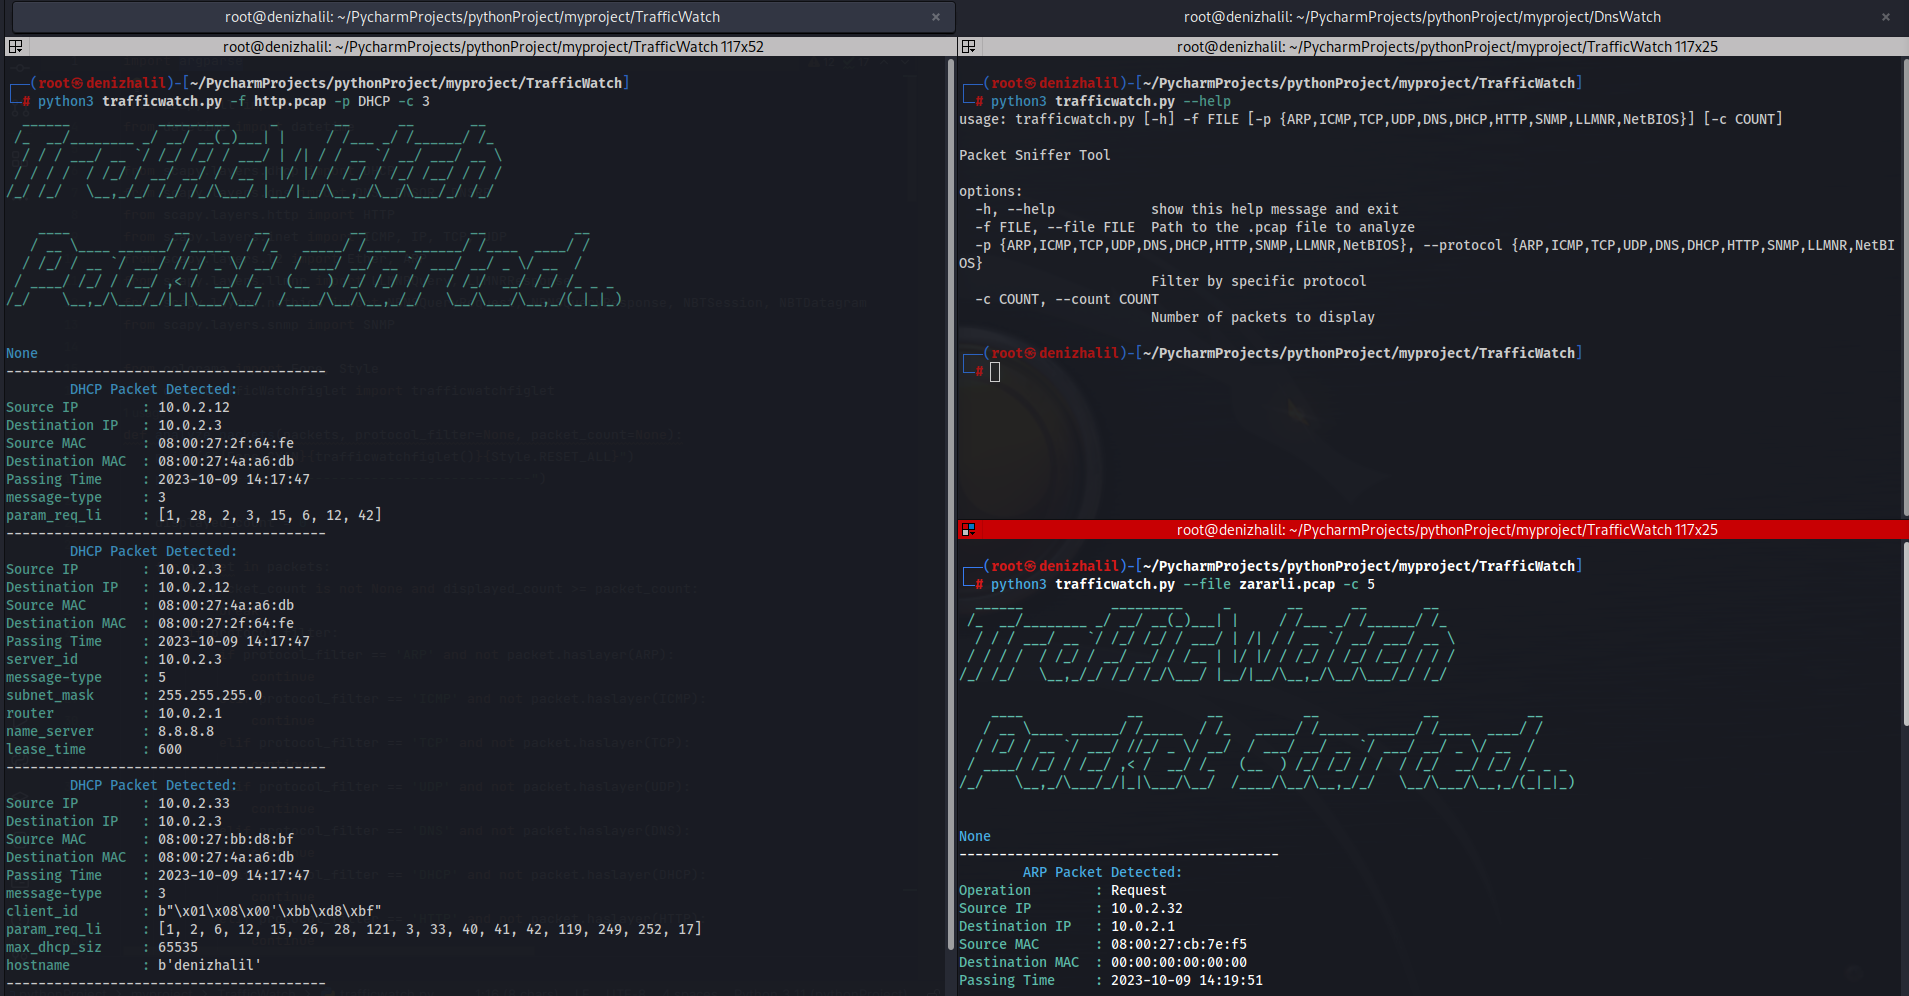
TrafficWatch
 halildeniz/trafficwatch
PCAP-based packet sniffer and analyzer supporting ARP, ICMP, TCP, UDP, DNS, DHCP, HTTP, SNMP, LLMNR, and NetBIOS protocol inspection with filtering…
information-gatheringnetwork-mappingnetwork-security+1
halildeniz/trafficwatchPCAP-based packet sniffer and analyzer supporting ARP, ICMP, TCP, UDP, DNS, DHCP, HTTP, SNMP, LLMNR, and NetBIOS protocol inspection with filtering…
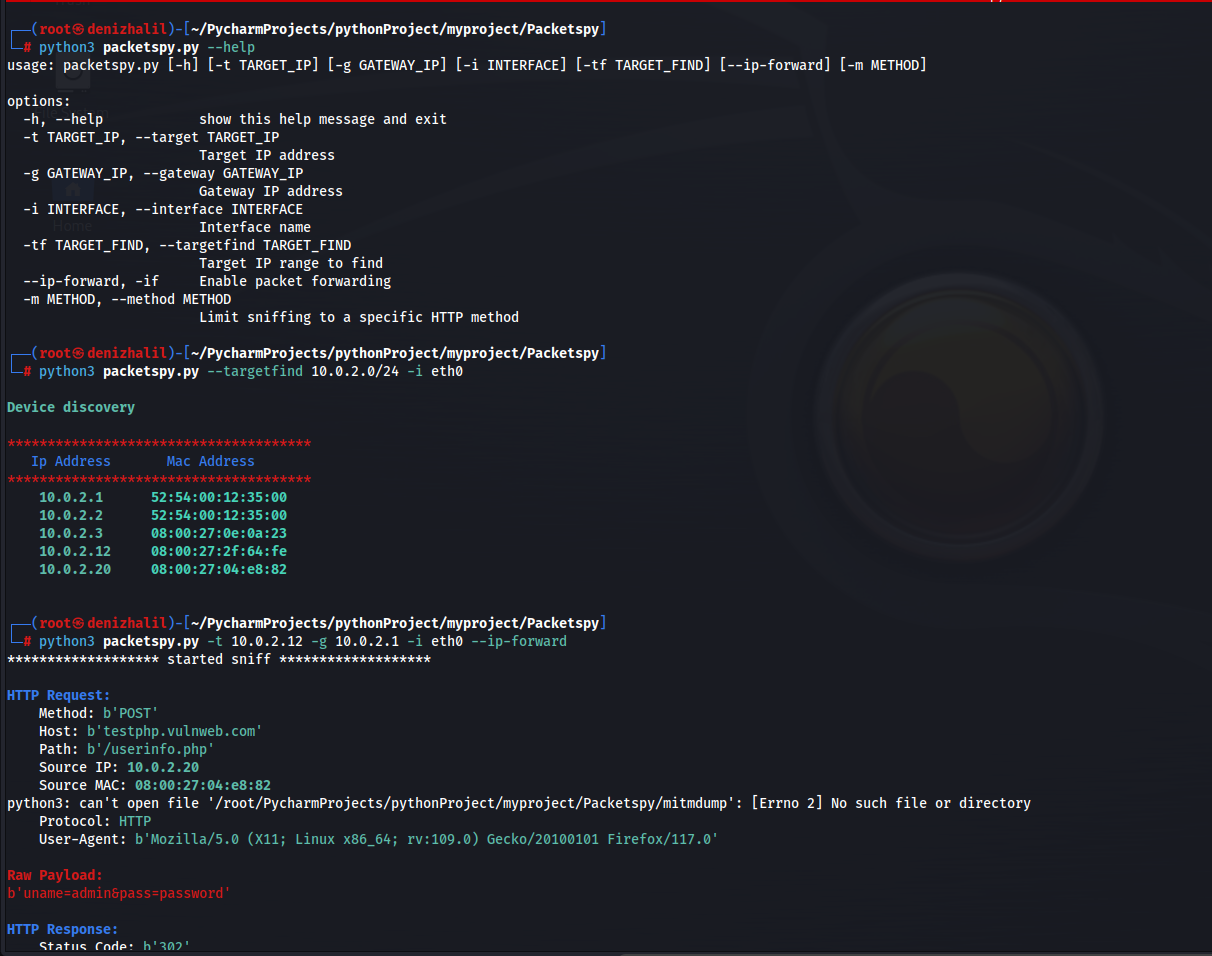 halildeniz/packetspy
Network packet sniffer for real-time traffic capture, HTTP inspection, raw payload analysis, and device discovery with built-in man-in-the-middle…
 kirkdjohnson/wireshark
Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…
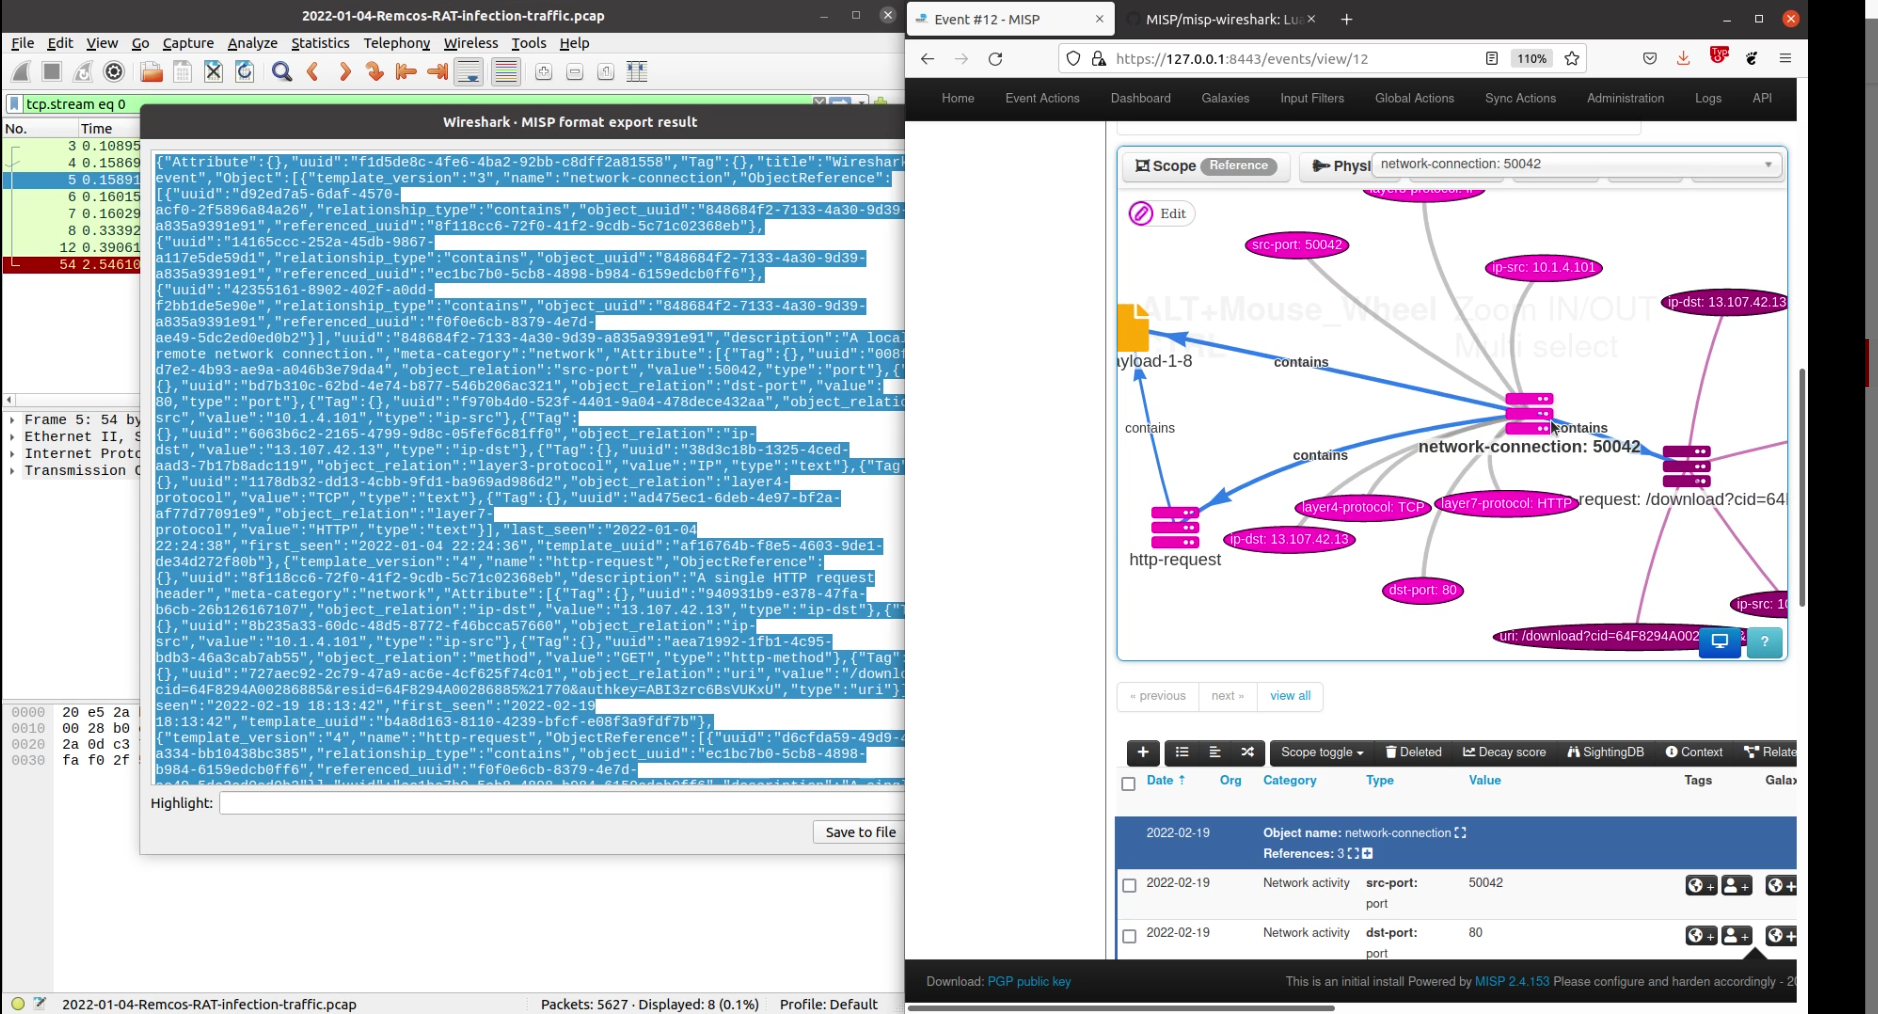 misp/misp-wireshark
Lua plugin to extract data from Wireshark and convert it into MISP format
 hhhrrrttt222111/ethical-hacking-tools
Complete Listing and Usage of Tools used for Ethical Hacking
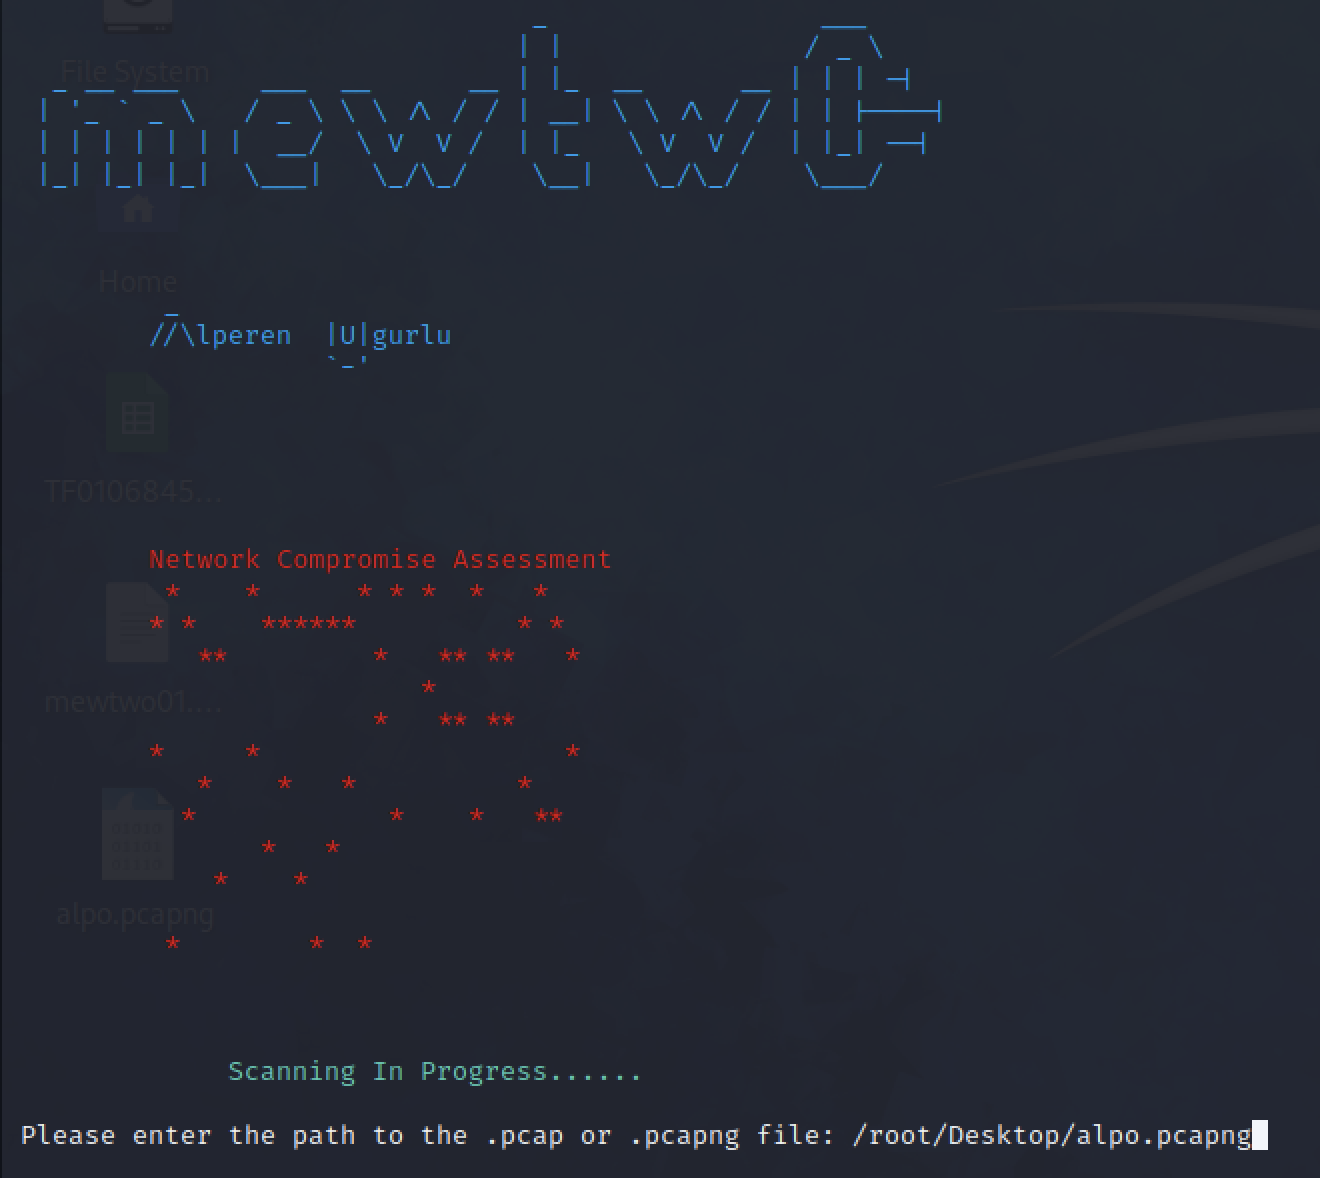 alperenugurlu/network_assessment
With Wireshark or TCPdump, you can determine whether there is harmful activity on your network traffic that you have recorded on the network you…
 gcla/termshark
A terminal UI for tshark, inspired by Wireshark
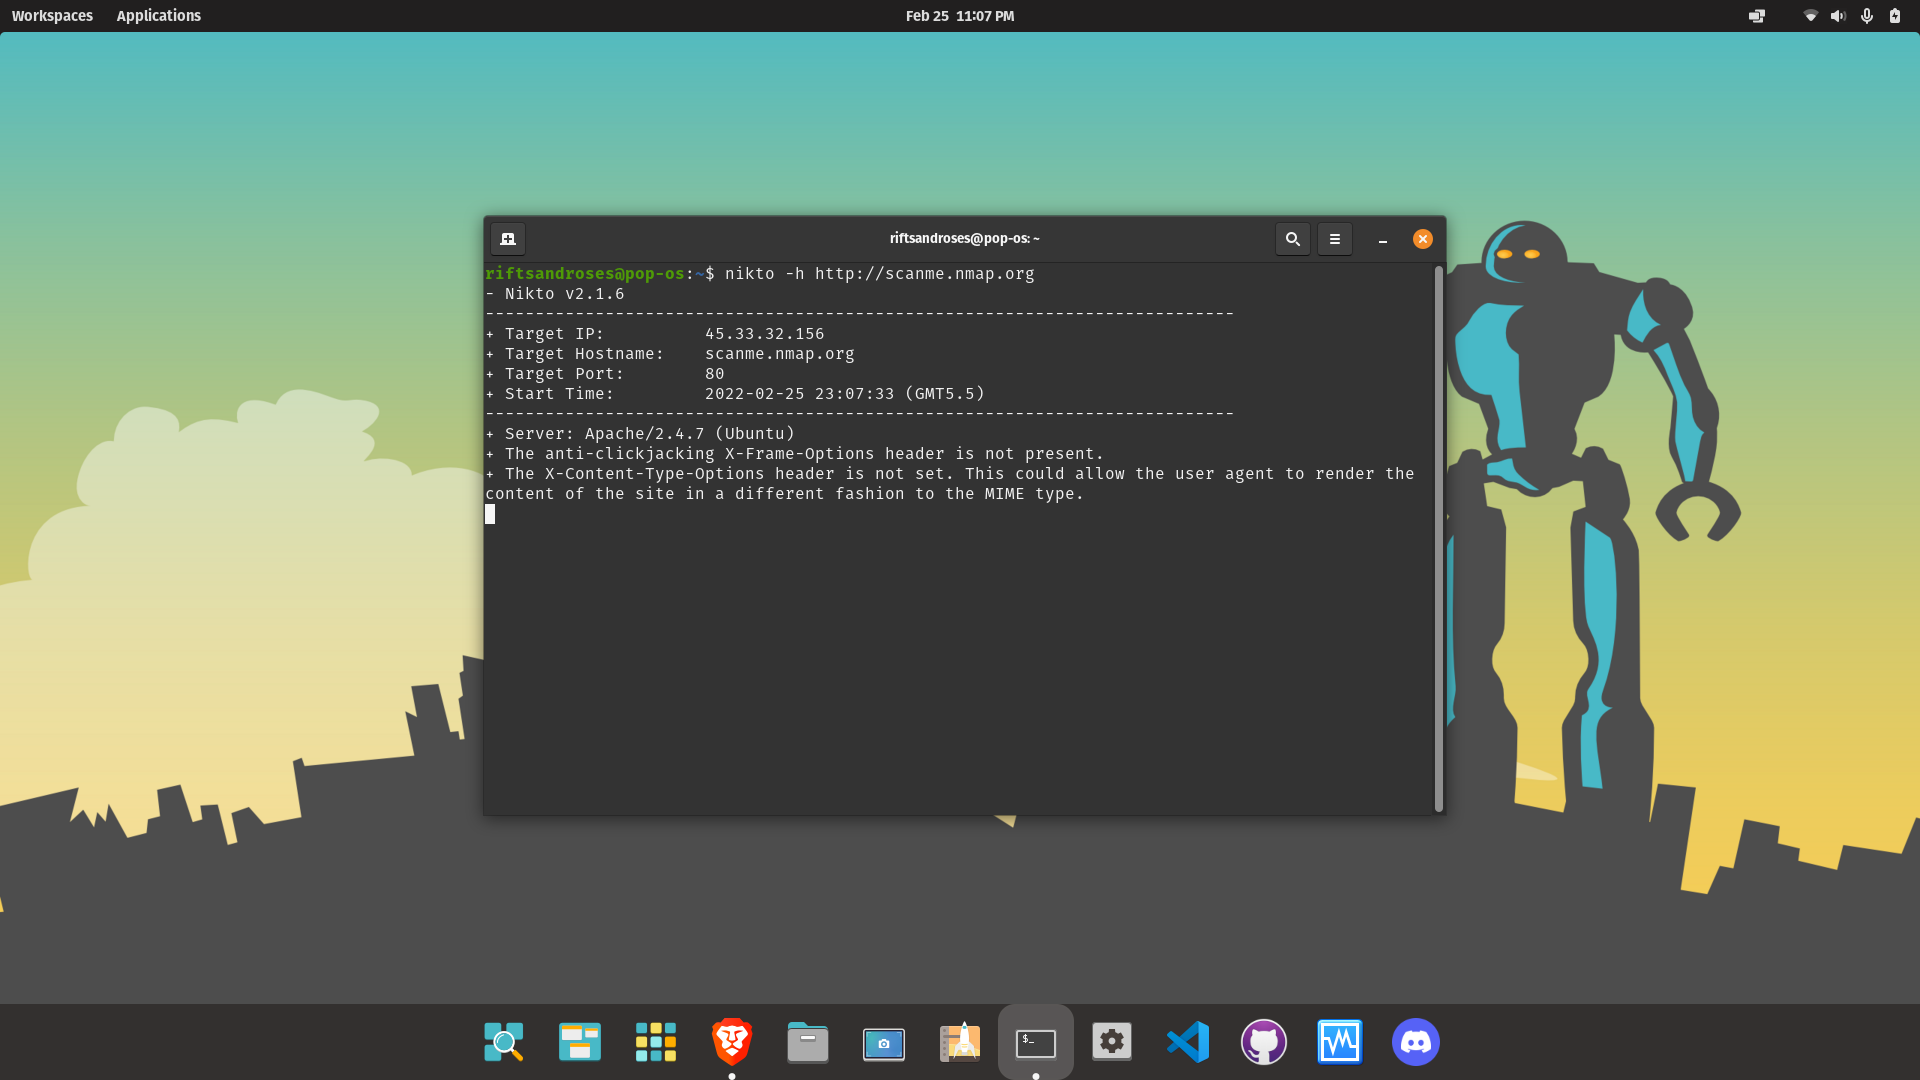
 ilk-toolkit/ilk-toolkit
A ToolKit that automatically installs & configures all the Tools needed to turn your Daily Driver Linux Distro into a Pentesting Machine
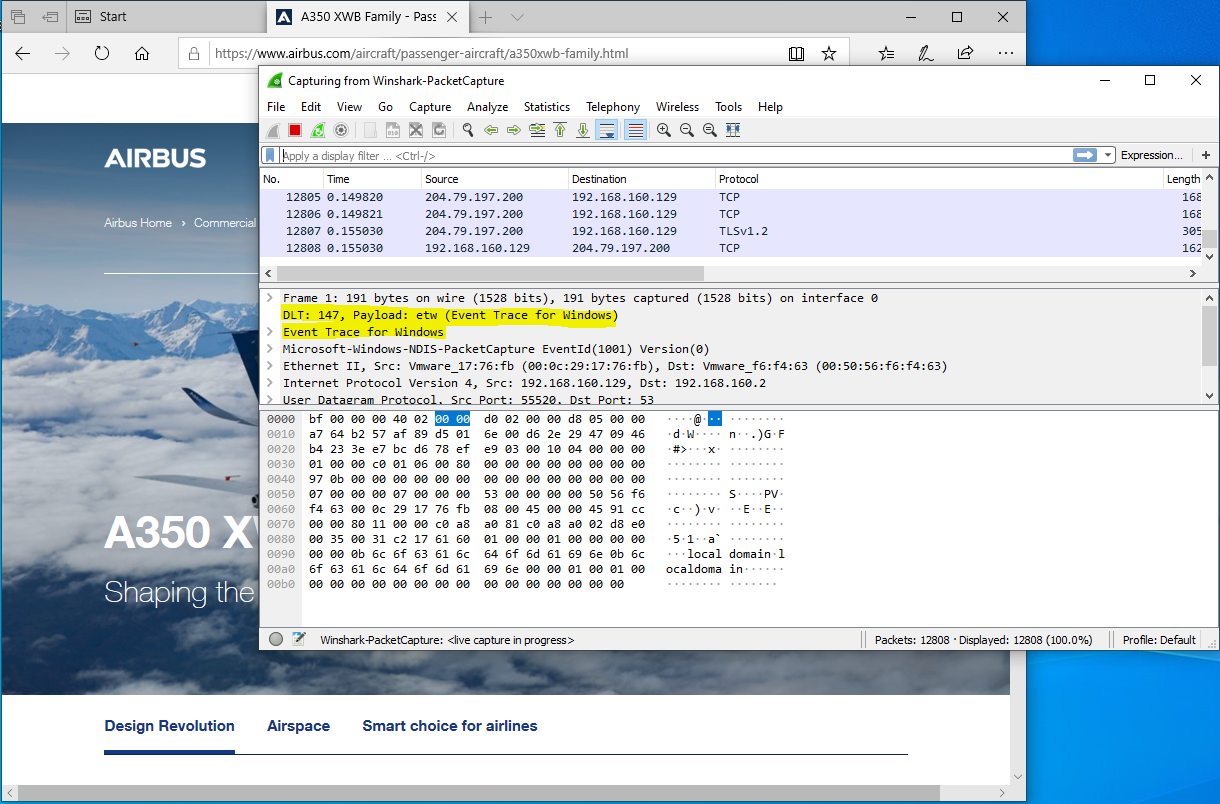 airbus-cert/winshark
A wireshark plugin to instrument ETW
 rjbhide/wireshark-forensics-plugin
Wireshark plugin that correlates network traffic with threat intelligence, asset tags, and vulnerability data to accelerate forensic analysis of PCAP…
 xdavidhu/mitmap
📡 A python program to create a fake AP and sniff data.
 pentesteracademy/patoolkit
PA Toolkit is a collection of traffic analysis plugins focused on security
 kiminewt/pyshark-legacy
Python wrapper for tshark, allowing python packet parsing using wireshark dissectors (Python2 legacy version)