

BSOD_bitlocker_recover
 fishermavis/bsod_bitlocker_recover
Python script for carving Bitlocker VMK keys
data-recoverydigital-forensicsdisk-forensics+3
26
fishermavis/bsod_bitlocker_recoverPython script for carving Bitlocker VMK keys
 barnew-st/ecdsa-private-key-recovery
A cryptographic research tool for analyzing signature vulnerabilities
 t6x/reaver-wps-fork-t6x
Brute-force attack tool against WPS registrar PINs to recover WPA/WPA2 passphrases, supporting online brute force and offline Pixie Dust attacks on…
 rowingdude/analyzemft
analyzeMFT.py is designed to fully parse the MFT file from an NTFS filesystem and present the results as accurately as possible in multiple formats.
 gregwar/fatcat
FAT filesystems explore, extract, repair, and forensic tool
 securityjoes/forensicminer
A really good DFIR automation for collecting and analyzing evidence designed for cybersecurity professionals.
 n0mi1k/pmkidcracker
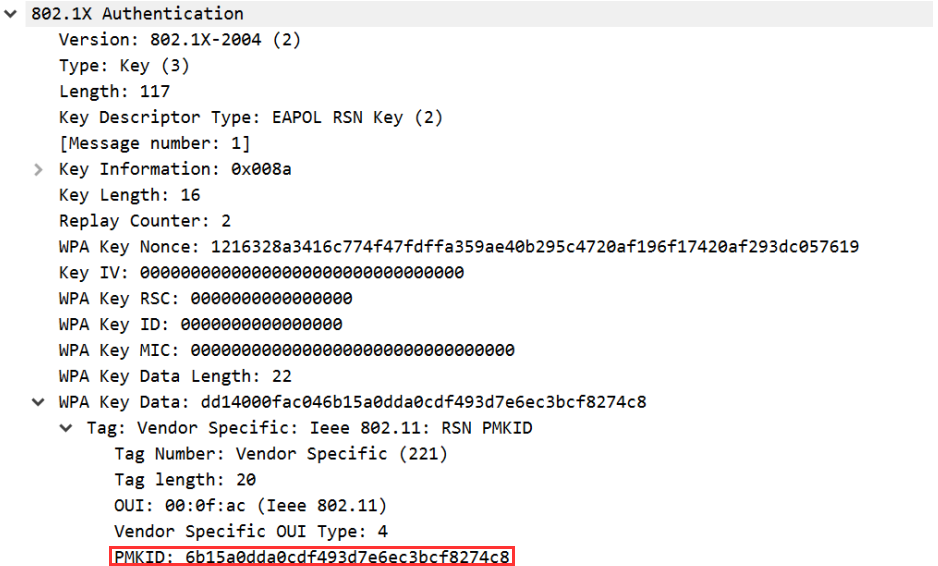
A tool to crack WPA2 passphrase with PMKID value without clients or de-authentication
 cisagov/esxiargs-recover
A tool to recover from ESXiArgs ransomware
 trustedsec/tscopy
Python tool that parses the NTFS $MFT to copy locked files during incident response, bypassing OS locks by reading raw disk locations. Supports…
 rajchowdhury240/cve-2018-13341
This Tool Aims to Exploit the CVE-2018-13341
 sleuthkit/scalpel
File carving and indexing tool for digital forensics, recovering files from disk images based on header/footer pattern matching, regular expressions,…
 fboldewin/atmmalscan
Command-line DFIR tool for scanning Windows ATM systems to detect malware traces in process memory and disk, with automated memory dump creation for…
 sekoialab/fastir_collector
Live Windows forensic acquisition tool that collects system artefacts (registry, memory, disk, files) into CSV/JSON for early compromise detection…
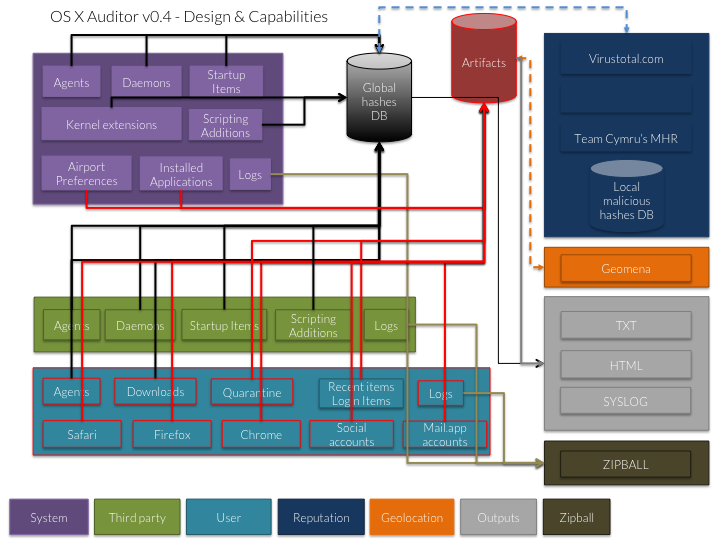 jipegit/osxauditor
OS X Auditor is a free Mac OS X computer forensics tool
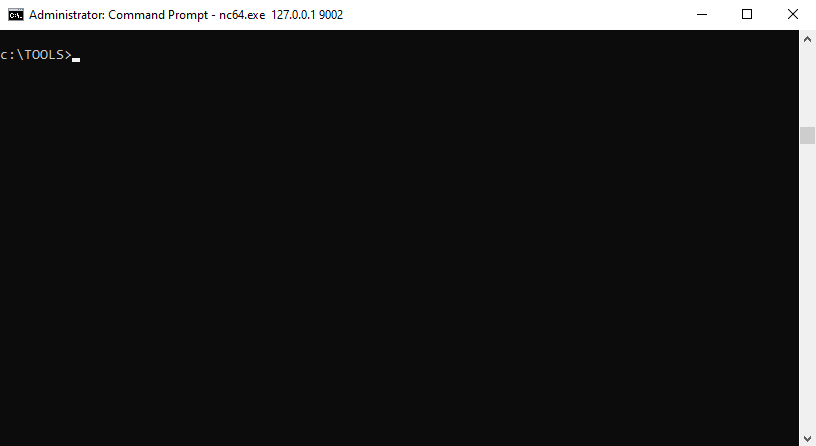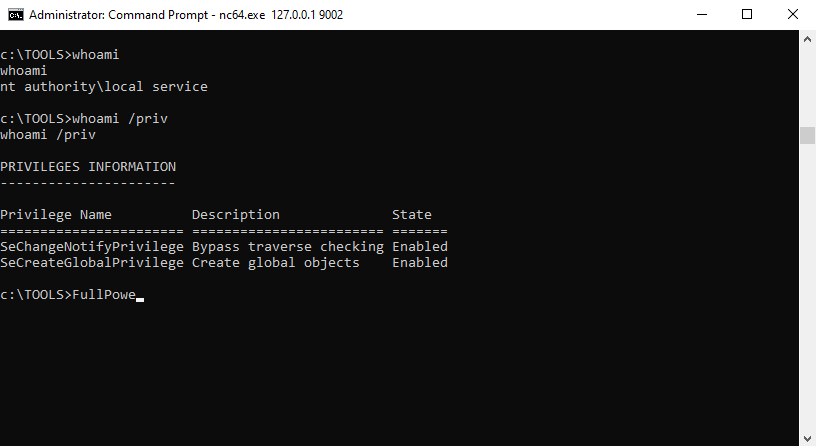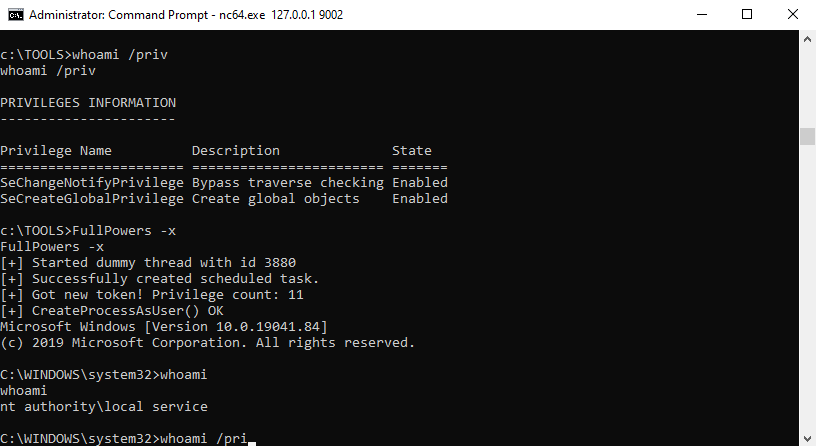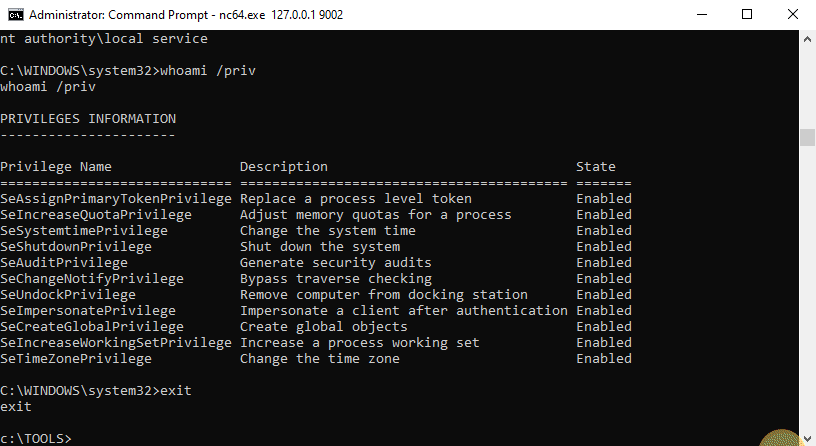 itm4n/fullpowers
Recover the default privilege set of a LOCAL/NETWORK SERVICE account
 axcheron/crestron_getsudopwd
Tool to exploit CVE-2018-13341 and recover hidden account password on Crestron devices
 jschicht/extractusnjrnl
Tool to extract the $UsnJrnl from an NTFS volume