
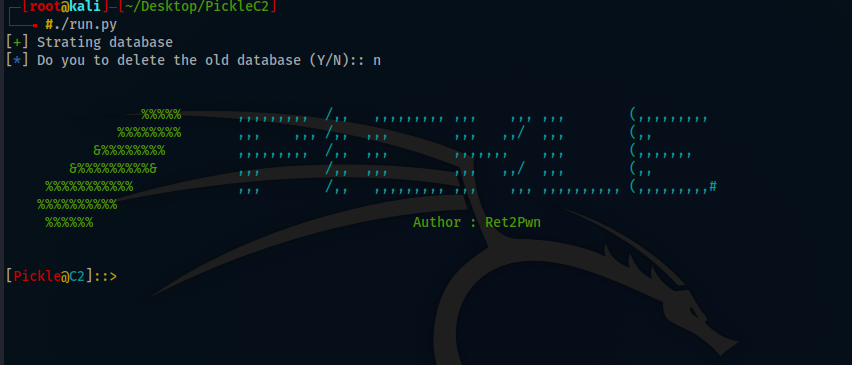
PickleC2
 xret2pwn/picklec2
Encrypted C2 framework for post-exploitation and lateral movement, supporting PowerShell implants and custom modules for red team engagements.
command-and-controllateral-movementpenetration-testing-frameworks+2
98
xret2pwn/picklec2Encrypted C2 framework for post-exploitation and lateral movement, supporting PowerShell implants and custom modules for red team engagements.
 med0x2e/gadgettojscript
A tool for generating .NET serialized gadgets that can trigger .NET assembly load/execution when deserialized using BinaryFormatter from JS/VBS/VBA…
 notmedic/netntlmtosilverticket
SpoolSample -> Responder w/NetNTLM Downgrade -> NetNTLMv1 -> NTLM -> Kerberos Silver Ticket
 3t4n/samba-3.0.24-cve-2007-2447-vunerable-
Vulnerable Samba 3.0.24 environment for reproducing CVE-2007-2447 command execution, intended for exploit testing and security research.
 nccgroup/keimpx
Check for valid credentials across a network over SMB
 glorisonlai/printnightmare
Proof-of-concept implementation of CVE-2021-34527 (PrintNightmare) for exploiting Windows Print Spooler remote code execution and privilege…
 ptter23/cve-2021-1675
CVE-2021-1675: ZERO-DAY VULNERABILITY IN WINDOWS PRINTER SERVICE WITH AN EXPLOIT AVAILABLE IN ALL OPERATING SYSTEM VERSIONS
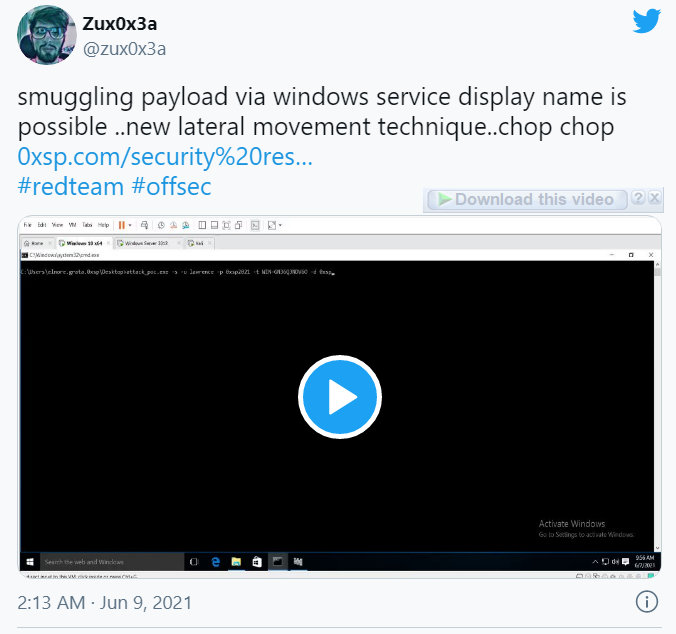 zux0x3a/tchopper
conduct lateral movement attack by leveraging unfiltered services display name to smuggle binaries as chunks into the target machine
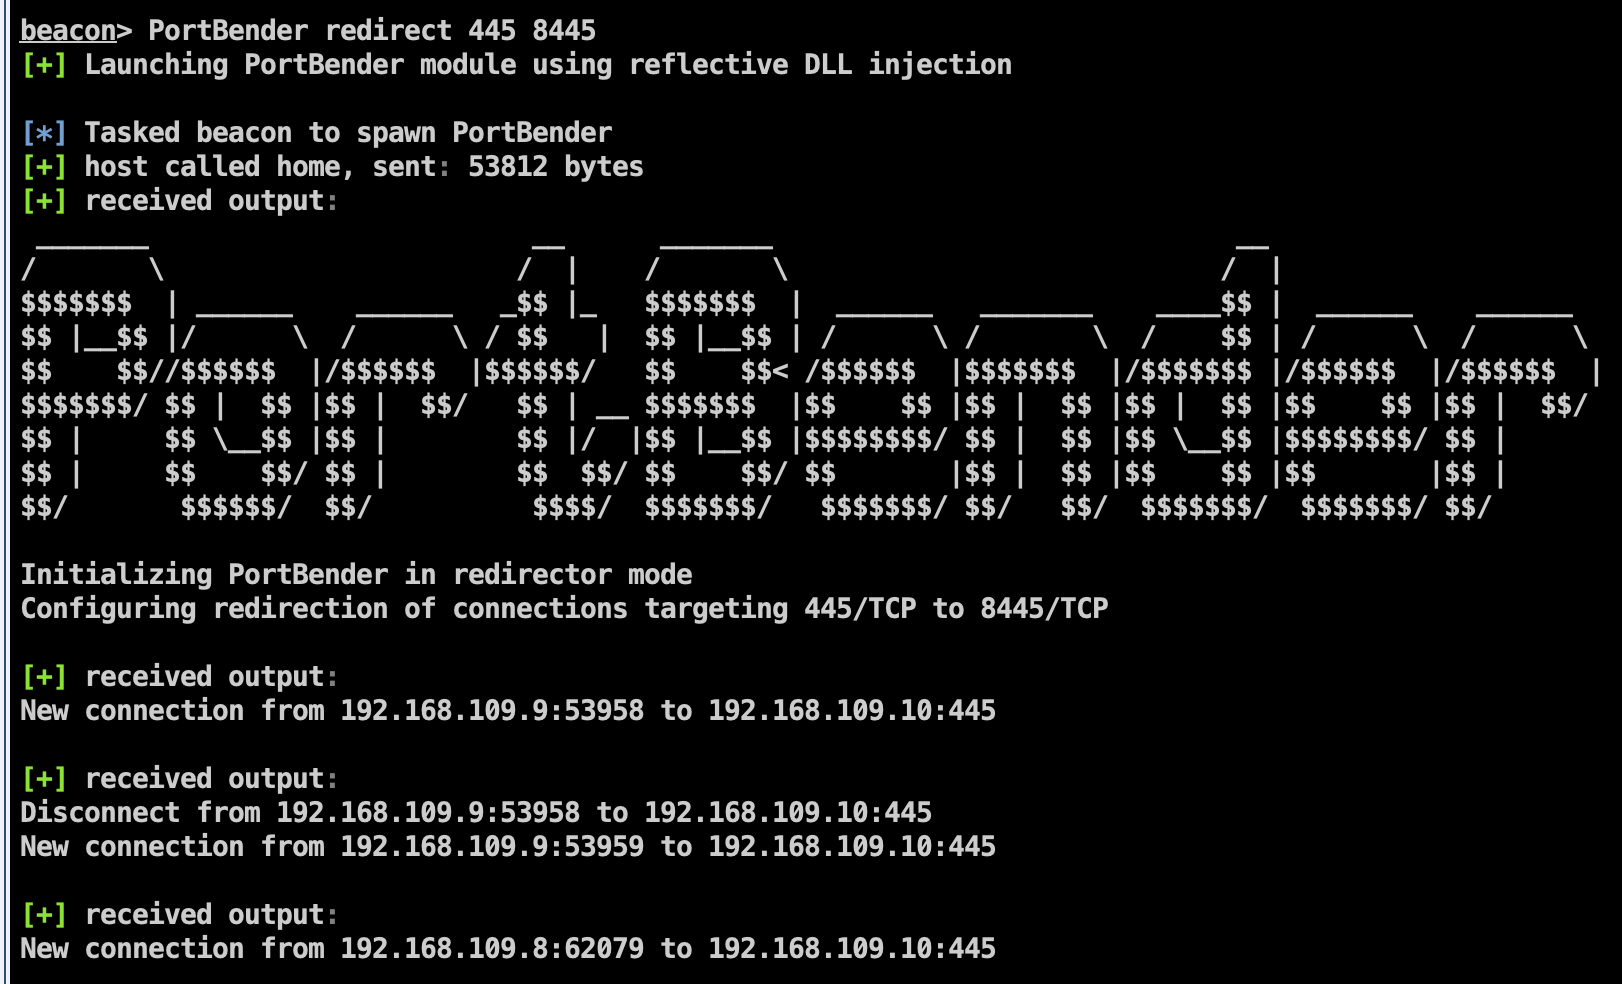 praetorian-inc/portbender
TCP Port Redirection Utility
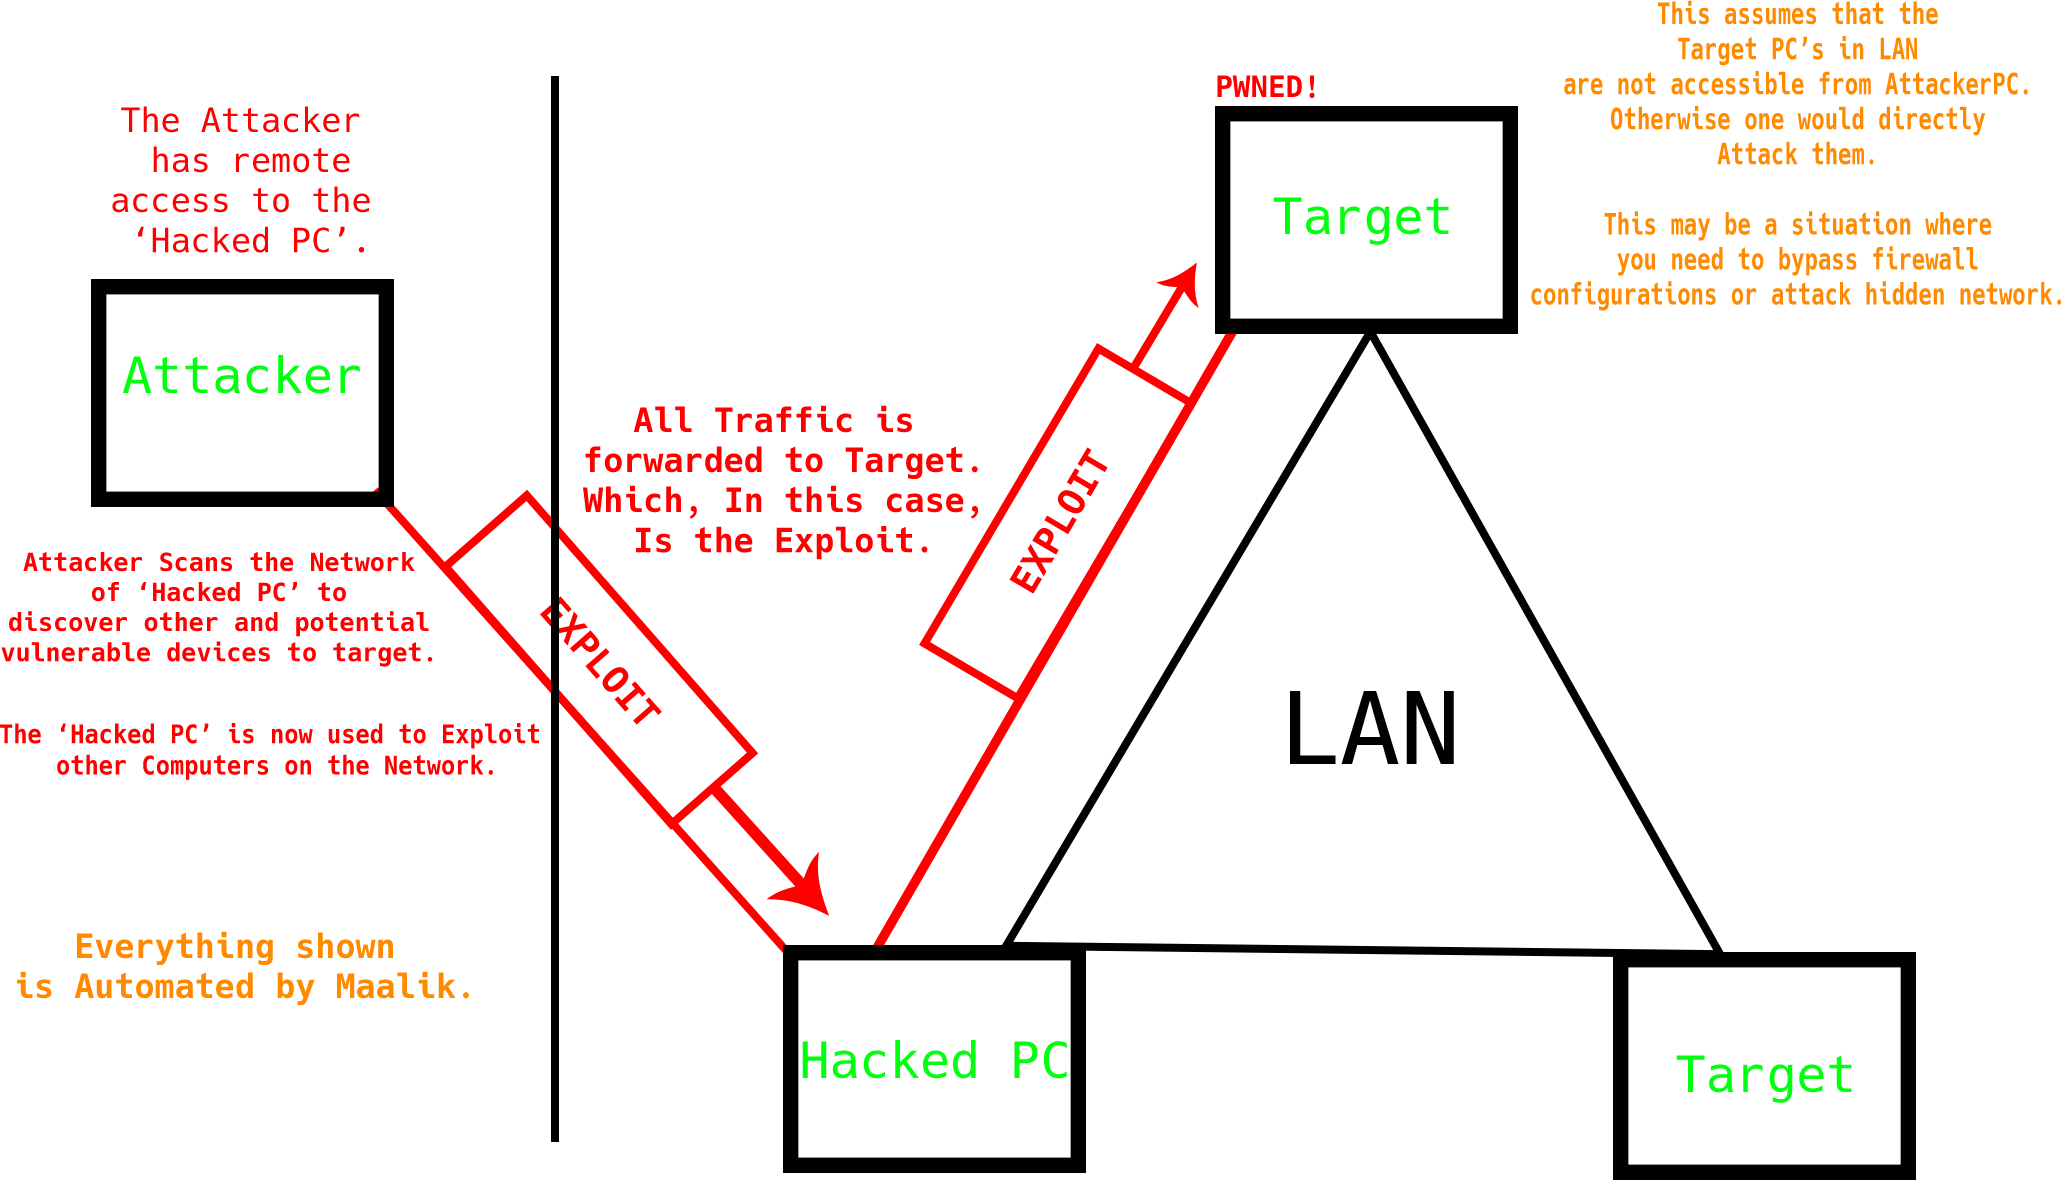 quantumcore/maalik
Feature-rich Post Exploitation Framework with Network Pivoting capabilities.
 mustafadalga/arp-spoof-detector
Bilgisayarınıza yapılan ARP Spoofing saldırılarını tespit eden ARP Spoof Detector Scripti.
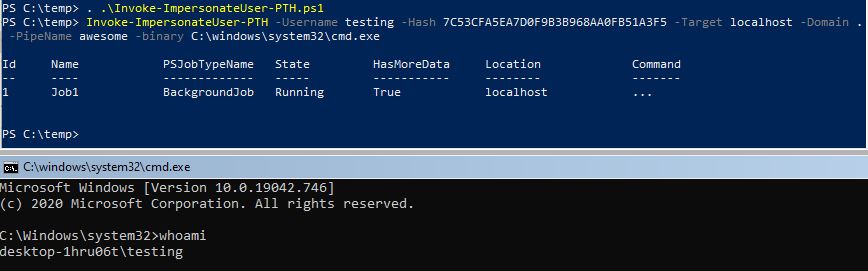 s3cur3th1ssh1t/namedpipepth
Pass the Hash to a named pipe for token Impersonation
 itssmikefm/cve-2020-1472
Python exploit for CVE-2020-1472 (Zerologon) targeting Netlogon authentication to compromise Active Directory domain controllers and escalate…
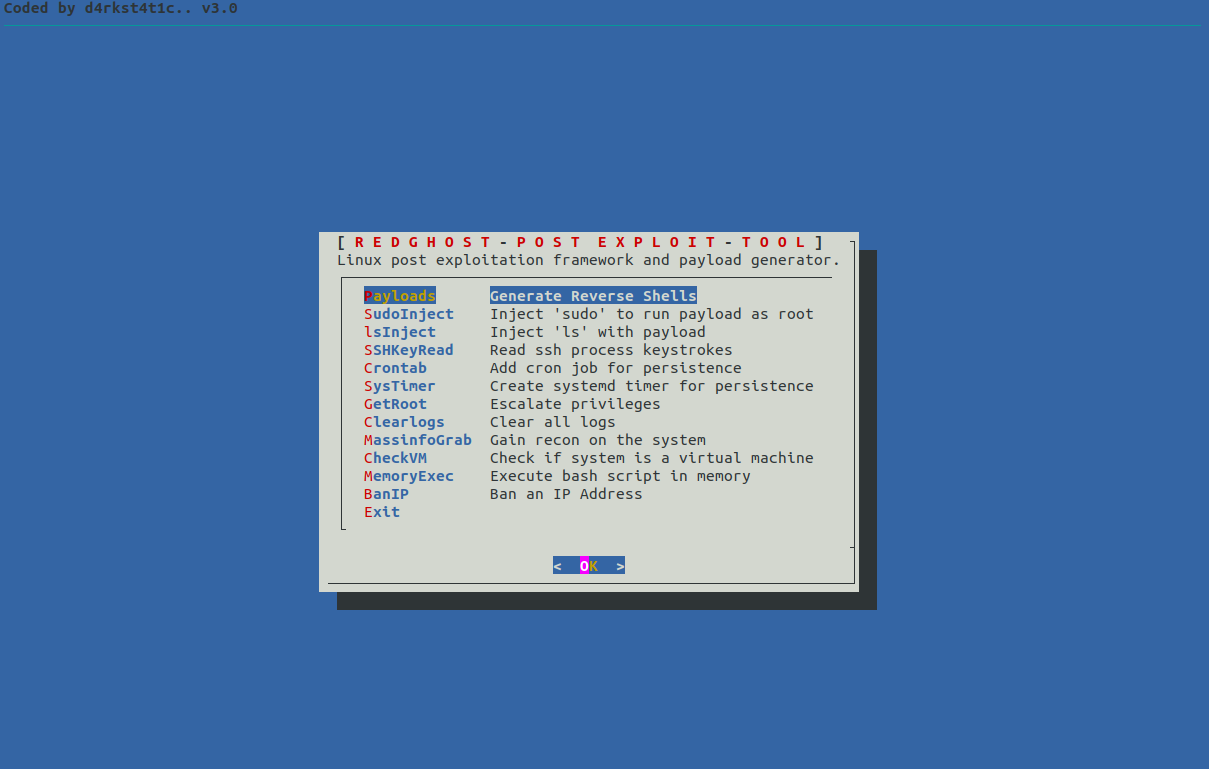 d4rk007/redghost
Linux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…
 fengzhouc/cve-2021-21300
Proof-of-concept exploit for CVE-2021-21300, demonstrating remote code execution via malicious git repository cloning with symlink and filter abuse…
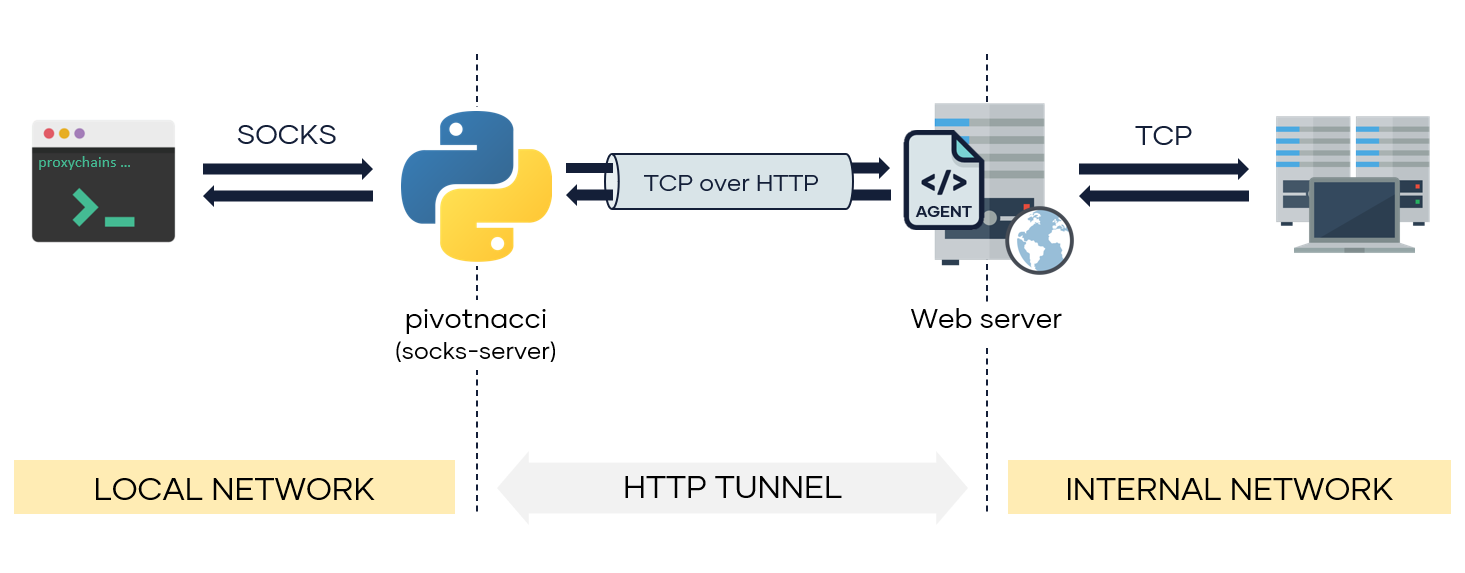 blackarrowsec/pivotnacci
A tool to make socks connections through HTTP agents
 int0/cve-2015-1769
Proof-of-concept exploit for CVE-2015-1769 using a crafted VHD file and symbolic link to trigger a Windows privilege escalation via Mount Manager.