
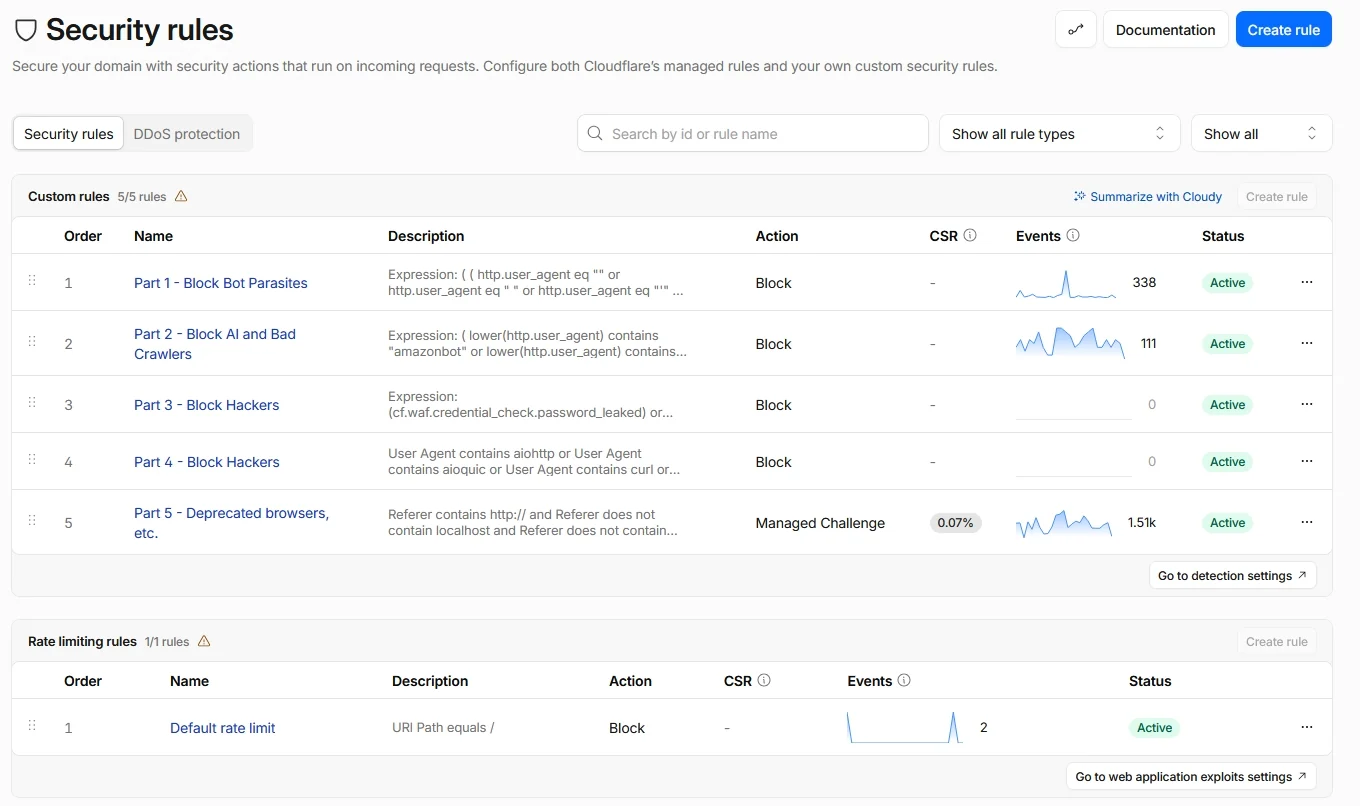
cloudflare-security-art
 buybitart/cloudflare-security-art
Cloudflare Free Plan security rules (Zero Trust approach) for small websites
anti-botconfiguration-auditingcurated-resources+5
224
buybitart/cloudflare-security-artCloudflare Free Plan security rules (Zero Trust approach) for small websites
 lifting-bits/sleigh
CMake build of Ghidra's SLEIGH processor specification library, providing standalone disassembly and p-code lifting engines for reverse engineering…
 gmh5225/linux-iptables-firewall-ultrafirewall
Defensive Linux firewall toolkit combining IPTables rules and kernel configuration to protect hosts and servers against DoS, DDoS, and network…
 rknf404/chromium-hardening-guide
Harden chromium (somewhat) for privacy and security (and performance)
 lolcaken/javascript-deobfuscator
Deobfuscator for javascript-obfuscator 5.x output (string arrays, control-flow flattening, self-defending, RC4/base64)
 rbidou/pyrasp
Runtime Application Self Protection for Python web servers, serverless functions and MCP servers, detecting attacks, prompt injection and data leaks…
 ejfkdev/jscd
Reverse bytenode .jsc (V8 code cache) to JavaScript — static, pure Rust, no patched V8/Node. Node 8→26 / V8 5.8–14.6; 25k .jsc tested, 0 fail.
 b4sith-sec/gu3ssweak
Deliberately vulnerable Android app for mobile security research and bug bounty practice - OWASP Mobile Top 10
 thomaspoppelgaard/netscaler-ctx697096-checker
Read-only checker for Citrix NetScaler CTX697096 (CVE-2026-88771–88778): verifies build, CVE preconditions and upgrade risks, and sweeps public IoCs…
 techupdate24/capacitor-flaw-cve-2026-103922
A complete guide and workflow for integrating Agile sprints with DevOps CI/CD pipelines.
 bombobombone/cve-2026-103442
Local proof-of-concept and sanitized report for CVE-2026-103442, a PHP object injection in MediaWiki CentralAuth's merge-session handling that can…
 bombobombone/cve-2026-103437
Local proof-of-concept and sanitized report for CVE-2026-103437, a canonical URL XSS in MediaWiki ReadingLists triggered via crafted import links.
 bombobombone/cve-2026-100381
Report and PoC for CVE-2026-100381, a DOM XSS in MediaWiki UploadWizard Flickr collection and set titles, with patch verification notes and a local…
 viralmaniar/vulnvault
Developer-focused knowledge base of application security vulnerabilities with insecure vs secure code examples, prevention guidance, and OWASP/CWE…
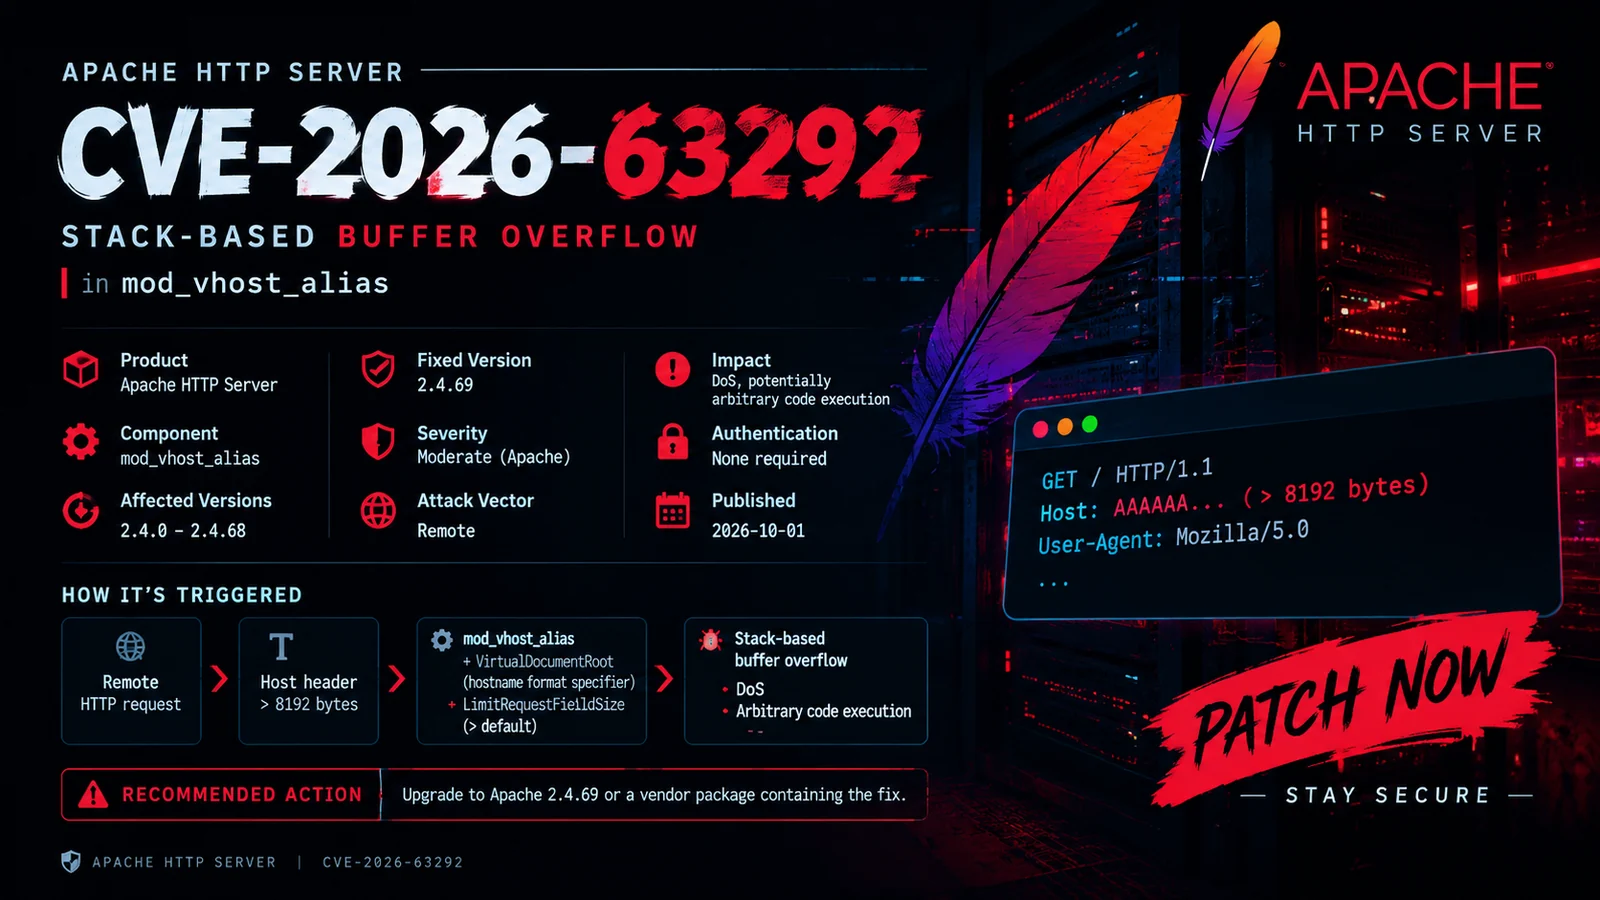 0xblackash/cve-2026-63292
Documents CVE-2026-63292, a stack-based buffer overflow in Apache mod_vhost_alias, with affected versions, safe version and configuration checks, and…
 wayang1337/cve-2026-18143
Request a Quote for WooCommerce (Addify) <= 2.9.2 Unauthenticated arbitrary file upload via afrfq_submit_quote_via_popup
 ncf0126/nagios-xi-s-cve-2023-40931-exploit
Python exploit targeting the Nagios XI SQL injection vulnerability CVE-2023-40931, enabling injection-based access against affected instances.
 wuyou6956-glitch/cve-2026-26026-poc
Proof-of-concept code for CVE-2026-26026, demonstrating the vulnerability for research and validation purposes.