
plausible-editor-invite
 abraxas/plausible-editor-invite
Plausible Analytics master d44e104 - High - Remote - Privilege leftover - editor people HTML leaks transfer nanoid
exploitationlabs-practicepenetration-testing+4
abraxas/plausible-editor-invitePlausible Analytics master d44e104 - High - Remote - Privilege leftover - editor people HTML leaks transfer nanoid
 abraxas/plausible-traffic-notify
Plausible Analytics master d44e104 - High - Remote - IDOR - PUT traffic-change-notification site_id mass assignment
 kolmteistov/gobalance-patch
Security patch and proof-of-concept for GoBalance onion load balancer, covering master key recovery via blindedSign and forged descriptor acceptance,…
 burrowers/garble
Obfuscates Go builds by wrapping the Go toolchain, replacing identifiers, package paths, and position data with hashes and stripping debug and build…
 crypt0p3g/dpapi-toolkit
Drop any Windows DPAPI artifact and it identifies the format and the exact master key it needs, then decrypts once you supply the key. Offline, CLI +…
 amperclock/cve-2023-32784-kdbxpassdmp
Retrieves the master password from Keepass memory dump, using a hint of bruteforce.
 cyberdudebivash/cyberdudebivash-5g-core-key-rotation-ghost-admin-auditor
Production-grade tool for detecting & remediating CVE-2026-0622 (Ghost Admin privilege escalation & master key exposure in 5G core software).
 qubesos/qubes-core-admin
Manages the core lifecycle of Qubes OS domains via a Python admin API, handling secure compartmentalization with Xen and exposing an event system for…
 pugazhendii22/keepass-exfil-forensics
Network forensics writeup + tooling for a TryHackMe DFIR challenge: reverses a hex→Base64→XOR exfiltration chain from PCAP traffic, then recovers a…
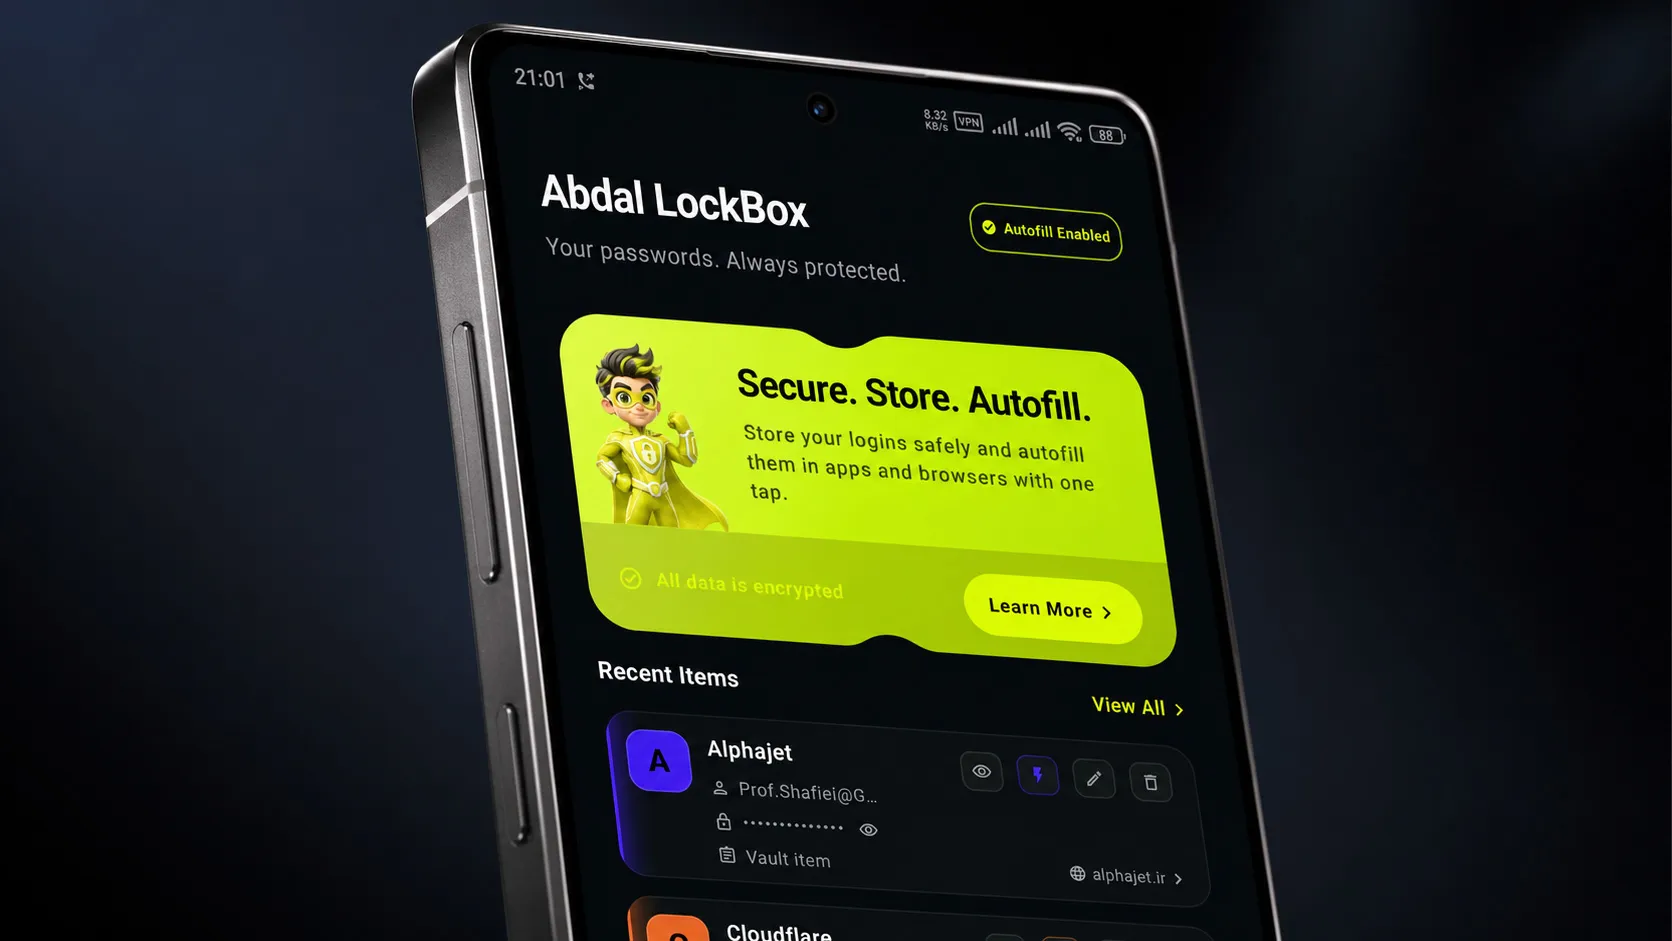
 prof.shafiei/abdal-lockbox
Local-first encrypted password vault for Android with Master Password access, Recovery Key support, Autofill integration, and portable encrypted…
 flangvik/sharpcollection
Nightly builds of common C# offensive tools, fresh from their respective master branches built and released in a CDI fashion using Azure DevOps…
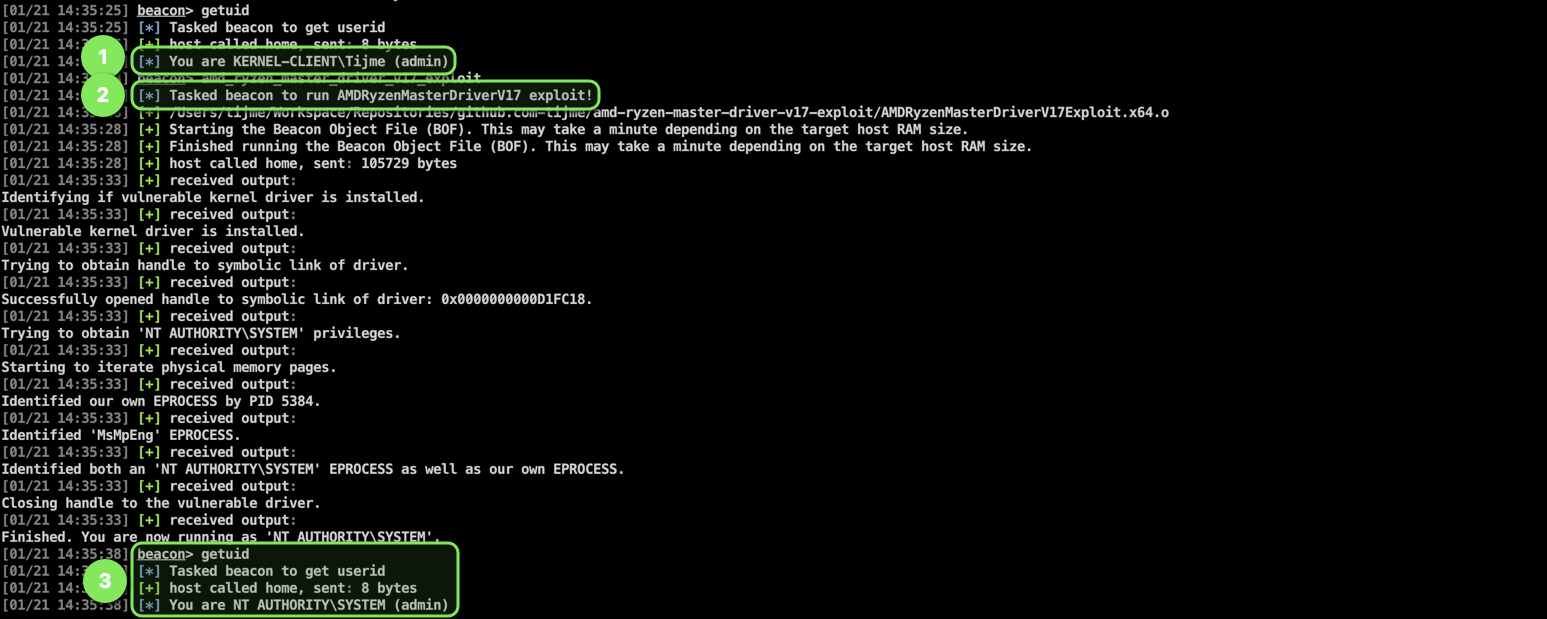 tijme/amd-ryzen-master-driver-v17-exploit
Cobalt Strike (CS) Beacon Object File (BOF) for kernel exploitation using AMD's Ryzen Master Driver (version 17).
 b1ack0wl/miniupnpd_poc
Read out-of-bounds PoC for miniupnpd <= v2.1
 theopaid/cve-2026-66729-out-of-bounds-read-in-facil.io-mime-parser-leads-to-server-crash
Security Advisory: Out-of-Bounds Read in facil.io MIME Parser leads to Server crash
 theopaid/cve-2026-66730-infinite-loop-dos-in-facil.io-mime-parser
Security Advisory: Infinite Loop DoS in facil.io MIME Parser (Partial Boundary)
 theopaid/cve-2026-66731-negative-chunk-size-parsing-causes-memory-corruption-leading-to-server-crash
Security advisory for CVE-2026-66731 with root cause analysis, PoC exploit, and fix suggestions for facil.io HTTP/1.1 chunked encoding parser bug.
 wso2/carbon-identity-framework
Core framework for identity and access management, providing authentication, authorization, and identity governance capabilities for enterprise…