

owasp-ctf-in-a-box
 owasp/owasp-ctf-in-a-box
Self-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies
container-securityctfdevsecops+6
11
owasp/owasp-ctf-in-a-boxSelf-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies
 owasp/owasp-ctf
Self-hosted CTF control plane for security-learning events: team registration, live leaderboard, and patch-to-score, quiz, jeopardy, and AI challenge…
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
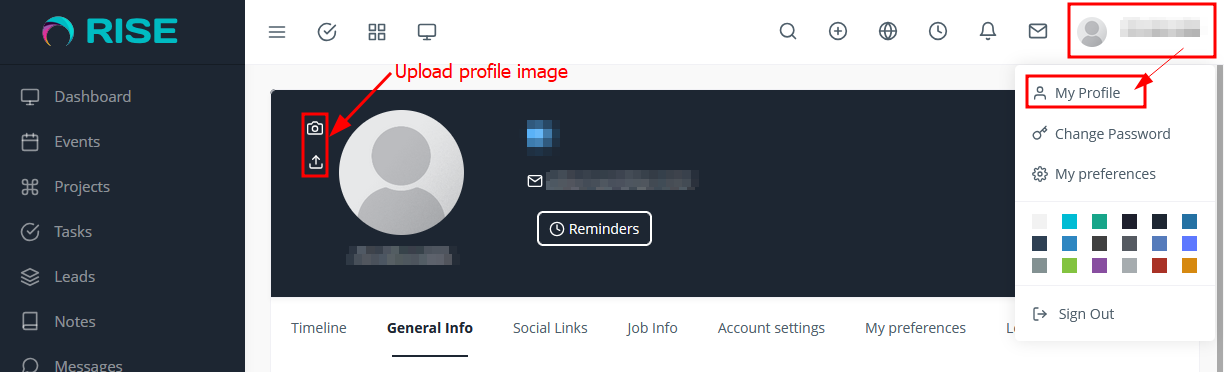 l4zyfox/rise-ultimate_project_manager_e_crm
CVE-2025-3855 - RISE Ultimate Project Manager - IDOR
 sunrayvision/vision-msi-thermal-control
MSI Modern 15H AI C1MGT-096IT Linux thermal management - Reverse engineered EC control with fan profiles and battery threshold
 bor8/cve-2022-34169
https://nvd.nist.gov/vuln/detail/CVE-2022-34169
 bolonobolo/cve-2018-14665
Proof-of-concept exploit for CVE-2018-14665, a local privilege escalation in Xorg on Linux distributions, with analysis and PoC for Red Hat.
 jas502n/cve-2018-14665
Local privilege escalation exploit for CVE-2018-14665 targeting X.Org Server on OpenBSD and Linux. Provides a proof-of-concept script to gain root…
 actions-security-demo/compromised-packages
StepSecurity owned org for analyzing compromised packages
 cameloo1/sharepoint-toolshell-micro-postmortem
Reproducible incident micro-postmortem for on-prem Microsoft SharePoint “ToolShell” (CVE-2025-53770): ATT&CK snapshot, “logs that matter” table,…
 mthbernardes/leakmanager
A tool to help you manage your leaks
 ekzhang/bore
Simple TCP tunnel in Rust that exposes local ports to a remote server, bypassing NAT firewalls. Lightweight, self-hostable, and easy to install.
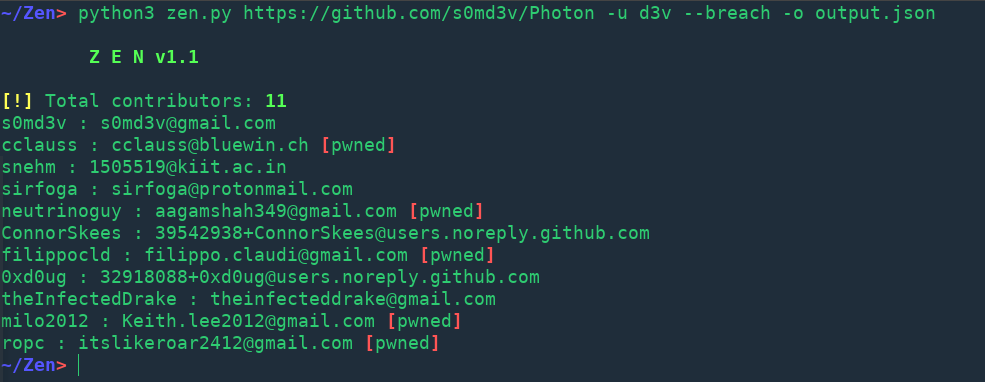 s0md3v/zen
CLI tool to find email addresses of GitHub users, contributors, and organization members, with multi-threading, JSON output, and breach checking via…
 boringtools/git-alerts
Tool to detect and monitor GitHub org users' public repositories for secrets and sensitive files
 soteria-security/365inspect
A PowerShell script that automates the security assessment of Microsoft 365 environments.
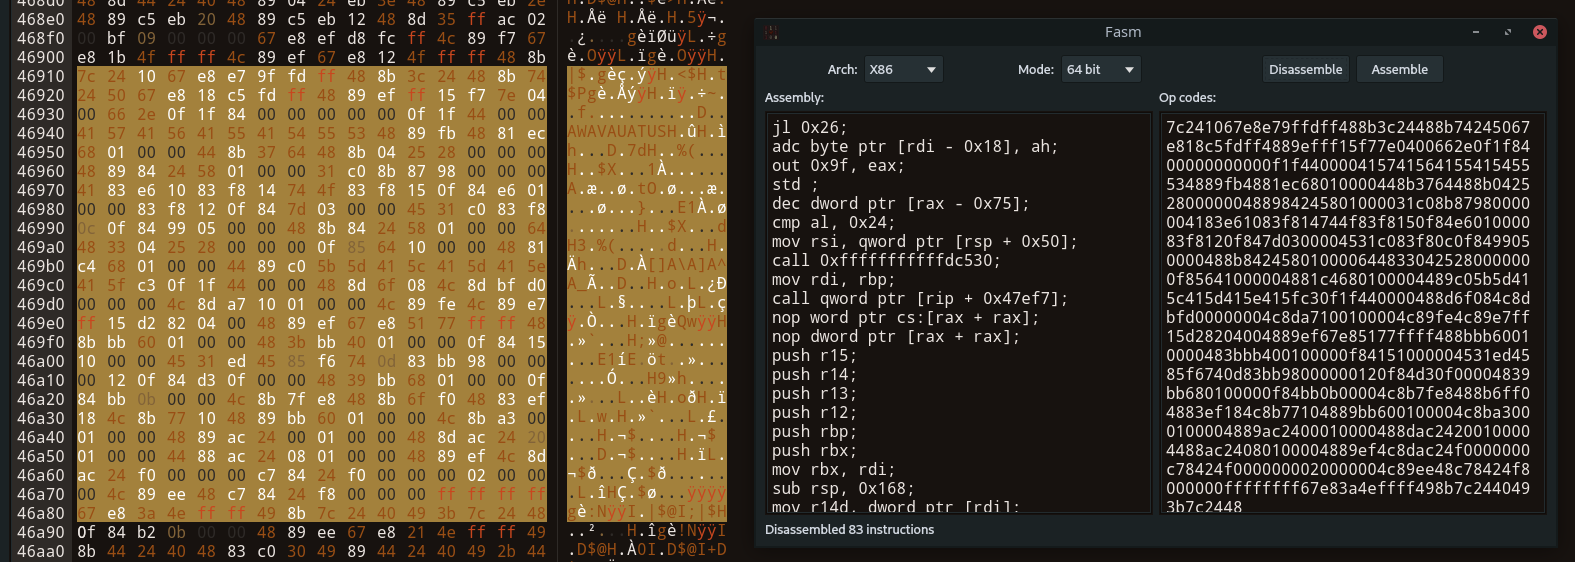 echo-devim/fhex
A Full-Featured HexEditor compatible with Linux/Windows/MacOS
 molly/gh-dork
Automated GitHub dorking tool that searches user, organization, and repository code for exposed secrets, credentials, and security misconfigurations…