
ghostlock-pfem10
 cxlfhx/ghostlock-pfem10
GhostLock (CVE-2026-43499 / IonStack) research for OPPO Find X5 Pro (PFEM10): exploit chain, progress, blocker log, and OPPO 5-series kernel notes
android-securitybinary-exploitationexploitation+7
cxlfhx/ghostlock-pfem10GhostLock (CVE-2026-43499 / IonStack) research for OPPO Find X5 Pro (PFEM10): exploit chain, progress, blocker log, and OPPO 5-series kernel notes
 imeiplus/galaxy-a37-root
CVE-2026-43499 exploit payload for Samsung Galaxy A37 (A376BXXS4AZG4, kernel 6.1.138-android14-11)
 xjoker/lenovo_y700_tb320fc_on_cve-2025-21479
In-memory kernel privilege escalation for Lenovo Legion Y700 2023 (TB320FC) exploiting CVE-2025-21479, a Qualcomm Adreno GPU SMMU flaw, with ReSukiSU…
 cflowsec/cve-2026-89026
Python PoC that forges a hard-coded HS256 JWT to exploit CVE-2026-89026 in Issabel pbxapi, enabling unauthenticated remote OS command execution via…
 huaguiqi/asus-i005-cve-2026-43499
CVE-2026-43499 (GhostLock) adaptation for ASUS ROG Phone 5S — UAF trigger + pselect stack reclaim, KASLR leak blocked
 ctdal/cve-2026-41940-poc
Exploits CVE-2026-41940, a cPanel/WHM authentication bypass, to gain root WHM access and run post-exploitation commands, account listing, and…
 keloke/dubbo-deserialization
[CVE-2020-1948] Apache Dubbo Provider default deserialization cause RCE
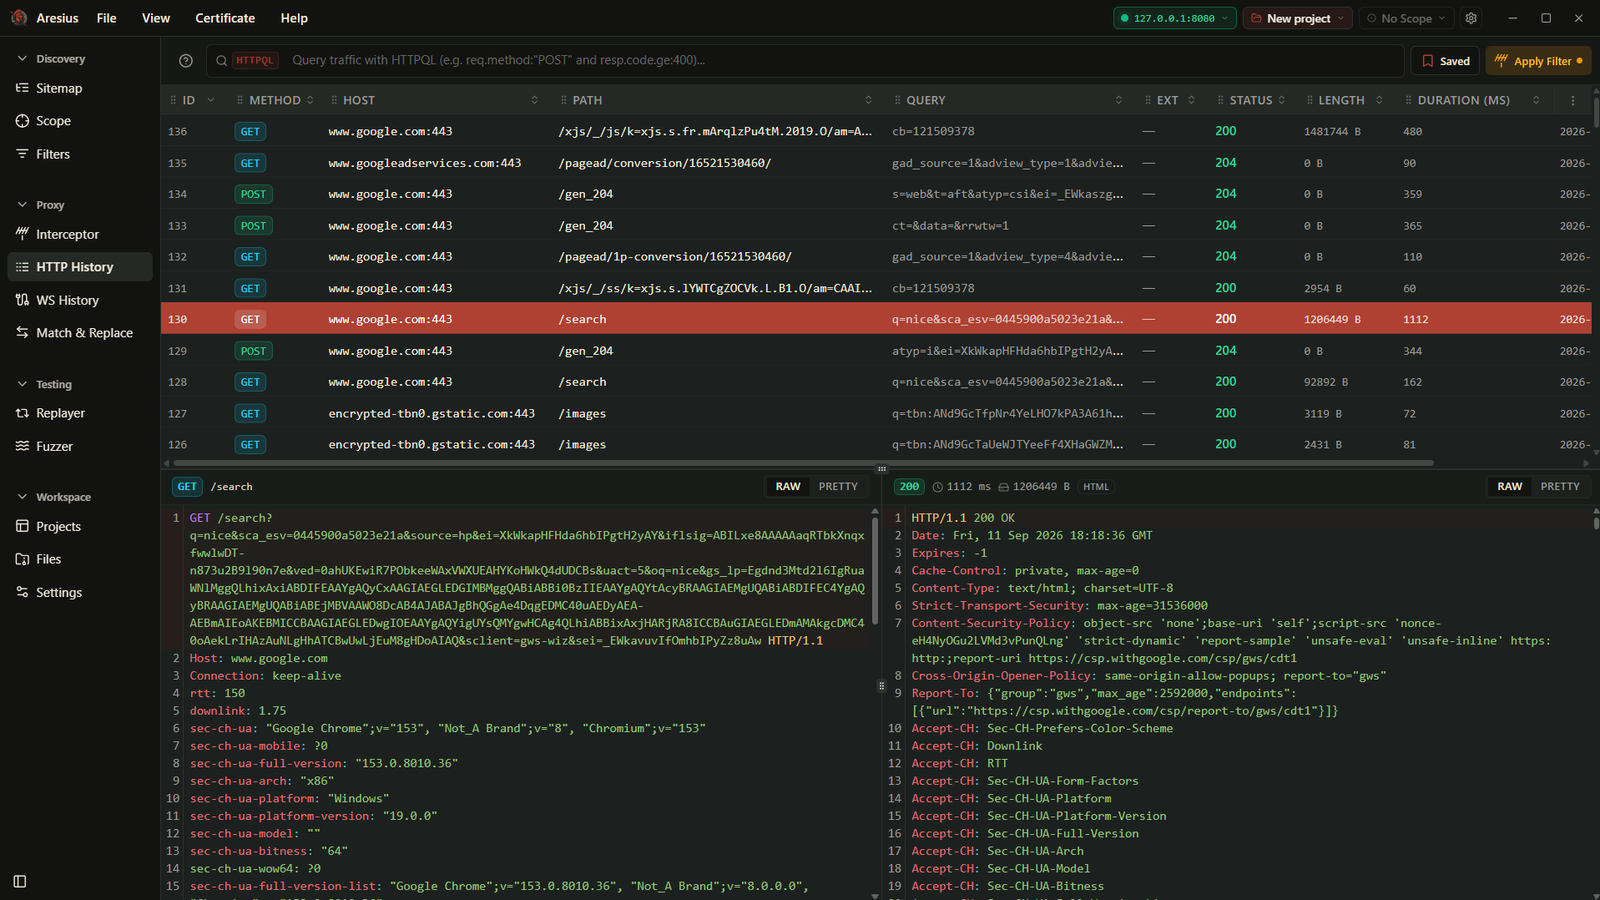 0xmarik/aresius
Native HTTP/HTTPS interception proxy for penetration testers and bug bounty hunters with live request tampering, request replay, high-speed fuzzing,…
 binzhwang/actguard
Pre-execution action-auditing defense that detects and masks indirect prompt injection in tool-using LLM agents using embedding retrieval and…
 udyz/cve-2026-86218
Proof-of-concept exploit for CVE-2026-86218, an unauthenticated RCE in N-able N-central via Struts BeanUtils, with version detection and command…
 d1n3sh-0x3/cve-2026-92247
Python PoC for CVE-2026-92247, an authenticated RCE in SynaptikCMS file manager via PHP upload and rename validation bypass.
 redzrush101/zte-blade-v40-vita-unlock
Unlocking the ZTE Blade V40 Vita (P606F02 / Unisoc UMS9230 / UFS) bootloader via CVE-2022-38694 - Linux scripts, the FBE post-unlock hang fix, and…
 hui191/cve-2026-43499-aak-an00
Honor WIN RT (AAK-AN00) CVE-2026-43499 temporary root - research notes
 1ndevelopment/ghostlock-s26
GhostLock (CVE-2026-43499) app for the Galaxy S26 series
 bardlaudian/cve-2025-24071
Dependency-free Python PoC generator for CVE-2025-24071 that crafts a malicious .library-ms file in a ZIP to trigger Windows Explorer NTLM hash…
 funfactor1/cve-2026-82090-18-years-all-versions-cvss-9.2-critical-the-pocket-forever-day
CVE-2026-82090 · CVSS 9.2 CRITICAL · 0-click stored XSS in Mozilla Pocket — all versions (v0 → v8.33.0.0) · 18-year forever-day · no patch · MITRE…
 oscar-collado/langflow-cve-2026-17633-poc
PoC for CVE-2026-17633 — Authenticated RCE in IBM Langflow OSS 1.0.0–1.10.3 via custom_component endpoint. Includes CVE-2026-17632 AST scanner bypass…
 qq1111111111/pentest-i021-poc-1789486727
Temporary proof-of-concept verification artifacts for CVE-2024-4367, a PDF.js arbitrary JavaScript execution vulnerability.