

CVE-2017-8759-exploits
 ashr/cve-2017-8759-exploits
Two versions of CVE-2017-8759 exploits
code-analysisexploitationmalware-analysis+2
2
ashr/cve-2017-8759-exploitsTwo versions of CVE-2017-8759 exploits
 wra7h/sharppn
C# PrintNightmare (CVE-2021-1675)
 winter3un/cve-2021-1675
Remote privilege escalation exploit for CVE-2021-1675 (PrintNightmare) with DLL injection and port forwarding support for remote execution.
 wh04m1001/cve-2022-3368
Proof-of-concept for local privilege escalation in Avira Security via arbitrary file move, exploiting junction points to load a malicious DLL into a…
 trailer2/dll-planting-slack-4.33.73-cve-2023-38820
DLL Planting in the Slack 4.33.73 - CVE-2023-38820
 trailer2/corsair---dll-planting-cve-2023-38822
DLL Planting in the Corsair iCUE v.5.3.102 CVE-2023-38822
 trailer2/cod-mw-warzone-2---cve-2023-38821
DLL Planting in the CoD MW Warzone 2 - CVE-2023-38821
 tiger3080/cve-2025-9267
Seagate Toolkit for Windows (Installer <2.35.0.6) is vulnerable to insecure DLL loading. The installer loads DLLs from the working directory without…
 hackerhouse-opensource/cve-2021-34527
CVE-2021-34527 AddPrinterDriverEx() Privilege Escalation
 saumyajeetdas/poc-of-cve-2022-36271
This is working POC of CVE-2022-36271
 dazzyddos/clickonceblobber
Weaponize signed .NET ClickOnce applications for initial access by hijacking a dependency DLL via AppDomainManager injection and loading a C# port of…
 ard33/cve-2026-4255
Proof-of-concept for CVE-2026-4255, a DLL side-loading privilege escalation in Thermalright TR-VISION HOME, demonstrating PATH-based planting of…
 3gstudent/cve-2017-8464-exp
Support x86 and x64
 0xkickit/icue_dllhijack_lpe-cve-2024-22002
Proof-of-concept exploit for CVE-2024-22002, demonstrating local privilege escalation via DLL hijacking in CORSAIR iCUE's update service to run code…
 aungsoepaing/cve-2024-39069
CVE-2024-39069
 1neptune/chimera
Rust-based DLL hijacking loader for MobaXterm (CVE-2026-6421) with persistence
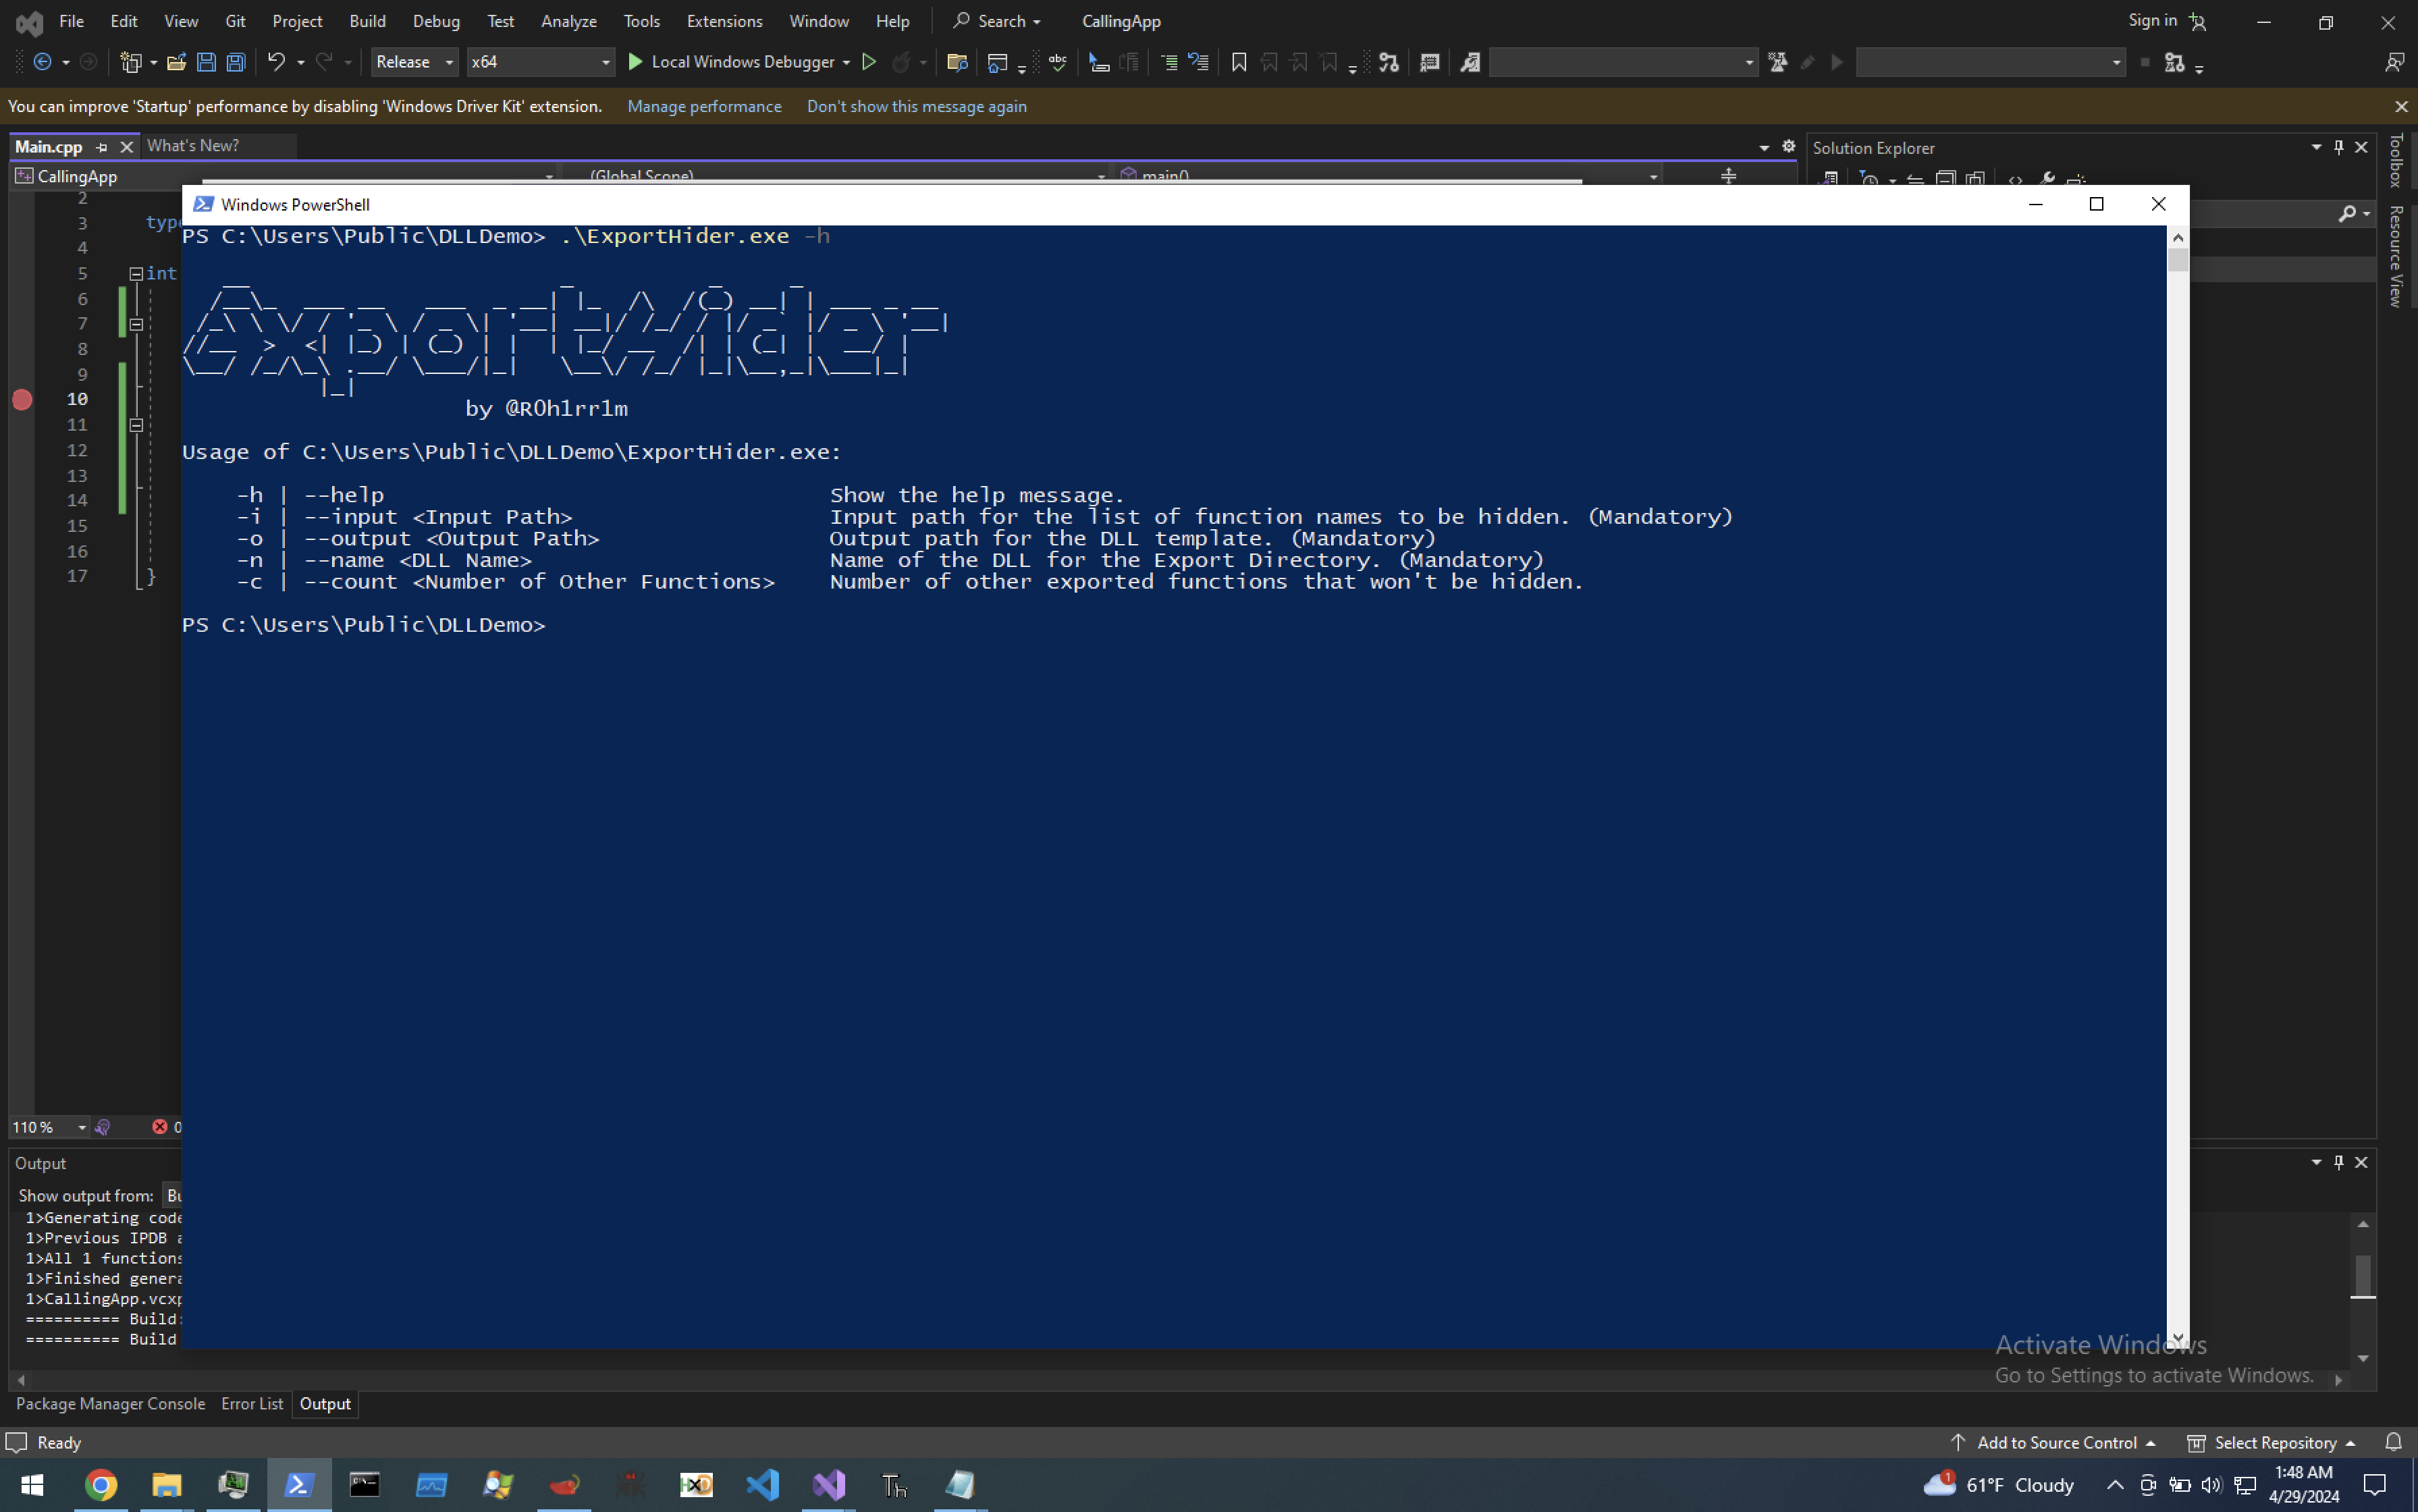 frkngksl/exporthider
ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.
 adem-hosni/mappedimagesdetector
Lightweight native Windows memory scanner for AV/EDR platforms, detecting suspicious mapped images and manual DLL injection techniques by IAT thunk