
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
355 results
meshdeck preview

meshdeck

GitHubadminempire/meshdeck

MeshDeck port for Arch Linux ARM - Wilson

command-and-controlexploitationlateral-movement+5
12 years ago
smbexec preview

smbexec

GitHubbrav0hax/smbexec

Rapid psexec-style attack tool using Samba for remote command execution, credential dumping, and lateral movement across Windows networks with hash…
command-and-controlexploitationlateral-movement+6
26211 years ago
DHCPig preview

DHCPig

GitHubkamorin/dhcpig

DHCP exhaustion script written in python using scapy network library

exploitationfuzzingnetwork-security+3
3547 days ago
ARPwner preview

ARPwner

GitHubntrippar/arpwner

ARP spoofing and network packet manipulation tool for man-in-the-middle attacks, traffic interception, and LAN reconnaissance using Python and pcap.
dns-analysisinformation-gatheringnetwork-security+3
9214 years ago
rosemary preview

rosemary

GitHubblue0x1/rosemary

Rosemary: Cross-platform kernel-level pivoting over QUIC. No TUN/TAP. No proxychains. No proxy settings.
command-and-controldns-analysislateral-movement+4
141 month ago
nacker preview

nacker

GitHubcarmaa/nacker

Nacker is a tool to circumvent 802.1x Network Access Control (NAC) on a wired LAN. Nacker will help you locate any non-802.1x configurable hosts on…

network-access-controlnetwork-securitypenetration-testing+2
10511 years ago
sliver-gui preview

sliver-gui

GitHubmr-in4inci3le/sliver-gui

A desktop operator console for Sliver C2, built with Wails. Provides a native, lightweight GUI interface for Sliver by directly interfacing with its…
command-and-controlexploitationlateral-movement+6
2171 month ago
CnC-Botnet-in-Python preview

CnC-Botnet-in-Python

GitHubmarcorosa/cnc-botnet-in-python

C&C Botnet written in Python with fabric
command-and-controllateral-movementpayload-development+4
344 years ago
SMBRat preview

SMBRat

GitHuboperatorequals/smbrat

A Windows Remote Administration Tool in Visual Basic with UNC paths
command-and-controlexploitationlateral-movement+8
227 years ago
GoAT preview

GoAT

GitHubpetercunha/goat

🐐 GoAT (Golang Advanced Trojan) is a trojan that uses Twitter as a C&C server
command-and-controlexploitationlateral-movement+7
2619 years ago
CVE-2026-6875-PoC-Exploit preview

CVE-2026-6875-PoC-Exploit

GitHubtc4dy/cve-2026-6875-poc-exploit

CVE-2026-6875 ServiceNow Pre-Auth RCE Framework 🔥 JS Injection → Sandbox Escape → RCE → Root. Features: --detect, --exec, reverse/interactive shell,…
exploitationlateral-movementpenetration-testing+7
32 months ago
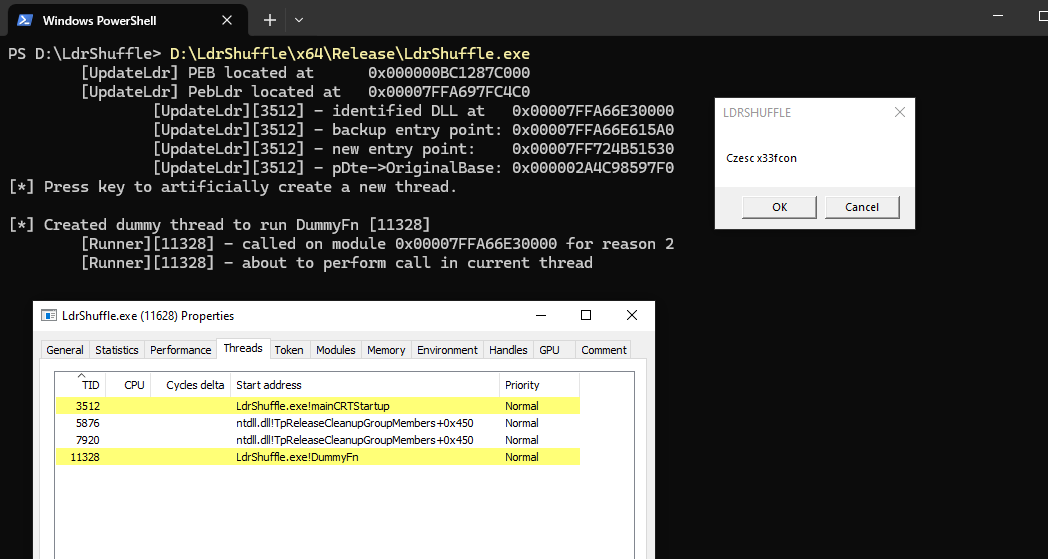
LdrShuffle preview

LdrShuffle

GitHubrwxstoned/ldrshuffle

Code execution/injection technique using DLL PEB module structure manipulation

binary-exploitationcode-analysisexploitation+6
2871 year ago
printerbugnew preview

printerbugnew

GitHubdecoder-it/printerbugnew

The DCERPC only printerbug.py version

authenticationcommand-and-controlexploitation+5
23410 months ago
RAITrigger preview

RAITrigger

GitHubrteccybersec/raitrigger

Local SYSTEM auth trigger for relaying
authenticationexploitationlateral-movement+2
1731 year ago
RpcProxyInvoke preview

RpcProxyInvoke

GitHubklezvirus/rpcproxyinvoke

Simple POC library to execute arbitrary calls proxying them via NdrServerCall2 or similar
binary-exploitationcommand-and-controlexploitation+8
1382 years ago
SockTail preview

SockTail

GitHubyeeb1/socktail

Lightweight Go binary that joins a device to a Tailscale network and exposes a local SOCKS5 proxy for ephemeral red team access. Supports…
command-and-controllateral-movementnetwork-security+4
57111 months ago
MiscTools preview

MiscTools

GitHubrasta-mouse/misctools

Miscellaneous Tools
command-and-controllateral-movementpenetration-testing+3
2695 years ago
injection preview

injection

GitHubjymcheong/injection

Windows process injection methods

binary-exploitationexploitationlateral-movement+3
98 years ago
Previous1…567…20Next