
ESP32-Bit-Pirate
 geo-tp/esp32-bit-pirate
A Hardware Hacking Tool with Web-Based CLI That Speaks Every Protocol
bluetooth-securitydebuggersembedded-systems-security+5
5.9k
geo-tp/esp32-bit-pirateA Hardware Hacking Tool with Web-Based CLI That Speaks Every Protocol
 earlephilhower/arduino-pico
Raspberry Pi Pico Arduino core, for all RP2040 and RP2350 boards
 riccardocataldi/access-point
Rogue open Wi-Fi AP for controlled traffic capture using hostapd, dnsmasq, and iptables NAT. Enables real-time client monitoring, DNS/DHCP logging,…
 razkom/ghost
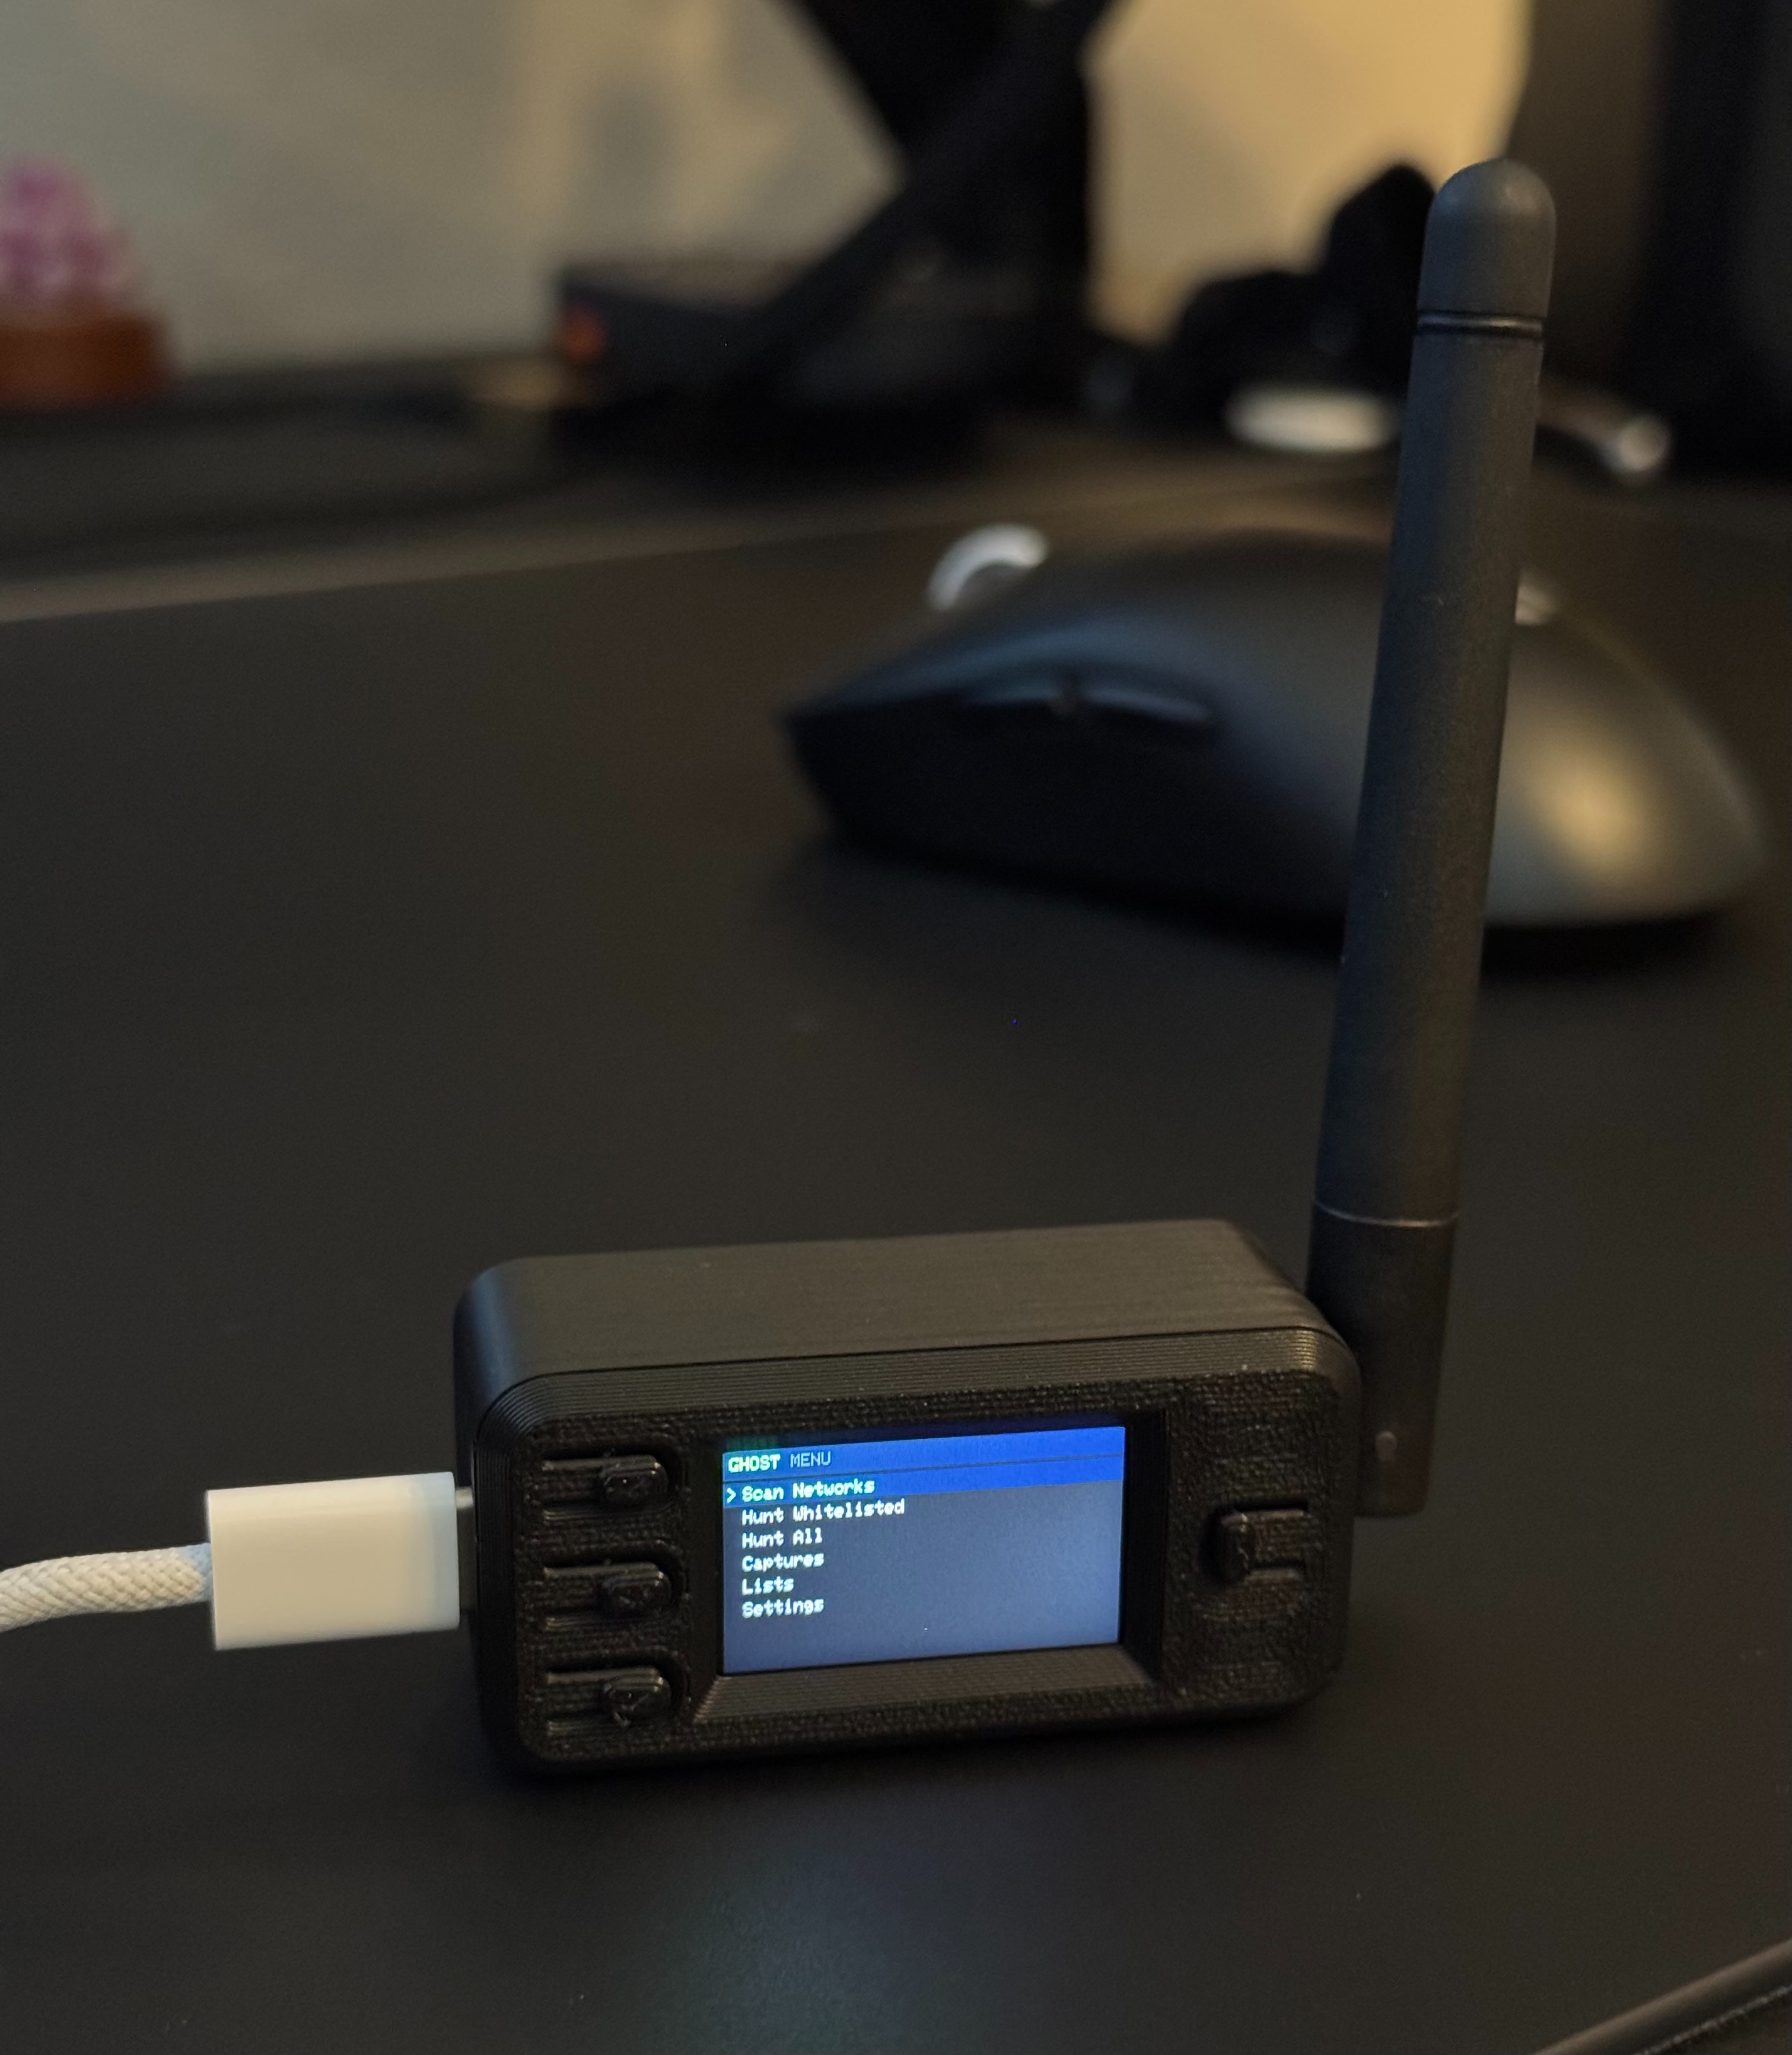
ESP32-S3 firmware for standalone WPA/WPA2 handshake capture and deauthentication testing via TFT UI, with pcap download over WiFi AP.
 matheus-garbelini/esp32_esp8266_attacks
Proof of Concept of ESP32/8266 Wi-Fi vulnerabilties (CVE-2019-12586, CVE-2019-12587, CVE-2019-12588)
 baiyibai/pico-usb-wifi
Firmware for Raspberry Pi Pico W that creates a driverless USB Wi-Fi adapter with transparent layer-2 bridging, WPA2/WPA3 authentication, and…
 rubenbe/opensoho
Lightweight OpenWRT device management platform for small networks. Centralized configuration, monitoring, and WiFi management for 2–20 devices with…
 francescopace/espectre
ESPectre - Motion detection system based on Wi-Fi spectre analysis (CSI), with Home Assistant integration.
 veteranop/trackem
Passive Device Tracker (Android)TrackEm Mobile is a real-time, passive Wi-Fi + Bluetooth LE probe-request scanner designed for OSINT, red-team ops,…
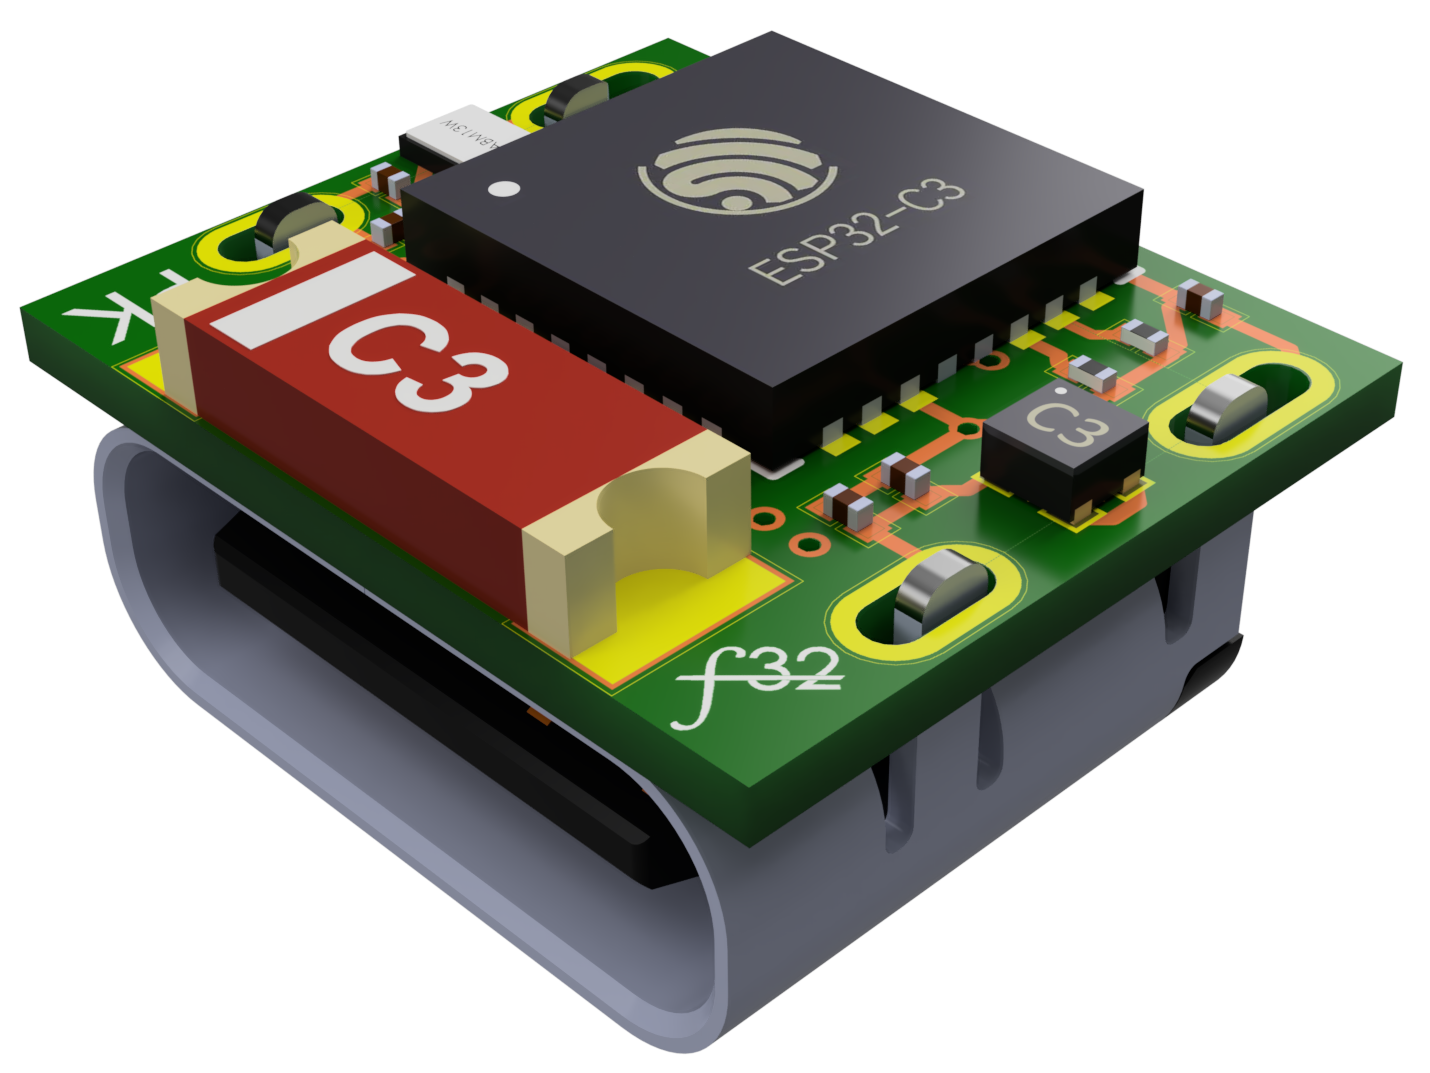 pegork/f32
Ultra-compact ESP32-C3 development board designed for embedded security research, featuring a captive portal example with WiFi scanning and LED…
 k3vinlusec/r7000_httpd_bof_cve-2020-15416
Walkthrough of CVE-2020-15416 buffer overflow exploit for Netgear R7000 router, including QEMU user-mode debugging environment setup and detailed…
 joelczk/cve-2025-52688
Proof-of-concept exploits for CVE-2025-52688: unauthenticated command injection and arbitrary file read vulnerabilities in Alcatel AP13161 enterprise…
 hanianis/cve-2025-63353
A vulnerability in fiberhome GPON ONU HG6145F1 RP4423 allows the device's factory default Wi-Fi password (WPA/WPA2 pre-shared key) to be predicted…
 h4ckusaur/cve-2024-57366
Remote code execution exploit for CVE-2024-57366 targeting WAVLINK routers via MAC address validation bypass and command injection, with automatic…
 embedi/ble_norton_core
Proof-of-concept exploit demonstrating command injection via BLE service in Norton Core Secure WiFi Router (CVE-2018-5234). Includes SSH access setup…
 dybrkr/wifi_leak
Proof-of-concept exploit for CVE-2018-4084, a WiFi credential leak vulnerability in macOS High Sierra, demonstrating interception of plaintext Wi-Fi…
 d4rkcat/killosx
use the Apple CoreText exploit (CVE-2012-3716) and launch an AP to affect all devices within wifi range
 fengchenzxc/cve-2020-28148
Wi-Fi portal authentication bypass exploit using MAC address spoofing to gain unauthorized network access, demonstrated on enterprise AC and AP…