delirium-ai-safety-benchmark

A diagnostic framework for measuring LLM vulnerability to Affective Contextual Erosion (ACE) and related liminal attack vectors. **Delirium** is not…

A diagnostic framework for measuring LLM vulnerability to Affective Contextual Erosion (ACE) and related liminal attack vectors. **Delirium** is not…

is an advanced security research framework designed to model, analyze, and demonstrate Local Privilege Escalation (LPE) mechanics associated with…

👾 CVE-2026-60206 - Oracle WebLogic SAML Auth Bypass Exploit Framework ⚡Bash & Python versions. Features: --detect safe check, --exploit…

Discuz! X5.0 Authentication Bypass Exploit Framework (CVE-2026-49952) - Critical vulnerability allowing unauthenticated database backup access via…

MCP Server for Metasploit

A repository that contains all the working PoC I have crafted for known CVEs, and details on any ongoing research I am currently doing (mostly Iot…

AI Smart Contract Security Analysis and PoC Generation Framework

🛡️ AI-powered portable cybersecurity & pentesting assistant built on ESP32-S3 (LilyGO T-Embed CC1101 & T-Watch S3). Features voice-controlled RF…

about CobaltStrike

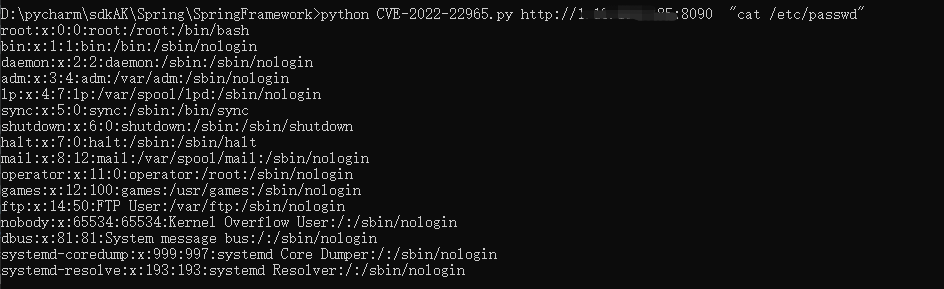
Python-based exploit for CVE-2022-22965 (Spring4Shell) with environment checks for Spring Framework, JDK version, Tomcat, and AccessLog configuration.

CVE-2017-11882(通杀Office 2003到2016)

Spring Framework RCE exploit (CVE-2022-22965) with analysis code and educational walkthrough for understanding the vulnerability and exploitation…

PrintNightMare LPE提权漏洞的CS 反射加载插件。开箱即用、通过内存加载、混淆加载的驱动名称来ByPass Defender/EDR。


Python exploit for Spring Framework CVE-2022-22965 remote code execution with webshell deployment and Burp payload support for penetration testing.

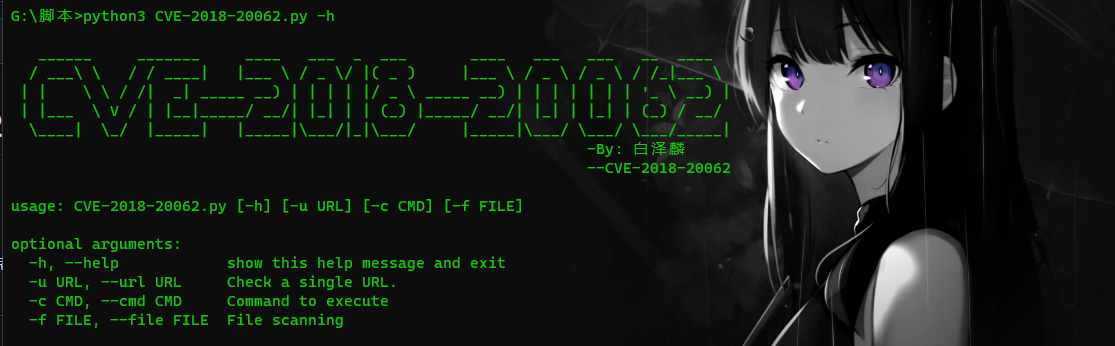
Exploit for CVE-2018-20062 targeting ThinkPHP 5.0.23, designed for vulnerability verification and penetration testing of web applications running the…

Detailed analysis and proof-of-concept exploit for CVE-2017-9822, an XXE/insecure deserialization vulnerability in DotNetNuke CMS leading to remote…

Exploit for MS12-020 (CVE-2012-0002) targeting Windows RDP vulnerability, with Metasploit integration for remote code execution and penetration…