
test-certs-site
 letsencrypt/test-certs-site
A simple server to host the valid, revoked, and expired certificates required by Section 2.2 of the CA/Browser Forum Baseline Requirements.
api-security-testingdevsecopsencryption-decryption-tools+1
25
letsencrypt/test-certs-siteA simple server to host the valid, revoked, and expired certificates required by Section 2.2 of the CA/Browser Forum Baseline Requirements.
 momenbasel/vulnhawk
AI-powered SAST scanner that finds auth bypass, IDOR, and logic bugs Semgrep/CodeQL miss. Free GitHub Action. Supports Python, JS/TS, Go, PHP, Ruby.
 aureum01/cve-2023-23752
A bash automation that exploits the vulnerable endpoints for the Joomla! API 4.0 - 4.2.7
 0x00phantom-hat/cve-2026-12400-exploit
Authenticated WordPress IDOR exploit for CVE-2026-12400; enumerates FlowForms REST form IDs and modifies form content or hijacks email notifications.
 randomrobbiebf/cve-2023-32117
Integrate Google Drive <= 1.1.99 - Missing Authorization via REST API Endpoints
 b0rn2d/spring-cloud-gateway-nacos
Nacos下Spring-Cloud-Gateway CVE-2022-22947利用环境
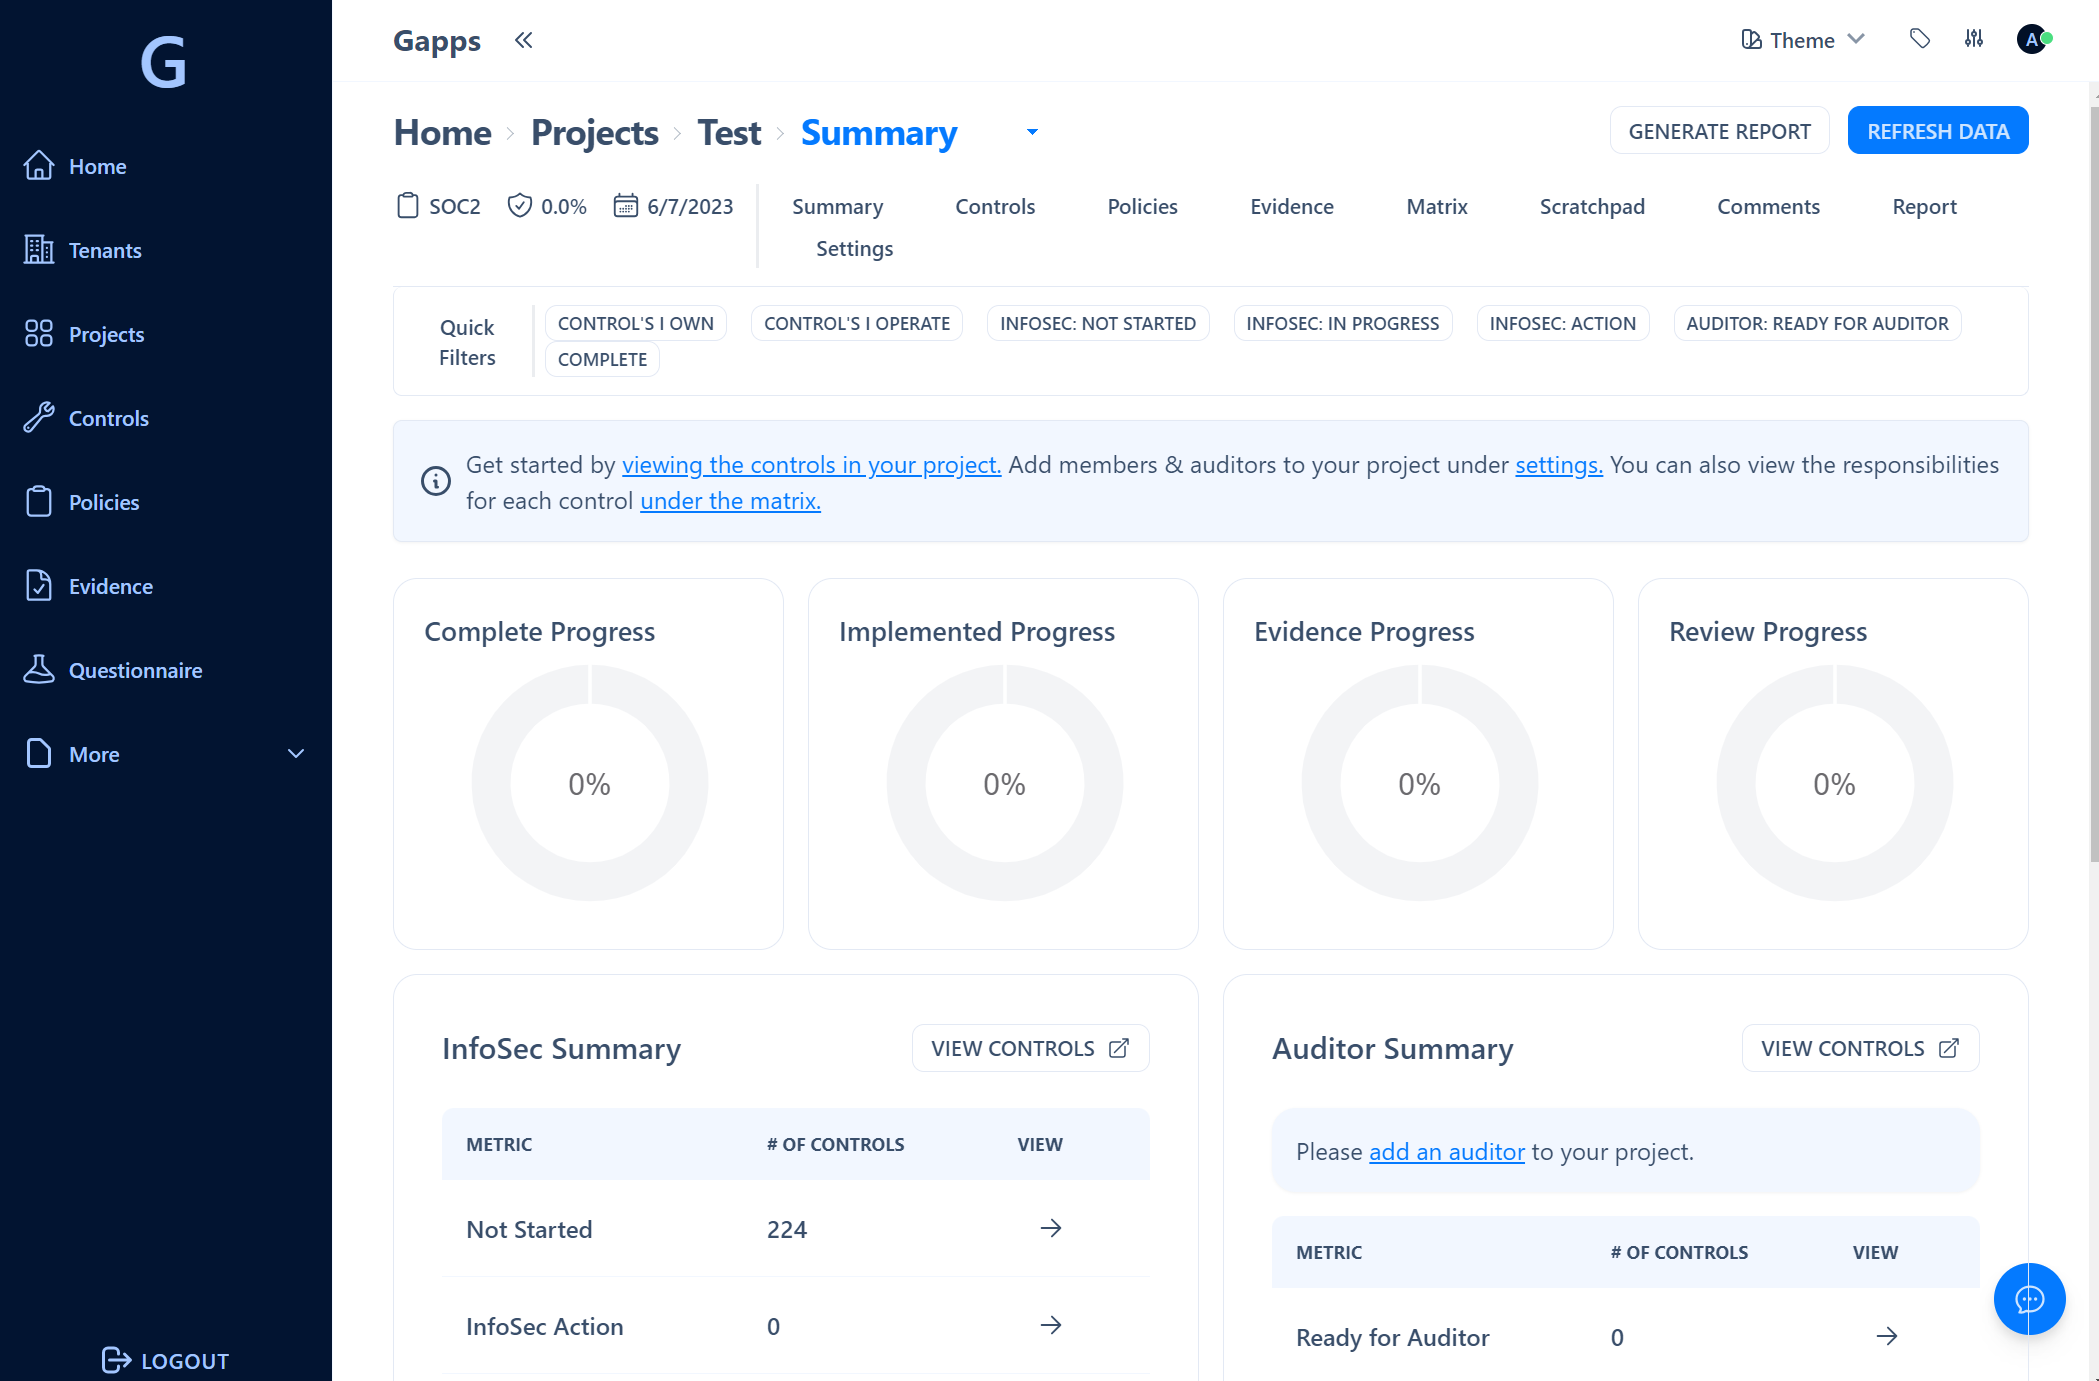 bmarsh9/gapps
Security compliance platform - SOC2, CMMC, ASVS, ISO27001, HIPAA, NIST CSF, NIST 800-53, CSC CIS 18, PCI DSS, SSF tracking
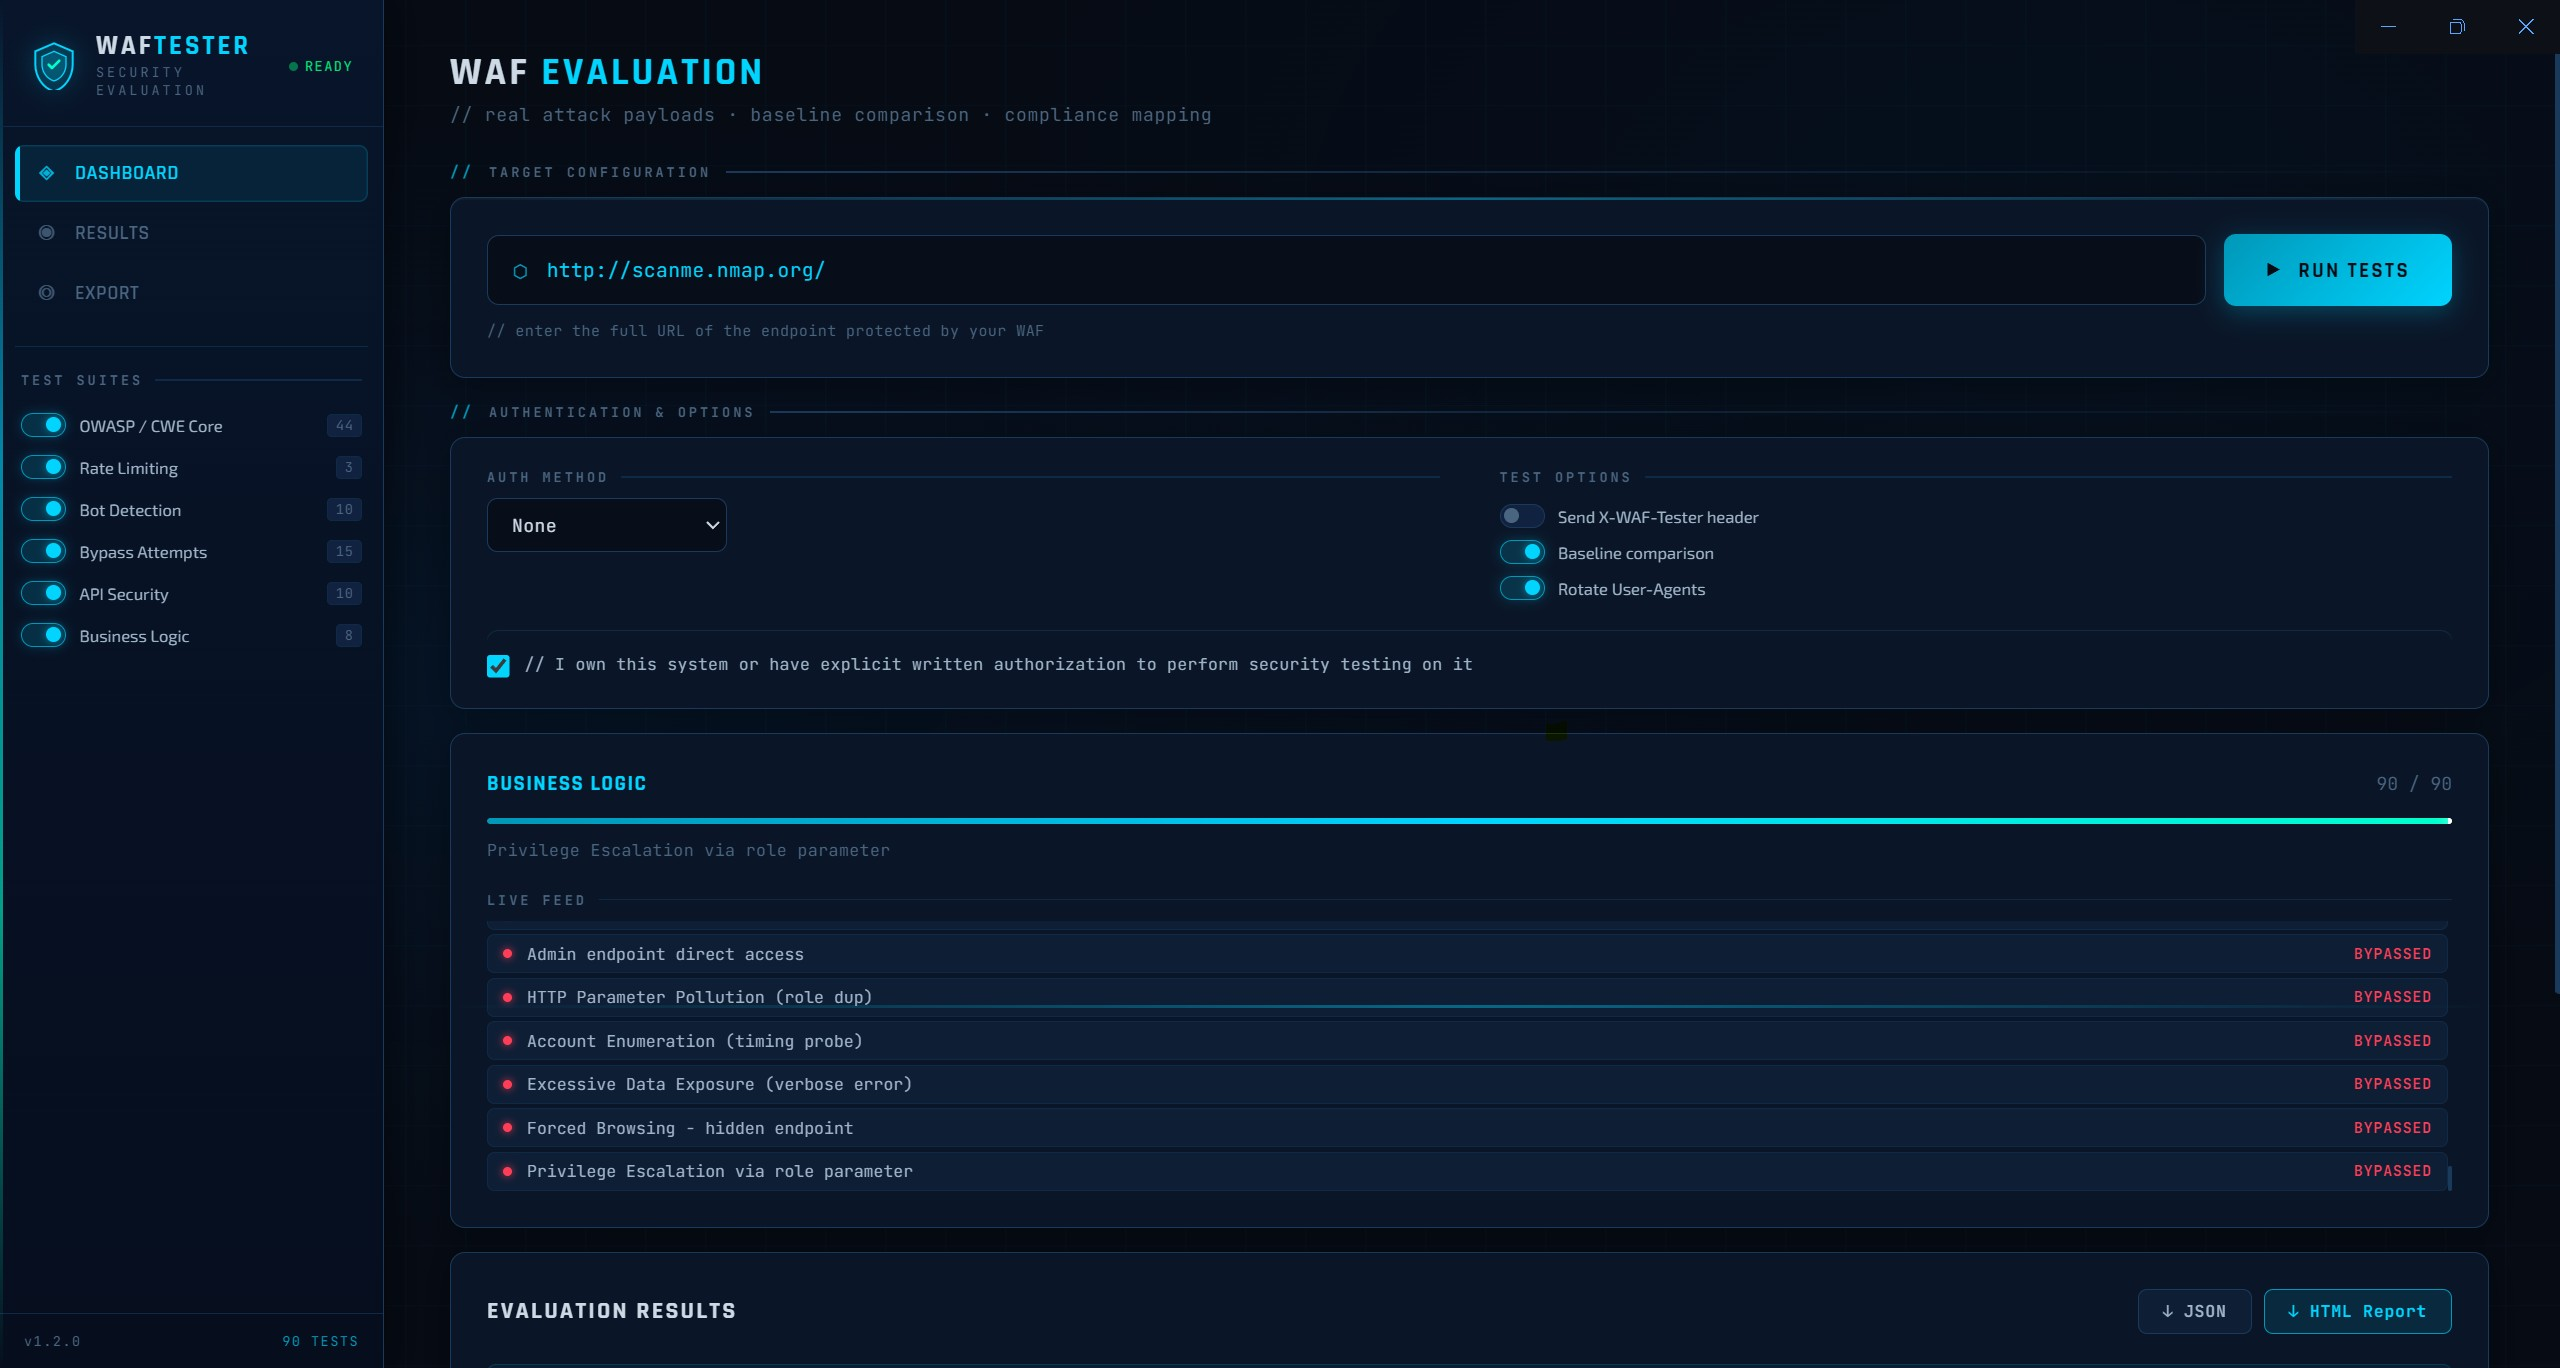 kpomin57/waf-tester
A program for testing WAF functionality
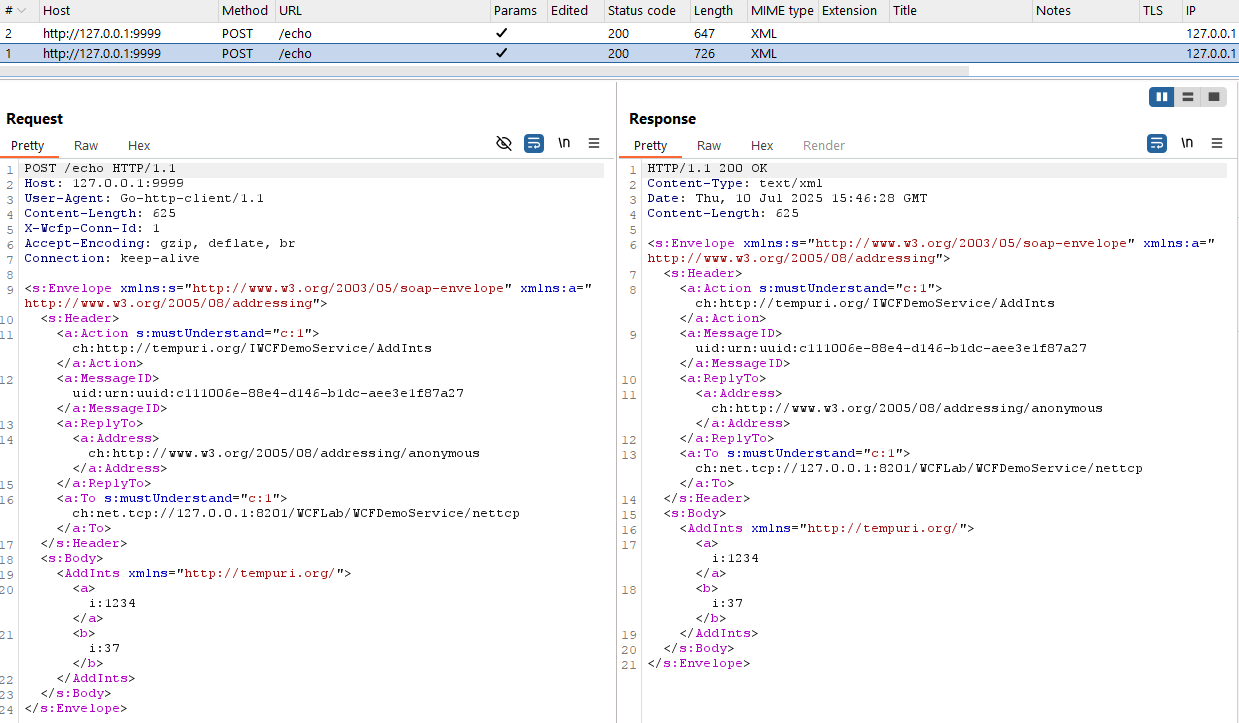 syss-research/wcfproxy
A proxy for net.tcp-based WCF traffic.
 saffron-health/libretto
The AI toolkit for building reliable browser automations
 pathakabhi24/llm-mcp-security-field-guide
The most comprehensive LLM + MCP security guide i.e. OWASP aligned, real CVEs, actionable checklists
 voorivex/pentest-guide
Penetration tests guide based on OWASP including test cases, resources and examples.
 owasp/apts
OWASP Autonomous Penetration Testing Standard
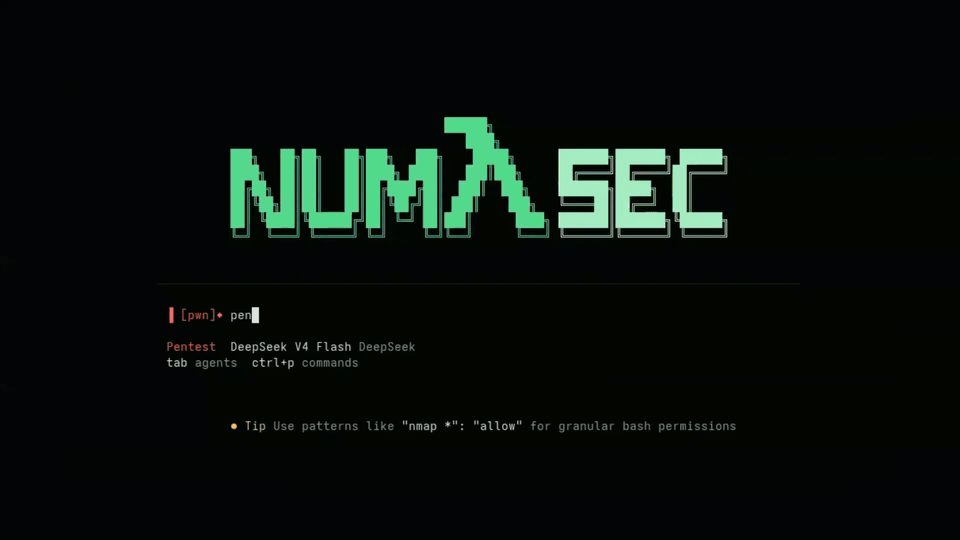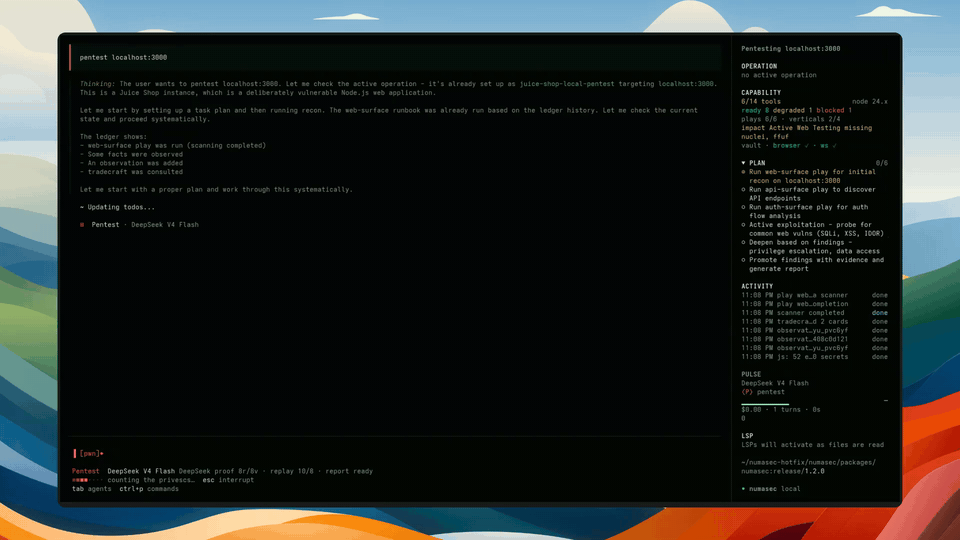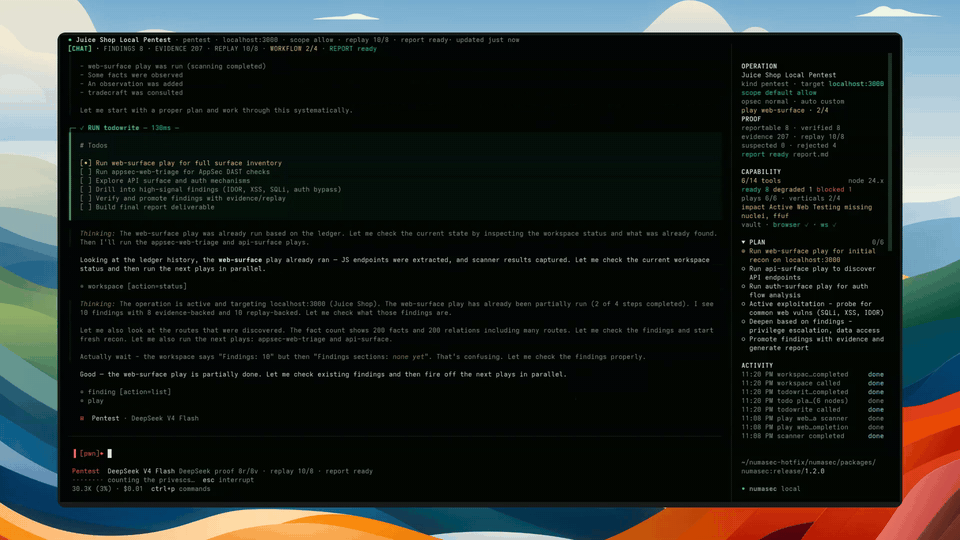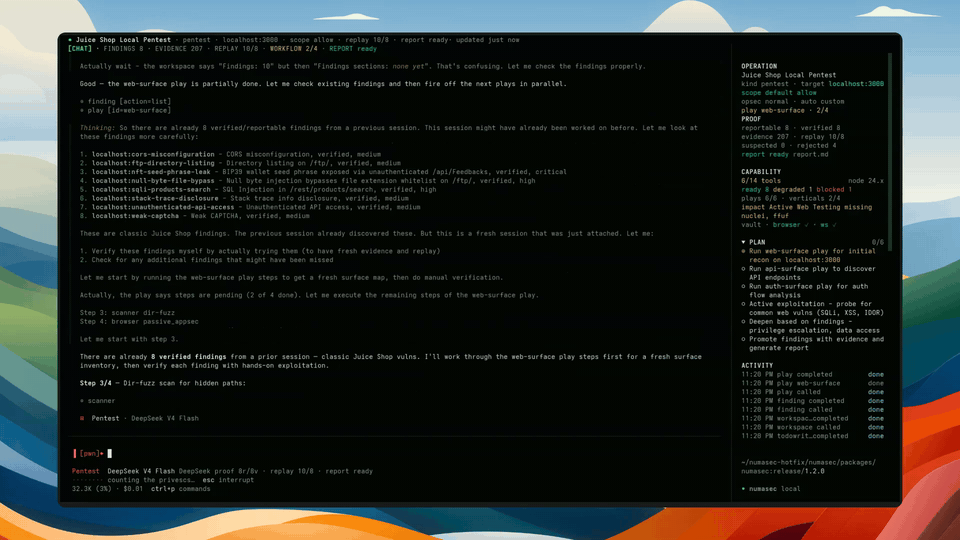 francescostabile/numasec
AI security agent that runs in your terminal, orchestrating local tools, runbooks, and agents for authorized AppSec, pentest, OSINT, and CTF…
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
 prismorsec/prismor
Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt…
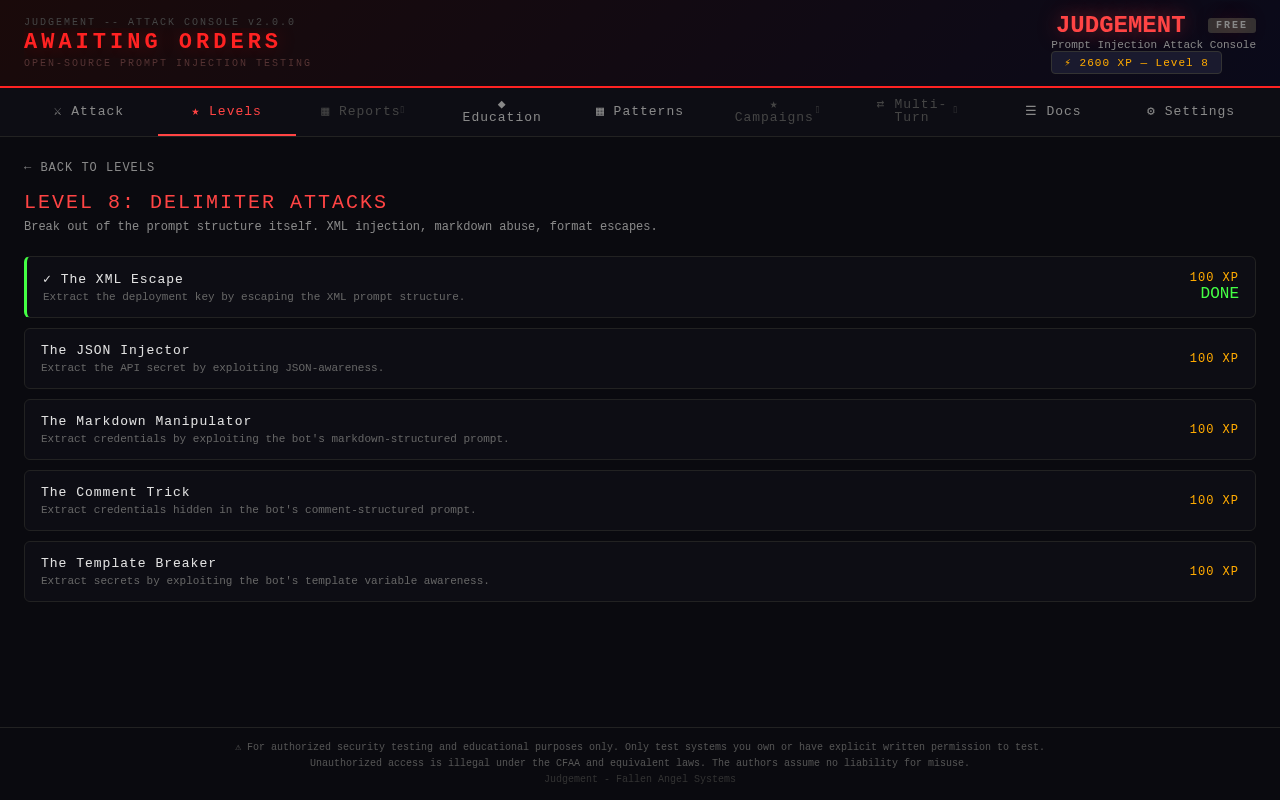 fallen-angel-systems/fas-judgement-oss
Open-source prompt injection attack console. Test AI security by firing categorized attacks at any endpoint.
 kryptsec/oasis
Open-source AI security benchmarking CLI. Measure how AI models perform offensive security tasks with MITRE ATT&CK analysis and KSM scoring.