

file-away-exploit
 whattheslime/file-away-exploit
Remote code execution exploit scripts for the WordPress File-Away plugin (CVE-2025-2512 & CVE-2025-2539)
exploitationinformation-gatheringpayload-development+5
1
whattheslime/file-away-exploitRemote code execution exploit scripts for the WordPress File-Away plugin (CVE-2025-2512 & CVE-2025-2539)
 oyst3r1ng/cve-2025-30567
Unauthorized Arbitrary File Download in WordPress WP01
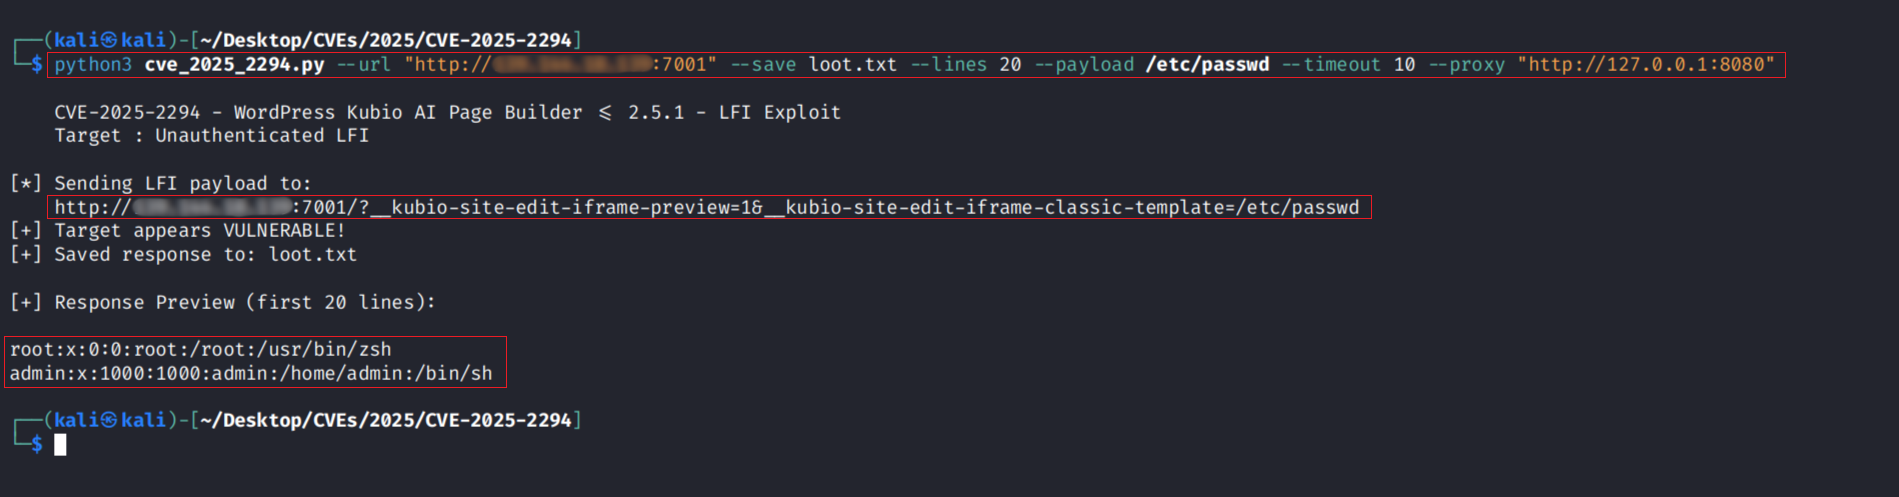 r0otk3r/cve-2025-2294
Python exploit script for CVE-2025-2294, an unauthenticated Local File Inclusion vulnerability in WordPress Kubio AI Page Builder ≤ 2.5.1. Supports…
 nxploited/cve-2024-56071
Simple Dashboard <= 2.0 - Unauthenticated Privilege Escalation
 evillm/cve-2024-45590-poc
Proof-of-concept exploit for CVE-2024-45590, demonstrating unauthenticated remote code execution in a WordPress plugin via arbitrary file upload.…
 kiphuong/cve-2024-3552
Proof-of-concept for CVE-2024-3552: SQL injection in WordPress Web Directory Free plugin (pre-1.7.0). Includes vulnerable code analysis, manual…
 kasoomi0228/cve-2024-25600-bricks-builder-wordpress
Automated exploit tool for CVE-2024-25600, enabling unauthenticated remote code execution on WordPress sites using the Bricks Builder plugin.…
 r0otk3r/cve-2024-25600
Python-based exploit for CVE-2024-25600 targeting Bricks Builder WordPress plugin RCE. Automates nonce extraction, payload injection, and arbitrary…
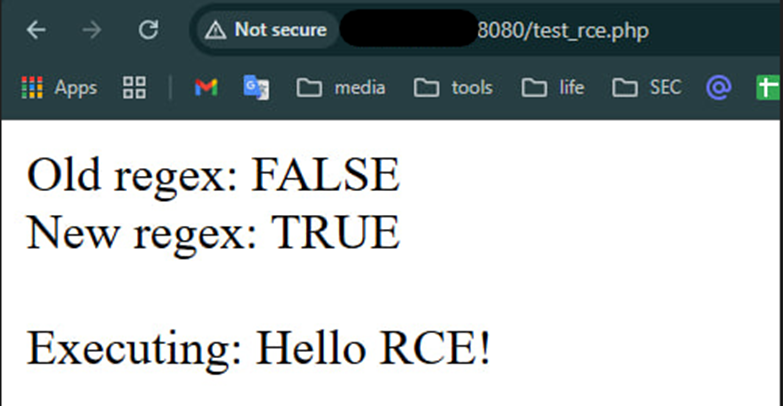 soltanali0/cve-2024-12877-exploit
Educational CVE-2024-12877 exploit demo for PHP Object Injection in GiveWP WordPress plugin. Includes root cause analysis, regex bypass techniques,…
 s3rgeym/cve-2020-9006
Exploit for CVE-2020-9006 targeting WordPress Popup-Builder plugin via SQL injection and PHP deserialization, with payload generation and Nmap…
 wpscanteam/wpscan
WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…
 ill-deed/cve-2025-34085-multi-target
Multi-target unauthenticated RCE scanner for CVE-2025-34085 affecting WordPress Simple File List plugin. Uploads, renames, and triggers PHP webshells…
 gh-ost00/cve-2024-27954
Automatic Plugin for WordPress < 3.92.1 Multiples Vulnerabilities
 fleetcaptain/everest-backup-cve-2025-11380
Proof-of-concept exploit for CVE-2025-11380 demonstrating unauthenticated backup access in the Everest Backup WordPress plugin, enabling security…
 w3bw/cve-2024-27956-rce-file-package
Exploit scripts and scanner for CVE-2024-27956, a WordPress plugin vulnerability, including a modified exploit with SSL verification bypass.
 tornad0007/cve-2024-25600-bricks-builder-plugin-for-wordpress
This tool is designed to exploit the CVE-2024-25600 vulnerability found in the Bricks Builder plugin for WordPress. The vulnerability allows for…
 anothersec/cve-2025-6440
WooCommerce Designer Pro 1.9.26 - Arbitrary File Upload
 0xwhoami35/cve-2025-2294
Python PoC for CVE-2025-2294, an unauthenticated Local File Inclusion in the Kubio AI Page Builder WordPress plugin (≤2.5.1), demonstrating arbitrary…