

CVE-2020-25273
 jonathanrey87/cve-2020-25273
Online Bus Booking System 1.0, there is Authentication bypass on the Admin Login screen in admin.php via username or password SQL injection.
authenticationeducationexploitation+3
jonathanrey87/cve-2020-25273Online Bus Booking System 1.0, there is Authentication bypass on the Admin Login screen in admin.php via username or password SQL injection.
 dsahen/cve-2023-22515-exp
cve-2023-22515的python利用脚本
 jeanback1/cve-2019-9053-exploit
Automated exploit for CVE-2019-9053, a time-based blind SQL injection in CMS Made Simple ≤2.2.9. Extracts admin credentials (username, email,…
 owasp/open-sammy
Web-based tool for assessing and tracking software security maturity using the OWASP SAMM and DSOMM models, with Docker support and automated mailing.
 d4vinci/twitter-info
A simple python script to grab twitter account info just by username or profile link
 bootstrapbool/xerteonlinetoolkits-rce
Unauthenticated Xerte Online Toolkits exploit. Requires knowing a valid username.
 atarantini/wpbf
Remotely test password strength of WordPress bloging software
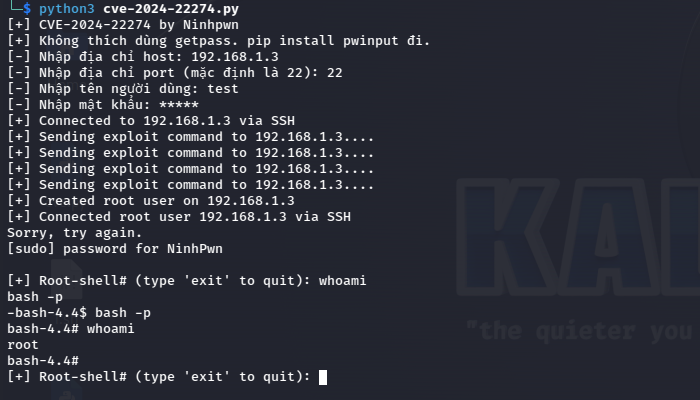 ninhpn1337/cve-2024-22274
Exploit for CVE-2024-22274 that creates a privileged user and spawns a root SSH shell on a target host using provided credentials.
 pentestfunctions/cve-2025-8088-multi-document
Exploit systems using older WinRAR without knowing their username (unlike other projects)
 r3dston3/cve-2023-23752
Proof-of-concept exploit for CVE-2023-23752 (Joomla 4.0.0-4.2.8) that extracts usernames and passwords via an information disclosure vulnerability.
 teambugsbunny/wpusersscan
Wordpress Username Enumeration /CVE-2017-5487,WordPress < 4.7.1 -
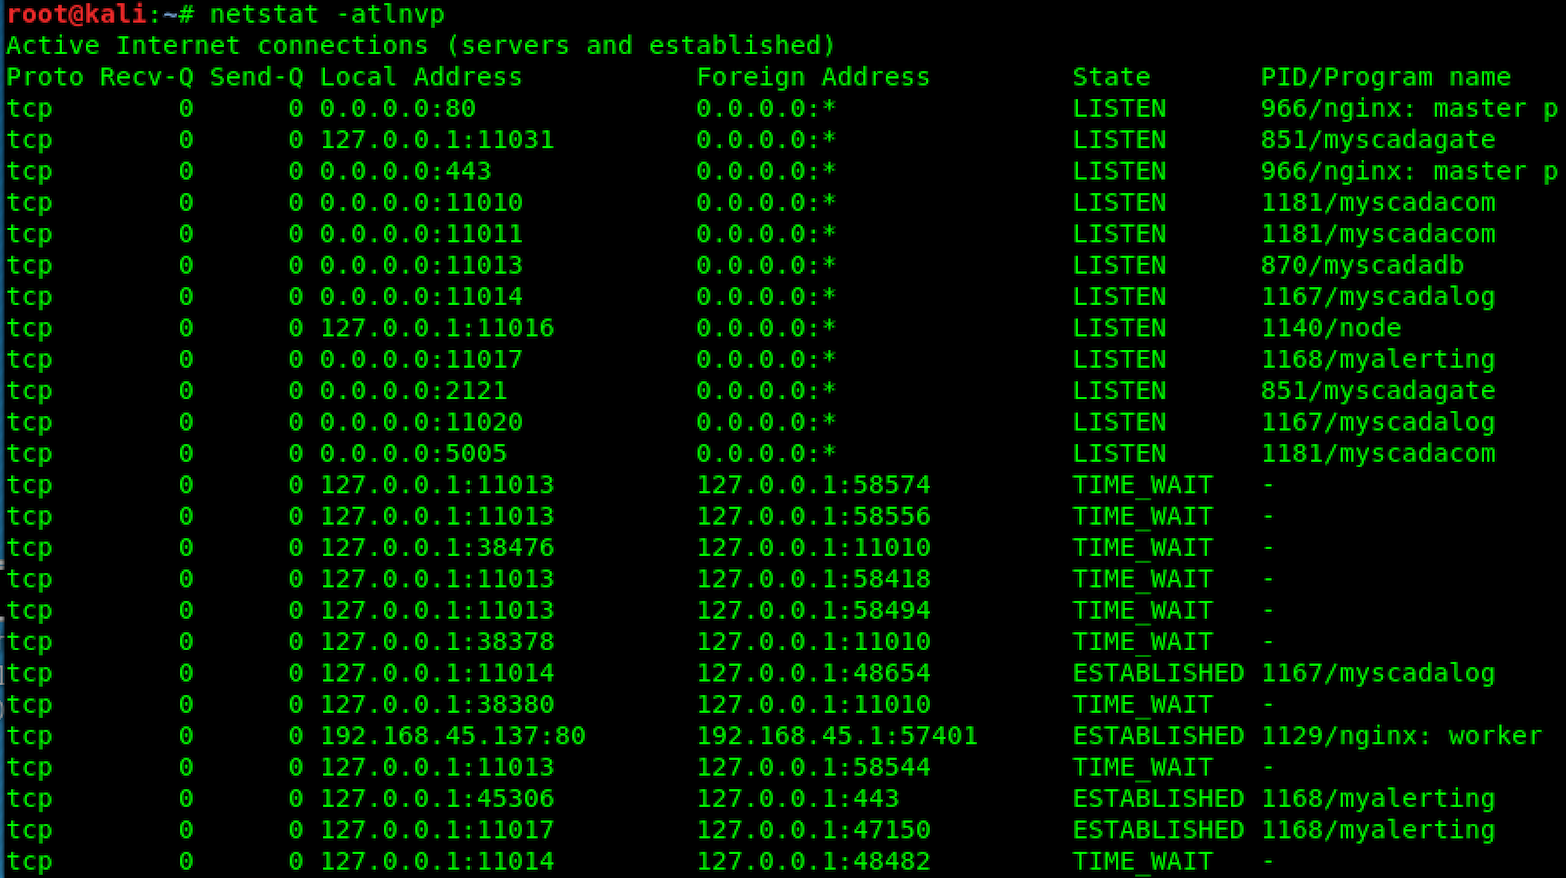 emreovunc/myscada-mypro-7-hardcoded-ftp-username-and-password
CVE-2018-11311 | mySCADA myPRO 7 Hardcoded FTP Username and Password Vulnerability
 machine-farmer/vicidial-cve-2024-8503-blind-sqli-poc
Unauthenticated time-based blind SQL injection PoC for VICIdial CVE-2024-8503, with metadata extraction, resumable scans, and strict safety limits.
 maxpl0it/unauthenticated-cve-2020-0796-poc
An unauthenticated PoC for CVE-2020-0796
 initroot/cve-2022-23342
Proof-of-concept for Active Directory username enumeration vulnerability in Hyland OnBase via login endpoint response differences, enabling…
 ofirhamam/oracleotm
Python tool for exploiting CVE-2021-35616
 makmour/open-ssh-user-enumeration
This script checks for the OpenSSH 7.7 (and prior) username enumeration vulnerability (CVE-2018-15473). It sends a malformed authentication packet…
 mfernstrom/offensivepascal-cve-2011-2523
FreePascal implementation of the vsFTPD 2.3.4 CVE-2011-2523