
PPPoEject
 manizada/pppoeject
Linux kernel local privilege escalation PoC for CVE-2026-68121, chaining PPPoE, FUSE, and IP6GRE to corrupt kernel memory and gain root.
binary-exploitationexploitationmemory-forensics+4
8
manizada/pppoejectLinux kernel local privilege escalation PoC for CVE-2026-68121, chaining PPPoE, FUSE, and IP6GRE to corrupt kernel memory and gain root.
 horkimhab/cve-2026-18574
Educational CVE-2026-18574 proof-of-concept repository for authorized security research, vulnerability awareness, and defensive testing in isolated…
 horkimhab/cve-2026-77179
Educational CVE-2026-77179 proof-of-concept repository for authorized security research, vulnerability awareness, and defensive testing in isolated…
 horkimhab/cve-2026-91843
Educational CVE research repository for CVE-2026-91843, providing vulnerability analysis and proof-of-concept material for authorized lab and…
 ylca0/idalib-cli
Agent-native CLI wrapping IDA Pro IDALib for stateless, JSON-output binary analysis: disassembly, Hex-Rays decompilation, CFG, xrefs, strings, and…
 gmh5225/evilkaspersky
Windows kernel driver experiment based on KasperskyHook that uses direct syscalls for interprocess memory copying, with support for unloading the…
 horkimhab/cve-2026-19975
Proof-of-concept and research repository for CVE-2026-19975 in Azuriom, with setup instructions and a linked technical writeup for authorized…
 cxlfhx/ghostlock-pfem10
GhostLock (CVE-2026-43499 / IonStack) research for OPPO Find X5 Pro (PFEM10): exploit chain, progress, blocker log, and OPPO 5-series kernel notes
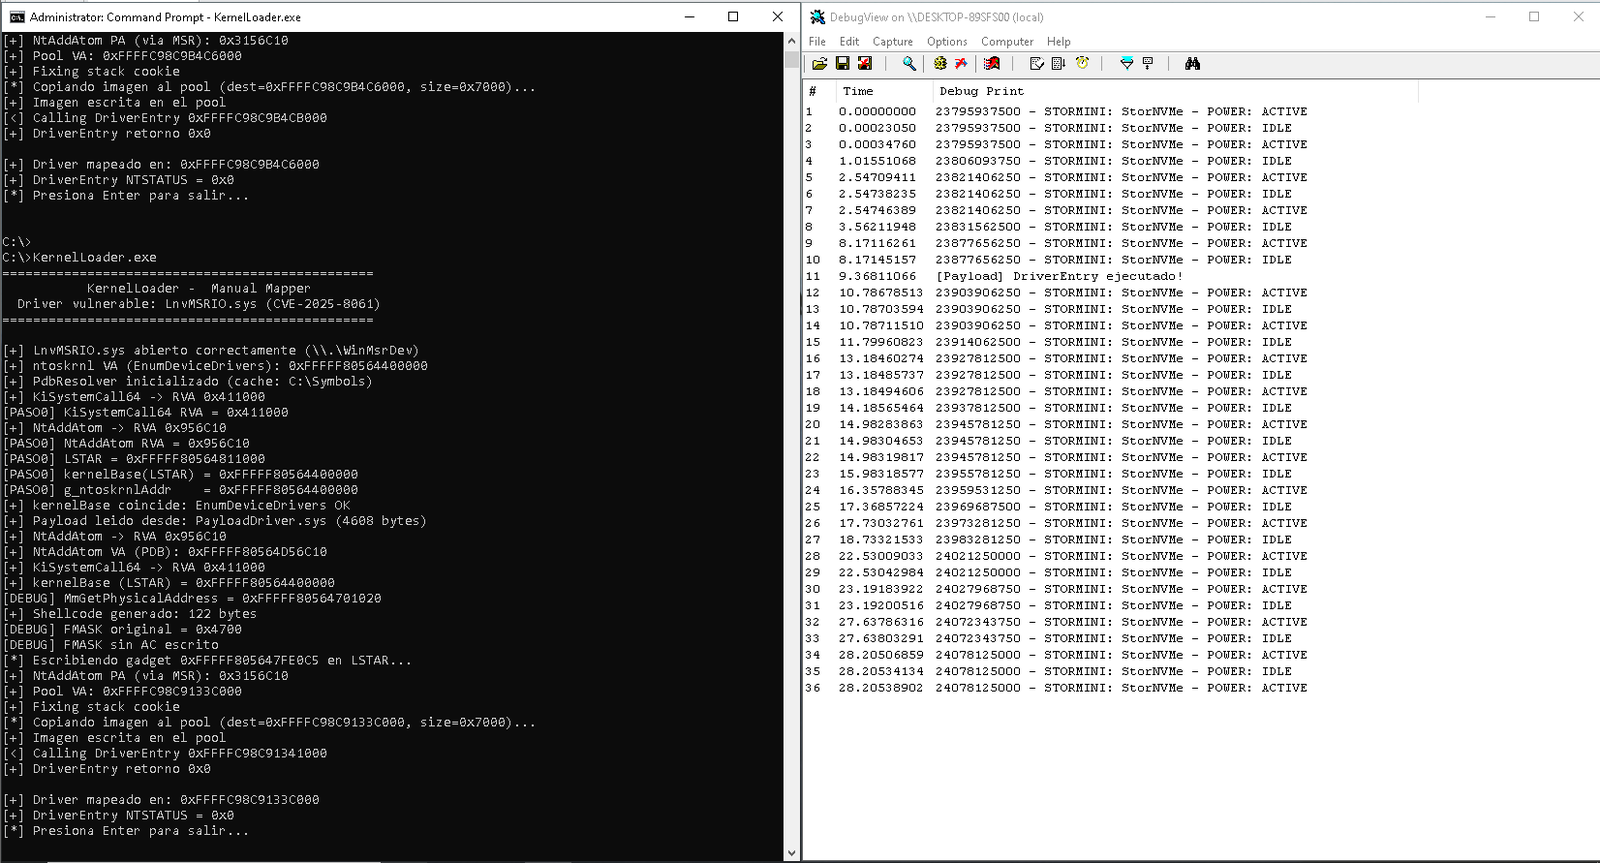 ull0a/msrmapper
Manual kernel driver mapper for Windows x64 that abuses CVE-2025-8061 in Lenovo's LnvMSRIO.sys to perform a BYOVD attack, mapping PE64 drivers into…
 anonmoty/xxstrike
XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.
 csrxamfi/cve-2026-65330
Perl proof-of-concept exploit demonstrating a use-after-free in the NECP trie, with a heap spray option for triggering the kernel memory corruption.
 horkimhab/cve-2026-5430
Educational CVE-2026-5430 research repository with proof-of-concept material for authorized security testing in isolated lab environments.
 horkimhab/cve-2026-65374
Educational CVE-2026-65374 research repository with lab setup guidance for authorized vulnerability testing and defensive security study.
 horkimhab/cve-2026-15315
Educational CVE research repository covering CVE-2026-15315 and CVE-2026-15316 TP-Link Tapo camera authentication bypass and DoS vulnerabilities for…
 gmh5225/dsark64
BYOVD proof-of-concept abusing the WHQL-signed DsArk64.sys driver for ring-0 process termination and kernel read/write via encrypted IOCTLs and…
 horkimhab/cve-2026-76461
Educational security research repository for learning, testing, and researching CVE vulnerabilities and defensive practices in isolated lab…
 harshrajsinghania/cve-2026-90782-s2opc-status-clobber
Standalone PoC for CVE-2026-90782: status-clobbering NULL dereference in S2OPC alloc_notification_message_items() (DataChange fails, Event succeeds)
 sneakynachos/cve-2026-87491-and-cve-2026-85046-the-bagel-fell-off-the-counter
Chrome 152 V8 exploit chaining CVE-2026-85046 and CVE-2026-87491 to corrupt the heap, forge Wasm metadata, and execute native code from the renderer.