hello-ReGrade-security

Find the vulnerability your tests were never written to catch. A ReGrade demo modeling CVE-2023-5968: catch a password-hash leak by comparing an app…

Find the vulnerability your tests were never written to catch. A ReGrade demo modeling CVE-2023-5968: catch a password-hash leak by comparing an app…

Spring4Shell , Spring Framework RCE (CVE-2022-22965) , Burpsuite Plugin

Here's a Python script that checks if the polyfill.io domain is present in the Content Security Policy (CSP) header of a given web application.

Local Docker lab for reproducing CVE-2026-55255, an IDOR vulnerability in Langflow's Responses API. Validates cross-user flow execution in vulnerable…

Reproducer for CVE-2026-48204: Apache Camel camel-mongodb-gridfs gridfs.* header injection overriding the GridFS operation (enumerate/read/delete…

Docker-based lab for reproducing CVE-2026-46645, an authorization bypass in SQLAdmin's ajax_lookup endpoint. Includes vulnerable and patched targets,…

Reproducer for CVE-2026-46592: Apache Camel camel-cxf operationName header injection redirecting the invoked SOAP operation (confused deputy) from a…

Reproducer for CVE-2026-46588: Apache Camel camel-couchdb CouchDb* header injection (operation confusion) subverting a write-only endpoint into read…

Reproducer for CVE-2026-46587: Apache Camel camel-couchbase CCB_* header injection enabling document disclosure, tampering, and TTL-forced data…

Reproducer for CVE-2026-46453 — Apache Camel camel-elasticsearch-rest-client unprefixed-header injection (operation/query override via inbound HTTP…

Strapi CVE-2026-27886. Leaking sensitive data via relational filtering due to lack of query sanitization

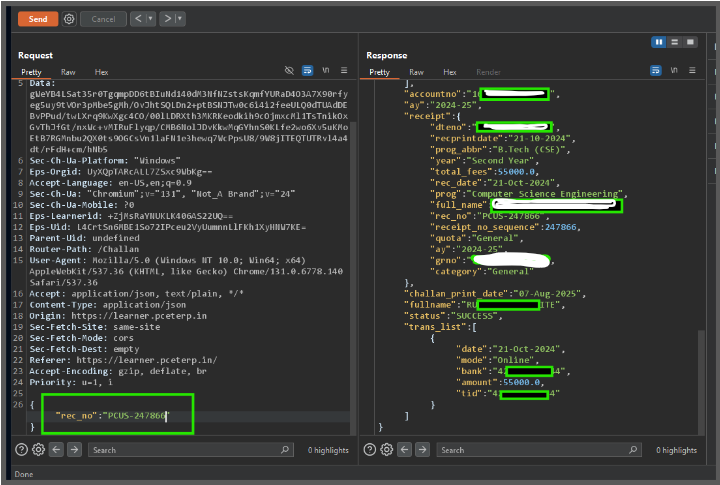
The vulnerability exists in the Student Payment API. The application fails to properly validate whether the user requesting a receipt is authorized…

Security research & exploitation analysis of CVE-2025-55182 (React) — CVSS + OWASP Top 10 mapping

CVE-2025-55182 testing toolkit with Postman collection, cURL examples, and F5 WAF signature validation for vulnerability assessment and protection…

WordPress Verification SMS with TargetSMS Plugin <= 1.5 is vulnerable to Remote Code Execution (RCE)

OWASP Smart Contract Security (SCS) Project

Takes third-party HTML and produces HTML that is safe to embed in your web application. Fast and easy to configure.

OWASP Secure Agent Playbook Project