perwendel__spark_CVE-2016-9177_2-5-1

Exploit for CVE-2016-9177 targeting Spark Java web framework, demonstrating directory traversal vulnerability in version 2.5.1 for security testing…

Exploit for CVE-2016-9177 targeting Spark Java web framework, demonstrating directory traversal vulnerability in version 2.5.1 for security testing…

Lightweight Java 8 web framework with routing, filters, and static file serving. Includes security advisory for older versions and CRUD API examples.

Lightweight Java 8 web framework for building REST APIs and web applications, with built-in routing, static file serving, and template engine support.

Validation target: minimal WordPress core slice reproducing the wp2shell (CVE-2026-63030 + CVE-2026-60137) REST-to-SQLi chain

Insecure Permissions WeDayCare

The code for personally reproducing the corresponding vulnerability

Write-ups from completed TryHackMe rooms — Linux privilege escalation, sudo buffer overflow (CVE-2019-18634), and OWASP Top 10 (2025).

XSS Test Swagger 3.14.1 to 3.37.0

Type-safe HTTP client library for Android and Java, enabling REST API communication with annotation-based request configuration and converter support.

Spring-Cloud-Gateway-CVE-2022-22947

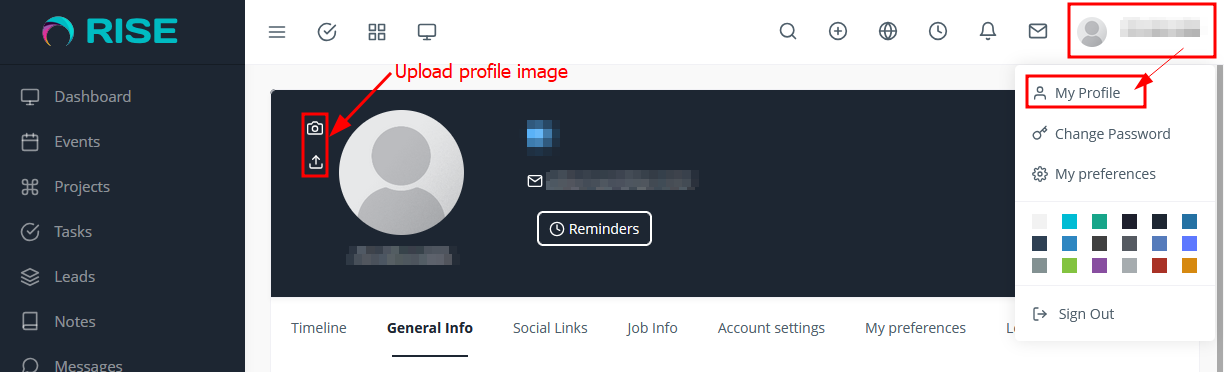
CVE-2025-3855 - RISE Ultimate Project Manager - IDOR

A web-based vulnerability scanner for CVE-2025-55182, a critical Remote Code Execution (RCE) vulnerability in React Server Components.

Time-based blind SQL injection proof-of-concept for LiteLLM v1.65.4. Exploits the `/key/block` endpoint to extract database contents and read server…

Proof-of-concept for CVE-2025-63406 in GroupOffice, demonstrating API-based object manipulation and authentication flow for vulnerability analysis…

Automated Web Vulnerability Assessment of DVWA using OWASP ZAP to identify and analyze critical security flaws like Remote Code Execution…

演示 Next.js 中的 Middleware 授權繞過漏洞 (CVE-2025-29927) 允許未經授權的用戶存取受保護的資訊。

Scanner: CVE-2026-42208 LiteLLM SQL Injection — Python scanner for BerriAI LiteLLM proxy instances

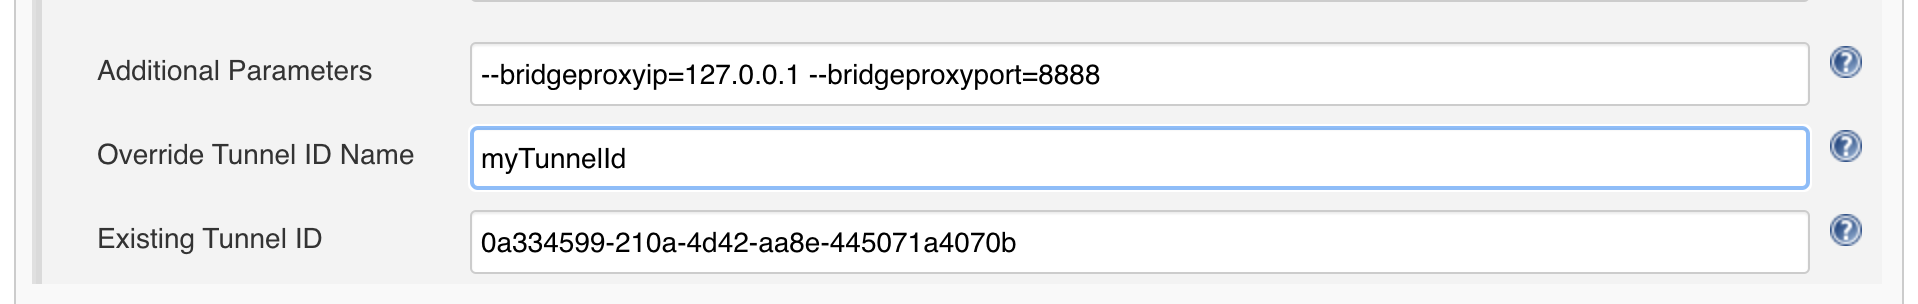
Jenkins plugin for automated mobile app testing via Perfecto cloud, managing secure tunnel connections and app uploads within CI/CD pipelines.