Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
203 results
Android-Disassembler preview

Android-Disassembler

GitHubyhs0602/android-disassembler

Disassemble ANY files including .so (NDK, JNI), Windows PE(EXE, DLL, SYS, etc), linux binaries, libraries, and any other files such as pictures,…
android-securitybinary-analysisdebuggers+4
709
7 months ago
DropSpawn_BOF preview

DropSpawn_BOF

GitHuboctoberfest7/dropspawn_bof

CobaltStrike BOF to spawn Beacons using DLL Application Directory Hijacking
binary-exploitationexploitationpayload-development+4
2873 years ago
PythonMemoryModule preview

PythonMemoryModule

GitHubnaksyn/pythonmemorymodule

pure-python implementation of MemoryModule technique to load dll and unmanaged exe entirely from memory
exploit-frameworkspenetration-testingred-teaming
3402 years ago
Chimera preview

Chimera

GitHubgeorgesotiriadis/chimera

Automated DLL Sideloading Tool With EDR Evasion Capabilities
exploitationpayload-generationred-teaming+1
5072 years ago
RDPCredentialStealer preview

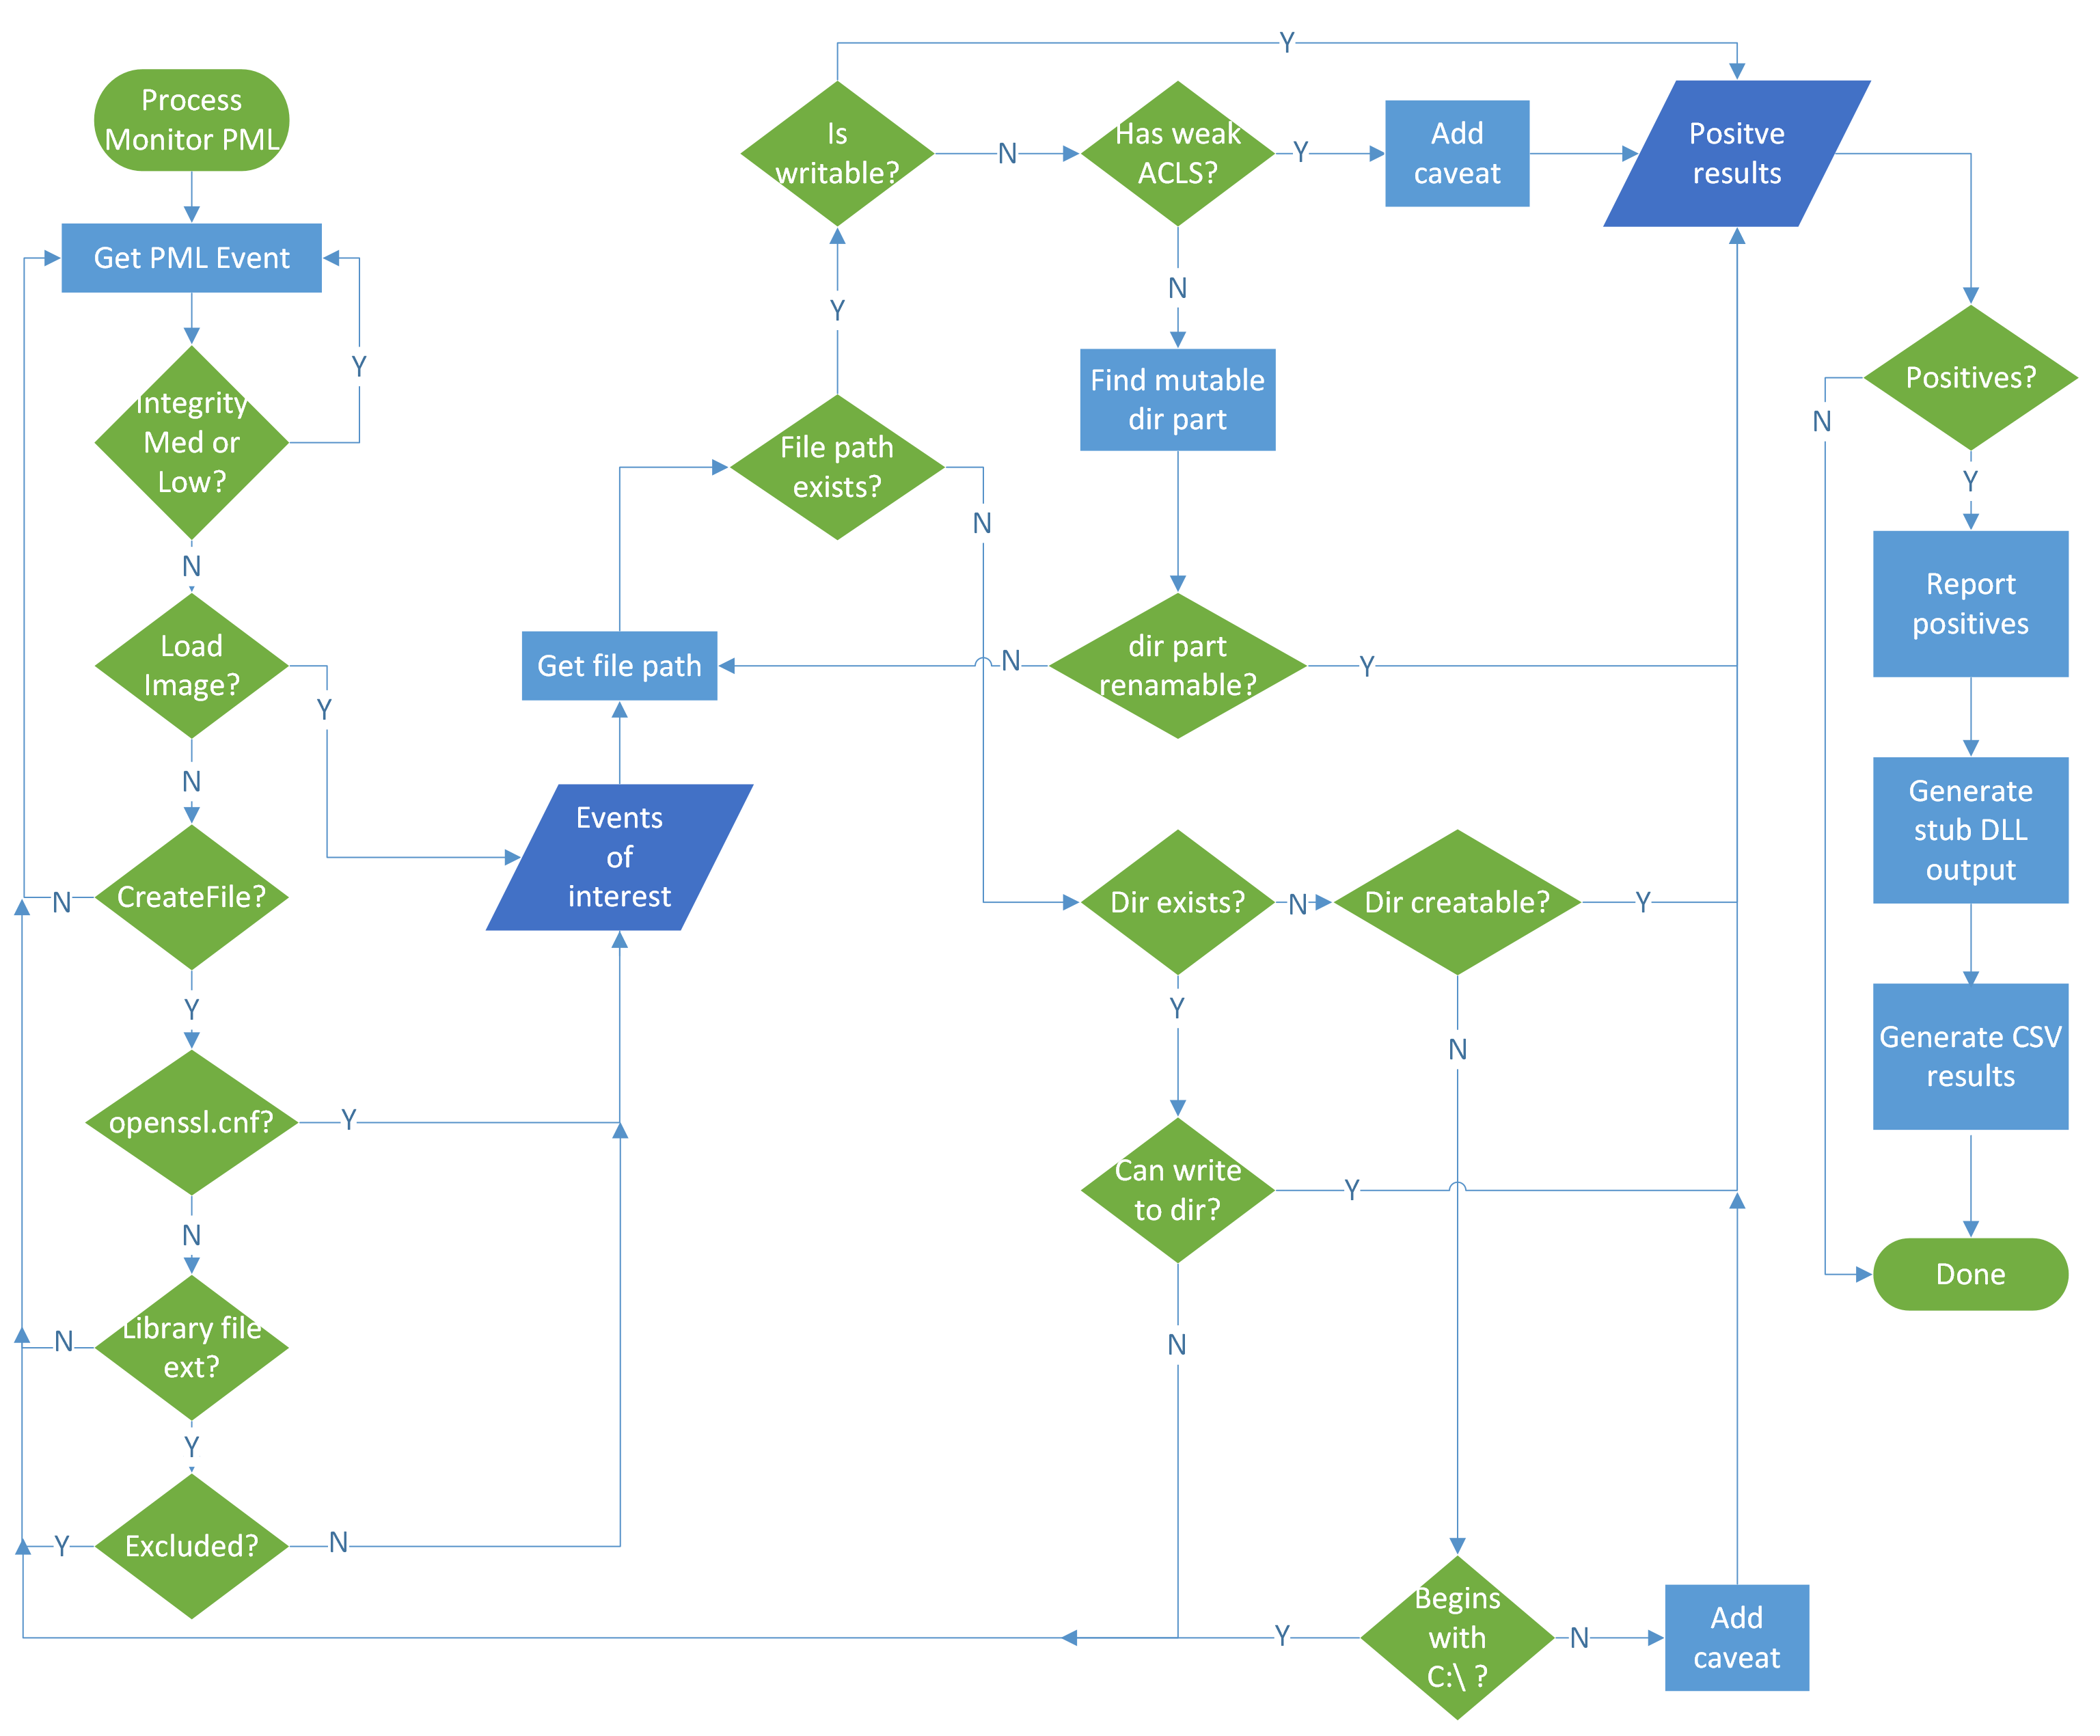
RDPCredentialStealer

GitHubs12cybersecurity/rdpcredentialstealer

Windows implant that steals RDP credentials via API hooking (Detours) and DLL injection, capturing usernames and passwords to a file for red-team…
post-exploitationred-teaming
2667 months ago
Crassus preview

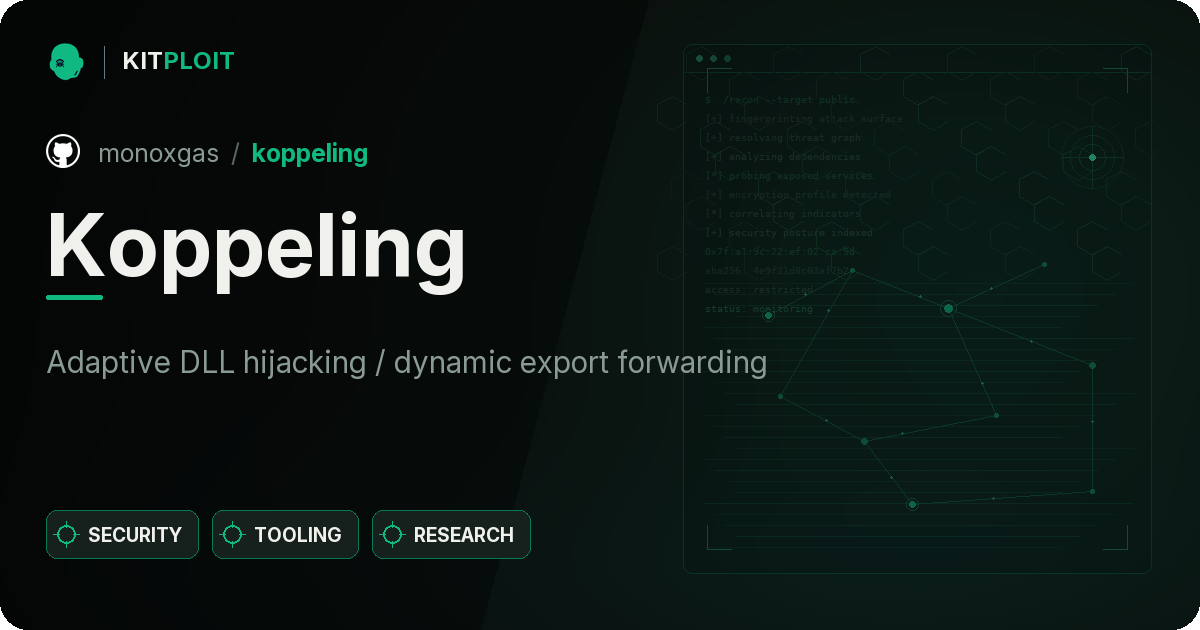
Crassus

GitHubvu-ls/crassus

Windows privilege escalation discovery tool that parses Process Monitor boot logs to identify DLL hijacking, weak ACLs, and other elevation paths,…
binary-analysisexploitationpenetration-testing+1
6334 days ago
Koppeling preview

Koppeling

GitHubmonoxgas/koppeling

Adaptive DLL hijacking / dynamic export forwarding
binary-exploitationexploitationpayload-development+1
8196 years ago
RottenPotatoNG preview

RottenPotatoNG

GitHubbreenmachine/rottenpotatong

New version of RottenPotato as a C++ DLL and standalone C++ binary - no need for meterpreter or other tools.

exploitationpenetration-testingpost-exploitation+1
9748 years ago
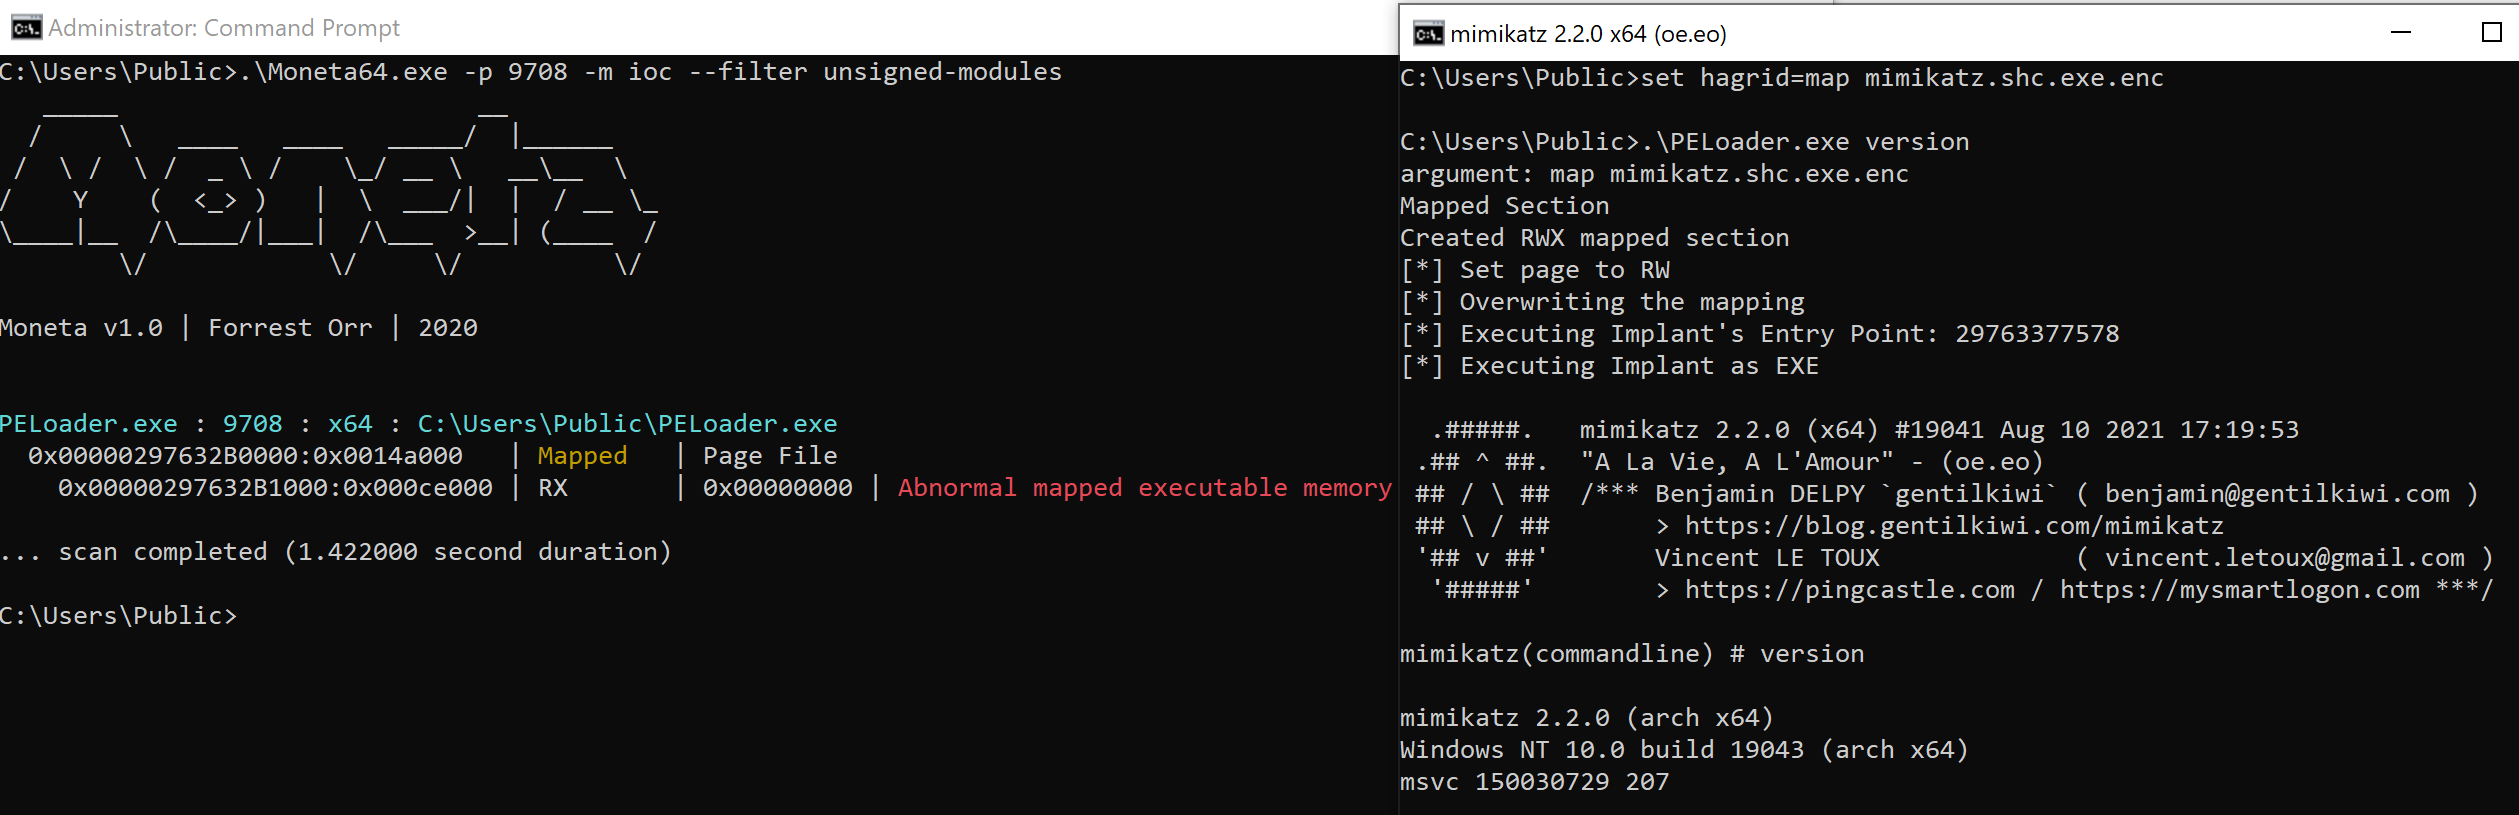
TeamsImplant preview

TeamsImplant

GitHuballevon412/teamsimplant

Stealthy DLL proxying implant for Microsoft Teams that injects AES-encrypted shellcode via unhooking techniques, providing persistent backdoor access…
command-and-controlexploit-frameworkspayload-development+5
2084 years ago
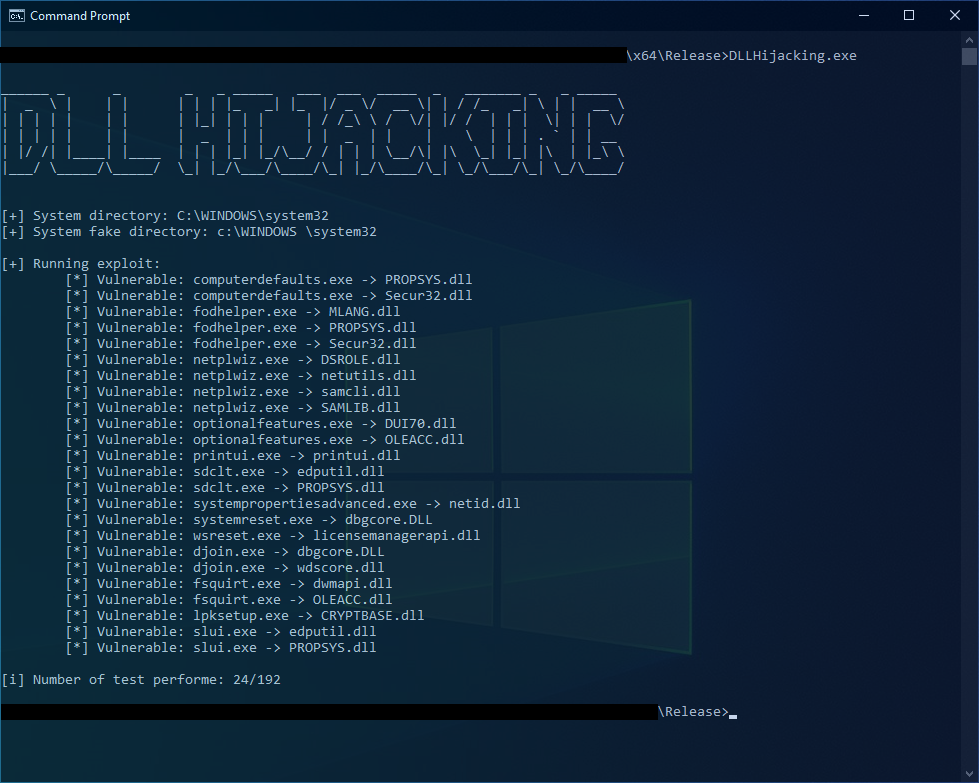
PELoader preview

PELoader

GitHubhagrid29/peloader

PE loader with various shellcode injection techniques
binary-analysisexploitationmalware-analysis+4
4554 years ago
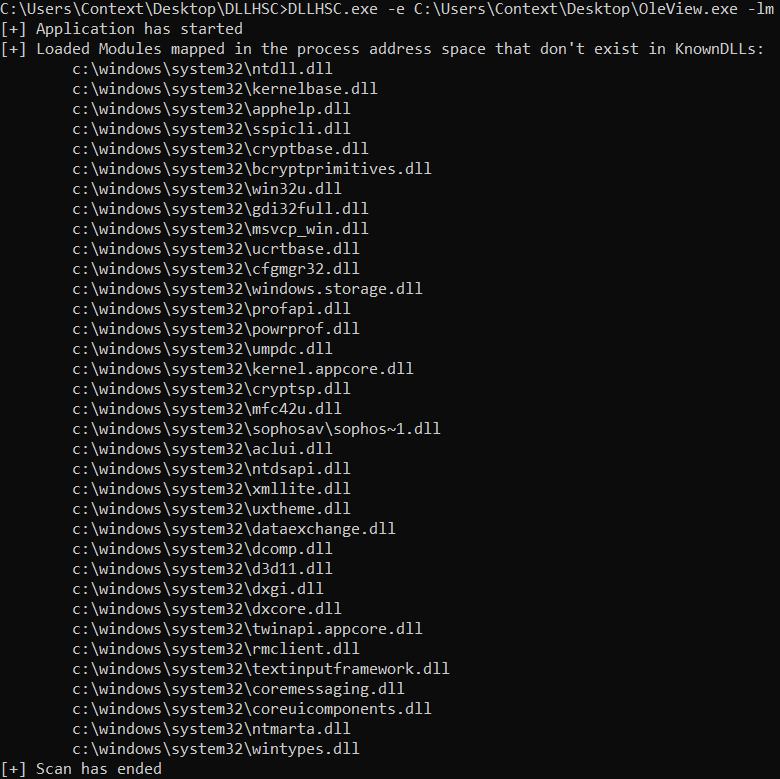
DLLHijackingScanner preview

DLLHijackingScanner

GitHubsecuproject/dllhijackingscanner

This is a PoC for bypassing UAC using DLL hijacking and abusing the "Trusted Directories" verification.

exploitationprivilege-escalationvulnerability-scanners
2835 years ago
RCLocals preview

RCLocals

GitHubyjesus/rclocals

Linux startup analyzer

defensive-toolsforensicshash-analysis+4
661 year ago
DLLHSC preview

DLLHSC

GitHubctxis/dllhsc

Automated scanner for discovering DLL search order hijacking candidates in Windows executables, featuring import table parsing, runtime module…

binary-analysisexploitationpayload-development+1
1586 years ago
byeintegrity-uac preview

byeintegrity-uac

GitHubazagarampur/byeintegrity-uac

Bypass UAC by hijacking a DLL located in the Native Image Cache

exploitationpenetration-testingprivilege-escalation+1
2114 years ago
zirconium preview

zirconium

GitHubrobertmotr/zirconium

DLL-injectable internal game cheat for Plutonium BO2 zombies
exploitationmemory-forensicspenetration-testing+2
122 months ago
GoDefender preview
Archived

GoDefender

GitHubkiexitdispatcher/godefender

Anti Virtulization, Anti Debugging, AntiVM, Anti Virtual Machine, Anti Debug, Anti Sandboxie, Anti Sandbox, VM Detect package. Windows ONLY.
anti-botbinary-analysisdefensive-tools+3
85810 months ago
Mangle preview
Archived

Mangle

GitHuboptiv/mangle

Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs

binary-analysisdefensive-toolsexploitation+6
1.2k3 years ago
venom-rs preview
Archived

venom-rs

GitHubmemn0ps/venom-rs

Rusty Injection - Shellcode Reflective DLL Injection (sRDI) in Rust (Codename: Venom)

payload-developmentpost-exploitationred-teaming+2
3702 years ago
Previous1…101112Next