

JavaSecLab
 whgojp/javaseclab
Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
code-analysisctfdevsecops+6
885
whgojp/javaseclabComprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
 owasp/wrongsecrets
Vulnerable app with examples showing how to not use secrets
 fi3ro/cve-2015-5377
Java deserialization exploit targeting Elasticsearch 1.5.2 transport protocol (port 9300) using Groovy MethodClosure chain for remote code execution…
 imjdl/cve-2012-4431
Apache Tomcat source code repository for CVE-2012-4431, a Java servlet container vulnerability. Provides the vulnerable codebase for analysis and…
 bobtheshoplifter/spring4shell-poc
Spring4Shell Proof Of Concept/And vulnerable application CVE-2022-22965
 seanpesce/cve-2024-22243
Example exploitable scenarios for CVE-2024-22243 affecting the Spring framework (open redirect & SSRF).
 fox-it/log4j-finder
Find vulnerable Log4j2 versions on disk and also inside Java Archive Files (Log4Shell CVE-2021-44228, CVE-2021-45046, CVE-2021-45105)
 llamaonsecurity/cve-2018-12533
Payload generator and proof-of-concept exploit for CVE-2018-12533 (Richfaces deserialization/EL injection) with Docker-based vulnerable environment…
 isuruwa/log4j
Scanner and proof-of-concept exploit for Log4j RCE (CVE-2021-44228). Creates a vulnerable application and runs the exploit with a netcat listener.
 theronielanddaronpodcastshow/svja
The Super Vulnerable Java Application (SVJA), as demonstrated in the Roniel and DaRon Podcast Show, is an Apache Struts application designed to…
 hantwister/o5logon-fetch
Attempts to exploit CVE-2012-3137 on vulnerable Oracle servers
 xiaoqimikko/netty-resolver-dns-check
Offline static checker that inspects packaged Java jars for vulnerable netty-resolver-dns versions and detects whether Spring WebClient actually uses…
 notkmhn/cve-2022-21449-tls-poc
CVE-2022-21449 Proof of Concept demonstrating its usage with a client running on a vulnerable Java version and a malicious TLS server
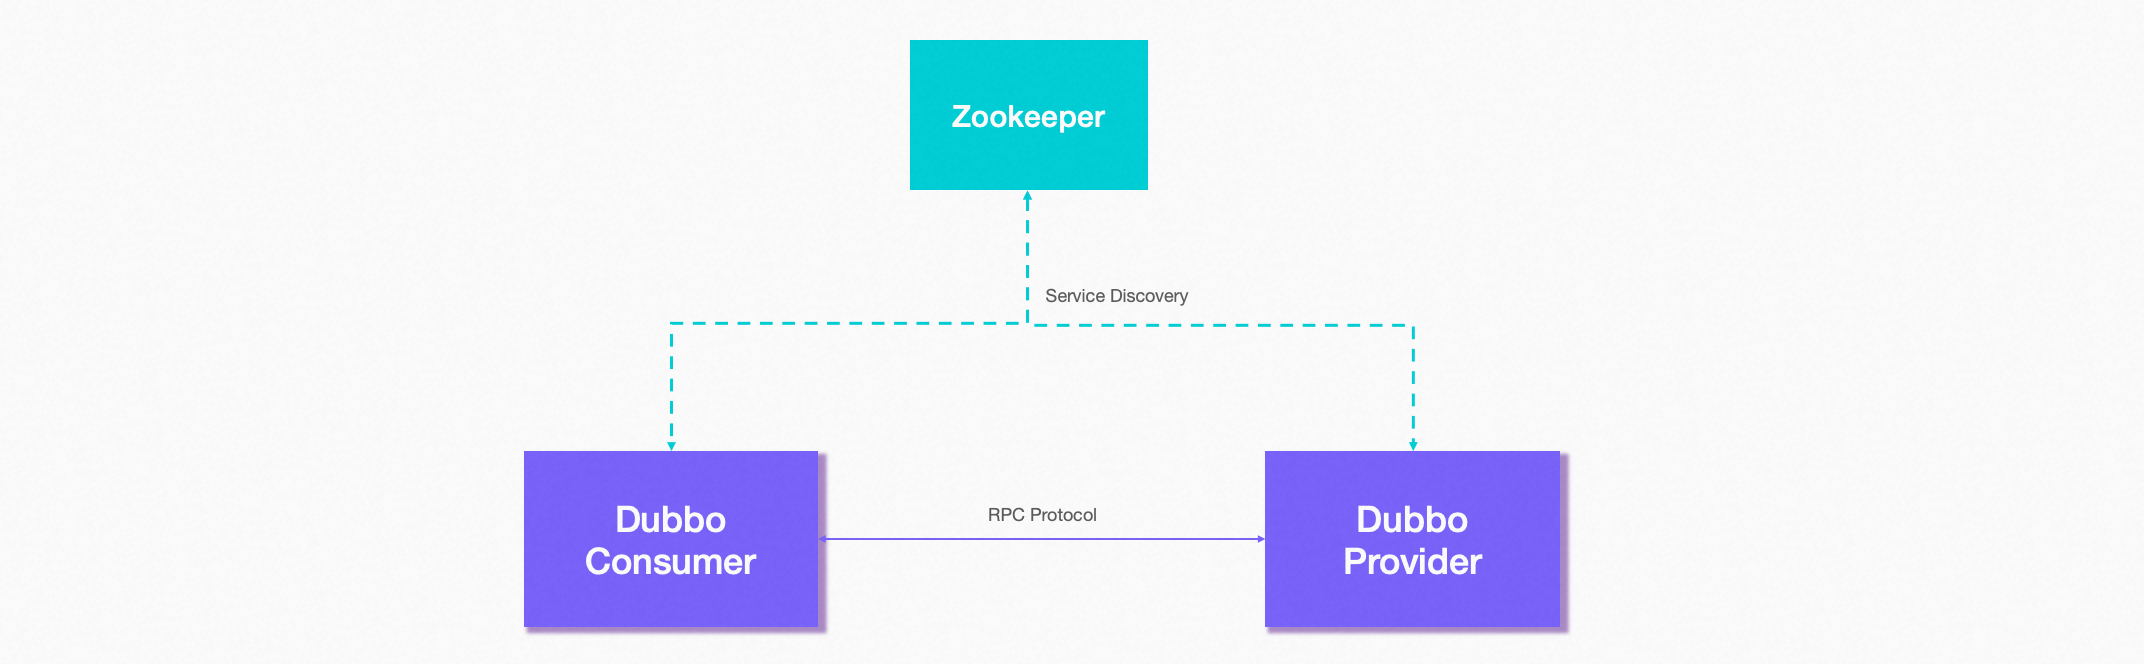 shoucheng3/apache__dubbo_cve-2021-30180_2-7-9
Exploit for CVE-2021-30180 targeting Apache Dubbo RPC framework, enabling remote code execution via crafted RPC requests in vulnerable versions.
 hillu/local-log4j-vuln-scanner
[Moved to Codeberg] Simple local scanner for vulnerable log4j instances
 clayofgilgamesh/cve-2026-29000
CTF lab and exploit toolkit for CVE-2026-29000, a pac4j-jwt JWE authentication bypass. Includes vulnerable Flask target, token forging library,…
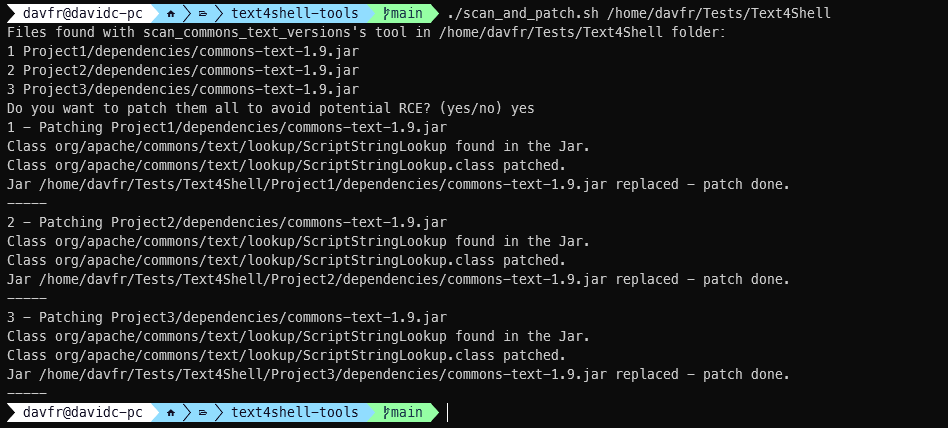 jfrog/text4shell-tools
Detect and patch vulnerable Apache Commons Text in Java JAR/WAR artifacts; fingerprint classes and scan bytecode for CVE-2022-42889 (Text4Shell) call…
 iris-sast/zip4j
CWE-Bench-Java CVE-2018-1002202 versions 1.3.2, 1.3.3