

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
107 results
R2Socks preview

R2Socks

GitHubivancabrera02/r2socks

SOCKS5 proxy tunneled through Cloudflare R2 object storage, with Python and dependency-free C++ agents relaying TCP traffic via encrypted R2 objects…

command-and-controldata-exfiltrationencryption-decryption-tools+5
39
1 month ago
metasploit-payloads preview

metasploit-payloads

GitHubrapid7/metasploit-payloads

Unified repository for different Metasploit Framework payloads

command-and-controlexploitationexploit-frameworks+9
2.1k7 days ago
Xenon preview

Xenon

GitHubmythicagents/xenon

A Mythic agent for Windows written in C

command-and-controldata-exfiltrationdefensive-tools+9
1881 month ago
Stracciatella preview

Stracciatella

GitHubmgeeky/stracciatella

OpSec-safe Powershell runspace from within C# (aka SharpPick) with AMSI, Constrained Language Mode and Script Block Logging disabled at startup

command-and-controlexploit-frameworksids-ips-evasion+7
5444 years ago
beef preview

beef

GitHubbeefproject/beef

The Browser Exploitation Framework Project
command-and-controlexploitationexploit-frameworks+8
11.1k4 days ago
MeshCore preview

MeshCore

GitHubmeshcore-dev/meshcore

A new lightweight, hybrid routing mesh protocol for packet radios

command-and-controldata-exfiltrationeducation+8
3.9k5 days ago
wasmforge preview

wasmforge

GitHubpraetorian-inc/wasmforge

WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
binary-analysiscommand-and-controlexploit-frameworks+9
1343 months ago
DcRat preview
Archived

DcRat

GitHubqwqdanchun/dcrat

A simple remote tool in C#.
command-and-controldata-exfiltrationids-ips-evasion+9
1.0k4 years ago
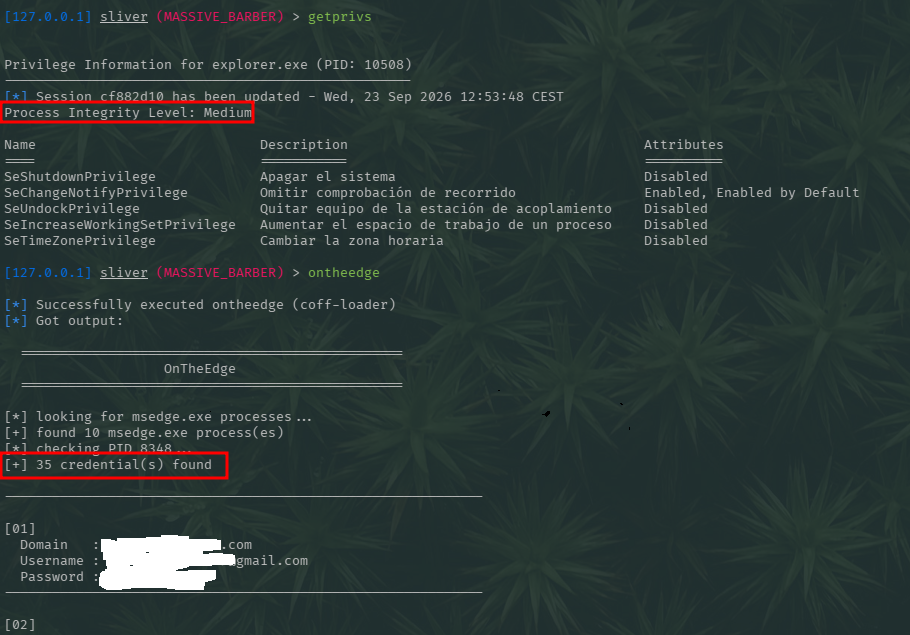
OnTheEdge preview

OnTheEdge

GitHubjssngc/ontheedge

Windows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…
command-and-controldata-exfiltrationmalware-analysis+4
1127 days ago
LOIC preview
Archived

LOIC

GitHubneweracracker/loic

Deprecated - Low Orbit Ion Cannon - An open source network stress tool, written in C#. Based on Praetox's LOIC project. USE ON YOUR OWN RISK. WITHOUT…
command-and-controleducationnetwork-mapping+2
3.0k4 years ago
CIMplant preview

CIMplant

GitHubredsiege/cimplant

C# port of WMImplant which uses either CIM or WMI to query remote systems
command-and-controlinformation-gatheringlateral-movement+4
2045 years ago
Stealth-Kid-RAT preview

Stealth-Kid-RAT

GitHubartbitrage/stealth-kid-rat

Stealth Kid RAT (SKR) is an open-source multi-platform Remote Access Trojan (RAT) written in C#. Released under MIT license. The SKR project is fully…
command-and-controleducationpayload-development+3
245 years ago
Striker preview

Striker

GitHub4g3nt47/striker

Multi-operator C2 framework with native C and Python agents, HTTP(S) channels, asynchronous tasking, and a reactive web UI for red team operations.
command-and-controlpayload-generationred-teaming+1
3003 years ago
ImpulsiveDLLHijack preview

ImpulsiveDLLHijack

GitHubknight0x07/impulsivedllhijack

C# based tool which automates the process of discovering and exploiting DLL Hijacks in target binaries. The Hijacked paths discovered can later be…

binary-exploitationexploitationpersistence-mechanisms+2
5575 years ago
BadOutlook preview

BadOutlook

GitHubaahmad097/badoutlook

Proof-of-concept C# tool that reads Outlook emails via COM interface, extracts base64-encoded shellcode from trigger subject lines, and executes…

command-and-controlemail-securityexploitation+3
1375 years ago
RedPersist preview

RedPersist

GitHubmertdas/redpersist

C# tool for establishing Windows persistence via multiple techniques including scheduled tasks, WMI events, startup folders, and registry hijacking,…
persistence-mechanismspost-exploitationred-teaming
2223 years ago
MalvexC2 preview

MalvexC2

GitHuberarnitox/malvexc2

A simple C2 Framework written in modern C++
command-and-controleducationexploit-frameworks+6
343 months ago
aura-botnet preview

aura-botnet

GitHubwatersalesman/aura-botnet

A super portable botnet framework with a Django-based C2 server. The client is written in C++, with alternate clients written in Rust, Bash, and…

command-and-controleducationpenetration-testing+1
1447 years ago
Previous123456Next