Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
203 results
QuickAssist_UAC_Bypass preview

QuickAssist_UAC_Bypass

GitHubr41n3rzuf477/quickassist_uac_bypass

UAC bypass PoC abusing the UIAccess QuickAssist binary to load an attacker-controlled DLL via WebView2 BrowserExecutableFolder, then hijack elevated…

defensive-toolsexploitationpayload-development+4
244

3 months ago
sRDI preview

sRDI

GitHubmonoxgas/srdi

Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode

exploitationids-ips-evasionmemory-forensics+7
2.5k4 years ago
RC4Decryption preview

RC4Decryption

GitHubweedhashpeddler/rc4decryption

Abuses the Microsoft-signed tlscsp.dll LOLBin to run RC4 encrypt/decrypt via LsCsp_EncryptHwid, patching the hardcoded key in memory for BYOK…

binary-analysiscryptographydefensive-tools+6
371 month ago
EternalBlueC preview

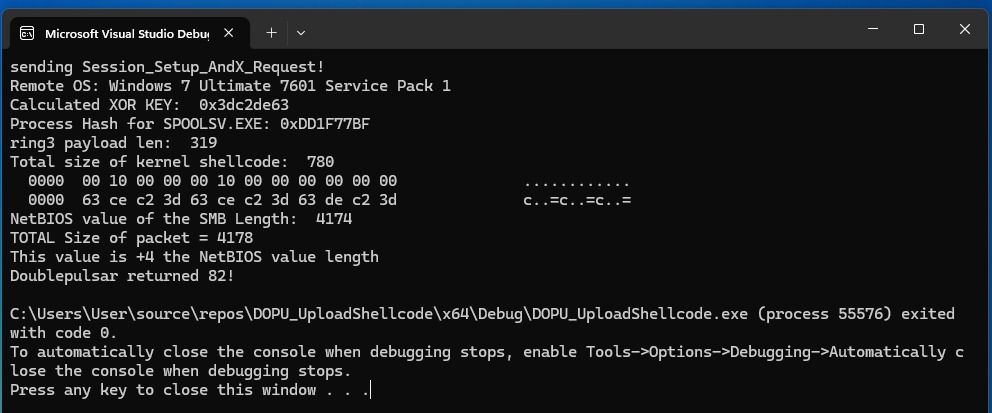
EternalBlueC

GitHubbhassani/eternalbluec

EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…

binary-exploitationeducationexploitation+7
6131 month ago
DuplicateDump preview

DuplicateDump

GitHubhagrid29/duplicatedump

Dumping LSASS with a duplicated handle from custom LSA plugin

post-exploitationprivilege-escalationred-teaming
2074 years ago
SigFlip preview

SigFlip

GitHubmed0x2e/sigflip

SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.

binary-analysiscode-analysisdefensive-tools+5
1.3k3 years ago
malware-analysis-fake-hwmonitor preview

malware-analysis-fake-hwmonitor

GitHubdmitry-matvienko/malware-analysis-fake-hwmonitor

Technical analysis, writeup, and YARA rules for a DLL Sideloading campaign disguised as HWMonitor

defensive-toolsdigital-forensicseducation+6
11 month ago
MemoryModulePP preview

MemoryModulePP

GitHubstrivexjun/memorymodulepp

C++ library to load DLLs directly from memory without touching disk, with exception handling support, enabling stealthy code execution and evasion of…

binary-analysisexploitationmalware-analysis+2
2256 years ago
Fritter preview

Fritter

GitHub0xrootpls/fritter

Polymorphic shellcode generator for in-memory execution of EXE, DLL, .NET, VBScript, and JScript with per-output and per-build randomization for…

binary-exploitationexploitationpayload-development+5
2482 months ago
ghostdebug preview

ghostdebug

GitHubvollragm/ghostdebug

Debugger utilizing stealth hooks to hide from debugger detection

binary-analysisdebuggersdefensive-tools+1
272 months ago
chimera preview

chimera

GitHub1neptune/chimera

Rust-based DLL hijacking loader for MobaXterm (CVE-2026-6421) with persistence

binary-exploitationexploitationpayload-development+4
3 months ago
CVE-2026-50343-InstallService-EoP preview

CVE-2026-50343-InstallService-EoP

GitHubrat5ak/cve-2026-50343-installservice-eop

CVE-2026-50343 InstallService StaticPluginMap EoP - standard user to SYSTEM

binary-exploitationeducationexploitation+3
483 months ago
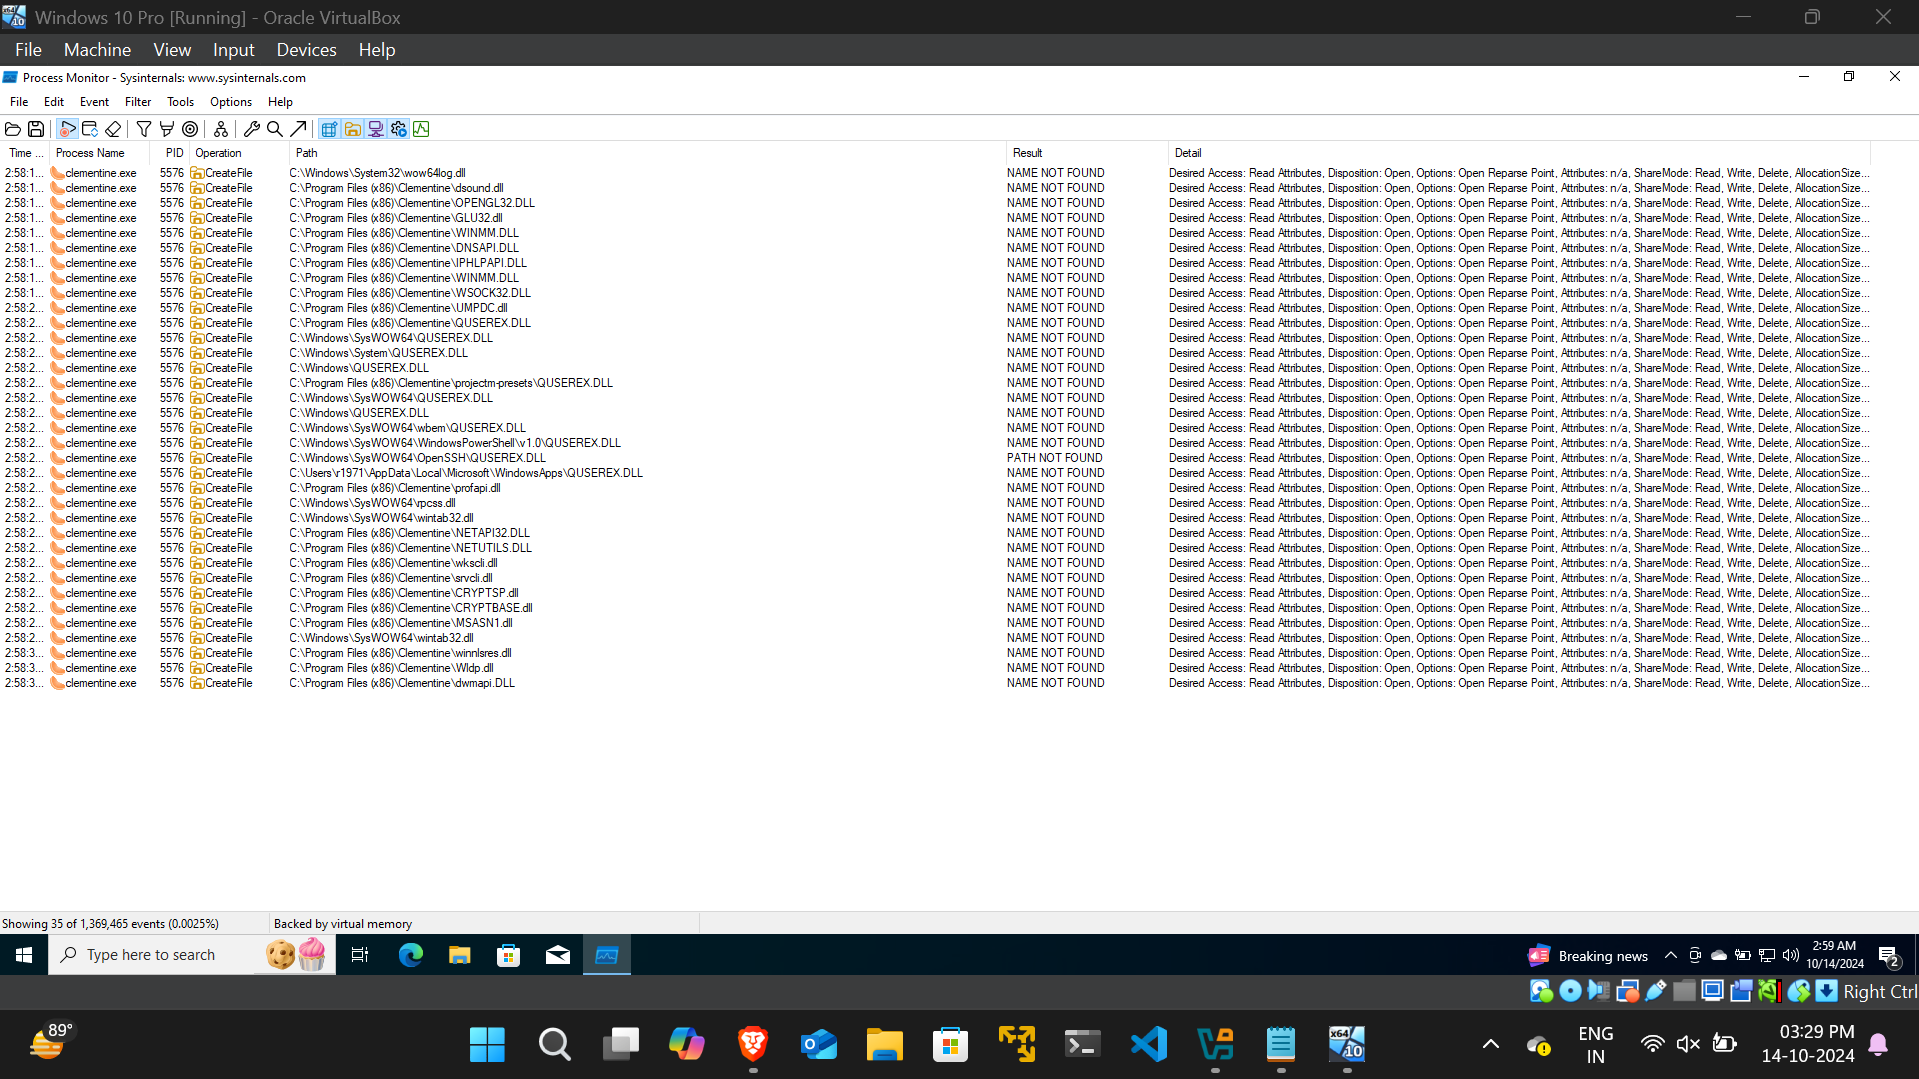
CVE-2024-50986 preview

CVE-2024-50986

GitHubriftsandroses/cve-2024-50986

An issue in Clementine v.1.3.1 allows a local attacker to execute arbitrary code via a crafted DLL file (DLL Hijacking)

binary-exploitationexploitationpayload-generation+4
1 year ago
CdpSvcLPE preview

CdpSvcLPE

GitHubsailay1996/cdpsvclpe

Windows Local Privilege Escalation via CdpSvc service (Writeable SYSTEM path Dll Hijacking)

exploitationpayload-developmentpenetration-testing+3
2564 years ago
Crassus preview

Crassus

GitHubvu-ls/crassus

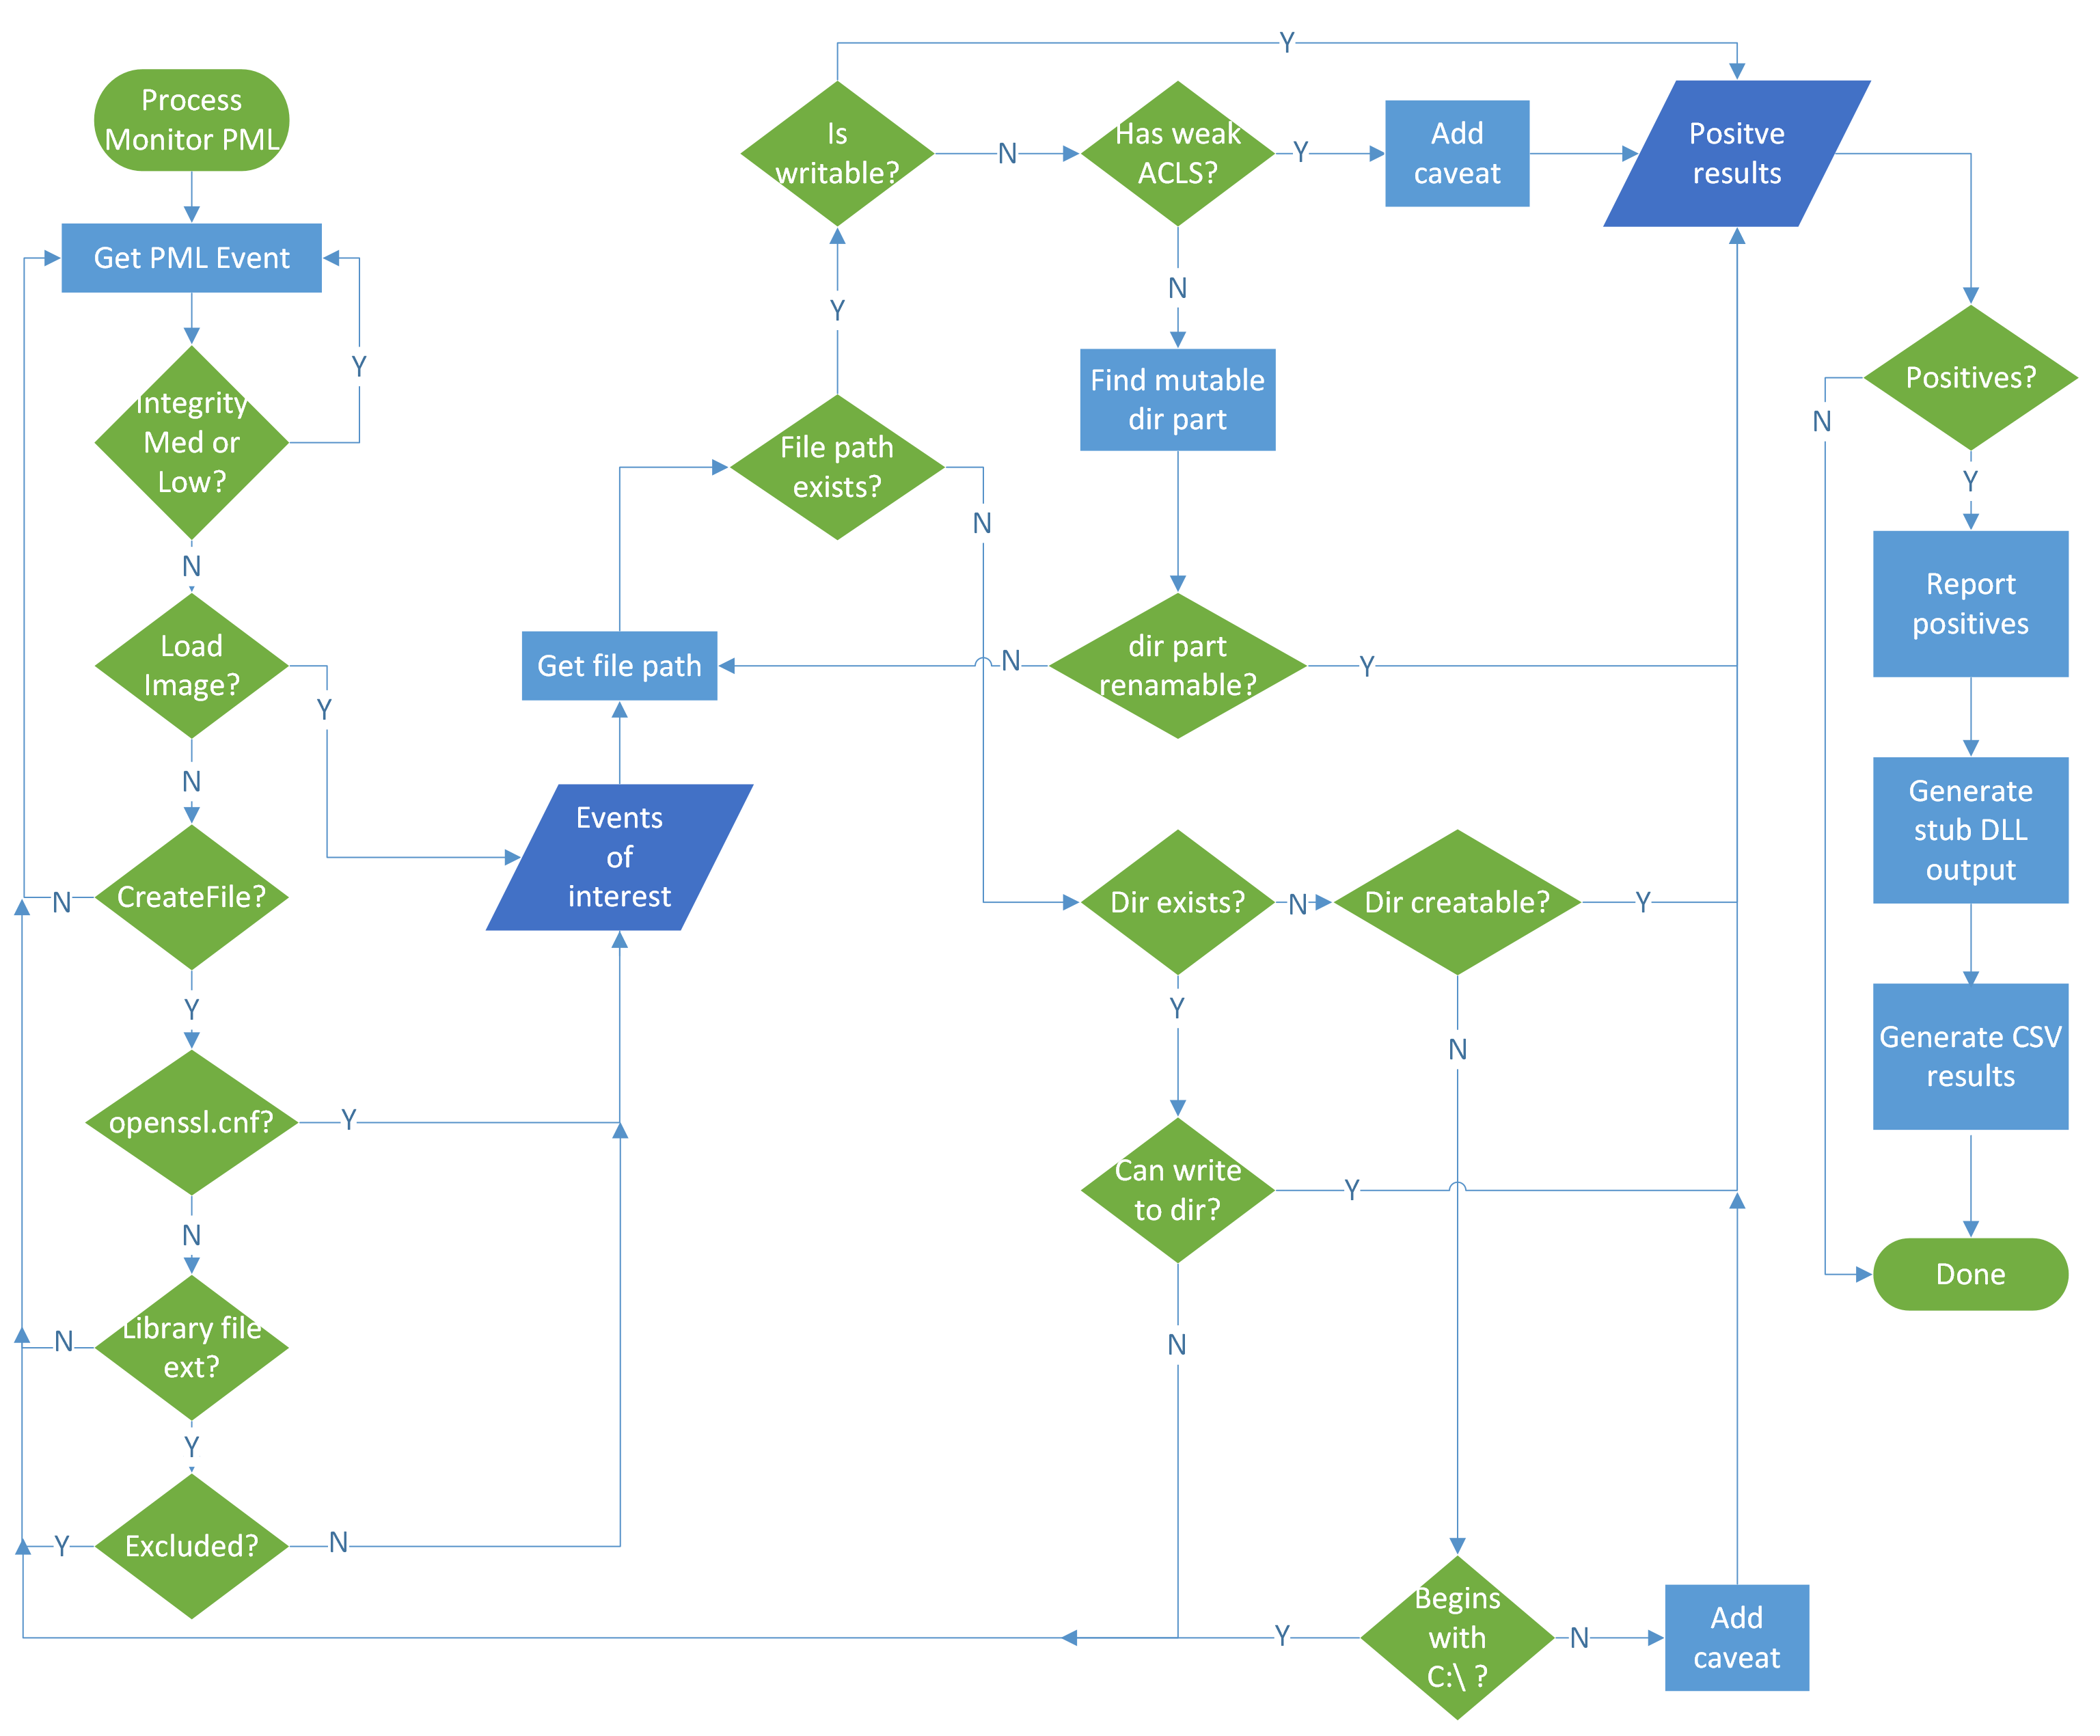
Windows privilege escalation discovery tool that parses Process Monitor boot logs to identify DLL hijacking, weak ACLs, and other elevation paths,…

binary-analysisexploitationpenetration-testing+1
6333 days ago
Detours preview

Detours

GitHubmicrosoft/detours

Runtime Windows API interception library for hooking, monitoring, and instrumenting function calls. Supports binary rewriting and DLL injection,…

debuggersdynamic-code-analysisreverse-engineering+1
6.4k1 month ago
ImpulsiveDLLHijack preview

ImpulsiveDLLHijack

GitHubknight0x07/impulsivedllhijack

C# based tool which automates the process of discovering and exploiting DLL Hijacks in target binaries. The Hijacked paths discovered can later be…

binary-exploitationexploitationpersistence-mechanisms+2
5545 years ago
staged-DLL-Injection-SMB- preview

staged-DLL-Injection-SMB-

GitHubkasturixbm5/staged-dll-injection-smb-

Staged DLL injection proof-of-concept built in C using Win32 APIs — developed in an isolated lab environment for red team certification study (CRTO).

educationexploitationlabs-practice+5
425 months ago
Previous12…12Next