CVE-2021-40905
 edgarloyola/cve-2021-40905
Proof-of-concept exploit for CVE-2021-40905, a remote code execution vulnerability in CheckMK Management Web Console via crafted .mkp extension…
code-analysisexploitationpenetration-testing+2
edgarloyola/cve-2021-40905Proof-of-concept exploit for CVE-2021-40905, a remote code execution vulnerability in CheckMK Management Web Console via crafted .mkp extension…
 afine-com/cve-2024-5737
AdmirorFrames Joomla! Extension < 5.0 - HTML Injection
 forefy/reburp
A Burp Suite extension that exposes the full Montoya API as a local REST API, with Swagger UI
 f0ng/text4shellburpscanner
Burp Suite extension for detecting CVE-2022-42889 (Text4Shell) vulnerability via passive scanning of HTTP requests and responses.
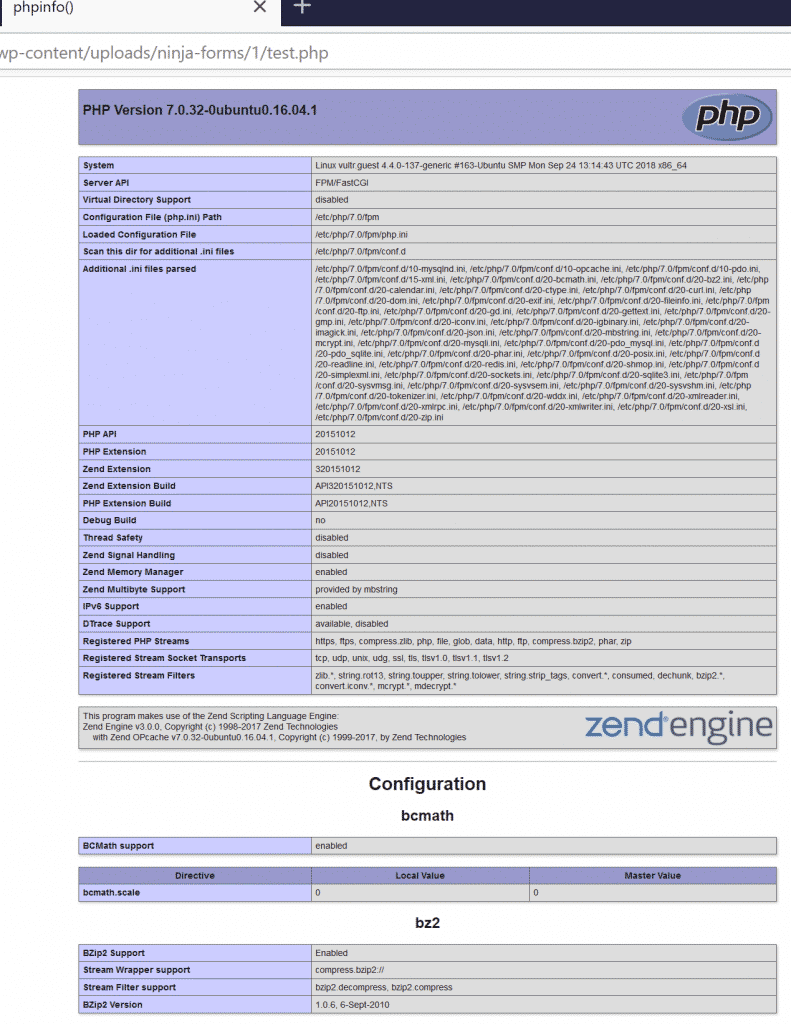 ktn1990/cve-2019-10869
(Wordpress) Ninja Forms File Uploads Extension <= 3.0.22 – Unauthenticated Arbitrary File Upload
 fru1ts/cve-2024-44902
Proof-of-concept exploit for CVE-2024-44902, a deserialization vulnerability in ThinkPHP v6.1.3–v8.0.4 enabling remote code execution via crafted…
 alfazhossain/cve-2025-55182-exploiter
CVE-2025-55182-Exploiter Google Chrome Extension. nextjs vulnerability #nextjscve
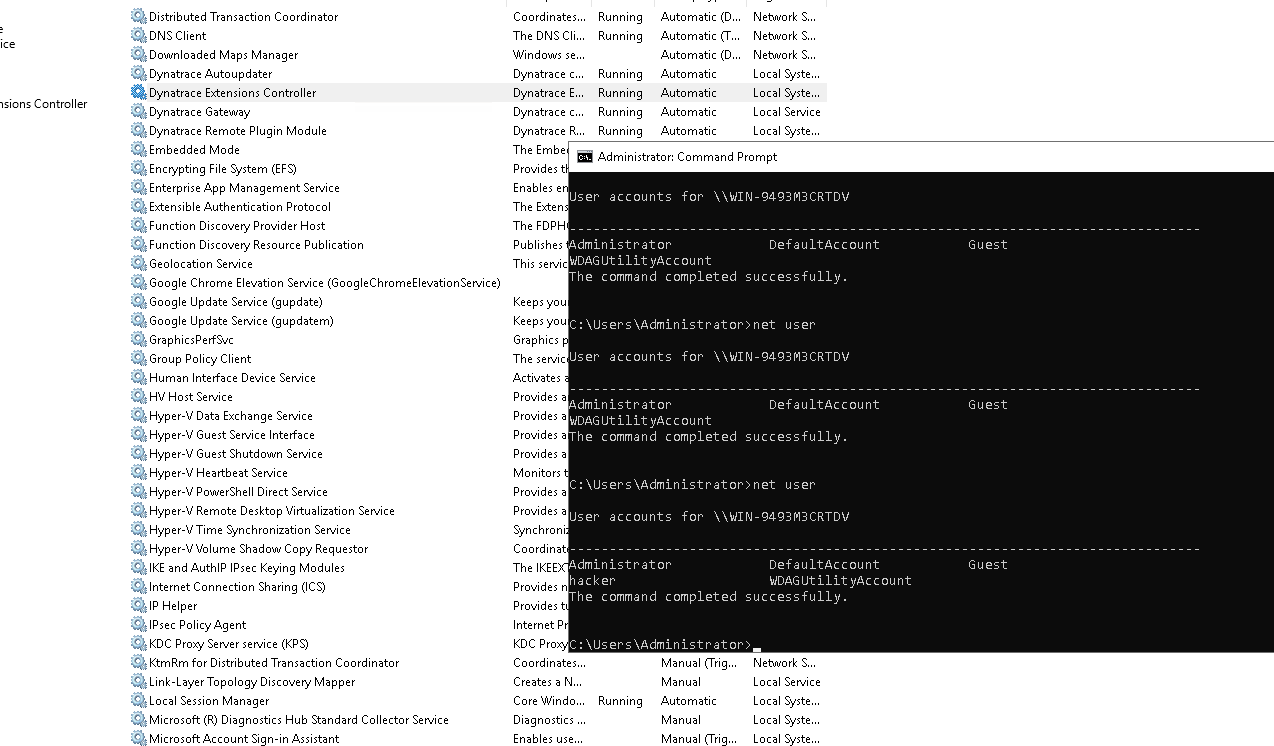 pentastic-be/cve-2025-61304
OS command injection vulnerability in Dynatrace ActiveGate ping extension up to 1.016 via crafted ip address
 ilhomjonr/cve-2026-70376
Advisory and Python PoC for Pluck CMS CSRF: fail-open Referer check plus double-extension upload enables webshell deployment and remote code…
 flame-11/cve-2016-15041-mainwp-dashboard
Vuln lab: MainWP Dashboard <= 3.1.2 Unauthenticated Stored XSS
 tiger-foxx/exploit-react-cve-2025-55182
This tool is a Proof of Concept (PoC) intended for security research and educational purposes only. Using this tool on systems without explicit…

 j0lt-github/react2shell-burp
Burp Suite extension for detecting CVE-2025-55182 (React2Shell) unsafe deserialization vulnerability. Features safe digest check, PoC redirect mode,…
 shentao83/news-8.6.0-cve-2026-8726-backport
Minimal security backport for CVE-2026-8726 in georgringer/news 8.6.0
 galoget/responsivefilemanager-cve-2022-46604
Responsive FileManager v.9.9.5 vulnerable to CVE-2022-46604.
 r00tjunip3r1/poc-cve-2024-6778
Proof-of-concept exploit for CVE-2024-6778, a Chromium sandbox escape via a malicious browser extension, achieving code execution on privileged WebUI…
 wubinworks/magento2-session-reaper-patch
Patch for CVE-2025-54236(a.k.a Session Reaper) which allows customer account takeover and RCE under certain conditions. This patch is actually a…